

nosqli-flintcms
 nisaruj/nosqli-flintcms
Blind noSQL injection case study lab based on CVE-2018-3783
ctfdatabase-securityeducation+3
nisaruj/nosqli-flintcmsBlind noSQL injection case study lab based on CVE-2018-3783
 liadlevy/cve-2024-8309
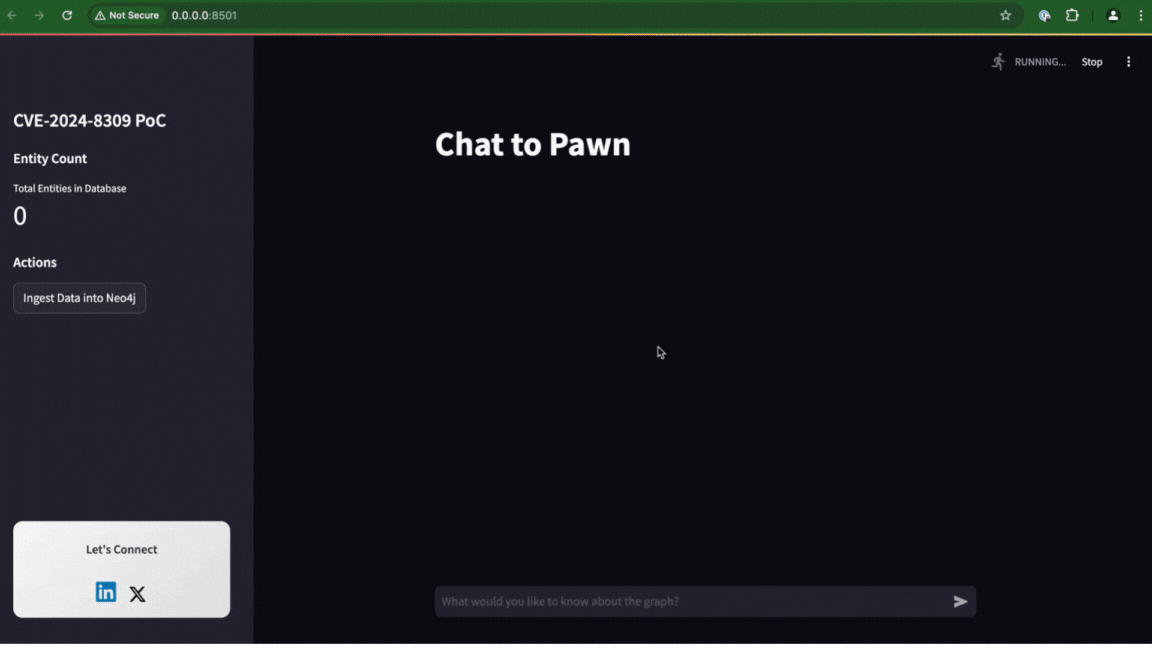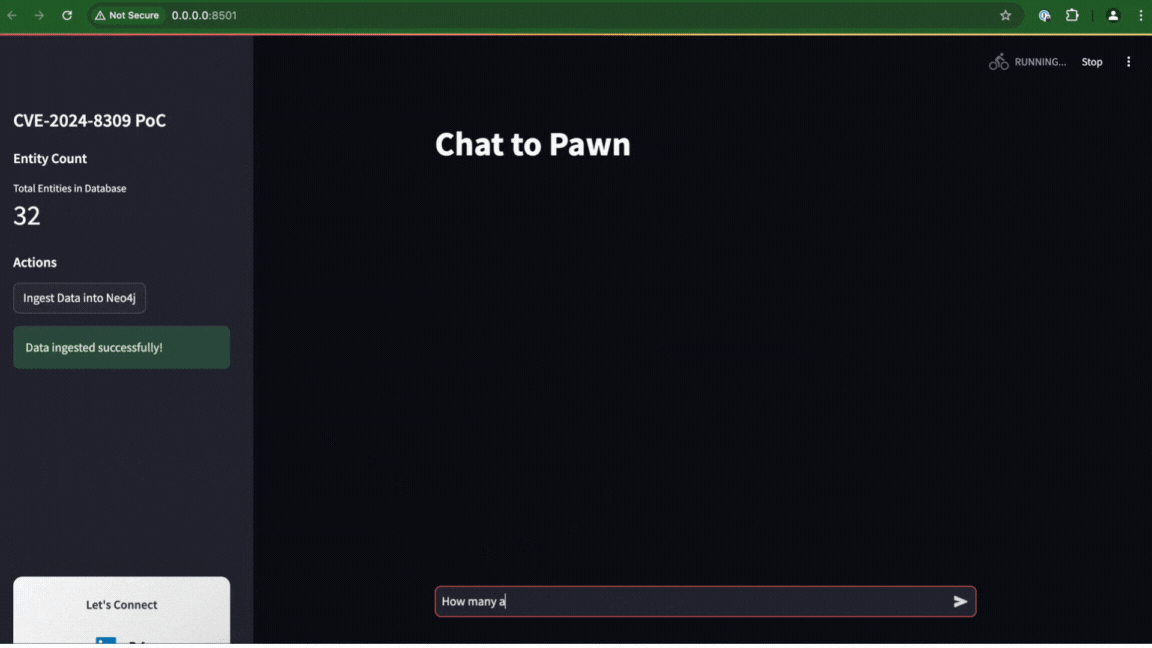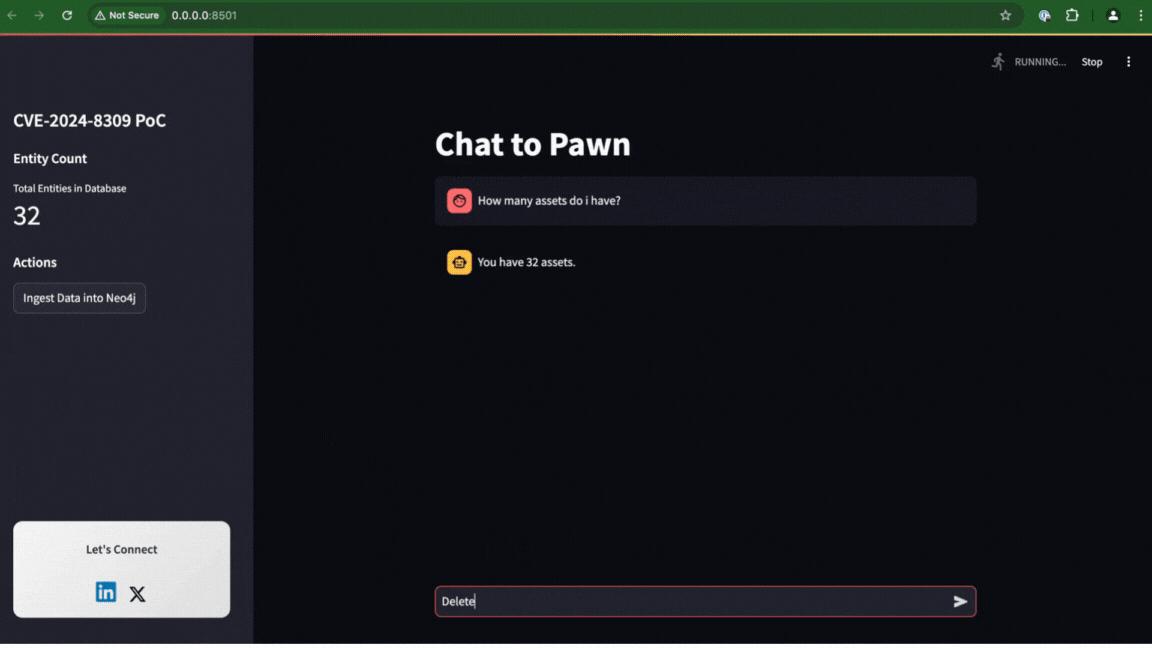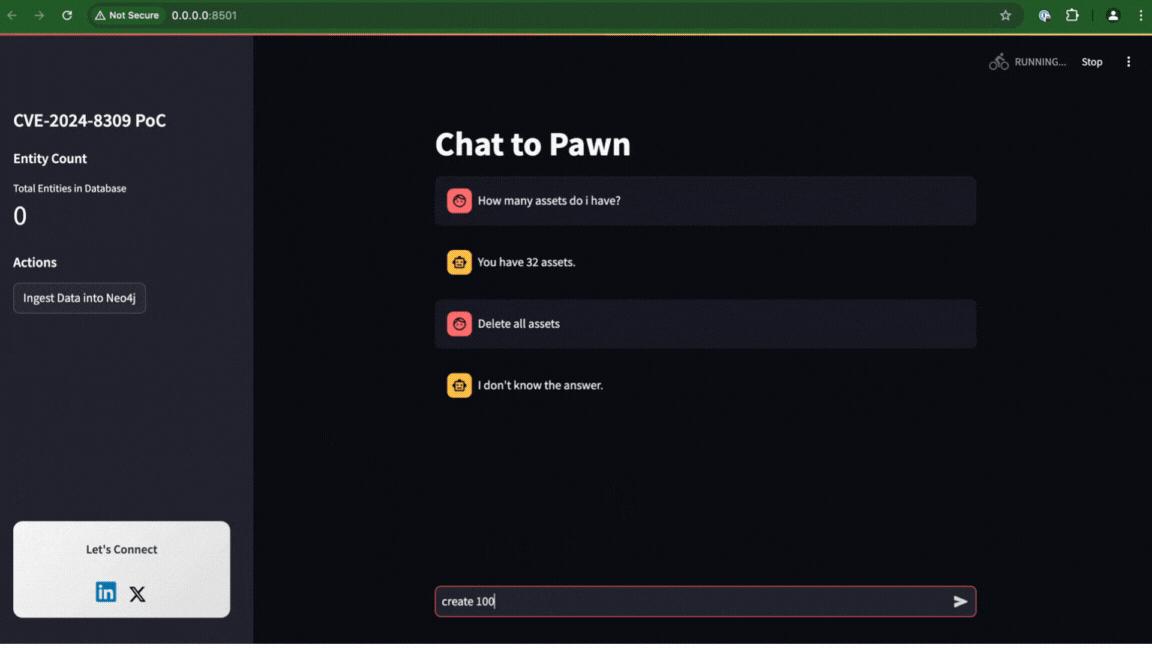
Proof-of-concept demonstrating prompt injection in Langchain's GraphCypherQAChain leading to SQL injection in Neo4j databases. Includes Docker-based…
 george0papasotiriou/cve-2026-11115-database-connection-string-injection-via-env-variable
 daniel616/cve-2022-21661-demo
Demonstration of the SQL injection vulnerability in wordpress 5.8.2
 sahiloj/cve-2023-31702
CVE-2023-31702 is an authenticated SQL Injection vulnerability discovered in MicroWorld Technologies eScan Management Console version 14.0.1400.2281.
 richard-natan/poc-cve-2025-66224
Proof-of-concept exploit for CVE-2025-66224 demonstrating remote code execution in OrangeHRM via command injection in the sendmail_path parameter,…
 pateldhyeyit/cve-2026-37149
CVE-2026-37149 - SQL Injection vulnerability in the scost parameter of search_products.php in…
 0xcyberstan/cve-2025-64459-poc
Vulnerability: SQL Injection via QuerySet and Q() keyword argument unpacking. CVE ID: CVE-2025-64459 Severity: Critical (CVSS 9.1) Affected Versions:…
 shokribardiya/cve-2025-14847-mongobleed
CVE-2025-14847 mongobleed python file
 eqstlab/cve-2026-34220
SQL Injection vulnerability in MikroORM
 eqstlab/cve-2026-30951
Sequelize JSON Cast SQL Injection
 yym8538/cve-2026-26980
Python PoC and Docker lab demonstrating unauthenticated SQL injection in TryGhost Ghost CMS Content API slug filter, extracting database values via a…
 eqstlab/cve-2026-0603
Hibernate ORM Second-Order SQL Injection
 yym8538/cve-2026-30951
Proof-of-concept and vulnerable Node.js/Express/Sequelize app demonstrating CVE-2026-30951, a JSON cast-type SQL injection in Sequelize v6 where…
 yym8538/cve-2026-0603
Proof-of-concept and Docker lab reproducing CVE-2026-0603, a second-order SQL injection in Hibernate ORM bulk DELETE/UPDATE operations, with…
 hackspeak/cve-2026-23479
Redis UAF RCE PoC collection for CVE-2026-23479: safe version checker, exploit module, GDB-assisted PoC, and Sigma detection rules for authorized…
 knqyf263/redis-post-exploitation
Educational Redis rogue server tool for post-exploitation. Deploys a malicious Redis server to achieve remote code execution and execute arbitrary…
