
CVE-2024-34693
 mr-r00t11/cve-2024-34693
An input validation vulnerability in Apache Superset allows an authenticated attacker to create a MariaDB connection with local_infile enabled,…
database-securitydata-exfiltrationexploitation+3
mr-r00t11/cve-2024-34693An input validation vulnerability in Apache Superset allows an authenticated attacker to create a MariaDB connection with local_infile enabled,…
 duo-labs/mysslstrip
Proof-of-concept tool demonstrating MITM attack to strip SSL/TLS from MySQL connections, exploiting CVE-2015-3152 for network penetration testing.
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 gchq/cyberchef
The Cyber Swiss Army Knife - a web app for encryption, encoding, compression and data analysis
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 tarunkant/gopherus
This tool generates gopher link for exploiting SSRF and gaining RCE in various servers
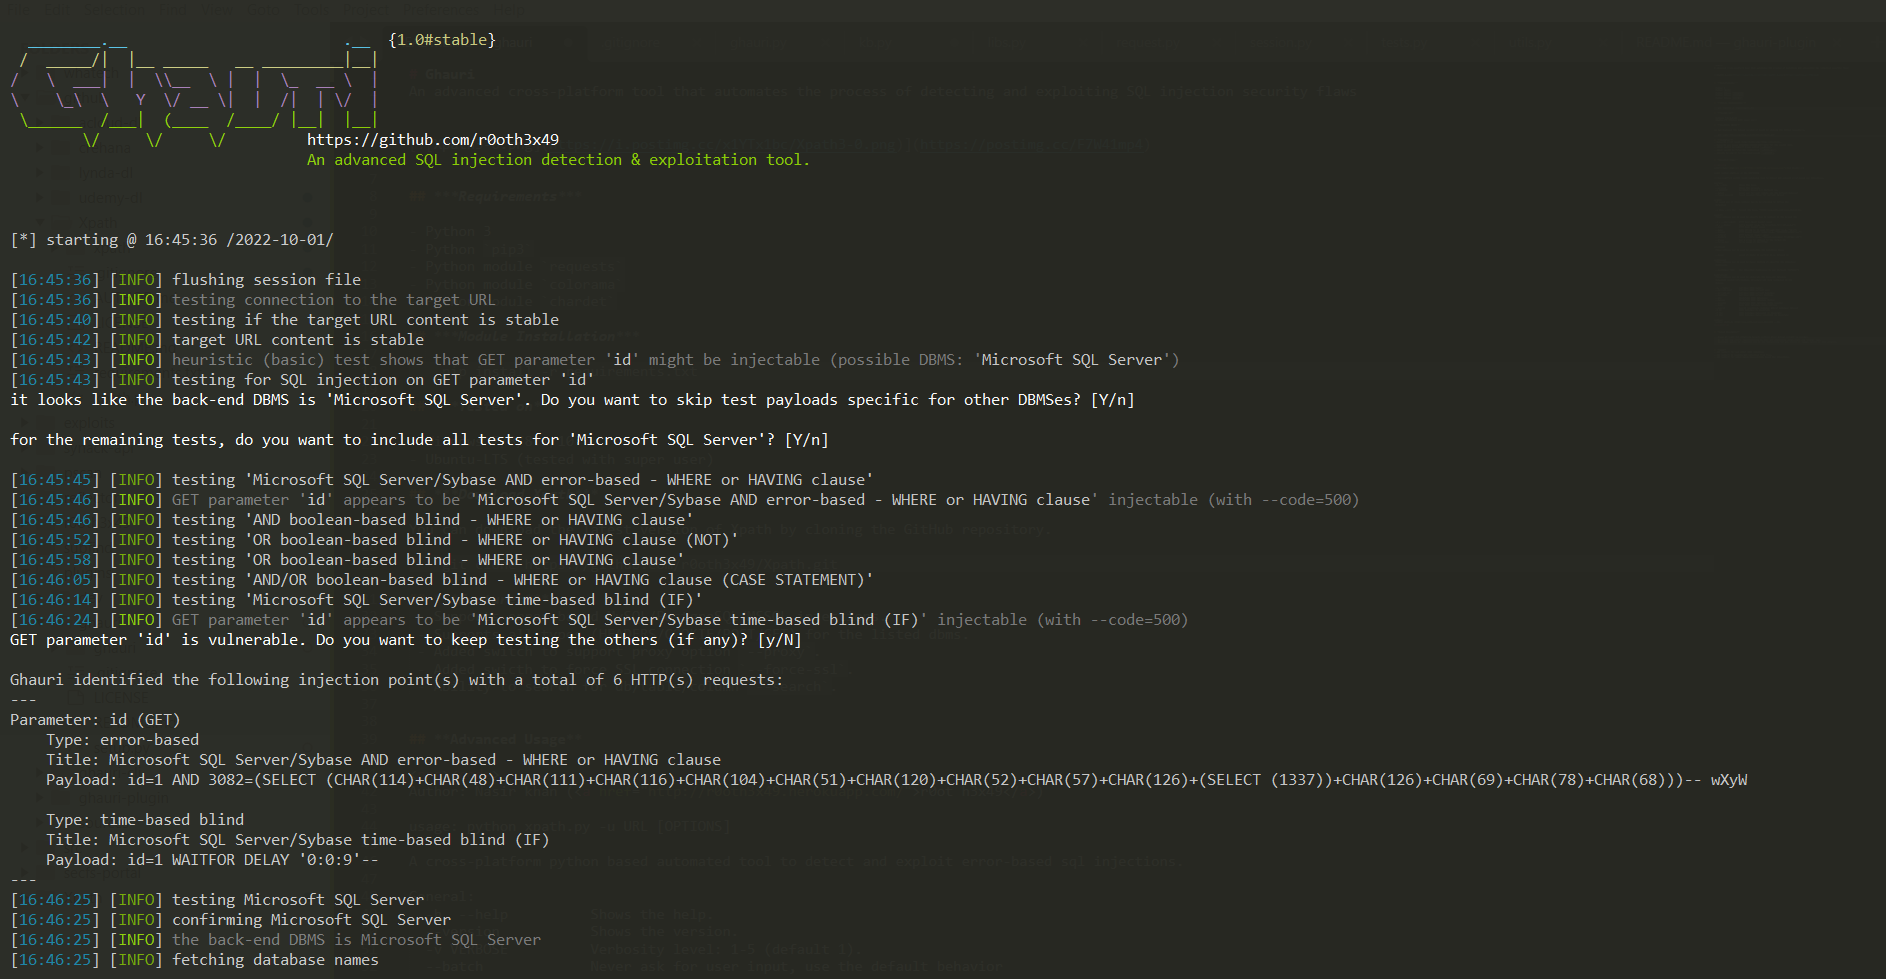 r0oth3x49/ghauri
An advanced cross-platform tool that automates the process of detecting and exploiting SQL injection security flaws
 codingo/nosqlmap
Automated NoSQL database enumeration and web application exploitation tool.
 b374k/b374k
PHP Webshell with handy features
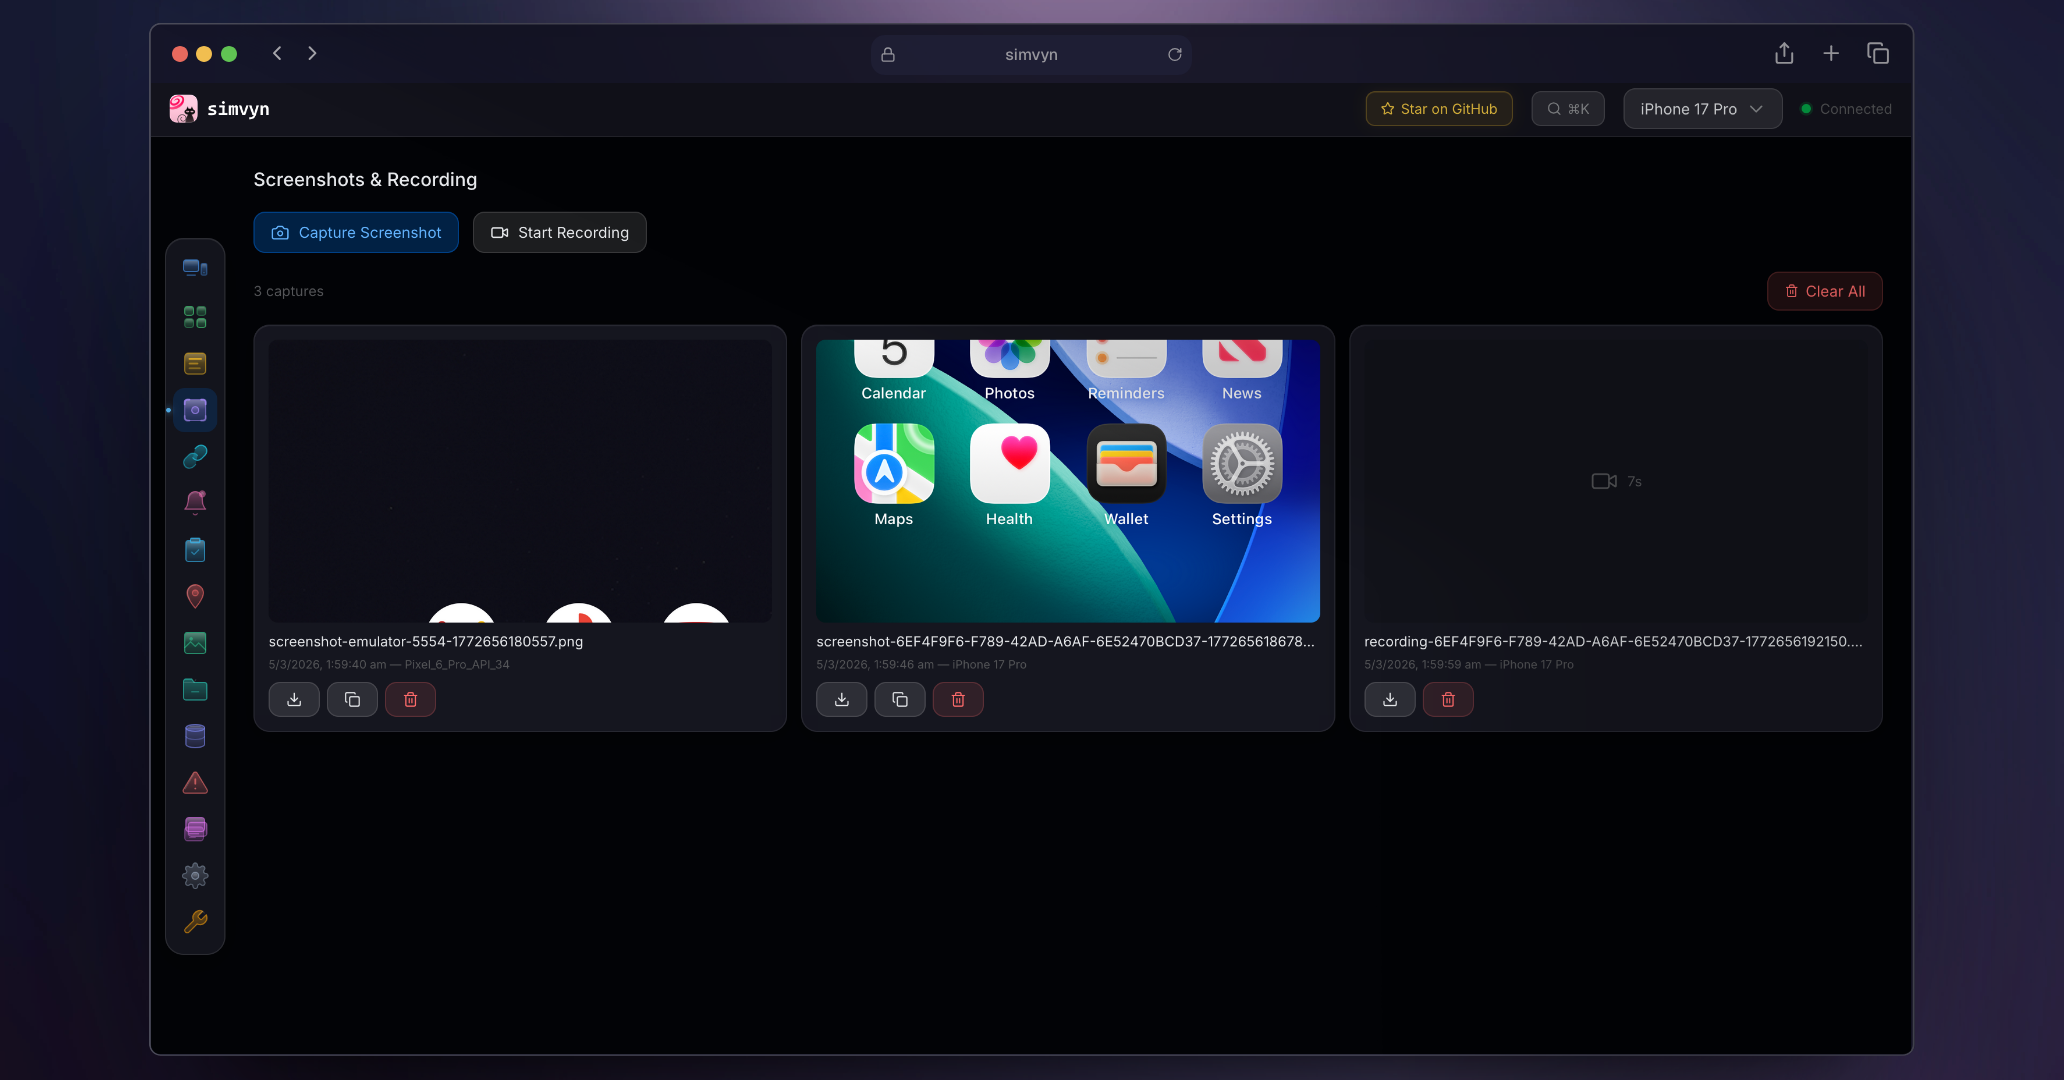 pranshuchittora/simvyn
Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI
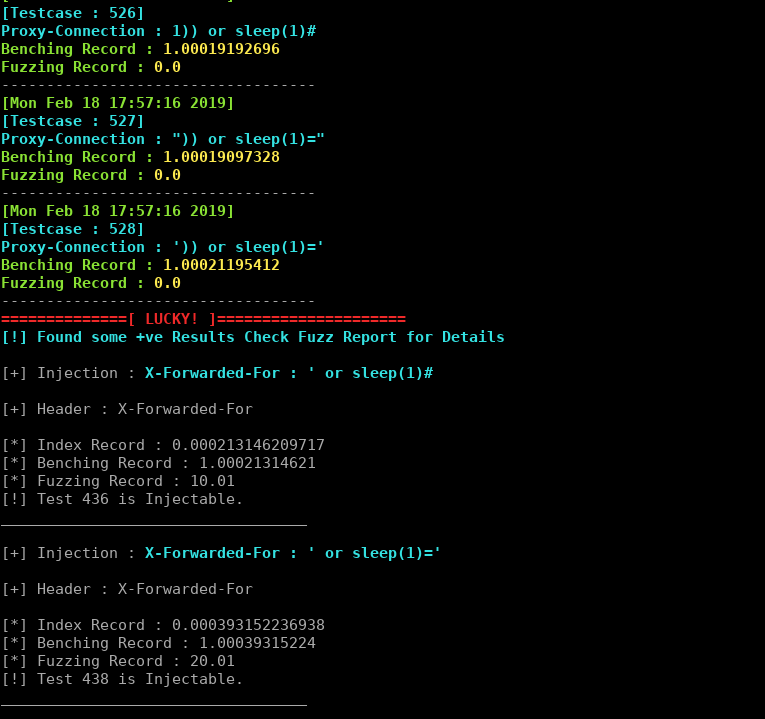 johntroony/blisqy
Version 0.2 - Exploit Time-based blind-SQL injection in HTTP-Headers (MySQL/MariaDB).
 torque59/nosqlpot
The NoSQL Honeypot Framework
 adamwhitehat/judge-jury-and-executable
A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…
 hikari-systems/slater
Low-memory graphdb with Bolt+tls support, at-rest encryption & vectors designed for local replica graph use cases.
 fsecurelabs/n1qlmap
The tool exfiltrates data from Couchbase database by exploiting N1QL injection vulnerabilities.
 nccgroup/raccoon
Salesforce object access auditor
 neo23x0/mongobleed-detector
Detection Script for MongoBleed Exploitation