
CVE-2026-20253
 het-kalariya/cve-2026-20253
Self-contained security training lab reproducing CVE-2026-20253 (Splunk Enterprise unauthenticated RCE). Provides a Docker-based environment to…
authenticationcommand-and-controlctf+9
het-kalariya/cve-2026-20253Self-contained security training lab reproducing CVE-2026-20253 (Splunk Enterprise unauthenticated RCE). Provides a Docker-based environment to…
 nisaruj/nosqli-flintcms
Blind noSQL injection case study lab based on CVE-2018-3783
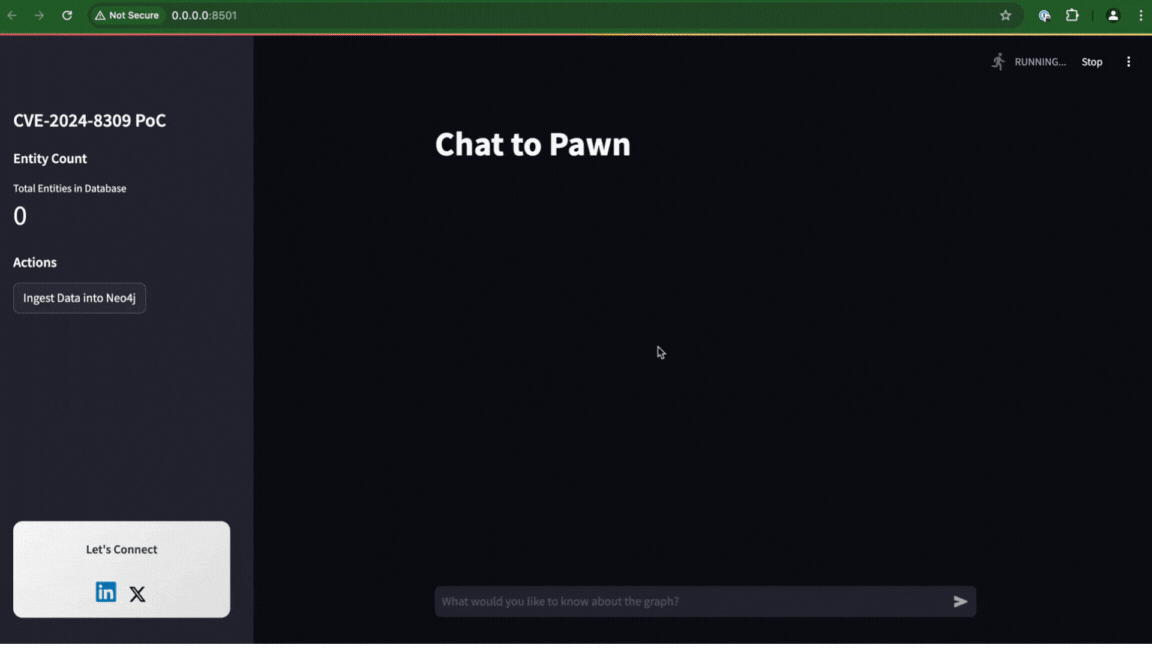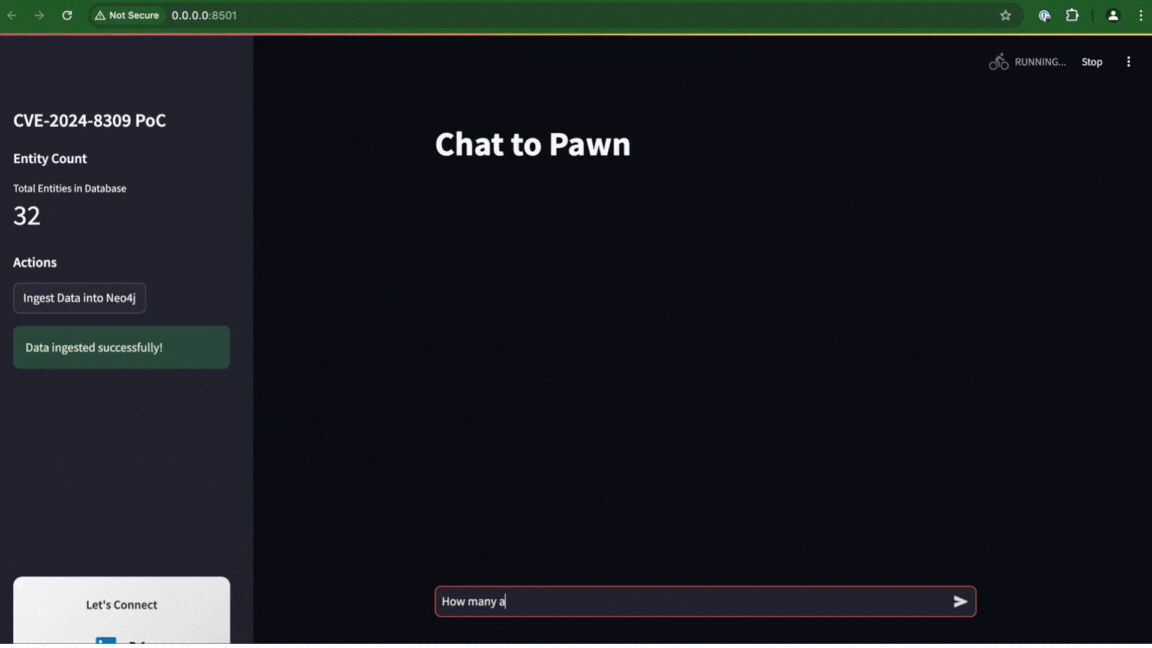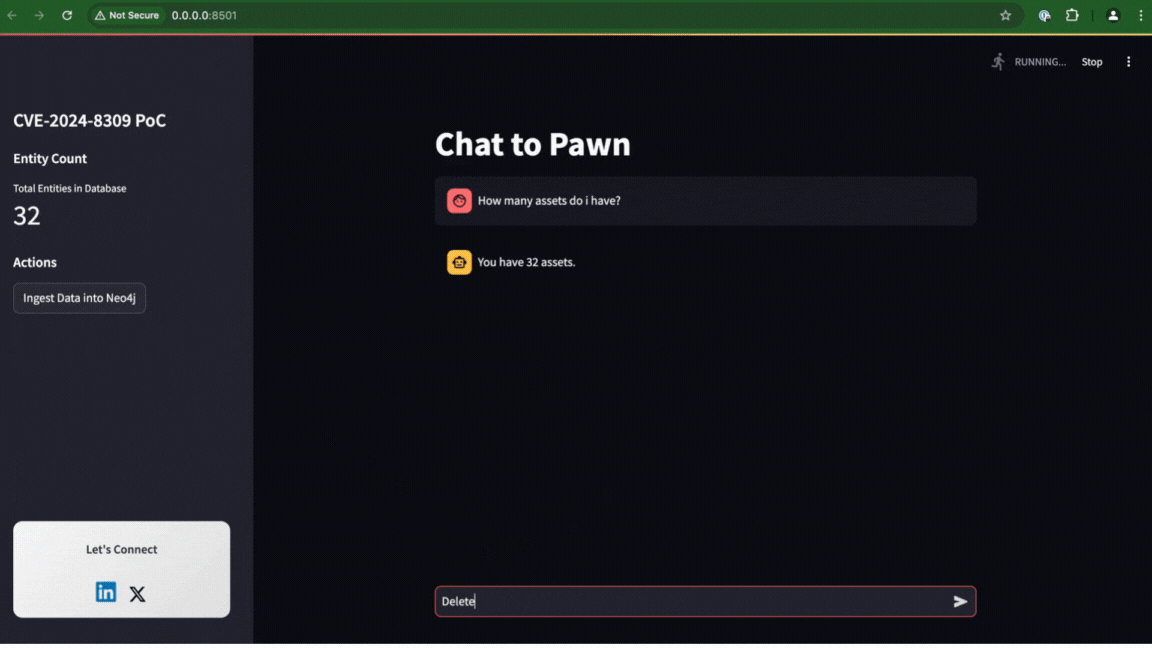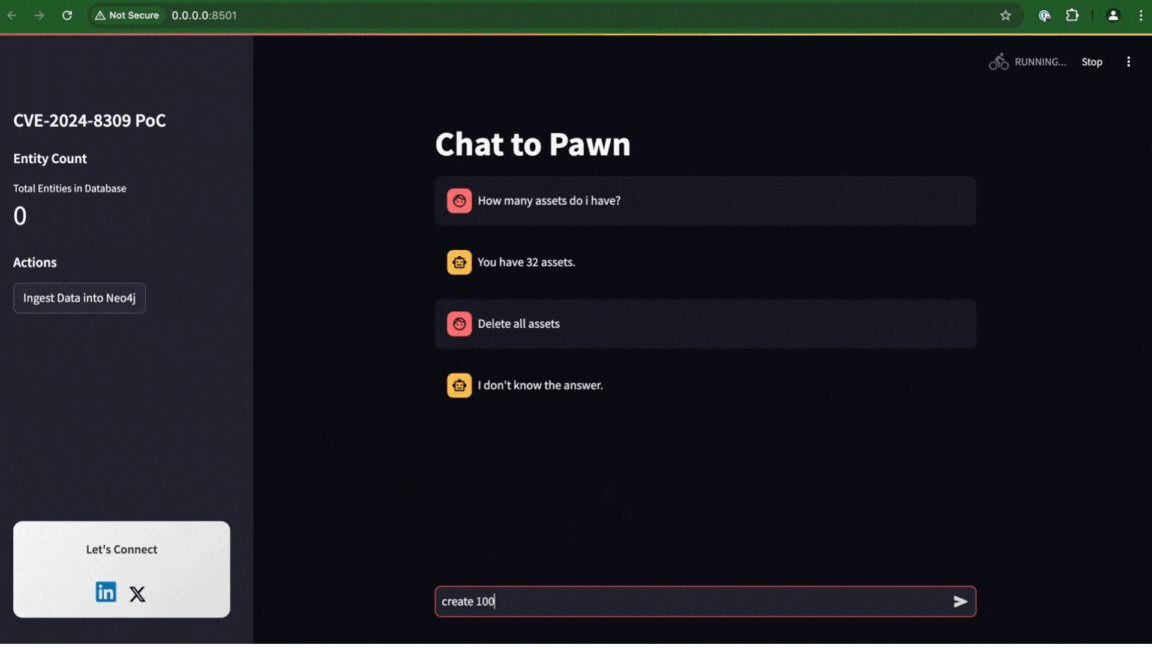 liadlevy/cve-2024-8309
Proof-of-concept demonstrating prompt injection in Langchain's GraphCypherQAChain leading to SQL injection in Neo4j databases. Includes Docker-based…
 george0papasotiriou/cve-2026-11115-database-connection-string-injection-via-env-variable
 daniel616/cve-2022-21661-demo
Demonstration of the SQL injection vulnerability in wordpress 5.8.2
 sahiloj/cve-2023-31702
CVE-2023-31702 is an authenticated SQL Injection vulnerability discovered in MicroWorld Technologies eScan Management Console version 14.0.1400.2281.
 pateldhyeyit/cve-2026-37149
CVE-2026-37149 - SQL Injection vulnerability in the scost parameter of search_products.php in…
 0xcyberstan/cve-2025-64459-poc
Vulnerability: SQL Injection via QuerySet and Q() keyword argument unpacking. CVE ID: CVE-2025-64459 Severity: Critical (CVSS 9.1) Affected Versions:…
 eqstlab/cve-2026-30951
Sequelize JSON Cast SQL Injection
 eqstlab/cve-2026-34220
SQL Injection vulnerability in MikroORM
 eqstlab/cve-2026-0603
Hibernate ORM Second-Order SQL Injection
 hackspeak/cve-2026-23479
Redis UAF RCE PoC collection for CVE-2026-23479: safe version checker, exploit module, GDB-assisted PoC, and Sigma detection rules for authorized…
 knqyf263/redis-post-exploitation
Educational Redis rogue server tool for post-exploitation. Deploys a malicious Redis server to achieve remote code execution and execute arbitrary…
 peakcyber-security/cve-2025-14847
CVE-2025-14847 | MongoBleed vulnerability proof of concept project
 sho-luv/mongobleed
CVE-2025-14847 (MongoBleed) scanner and exploit tool. Unauthenticated MongoDB heap memory leak via zlib decompression. Detection, memory extraction,…
 richard-natan/poc-cve-2025-66224
Proof-of-concept exploit for CVE-2025-66224 demonstrating remote code execution in OrangeHRM via command injection in the sendmail_path parameter,…
 afnaan-ahmed/cve-2025-14598
Technical advisory and analysis of CVE-2025-14598, a critical unauthenticated SQL injection in BET e-Portal enabling database manipulation and…
 malvika-thakur/cve-2019-14234
POC-Django JSONField/HStoreField SQL Injection Vulnerability (CVE-2019-14234)