

OracleOTM
 ofirhamam/oracleotm
Python tool for exploiting CVE-2021-35616
database-securityexploitationinformation-gathering+3
ofirhamam/oracleotmPython tool for exploiting CVE-2021-35616
 shentao83/news-8.6.0-cve-2026-8726-backport
Minimal security backport for CVE-2026-8726 in georgringer/news 8.6.0
 geniuszly/cve-2019-9193
is a PoC tool designed to exploit an authenticated Remote Code Execution (RCE) vulnerability in specific versions of PostgreSQL (9.3 - 11.7)
 ridhinva/drupal-jsonapi-sqli-scanner
Scanner: CVE-2026-9082 Drupal PostgreSQL SQLi via JSON:API — Python scanner for unauthenticated SQLi leading to RCE (CISA KEV)
 cerberusmrxi/cve-2026-44680-mikroorm-sql-injection-exploit-framework
PoC tool for CVE-2026-44680 affecting MikroORM ≤7.0.13. Exploits JSON path injection to extract database contents via UNION-based attacks. Features…
 nma-io/mongobleed
golang test tool for mongobleed (cve-2025-14847)
 paulsec/hqlmap
(Deprecated) HQLmap, Automatic tool to exploit HQL injections
 safebreach-labs/edraser
Remotely delete access logs, Windows event logs, databases, and files on target machines using automated scanning or manual attack selection for…
 mubix/solarflare
SolarWinds Orion Account Audit / Password Dumping Utility
 initroot/wodat
Windows Oracle Database Attack Toolkit
 adarshthakur14777-cyber/cve-2026-60137
wpsqli full SQLi extractor + dumper for CVE-2026-60137
 metthk/cve-2023-48084-revised
Python PoC exploiting time-based blind SQLi in Nagios XI to extract database contents, with multithreaded binary-search extraction and CLI…
 hamibubu/cve-2023-48084
Python program to dump all the databases, exploiting NagiosXI sqli vulnerability
 jas502n/sscms_decrypt
sscms database decrypt
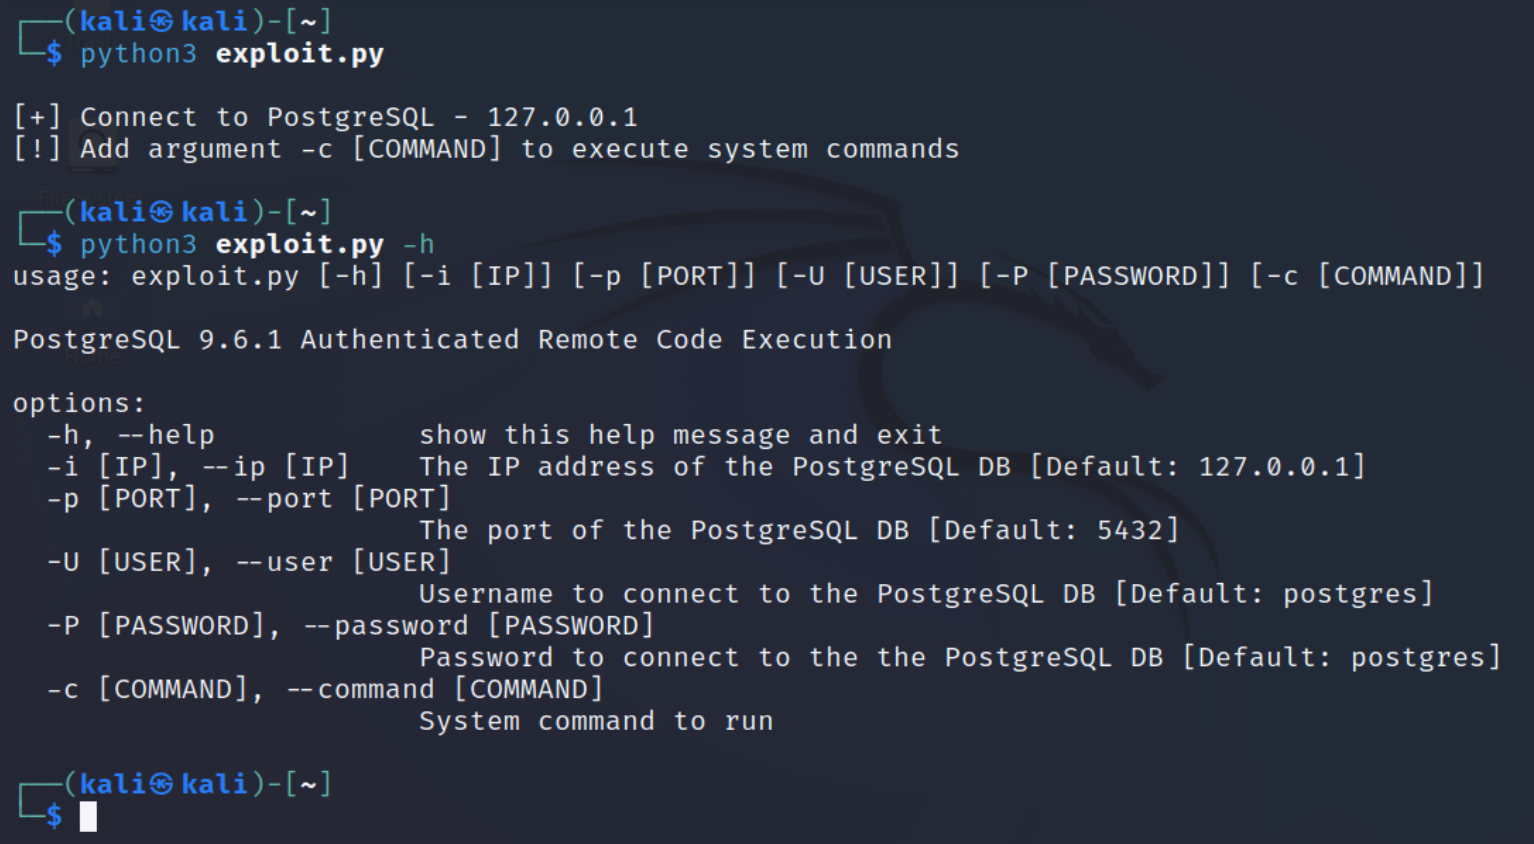 paulotrindadec/cve-2019-9193
Proof-of-concept exploit for authenticated remote code execution in PostgreSQL 9.6.1, demonstrating how misconfigured databases can be leveraged for…
 nanaao/cve-2021-29442-nacos-derby-rce-exp
Nacos Derby命令执行漏洞利用脚本