
proftpd-CVE-2026-42167-poc
 zeropathai/proftpd-cve-2026-42167-poc
POCs to demonstrate CVE-2026-42167 in ProFTPD
authentication-authorizationdatabase-securityeducation+6
23
zeropathai/proftpd-cve-2026-42167-pocPOCs to demonstrate CVE-2026-42167 in ProFTPD
 pedrocruz2202/mongobleed-scanner
🔍 Scan for MongoDB vulnerabilities with MongoBleed, a high-performance tool for detecting CVE-2025-14847 across large networks quickly and…
 nu11secur1ty/chusa
chusa - 注射 - the new generation of sqlmap
 oldboy21/ldap-password-hunter
Automated tool that hunts for world-readable passwords in Active Directory LDAP databases by leveraging Kerberos authentication and ldapsearch to…
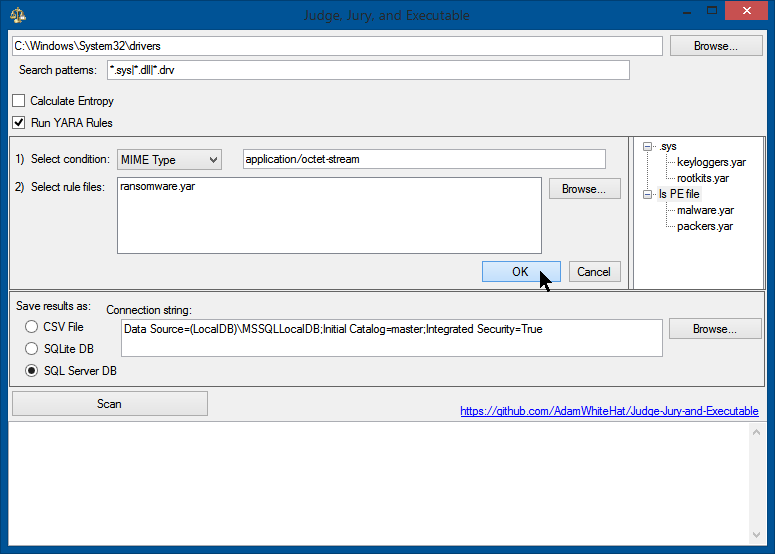 adamwhitehat/judge-jury-and-executable
A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…
 mr-r00t11/cve-2024-4879
CVE-2024-4879.py is a Python script designed to detect specific vulnerabilities in ServiceNow instances and dump database connection details if the…
 rockmelodies/django_sqli_target_cve-2025-64459
Exploit tool for CVE-2025-64459, targeting SQL injection vulnerabilities in Django applications. Enables automated testing and exploitation of…
 jdusane/cve-2024-4879
Python script designed to detect specific vulnerabilities in ServiceNow instances and dump database connection details if the vulnerability is found.…
 ofirhamam/oracleotm
Python tool for exploiting CVE-2021-35616
 metthk/cve-2023-48084-revised
Python PoC exploiting time-based blind SQLi in Nagios XI to extract database contents, with multithreaded binary-search extraction and CLI…
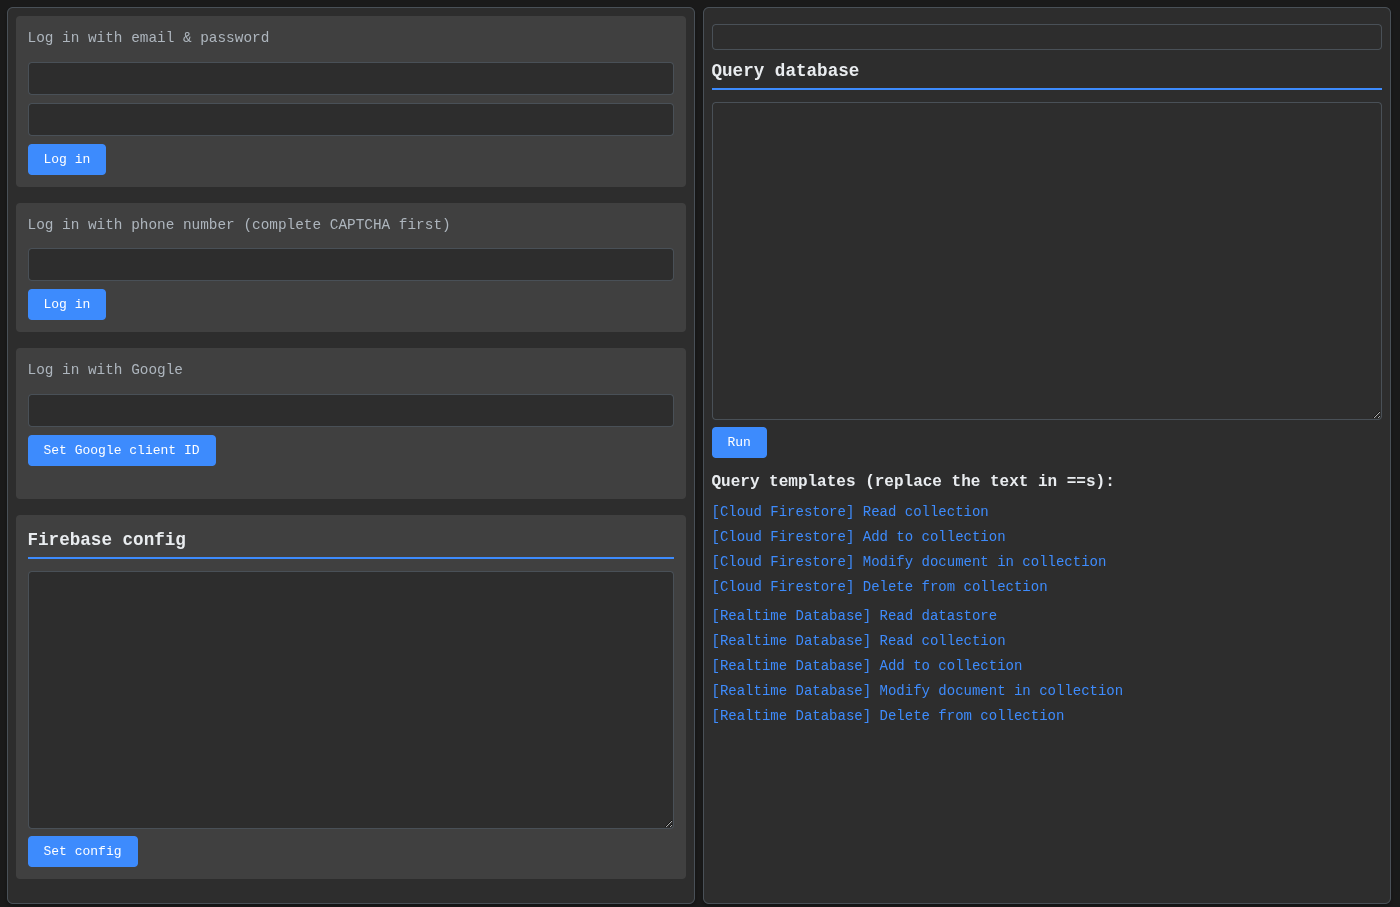 iosiro/baserunner
A tool for exploring Firebase datastores.
 heavyghost-le/poc_sql_injection_in_parse_server_prior_6.5.7_-_7.1.0
Advanced PostgreSQL database enumeration tool exploiting CVE-2024-39309 in Parse Server - Comprehensive SQL injection exploitation for security…
 adarshthakur14777-cyber/cve-2026-60137
wpsqli full SQLi extractor + dumper for CVE-2026-60137
 c137req/cve-2025-6713
craft aggregation pipeline to access data without proper authorisation due to improper handling of $mergeCursors in MongoDB >v8.0 <8.0.7, >v7.0…
 daniel2005d/mapxplore
Allow exporting the information downloaded with sqlmap to a relational Database like Postgres and sqlite
 m0b1u3/cve-2025-50565
Proof-of-concept exploit for an SQL injection vulnerability in Doubo ERP 1.0, enabling remote attackers to extract sensitive database information.
 gokul-krishnan-v-r/cve-2024-53900
Mongo Vulnub Lab...Try to Hack IT.....!
 sholls000/cve-2024-8465-poc
Intentionally vulnerable web application demonstrating SQL injection vulnerabilities (CVE-2024-8465) for educational purposes, including…