
cp30_XXE_partial_fix
 shanika04/cp30_xxe_partial_fix
version between CVE-2018-20433 and CVE-2019-5427
code-analysisdatabase-securitysupply-chain-security+1
shanika04/cp30_xxe_partial_fixversion between CVE-2018-20433 and CVE-2019-5427
 shoucheng3/xerial__sqlite-jdbc_cve-2023-32697_3-41-2-1
Java JDBC driver for SQLite databases with native library support across major operating systems, enabling standard database connectivity without…
 mubix/solarflare
SolarWinds Orion Account Audit / Password Dumping Utility
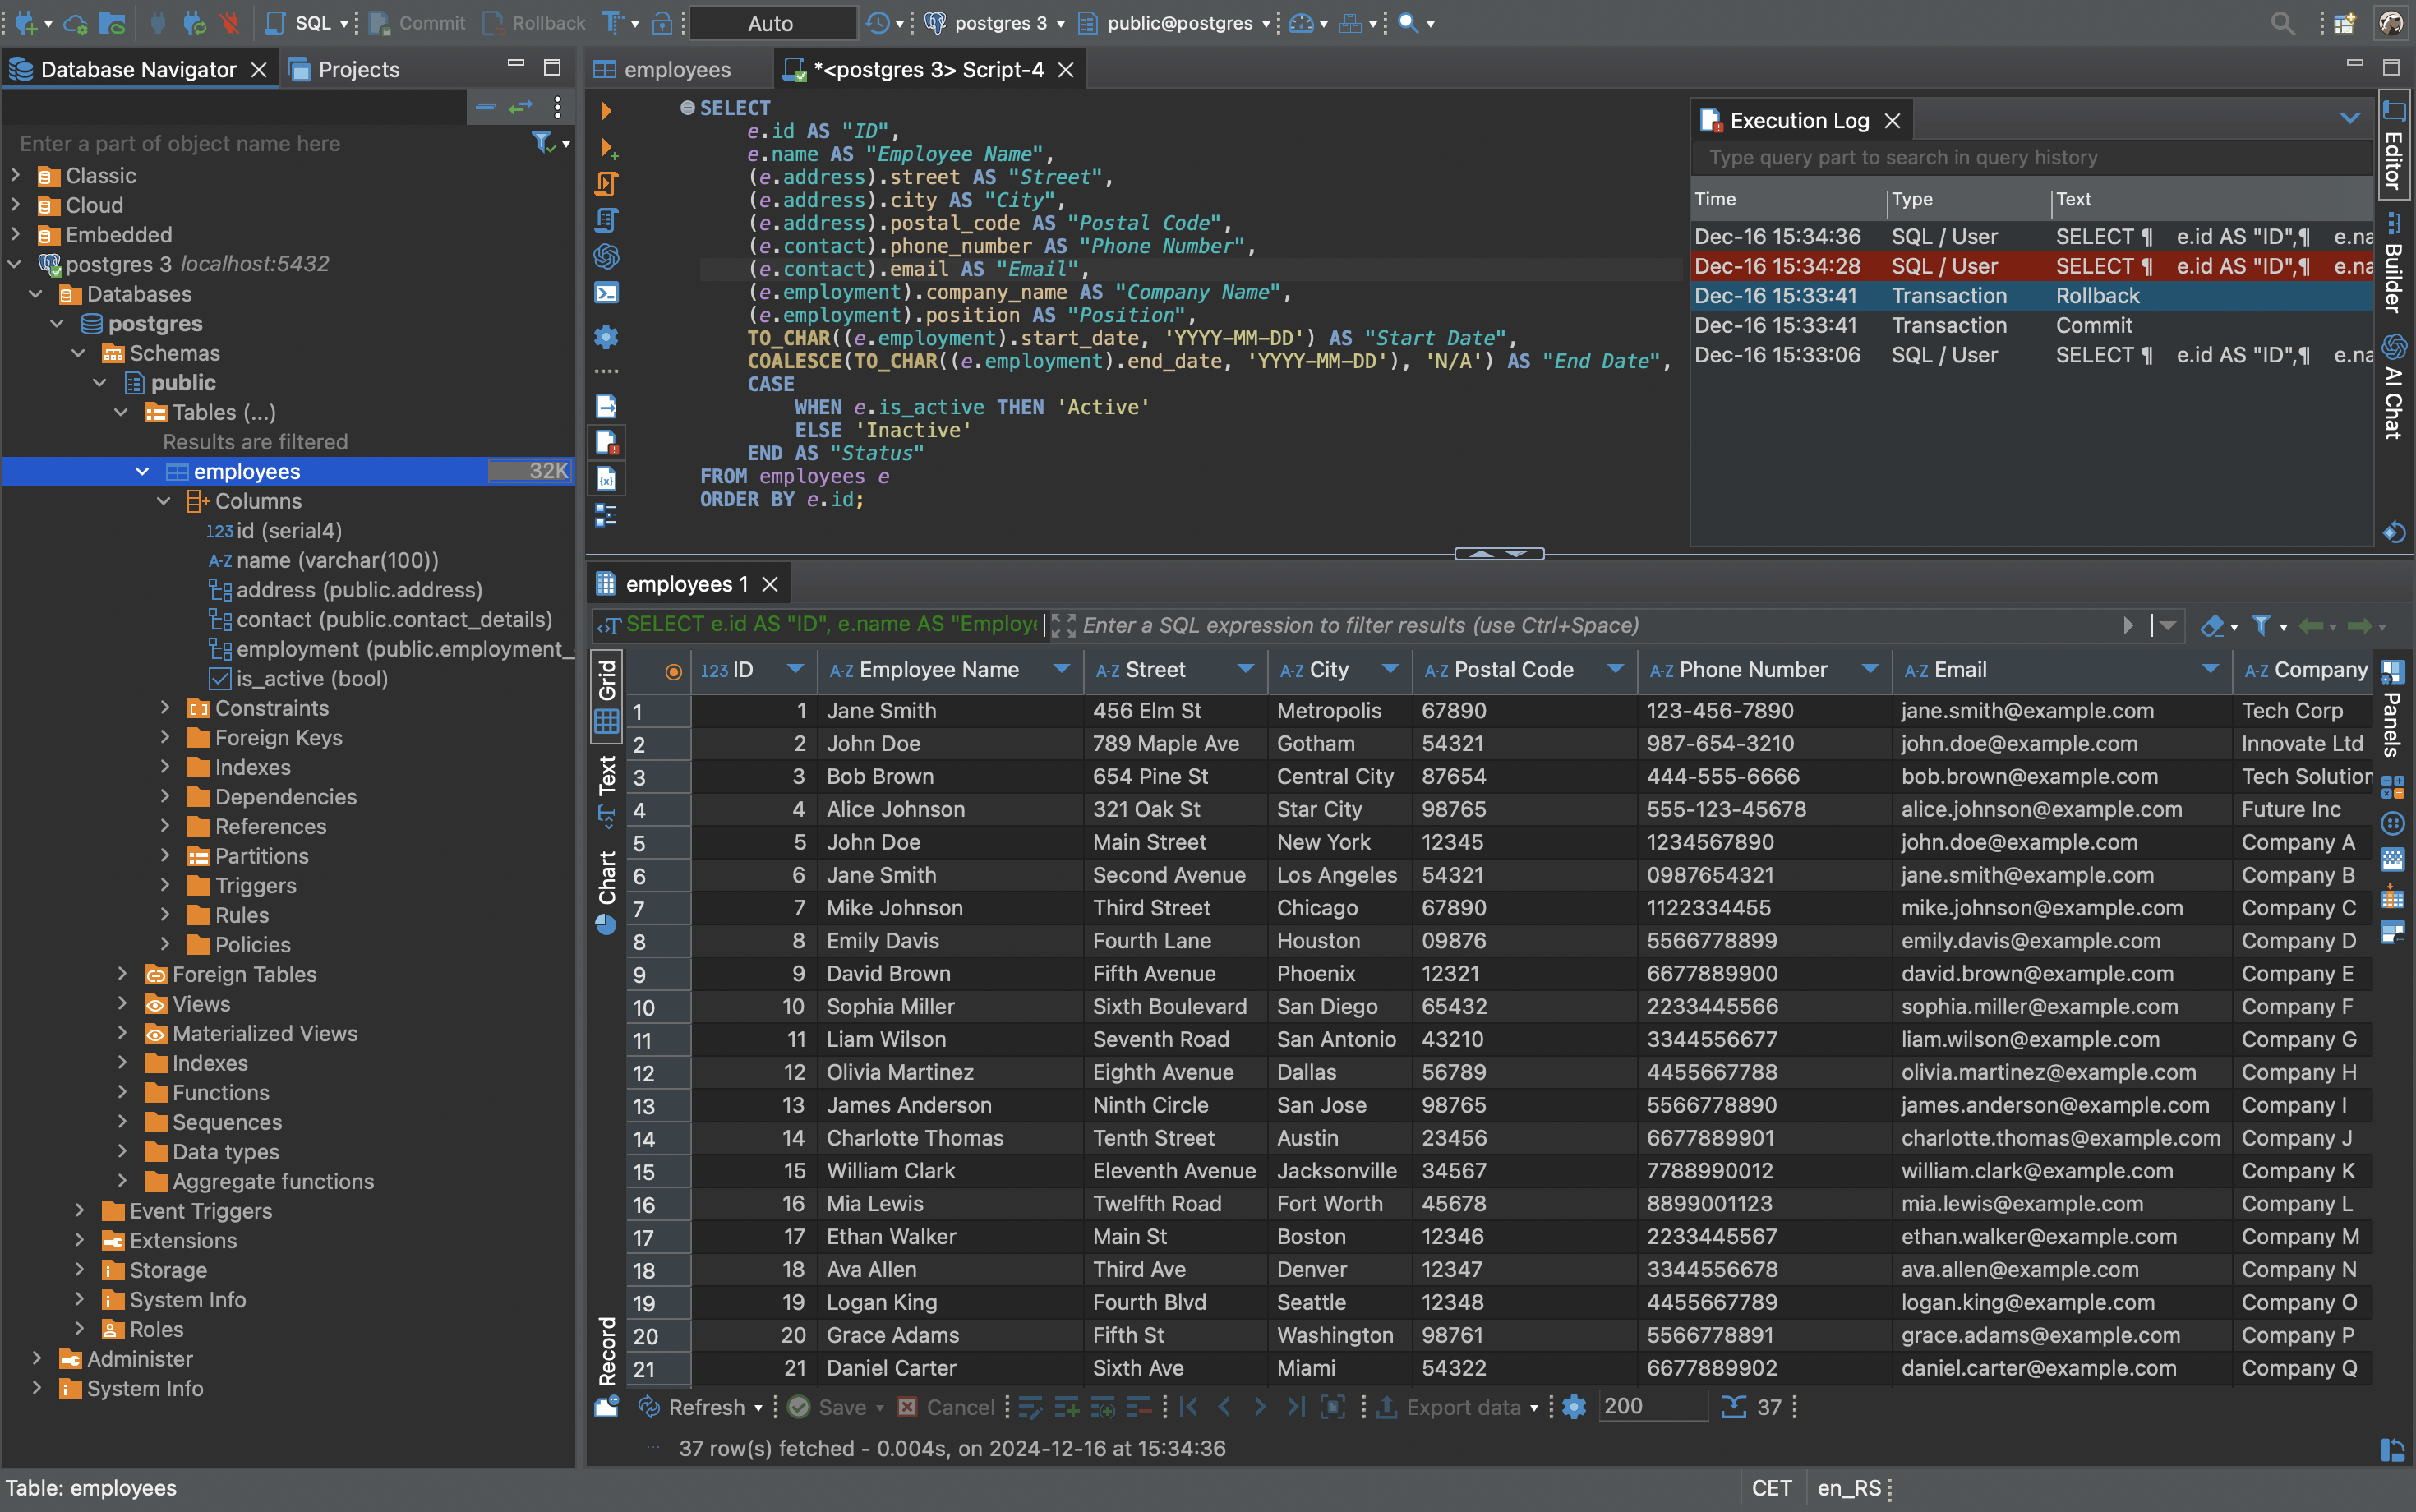 dbeaver/dbeaver
Free universal database tool and SQL client
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 jumpserver/jumpserver
JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH,…
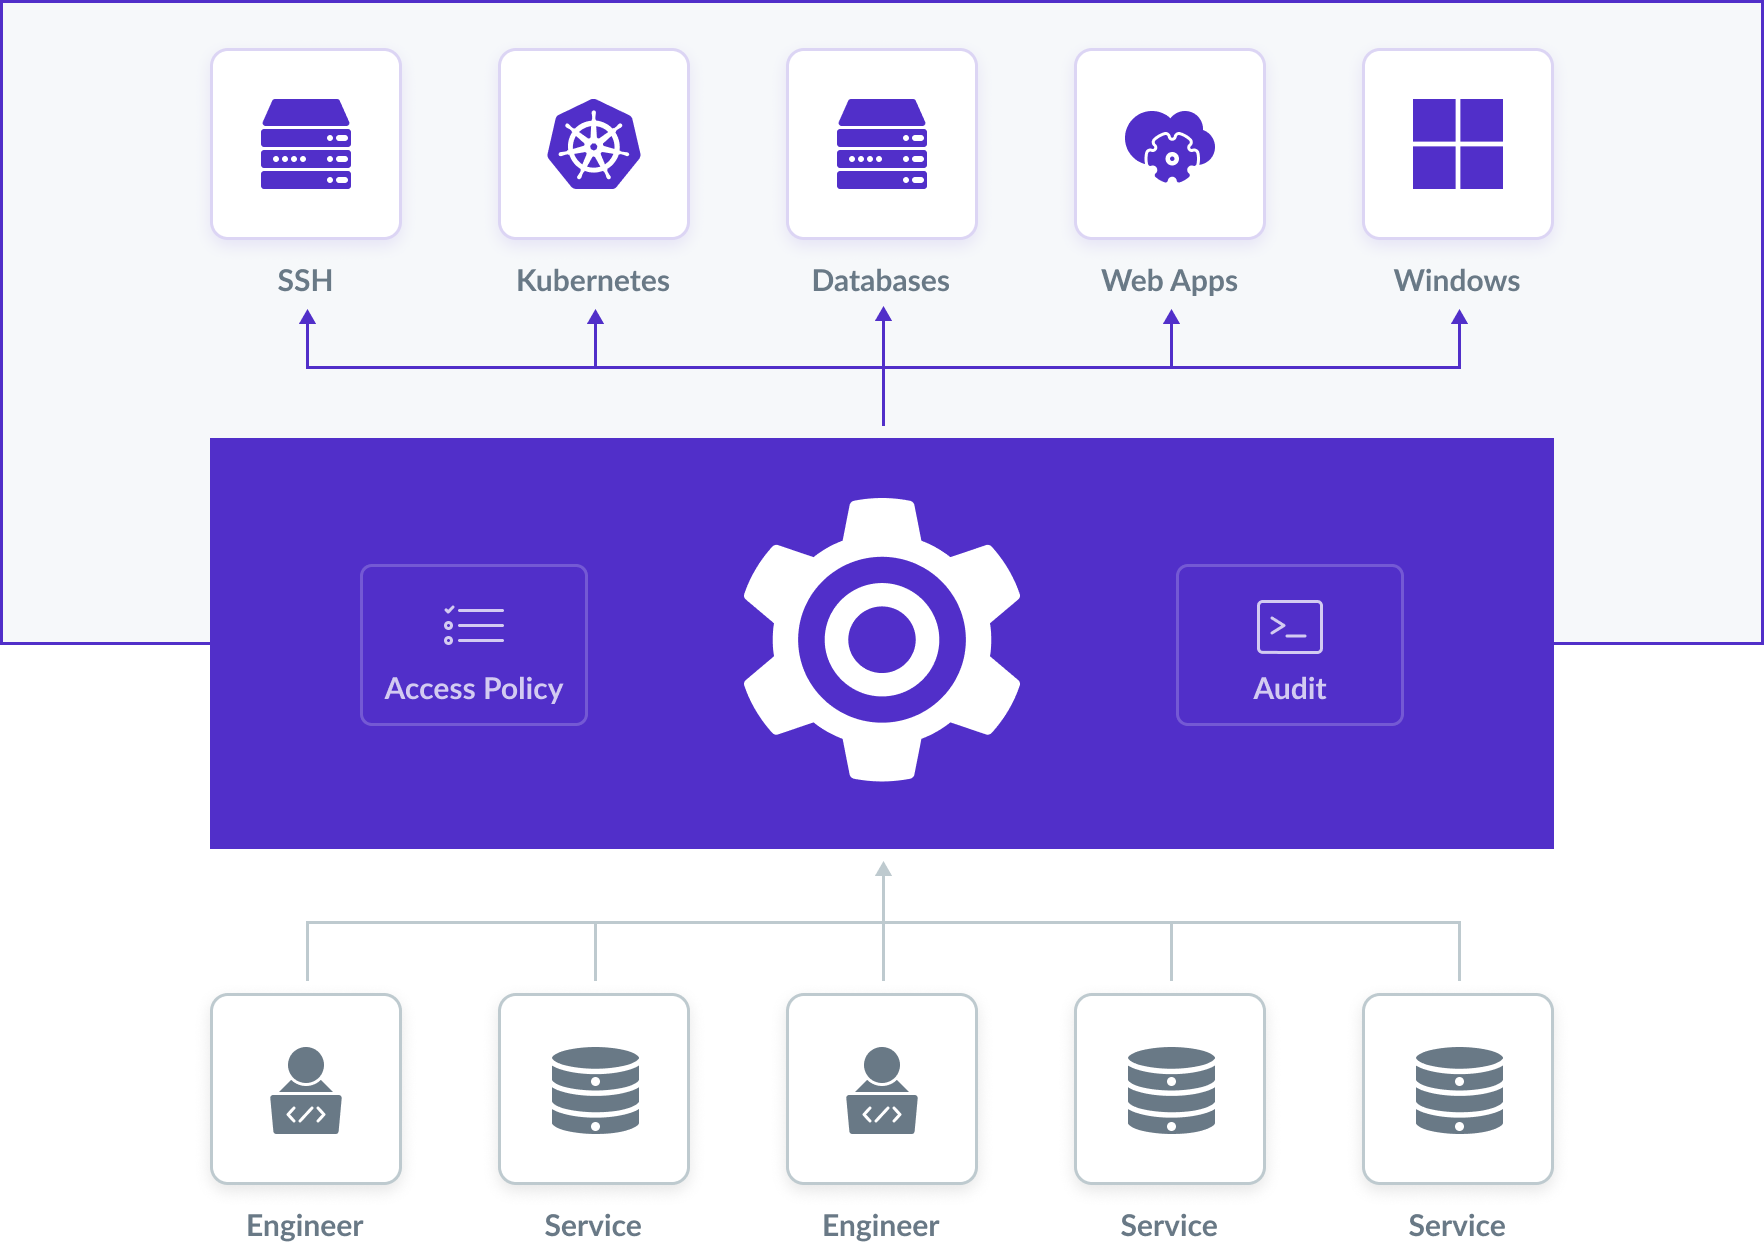 gravitational/teleport
The easiest, and most secure way to access and protect all of your infrastructure.
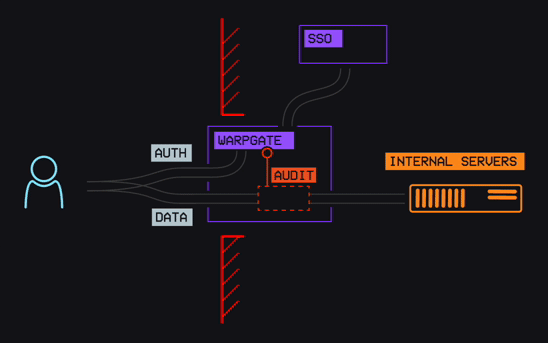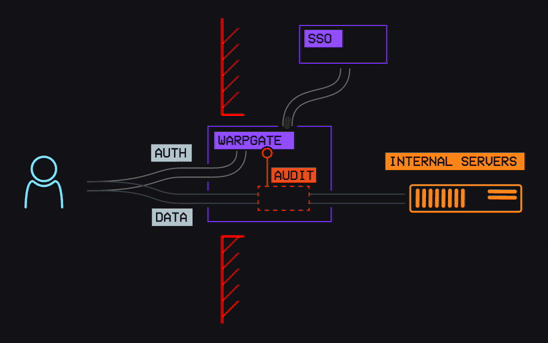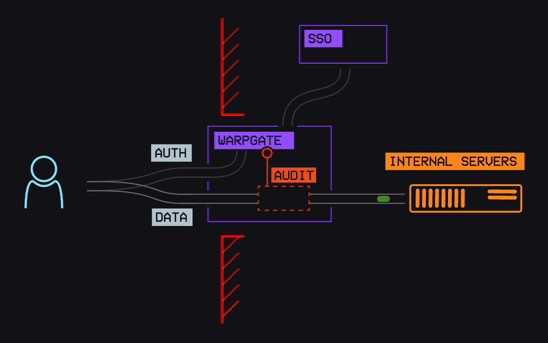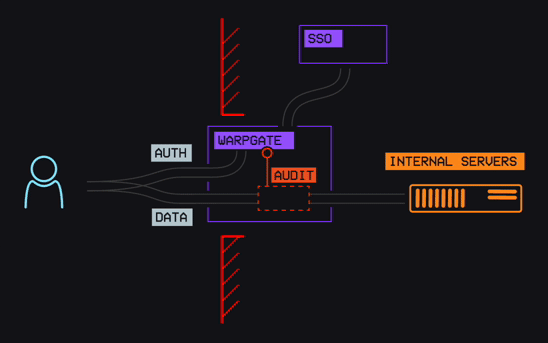 warp-tech/warpgate
Fully transparent SSH, HTTPS, Kubernetes, database and RDP/VNC bastion/PAM that doesn't need additional client-side software
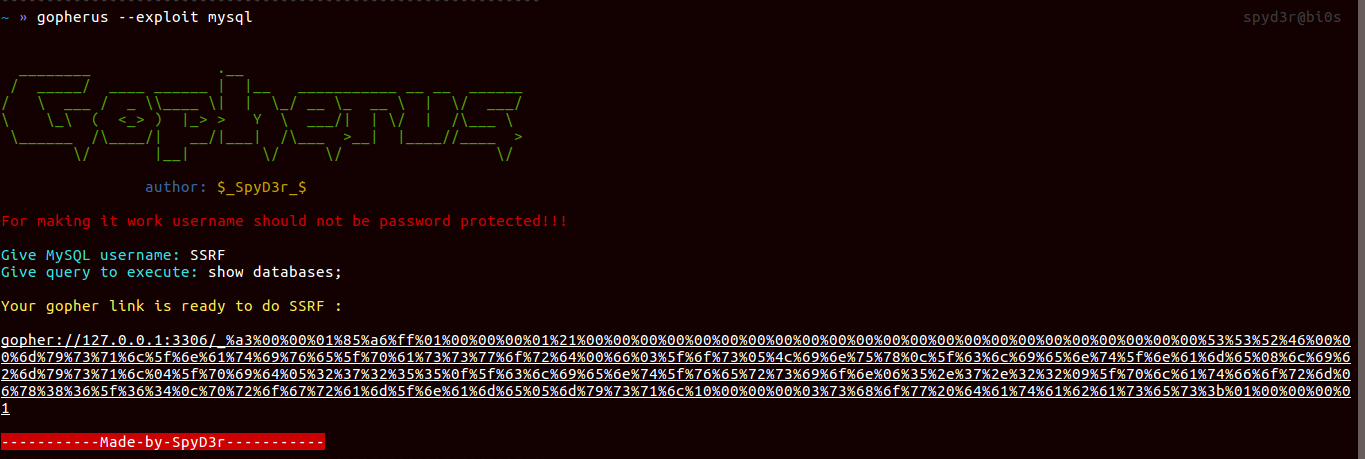 tarunkant/gopherus
This tool generates gopher link for exploiting SSRF and gaining RCE in various servers
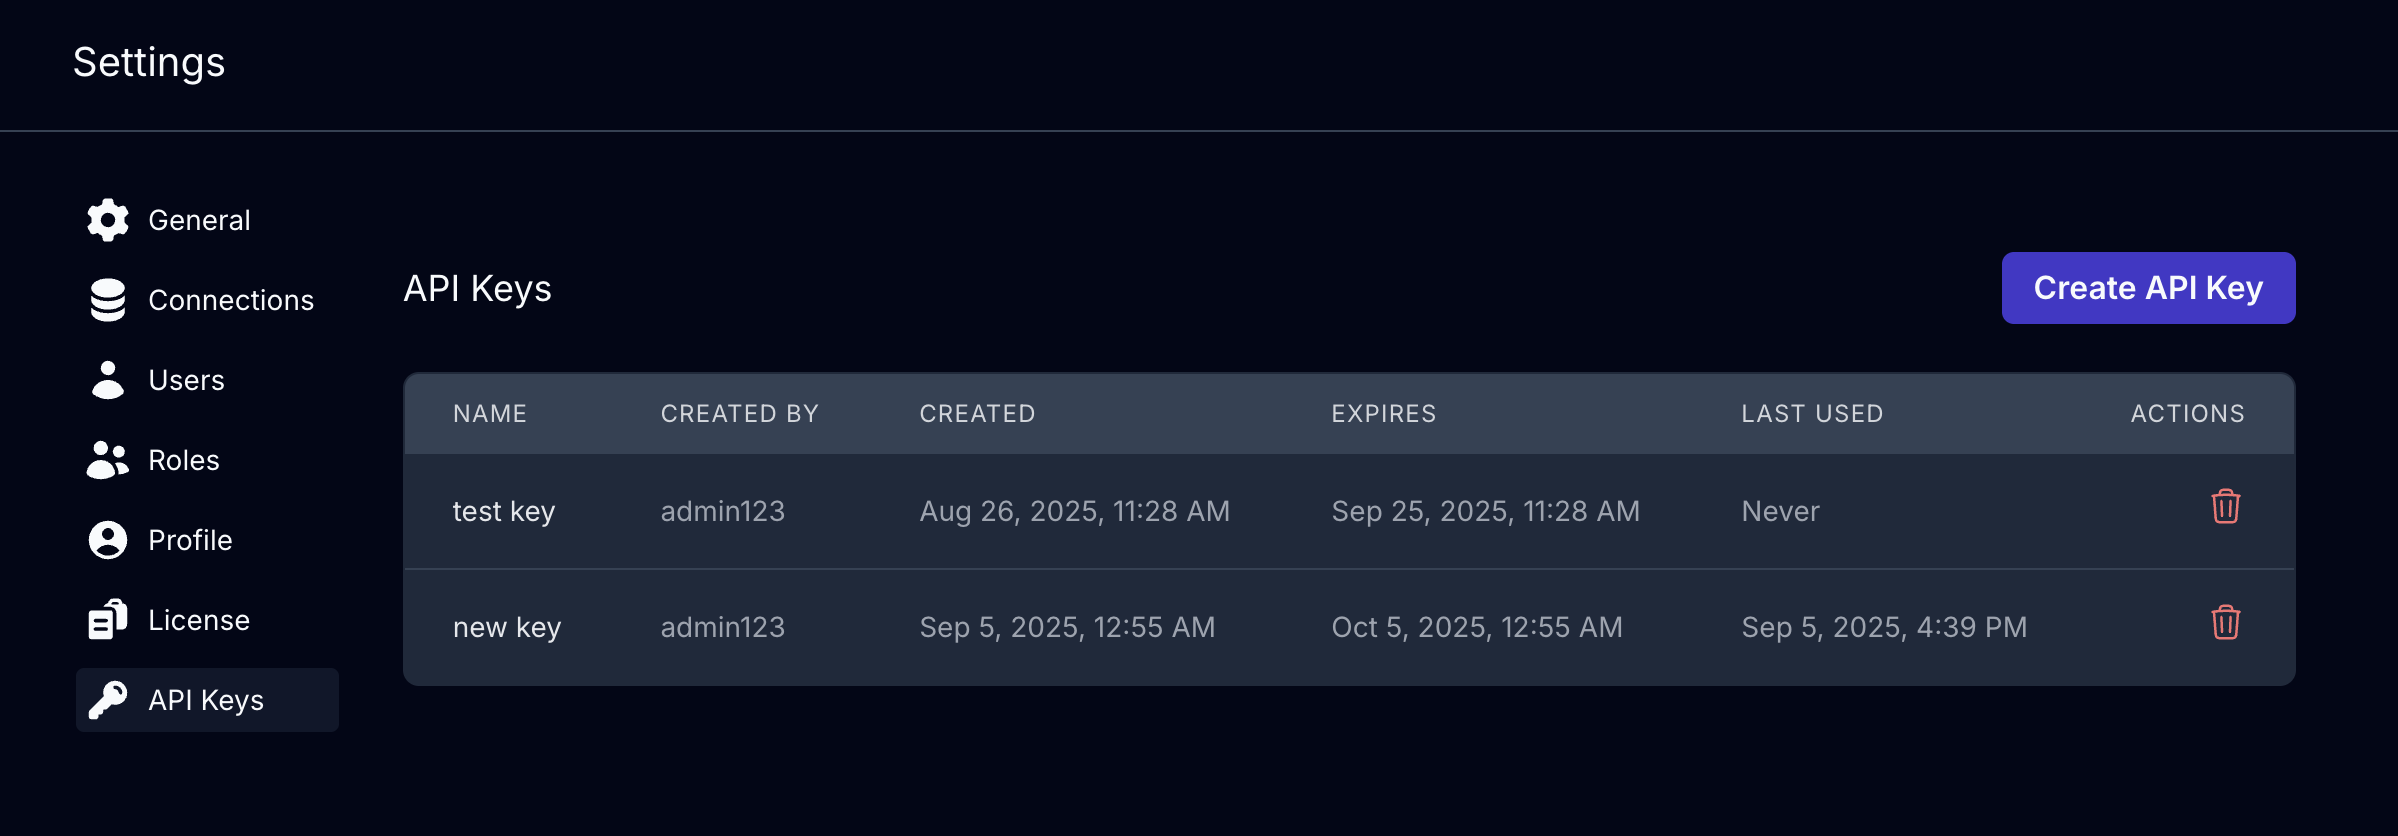 kviklet/kviklet
Pull Request-like Review/Approval flow for database queries. For compliant but smooth Engineering access to production.
 pingidentity/ldapsdk
UnboundID LDAP SDK for Java
 canyonroad/agentsh
Execution-Layer Security (ELS) for AI agents — policy-enforced shell with audit.
 xforcered/sqlrecon
A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.
 farenhytee/database-sentinel
Open-source security audits for Supabase: a read-only MCP server, a CLI agent and a Claude Skill. Finds RLS misconfigurations, exposed keys and risky…
 hikari-systems/slater
Low-memory graphdb with Bolt+tls support, at-rest encryption & vectors designed for local replica graph use cases.
 jakabakos/cve-2023-27524-apache-superset-auth-bypass-and-rce
Exploit for CVE-2023-27524 targeting Apache Superset auth bypass and RCE. Forges session cookies, enumerates databases/users, executes OS commands,…
 otterhacker/labs4u2self
Deployable AWS-hosted Active Directory pentest lab with domain controller and vulnerable MSSQL; practice S4U2Self abuse, SQL brute force, and RCE.
 repo4chu/cve-2026-78804_dolibarr_authenticated_sql_injection
The action responsible for setting the per-warehouse stock alert threshold (`seuil_stock_alerte`) accepts user-controlled input and later…