

CVE-2012-2122-Home-Lab
 netw0rk7/cve-2012-2122-home-lab
CVE-2012-2122 MySQL Authentication Bypass Home Lab
ctfdatabase-securityeducation+3
netw0rk7/cve-2012-2122-home-labCVE-2012-2122 MySQL Authentication Bypass Home Lab
 nanaao/cve-2021-29442-nacos-derby-rce-exp
Nacos Derby命令执行漏洞利用脚本
 gokul-krishnan-v-r/cve-2024-53900
Mongo Vulnub Lab...Try to Hack IT.....!
 r0oth3x49/ghauri
An advanced cross-platform tool that automates the process of detecting and exploiting SQL injection security flaws
 ron190/jsql-injection
Automated SQL injection detection and exploitation tool for extracting database information from web applications, supporting multiple injection…
 stampery/mongoaudit
🔥 A powerful MongoDB auditing and pentesting tool 🔥
 securebinary/firebaseexploiter
CLI tool to scan for and exploit insecure Firebase databases, supporting mass vulnerability scanning, custom JSON payload injection, and URI path…
 jas502n/redis-rce
remote code execute for redis4 and redis5
 netspi/sqlc2
SQLC2 is a PowerShell script for deploying and managing a command and control system that uses SQL Server as both the control server and the agent.
 synacktiv/cve-2024-43468
Exploit for CVE-2024-43468: unauthenticated SQL injection in Microsoft Configuration Manager Management Points, enabling arbitrary SQL execution and…
 codelatteid/carina
Webshell, Virtual Private Server (VPS) and cPanel Database
 adityaks/melee
Python-based tool to detect ransomware infections and malicious code in MySQL instances. Performs reconnaissance, user enumeration, and deep scans…
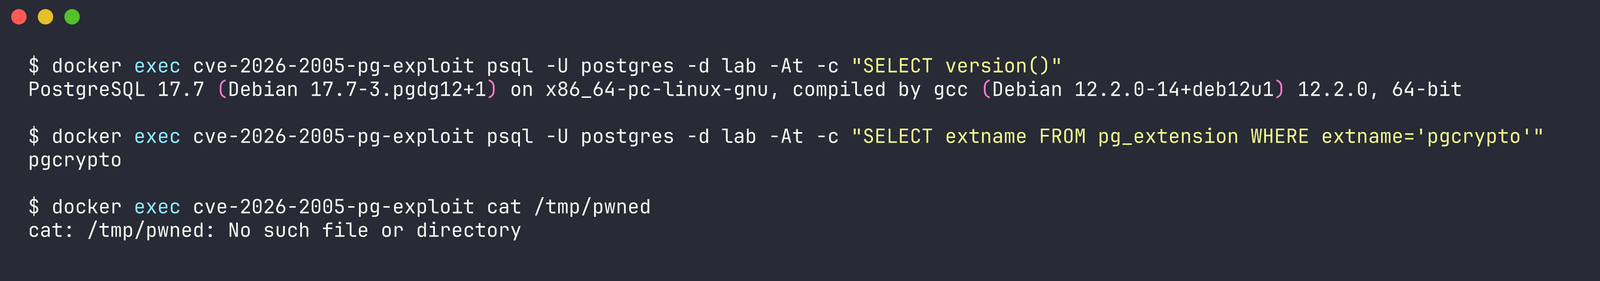 dinosn/cve-2026-2005
Exploit for CVE-2026-2005, a heap overflow in PostgreSQL's pgcrypto extension leading to remote code execution. Includes PoC generators, Docker lab,…
 tc4dy/cve-2026-58048-poc-exploit
👾 CVE-2026-58048 – cPanel Root SQL Execution Toolkit (CVSS 9.4) | Full Red/Blue Team Toolkit suite for unpatched cPanel & WHM 11.x. 2 tools: Safe…
 4minx/cve-2026-48842
Python PoC for CVE-2026-48842, a pre-auth SQL injection in Roundcube's virtuser_query plugin. Confirms the flaw via time-based differential and…
 qucklecrabik/cve-2026-23921
Proof-of-concept exploit for CVE-2026-23921, a time-based blind SQL injection in Zabbix API via the sortfield parameter, enabling data extraction…
 h4md153v63n/cve-2022-40032_simple-task-managing-system-v1.0-sql-injection-vulnerability-unauthenticated
CVE-2022-40032: Simple Task Managing System - 'login' and 'password' SQL Injection (Unauthenticated)
 secforce/cve-2008-1613
RedDot CMS versions 7.5 Build 7.5.0.48 and below full database enumeration exploit that takes advantage of a remote SQL injection vulnerability in…