
CVE-2024-22369
 oscerd/cve-2024-22369
CVE-2024-22369 Reproducer
database-securityeducationexploitation+3
42 years ago
oscerd/cve-2024-22369CVE-2024-22369 Reproducer
 boompig/cve-2016-6662
Exploit code for MySQL remote root code execution and privilege escalation (CVE-2016-6662), including Python and C implementations.

 mr-r00t11/cve-2024-34693
An input validation vulnerability in Apache Superset allows an authenticated attacker to create a MariaDB connection with local_infile enabled,…
 mateustesser/cve-2023-31719
Proof-of-concept exploit for CVE-2023-31719, demonstrating SQL injection in the FUXA web application's /api/signin endpoint via a crafted JSON…
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 wapiti-scanner/wapiti
Web vulnerability scanner written in Python3
 qianlijaingshan/milvus-auth-audit
Milvus 认证安全检测脚本:CVE-2025-64513 (sourceid后门) / CVE-2026-26190 (/expr弱token) / 内部端口53100
 pateldhyeyit/cve-2026-37149
CVE-2026-37149 - SQL Injection vulnerability in the scost parameter of search_products.php in…
 l0lsec/cve-2021-3262
CVE-2021-3262 - Blind SQL Injection in the editOEN parameter of TripSpark VEO Transportation / NovusEDU. Unauthenticated, internet-facing. Payloads,…
 holypryx/cve-2024-10140
SQL injection exploit script targeting CVE-2024-10140 in the /php/manage_supplier.php endpoint, enabling arbitrary SQL command injection via the id…
 huangyanqwq/cve-2023-49496_poc
Proof-of-concept exploit for CVE-2023-49496, demonstrating SQL injection in UCServer via the /login/wwx_corpInfo/ endpoint to extract sensitive…
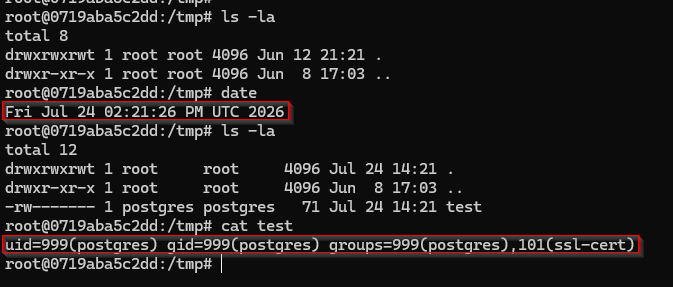 theliimbo/cve-2026-51992
Proof-of-concept and detailed writeup for CVE-2026-51992, an SQL injection vulnerability in ClickHouse PostgreSQL dictionaries allowing arbitrary…
 ubitquity/metabase-setup-endpoint-sqli-fix
Fixes unauthenticated SQL injection in a setup endpoint by replacing raw JDBC queries with ORM parameterization and constant-time token validation.
 shubham03007/cve-2025-28346
Code-projects Ticket Booking 1.0 is vulnerable to SQL Injection via the > Email parameter
 emad-almousa/cve-2020-2969
Proof-of-concept exploit for CVE-2020-2969 targeting unauthorized access to Oracle Database password hashes. Enables security researchers to test and…
 malvika-thakur/cve-2019-14234
POC-Django JSONField/HStoreField SQL Injection Vulnerability (CVE-2019-14234)