

NetExec
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
command-and-controldatabase-securityexploitation+14
5.8k
pennyw0rth/netexecPost-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
 kyos-public/keycloak-cve-2026-18963-hunt
Hunt for CVE-2026-18963 exploitation traces (Keycloak unauthenticated account takeover) in the Keycloak database
 abraxas/cve-2026-79752
CVE-2026-79752 disclosure pack for CakePHP 5.2.13 SQL injection via FunctionsBuilder::cast, with a Python PoC script and Docker lab for authorized…
 tc4dy/cve-2026-57821-poc-exploit
🔐 CVE-2026-57821 - Apache Fineract SQL Injection Toolkit 📚 Two Python scripts for authorized security testing: verifier.py (safe detection, no…
 sakthivel10q/cve-2025-14847
🛠 Exploit the CVE-2025-14847 vulnerability in MongoDB to disclose sensitive heap memory using a Python script that analyzes responses for new leaked…
 4minx/cve-2026-48842
Python PoC for CVE-2026-48842, a pre-auth SQL injection in Roundcube's virtuser_query plugin. Confirms the flaw via time-based differential and…
 karlvbiron/mad-cat
MAD-CAT (Meow Attack Data Corruption Automation Tool) is a comprehensive security tool designed to simulate data corruption attacks against multiple…
 0xsemz/magento-cve-2019-7139-sqli-poc
Python proof-of-concept exploit for CVE-2019-7139, an unauthenticated SQL injection in Magento's product_frontend_action endpoint, enumerating…
 qucklecrabik/cve-2026-23921
Proof-of-concept exploit for CVE-2026-23921, a time-based blind SQL injection in Zabbix API via the sortfield parameter, enabling data extraction…
 shentao83/news-8.6.0-cve-2026-8726-backport
Minimal security backport for CVE-2026-8726 in georgringer/news 8.6.0
 jhnhnck/cve-2019-9193
PoC tool designed to exploit an authenticated Remote Code Execution (RCE) vulnerability in certain versions of PostgreSQL (9.3 - 11.7)
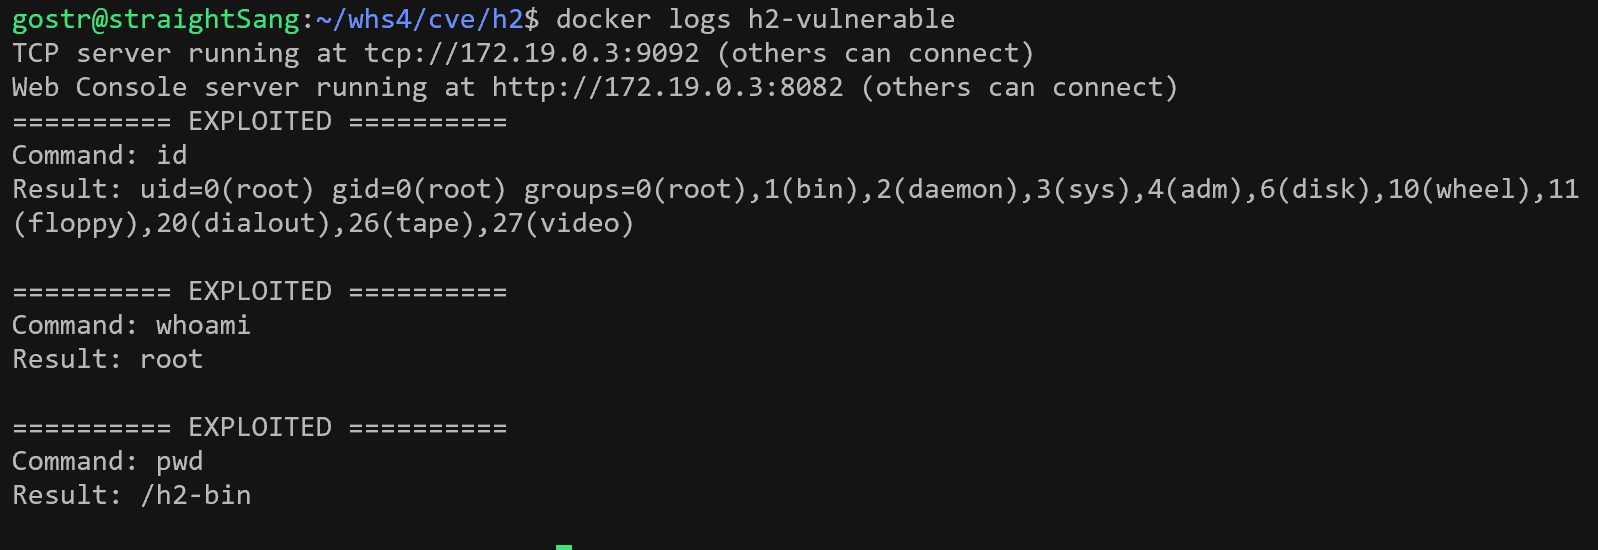 straightsang/h2-database-cve-2022-23221
vulhub/H2-database/CVE-2022-23221
 repo4chu/cve-2026-78804_dolibarr_authenticated_sql_injection
The action responsible for setting the per-warehouse stock alert threshold (`seuil_stock_alerte`) accepts user-controlled input and later…
 ivanesk315/cve-2023-25157
Local GeoServer/PostGIS lab reproducing OGC Filter SQL injection (CVE-2023-25157/25158) with vulnerable, patched, and mitigated A/B test modes.
 romain-deperne/cve-2026-41490
Detailed CVE-2026-41490 disclosure with PoC demonstrating unauthenticated SQL injection in Dagster database I/O managers via dynamic partition keys,…
 romain-deperne/cve-2026-33980
Proof-of-concept exploit for KQL injection in adx-mcp-server via the table_name parameter, enabling data exfiltration and destructive commands in…