
cve-search
 cve-search/cve-search
Local CVE/CPE vulnerability database with search, ranking, web interface, and API for offline vulnerability analysis and management.
database-securityinformation-gatheringioc-management+4
2.6k
cve-search/cve-searchLocal CVE/CPE vulnerability database with search, ranking, web interface, and API for offline vulnerability analysis and management.
 george0papasotiriou/cve-2026-21004-sqlite-fts3-match-infoleak-via-query-crafting
Proof-of-concept exploit for CVE-2026-21004: uses crafted SQLite FTS3/4 MATCH prefix queries as a blind oracle to recover indexed secret data…
 0xdak/cve-2026-69083_exploit
Python PoC for CVE-2026-69083, an unauthenticated SQL injection in SiYuan's asset-content search endpoint. Supports REGEXP breakout and raw SQL…
 ccchme/cve-2018-1058
Reproducible Docker-based demonstration of CVE-2018-1058 PostgreSQL privilege escalation via uncontrolled search path, with vulnerable and patched…
 smarttfoxx/cve-2025-67261
Abacre Retail Point of Sale 14.0.0.396 is vulnerable to content-based blind SQL injection. The vulnerability exists in the Search function of the…
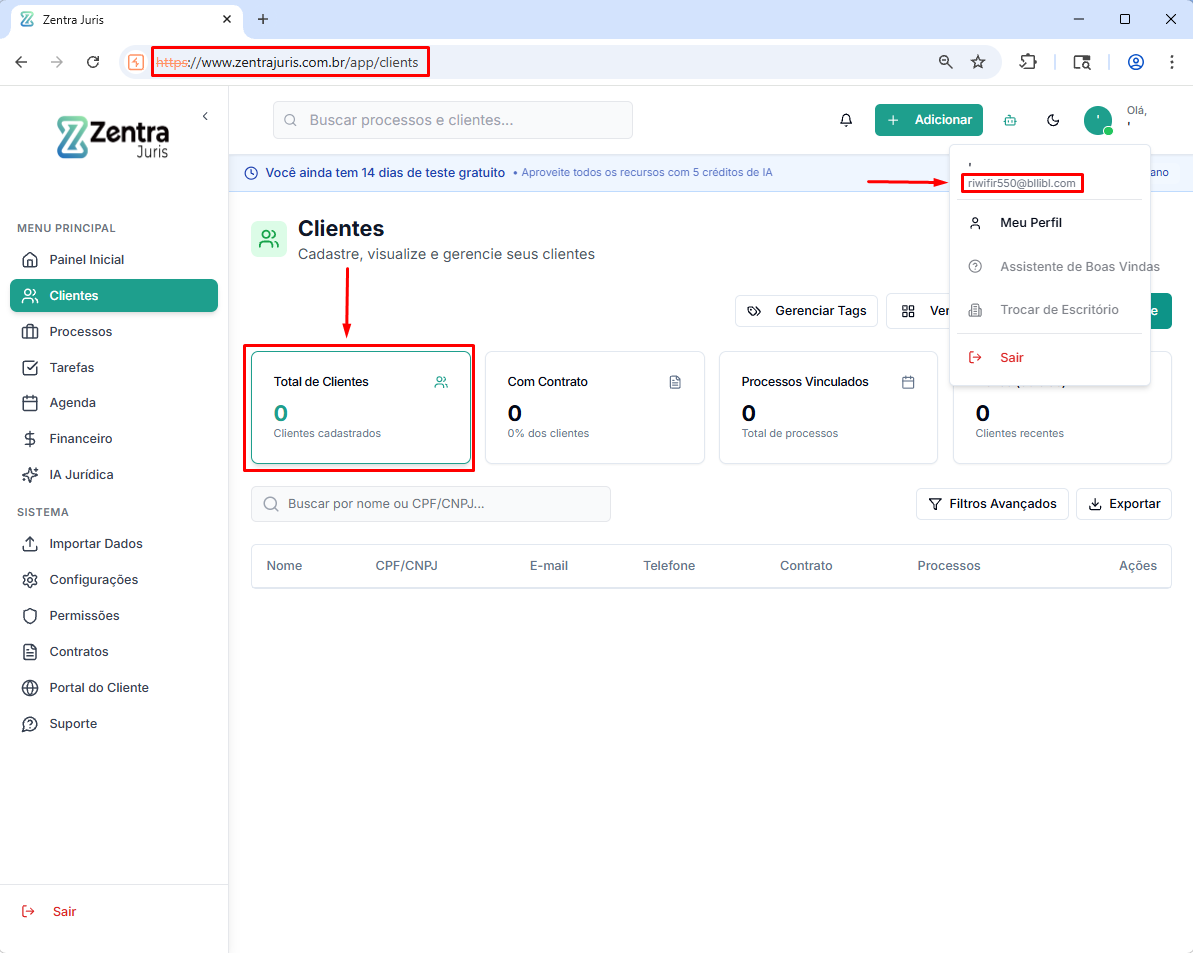 rrespxwnss/cve-2025-63572
A SQL injection vulnerability was discovered in the endpoint responsible for searching for platform clients. User input sent to the search parameter…
 redopsx/cve-2025-63943
SQL Injection vulnerability discovered in Grocery Store Management System 1.0
 nu11secur1ty/complete-google-dorks
Curated collection of Google dork queries for advanced search engine reconnaissance, uncovering exposed databases, configuration files, admin panels,…
 randomrobbiebf/cve-2024-9796
WordPress WP-Advanced-Search <= 3.3.9 - Unauthenticated SQL Injection
 ofirhamam/oracleotm
Python tool for exploiting CVE-2021-35616
 citcheese/odbparser
OSINT tool to search, parse and dump only the open Elasticsearch and MongoDB directories that have the data you care about exposing
 jimywork/stretcher
Tool designed to help identify open Elasticsearch servers that are exposing sensitive information