

MSSqlPwner
 scorpioneslabs/mssqlpwner
Advanced MSSQL penetration testing tool for lateral movement, command execution, NTLM relay, and brute-force attacks via linked servers and multiple…
authenticationdatabase-securityexploitation+5
469
scorpioneslabs/mssqlpwnerAdvanced MSSQL penetration testing tool for lateral movement, command execution, NTLM relay, and brute-force attacks via linked servers and multiple…
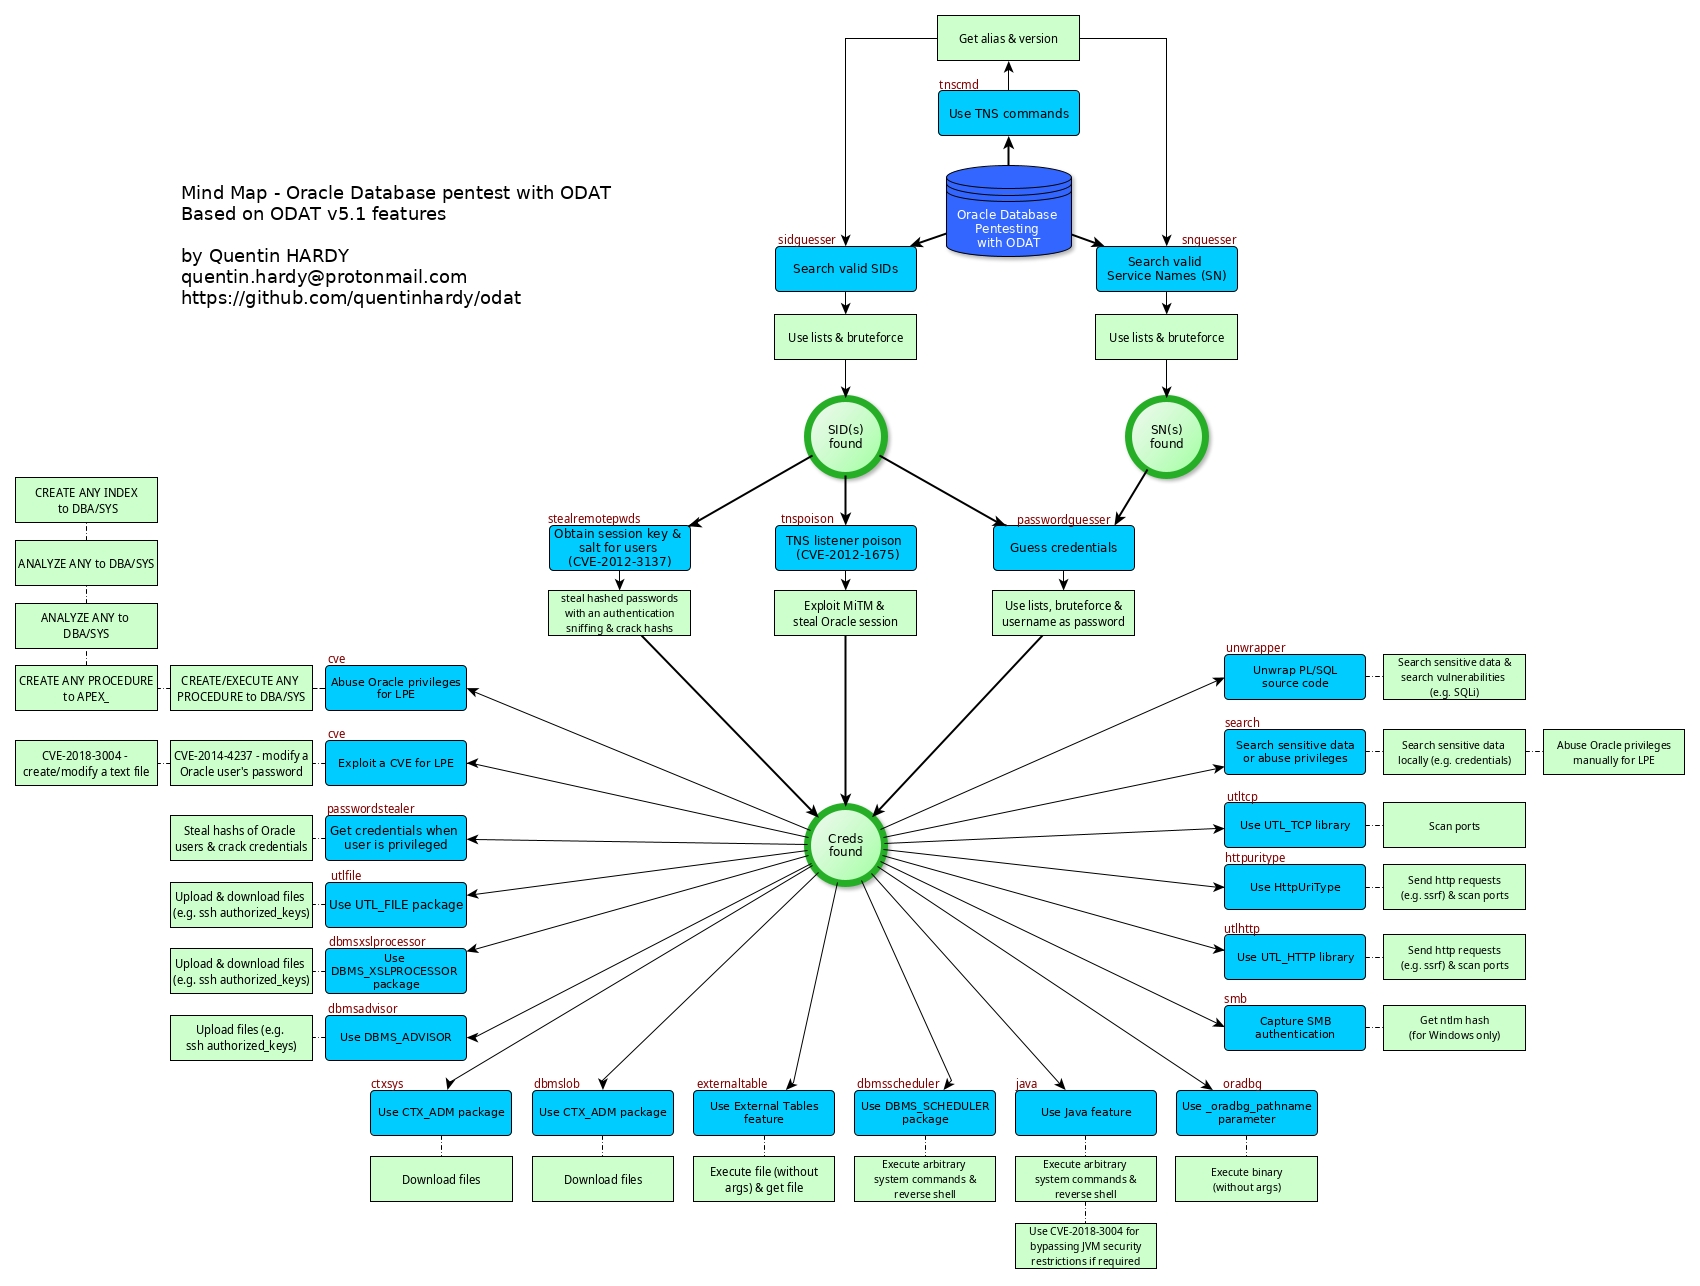 quentinhardy/odat
Penetration testing tool for Oracle Databases that discovers valid SIDs, brute-forces credentials, escalates privileges to DBA, executes system…
 xiaoxiaoranxxx/cve-2025-70829
An information exposure vulnerability in Datart v1.0.0-rc.3 allows authenticated attackers to access sensitive data via a custom H2 JDBC connection…
 mdriaz009/cve-2025-21574-exploit
Black-box exploit for CVE-2025-21574 targeting MySQL servers. Automates credential brute-forcing, anonymous access attempts, and triggers server…
 lisa-2905/cve-2024-56429
Exploit for CVE-2024-56429 demonstrating extraction of Apache Derby database boot password from iLabClient source code, enabling local database…
 m8sec/enumdb
Relational database brute force and post exploitation tool for MySQL and MSSQL
 emad-almousa/cve-2020-2969
Proof-of-concept exploit for CVE-2020-2969 targeting unauthorized access to Oracle Database password hashes. Enables security researchers to test and…
 h4md153v63n/cve-2022-40032_simple-task-managing-system-v1.0-sql-injection-vulnerability-unauthenticated
CVE-2022-40032: Simple Task Managing System - 'login' and 'password' SQL Injection (Unauthenticated)
 randomrobbiebf/postgres-bruteforcer
This tool takes a list of default creds and tests it against a postgresql server and logs any that work and the databases it has access to.
 initroot/wodat
Windows Oracle Database Attack Toolkit
 lorenzotullini/influxdb-exploit-cve-2019-20933
InfluxDB CVE-2019-20933 vulnerability exploit