

semgrep
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
api-securityapi-security-testingcode-analysis+9
16.9k13h 13m ago
semgrep/semgrepLightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 checkmarx/kics
Static analysis scanner for infrastructure-as-code that detects security vulnerabilities, compliance violations, and misconfigurations across…
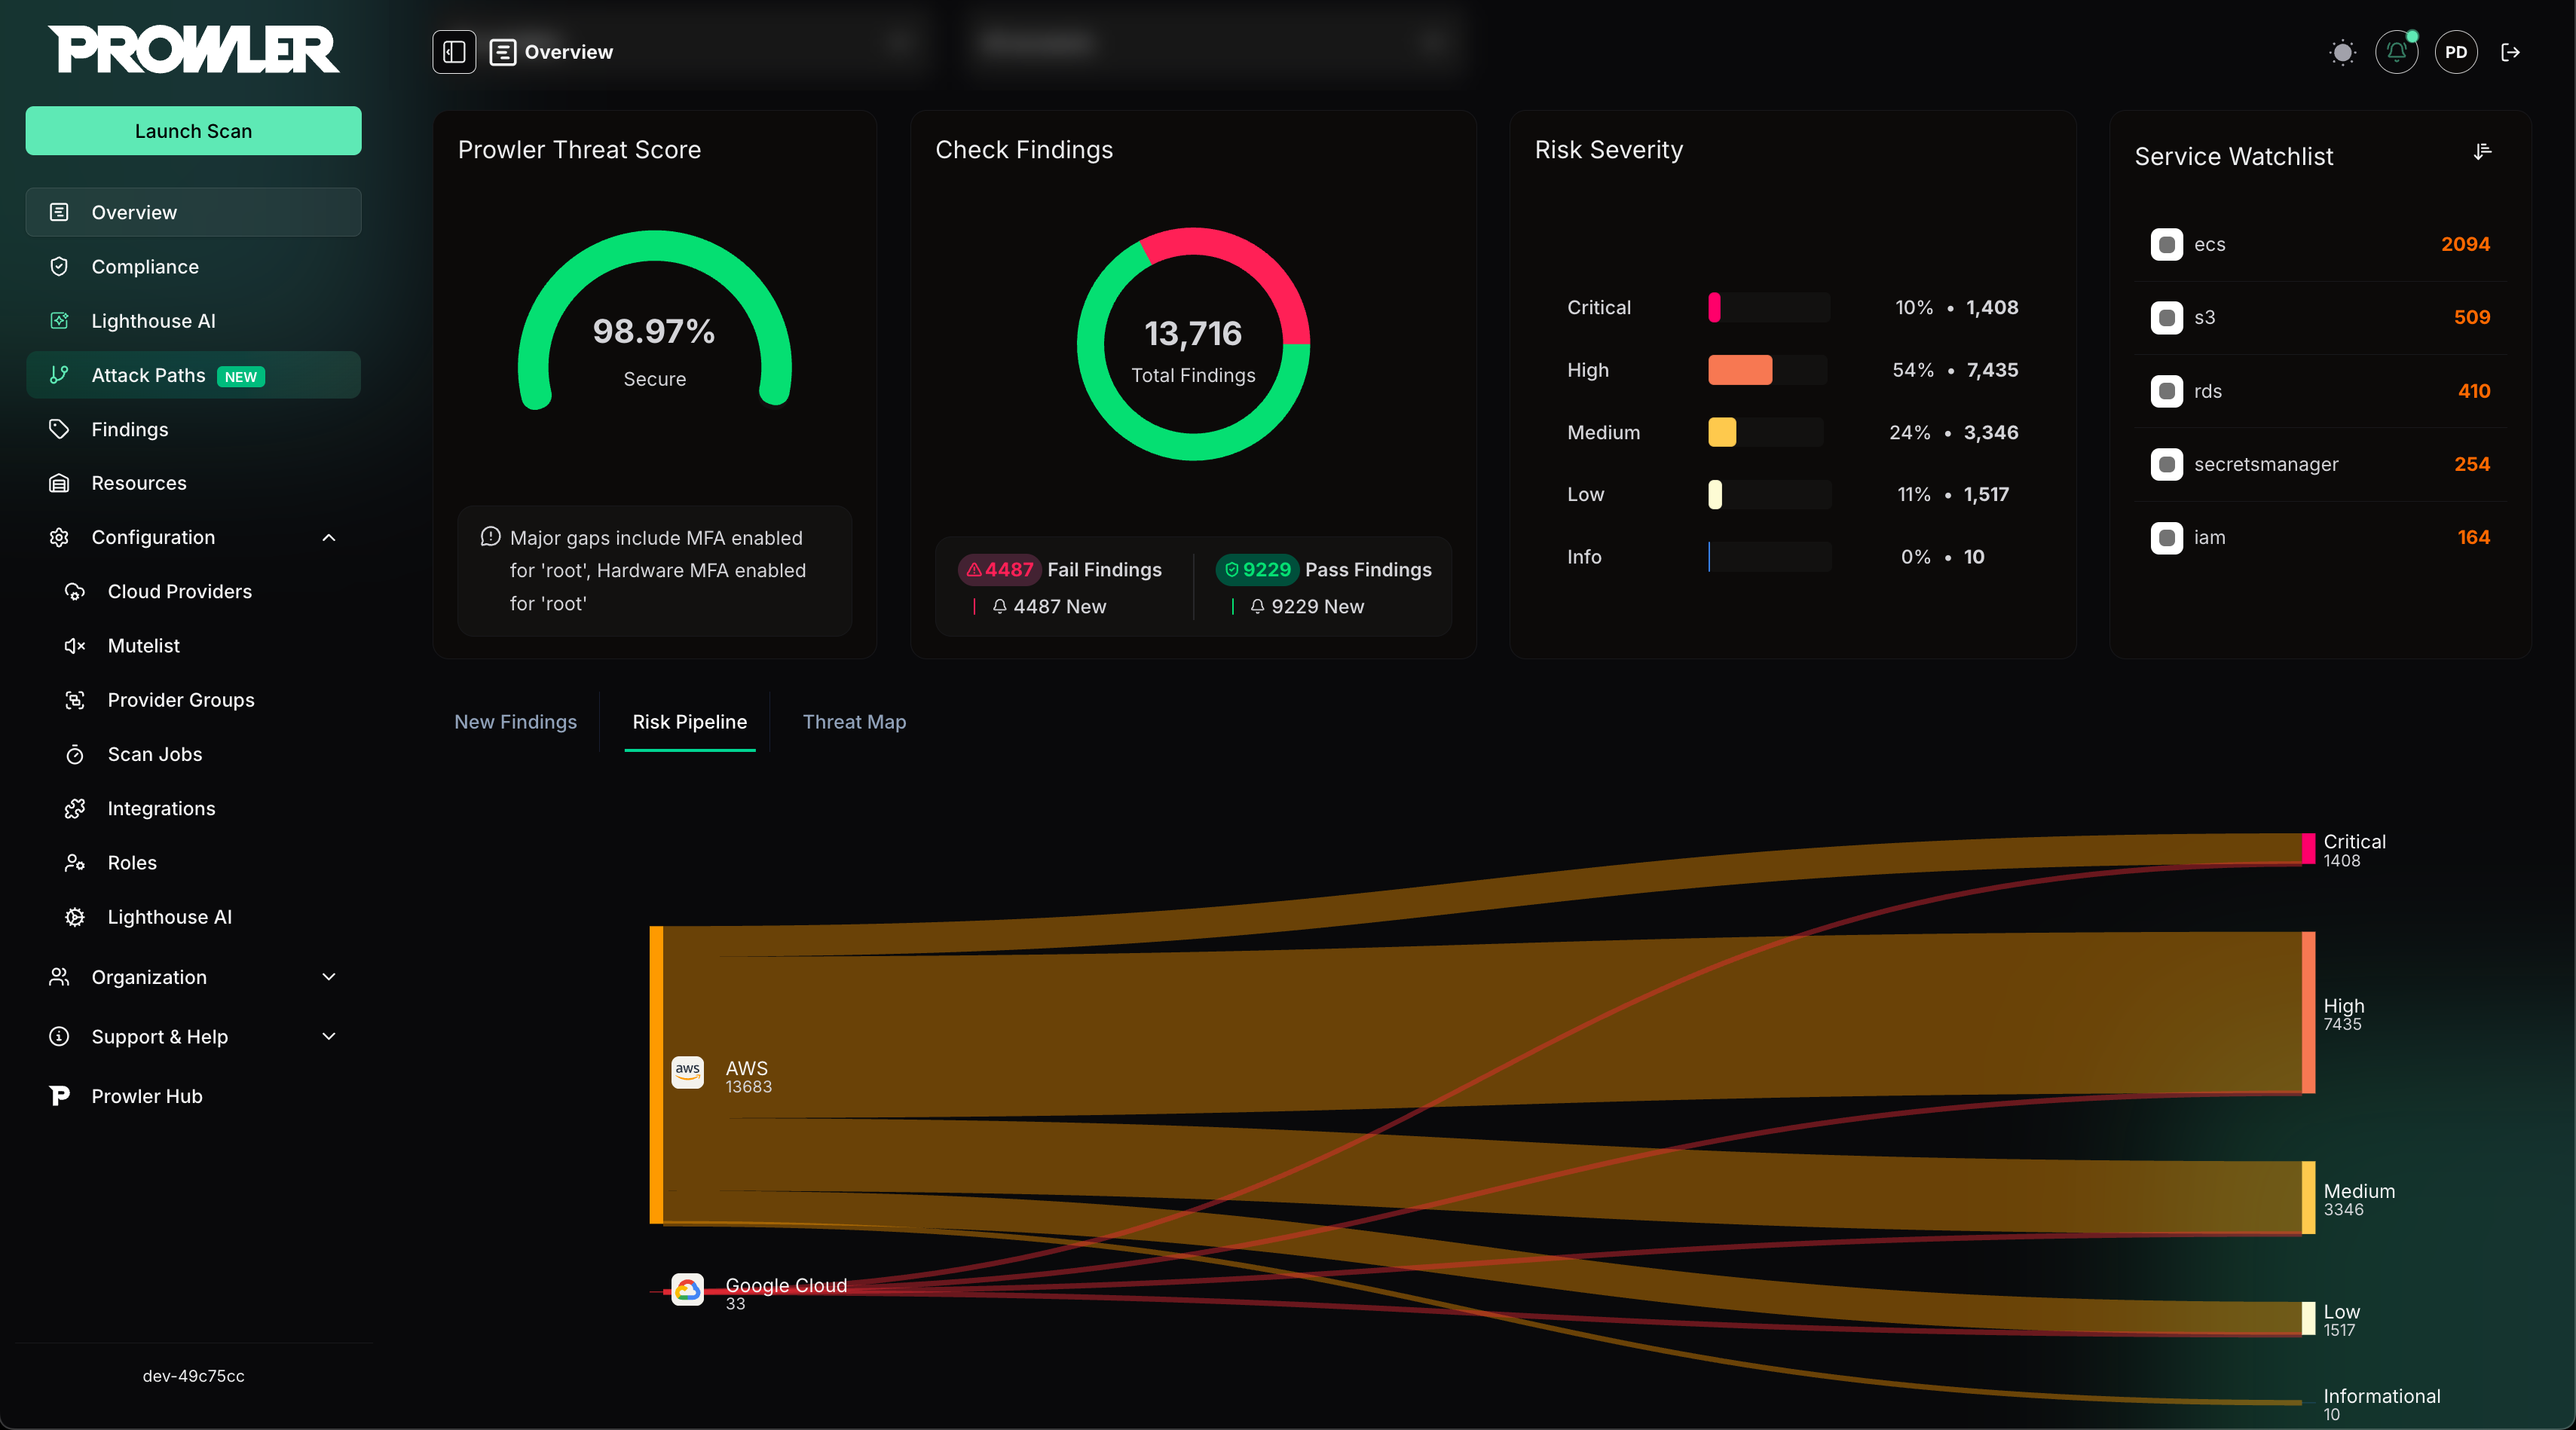 prowler-cloud/prowler
Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…
 pedrocruz2202/mongobleed-scanner
🔍 Scan for MongoDB vulnerabilities with MongoBleed, a high-performance tool for detecting CVE-2025-14847 across large networks quickly and…
 sakthivel10q/cve-2025-14847
🛠 Exploit the CVE-2025-14847 vulnerability in MongoDB to disclose sensitive heap memory using a Python script that analyzes responses for new leaked…
 wapiti-scanner/wapiti
Web vulnerability scanner written in Python3
 gchq/cyberchef
The Cyber Swiss Army Knife - a web app for encryption, encoding, compression and data analysis
 fortra/impacket
Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…
 pranshuchittora/simvyn
Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI
 abraxas/cve-2026-22599
Python PoC and Docker lab for CVE-2026-22599, an authenticated SQL injection in Strapi's Content-Type Builder write API via Knex raw defaultTo.
 abraxas/cve-2026-77635
Disclosure pack and Python PoC for CVE-2026-77635, an unauthenticated SQL injection in CakePHP's jsonValue() with PostgresDriver, including a…
 4minx/cve-2026-48842
Python PoC for CVE-2026-48842, a pre-auth SQL injection in Roundcube's virtuser_query plugin. Confirms the flaw via time-based differential and…
 0xsemz/magento-cve-2019-7139-sqli-poc
Python proof-of-concept exploit for CVE-2019-7139, an unauthenticated SQL injection in Magento's product_frontend_action endpoint, enumerating…
 qucklecrabik/cve-2026-23921
Proof-of-concept exploit for CVE-2026-23921, a time-based blind SQL injection in Zabbix API via the sortfield parameter, enabling data extraction…
 sqlancer/sqlancer
Automated testing to find logic and performance bugs in database systems
 shentao83/news-8.6.0-cve-2026-8726-backport
Minimal security backport for CVE-2026-8726 in georgringer/news 8.6.0