

semgrep
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
api-securityapi-security-testingcode-analysis+9
17.3k12h 13m ago
semgrep/semgrepLightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 pingidentity/ldapsdk
UnboundID LDAP SDK for Java
 tc4dy/cve-2026-57821-poc-exploit
🔐 CVE-2026-57821 - Apache Fineract SQL Injection Toolkit 📚 Two Python scripts for authorized security testing: verifier.py (safe detection, no…
 abraxas/cakephp-window-sqli
CakePHP 5.4.2 - High - Remote - SQLi - WindowExpression range/frame offsets spliced into SQL
 abraxas/sqlite-xfer-auth
SQLite 3.53.4 - High - Local - Privilege leftover - INSERT SELECT xfer skips source READ
 shentao83/news-8.6.0-cve-2026-8726-backport
Minimal security backport for CVE-2026-8726 in georgringer/news 8.6.0
 romain-deperne/cve-2026-33980
Proof-of-concept exploit for KQL injection in adx-mcp-server via the table_name parameter, enabling data exfiltration and destructive commands in…
 romain-deperne/cve-2026-32247
Proof-of-concept for CVE-2026-32247, a Cypher injection in graphiti-core via unsanitized node_labels, demonstrating data exfiltration and graph…
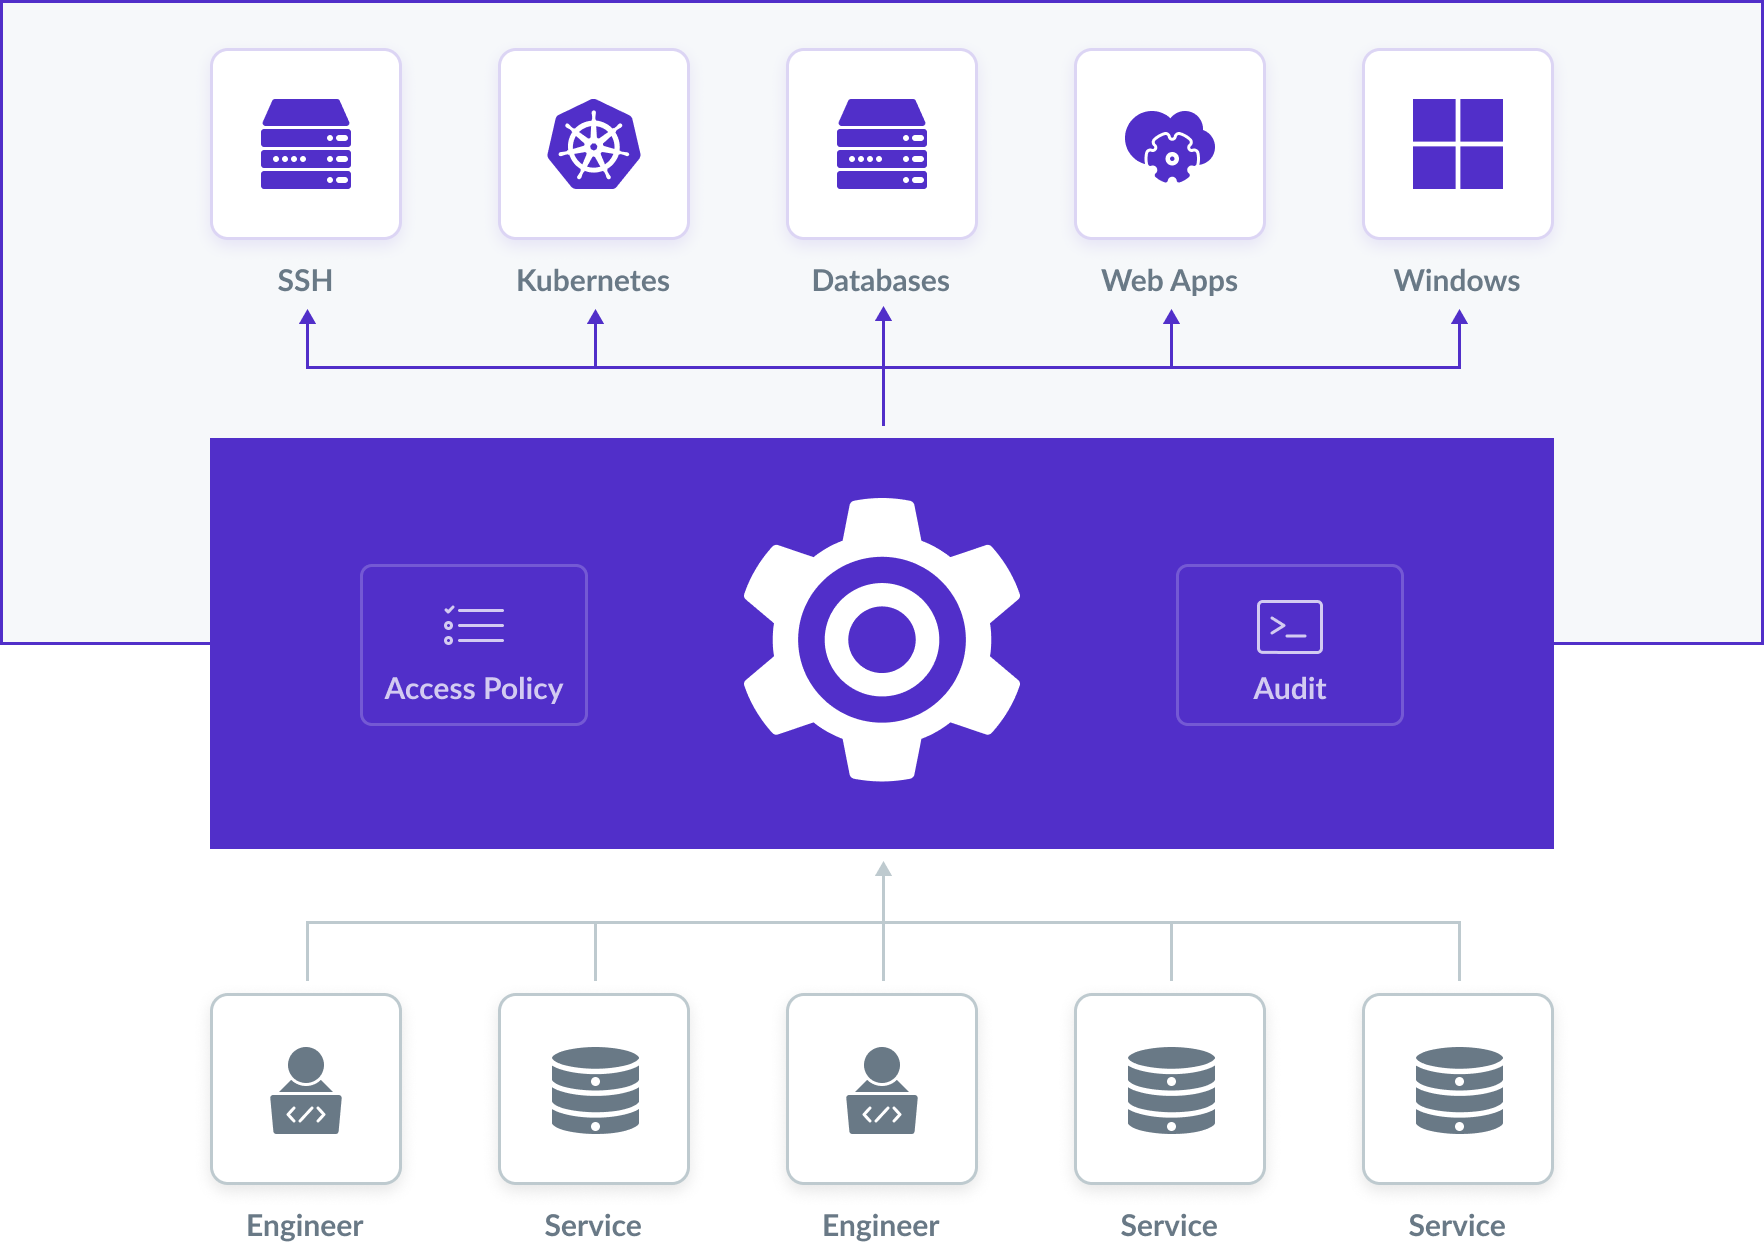 gravitational/teleport
The easiest, and most secure way to access and protect all of your infrastructure.
 20000419/cve-2026-39113
Advisory and AddressSanitizer reproducer for a SQLite SQLAR heap-buffer-overflow triggered by a crafted SZ value causing truncated allocation and…
 eqstlab/cve-2026-30951
Sequelize JSON Cast SQL Injection
 adarshthakur14777-cyber/cve-2026-60137
wpsqli full SQLi extractor + dumper for CVE-2026-60137
 biitts/cve-2026-52887-nocobase-sqli-rce
CVE-2026-52887 — NocoBase SQL injection -> PostgreSQL-superuser RCE (myInAppChannels:list filter, CVSS 10.0). Author PoC + source analysis + docker…
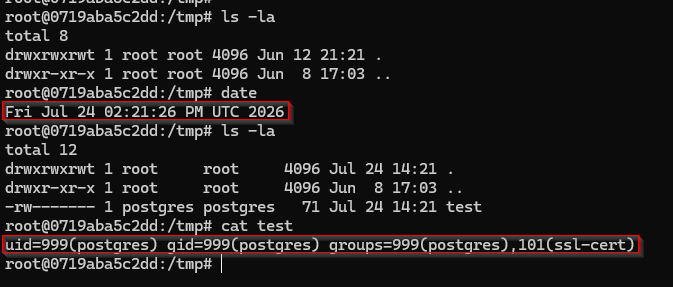 theliimbo/cve-2026-51992
Proof-of-concept and detailed writeup for CVE-2026-51992, an SQL injection vulnerability in ClickHouse PostgreSQL dictionaries allowing arbitrary…
 cerberusmrxi/cve-2026-44680-mikroorm-sql-injection-exploit-framework
PoC tool for CVE-2026-44680 affecting MikroORM ≤7.0.13. Exploits JSON path injection to extract database contents via UNION-based attacks. Features…
 sqlsure/sqlsure
Semantic inspector for SQL — catches fan-out double-counting, additivity violations, wrong join keys, and policy breaches before the query runs.…