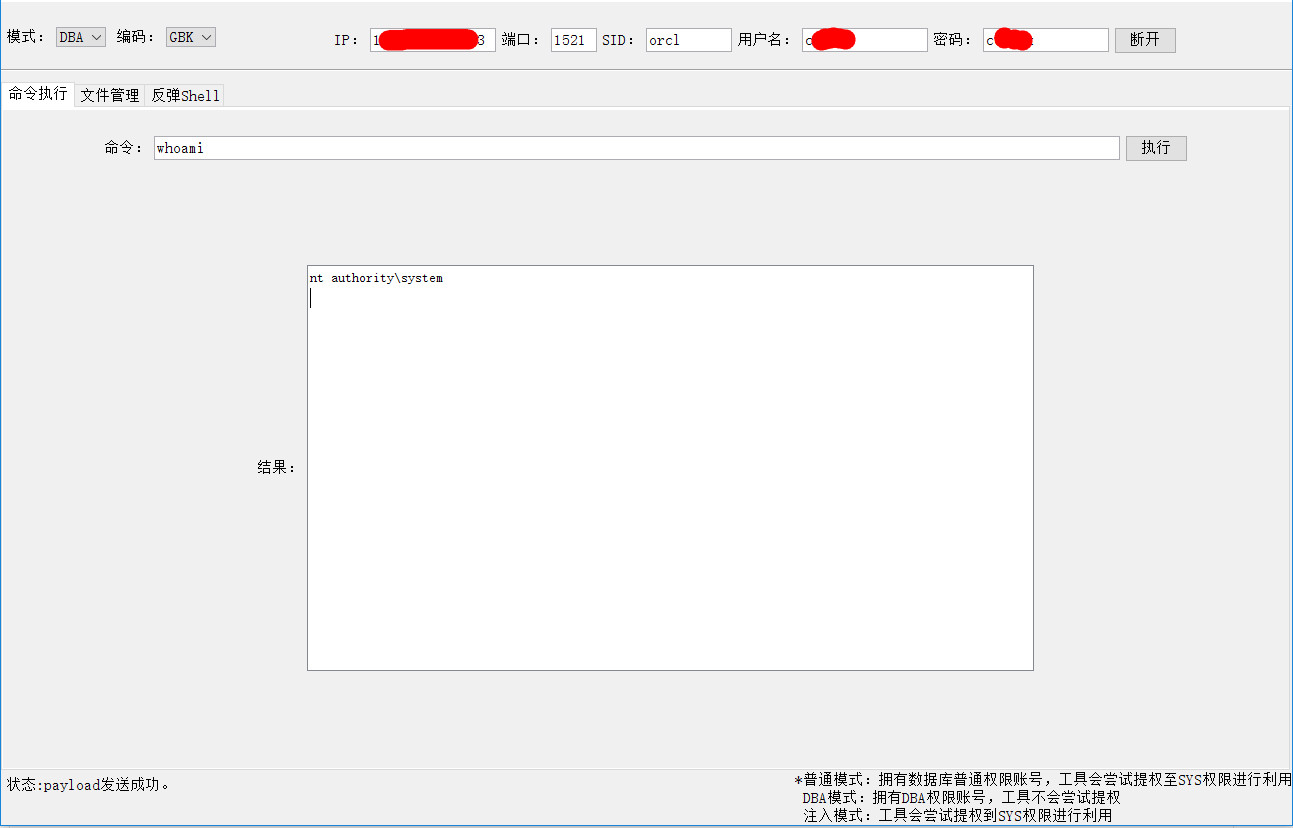
nmap
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
bluetooth-securitydatabase-securitydata-exfiltration+18
13.7k
nmap/nmapHigh-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 pgedge/pgedge-anonymizer
An anonymizer tool for replacing PII and similar data in dev/test databases copied from production
 repo4chu/cve-2026-78804_dolibarr_authenticated_sql_injection
The action responsible for setting the per-warehouse stock alert threshold (`seuil_stock_alerte`) accepts user-controlled input and later…
 goldendivider/cve-2026-6471-postgres-logical-decoding-dlopen
Proof-of-concept exploit for CVE-2026-6471, demonstrating privilege escalation in PostgreSQL via logical decoding dlopen to achieve arbitrary code…
 wattocyber/custom-oscp-tooling
OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…
 ashrafdev/mysql-remote-root-code-execution
0ldSQL_MySQL_RCE_exploit.py (ver. 1.0) (CVE-2016-6662) MySQL Remote Root Code Execution / Privesc PoC Exploit For testing purposes only. Do no…
 biitts/cve-2026-54350-budibase-nosql-injection
PoC for CVE-2026-54350 — Budibase unauthenticated NoSQL operator injection (CVSS 10.0). Read/mass-write any document collection via a PUBLIC query.
 al1ex/cve-2019-12086
jackson unserialize
 hann1bl3l3ct3r/cve-2026-11349
Modern Events Calendar Lite <= 7.33.0 — Unauthenticated SQL Injection
 xiaoxiaoranxxx/cve-2025-70829
An information exposure vulnerability in Datart v1.0.0-rc.3 allows authenticated attackers to access sensitive data via a custom H2 JDBC connection…
 mrlihd/cve-2024-57521-sql-injection-poc
Blind SQL injection proof-of-concept exploit for RuoYi v4.7.9, bypassing CVE-2024-42900 filter to dump databases via authenticated boolean-based…
 superswan/cve-2024-55963
CVE-2024-55963, allows unauthenticated remote code execution on Appsmith Enterprise platform due to a misconfigured PostgreSQL database included by…
 al1ex/cve-2021-27928
CVE-2021-27928 MariaDB/MySQL-'wsrep provider' 命令注入漏洞
 tarunkant/gopherus
This tool generates gopher link for exploiting SSRF and gaining RCE in various servers
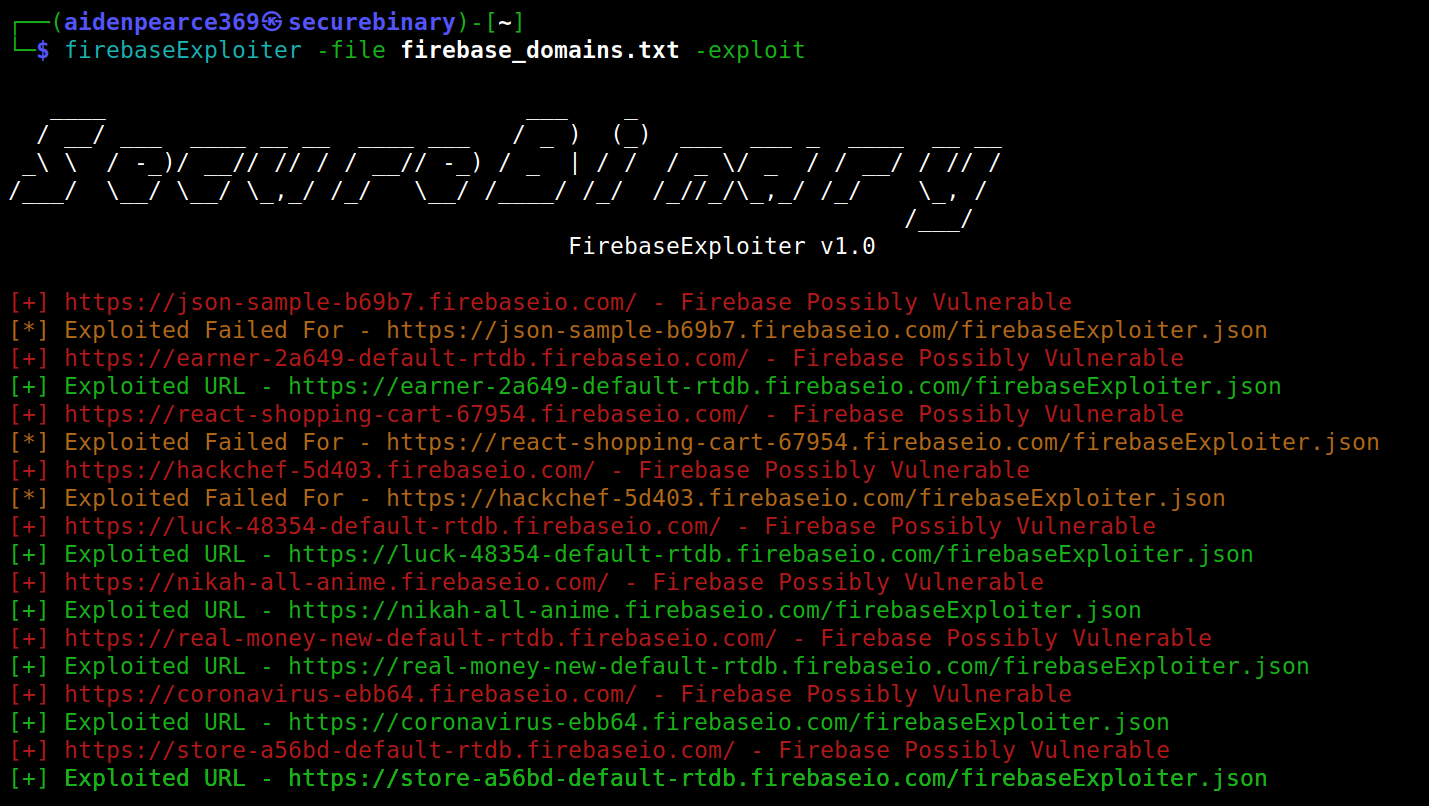 securebinary/firebaseexploiter
CLI tool to scan for and exploit insecure Firebase databases, supporting mass vulnerability scanning, custom JSON payload injection, and URI path…
 b4kesn4ke/cve-2019-9193
CVE-2019–9193 - PostgreSQL 9.3-12.3 Authenticated Remote Code Execution
 shamo0/cve-2021-27928-poc
CVE-2021-27928-POC