CVE-2026-78804_Dolibarr_authenticated_SQL_injection

The action responsible for setting the per-warehouse stock alert threshold (`seuil_stock_alerte`) accepts user-controlled input and later…

The action responsible for setting the per-warehouse stock alert threshold (`seuil_stock_alerte`) accepts user-controlled input and later…

Python PoC exploiting time-based blind SQLi in Nagios XI to extract database contents, with multithreaded binary-search extraction and CLI…

Scanner: CVE-2026-9082 Drupal PostgreSQL SQLi via JSON:API — Python scanner for unauthenticated SQLi leading to RCE (CISA KEV)

wpsqli full SQLi extractor + dumper for CVE-2026-60137

This tool generates gopher link for exploiting SSRF and gaining RCE in various servers

sscms database decrypt

A security assessment tool for Hitachi Vantara's Pentaho Business Analytics platform.

The easiest, and most secure way to access and protect all of your infrastructure.

PoC tool for CVE-2026-44680 affecting MikroORM ≤7.0.13. Exploits JSON path injection to extract database contents via UNION-based attacks. Features…

ISR-sqlget It's a blind SQL injection tool developed in Perl.

Execution-Layer Security (ELS) for AI agents — policy-enforced shell with audit.

chusa - 注射 - the new generation of sqlmap

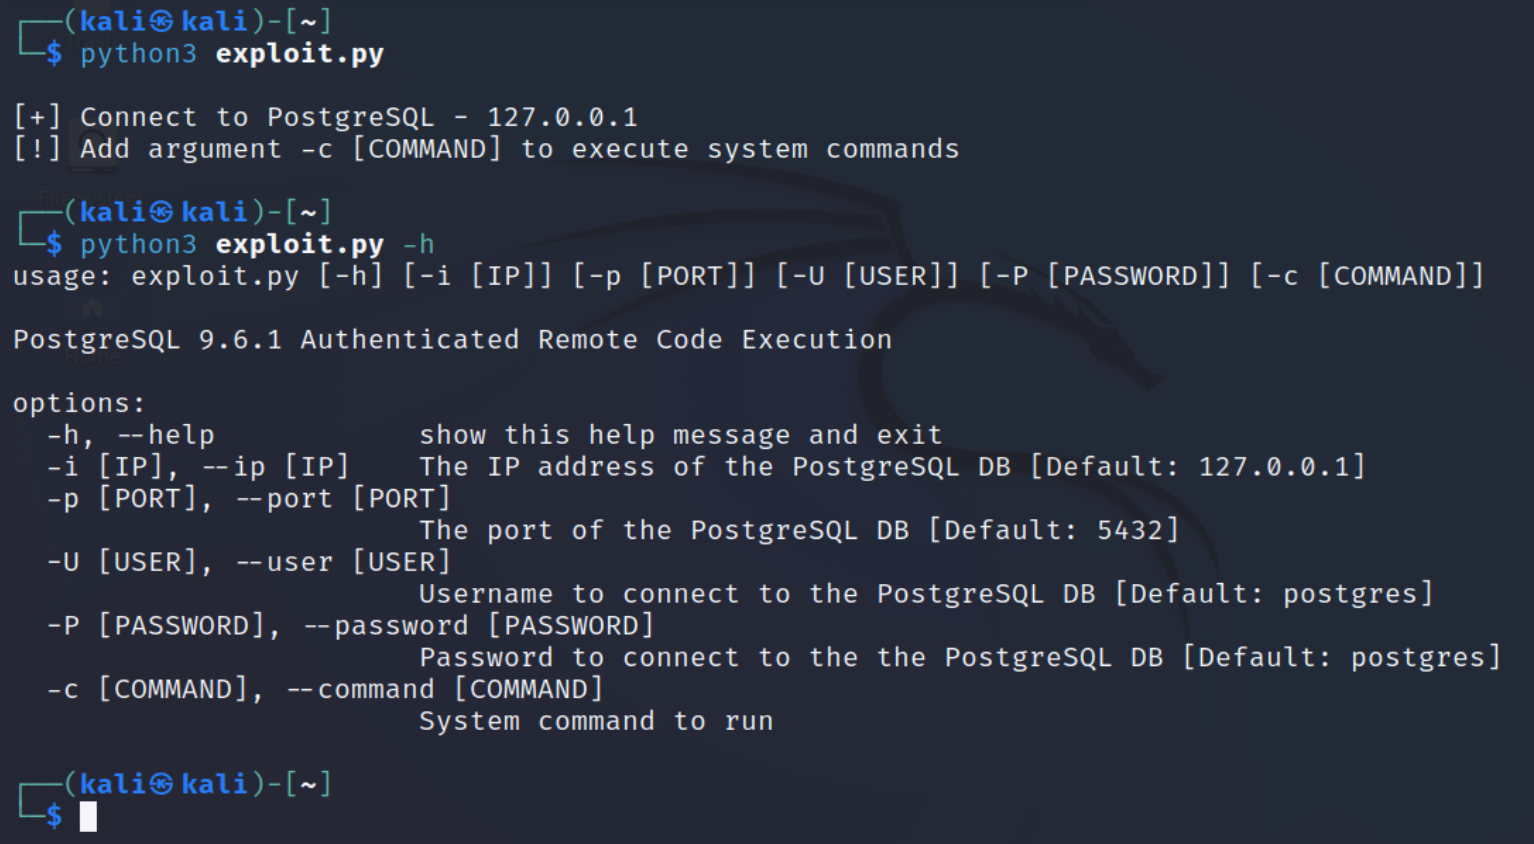
Proof-of-concept exploit for authenticated remote code execution in PostgreSQL 9.6.1, demonstrating how misconfigured databases can be leveraged for…

Advanced PostgreSQL database enumeration tool exploiting CVE-2024-39309 in Parse Server - Comprehensive SQL injection exploitation for security…

Python tool for exploiting CVE-2021-35616

UnboundID LDAP SDK for Java

Claude Skill that audits your projects for RLS misconfigurations, exposed keys, auth bypasses, and storage vulnerabilities. 27 anti-patterns sourced…

CVE-2016-4999