
CVE-2026-11115-Database-Connection-String-Injection-via-Env-Variable
 george0papasotiriou/cve-2026-11115-database-connection-string-injection-via-env-variable
database-securityeducationexploitation+3
george0papasotiriou/cve-2026-11115-database-connection-string-injection-via-env-variable rootsecdev/microburstsecretshunter
Scans exported Azure domain dumps for plaintext passwords, connection strings, storage keys, and other secrets; generates redacted CSV/HTML reports…
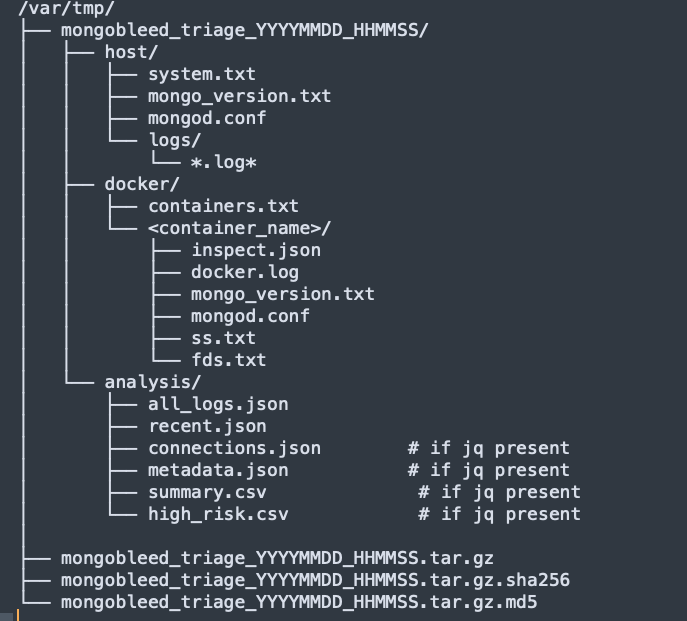 jemhadar/mongobleed-dfir-triage-script-cve-2025-14847
The script focuses on safe artifact acquisition first, followed by optional on-host analysis, and produces a portable, hashed forensic archive…
 mr-r00t11/cve-2024-34693
An input validation vulnerability in Apache Superset allows an authenticated attacker to create a MariaDB connection with local_infile enabled,…
 mr-r00t11/cve-2024-4879
CVE-2024-4879.py is a Python script designed to detect specific vulnerabilities in ServiceNow instances and dump database connection details if the…
 xiaoxiaoranxxx/cve-2025-70828
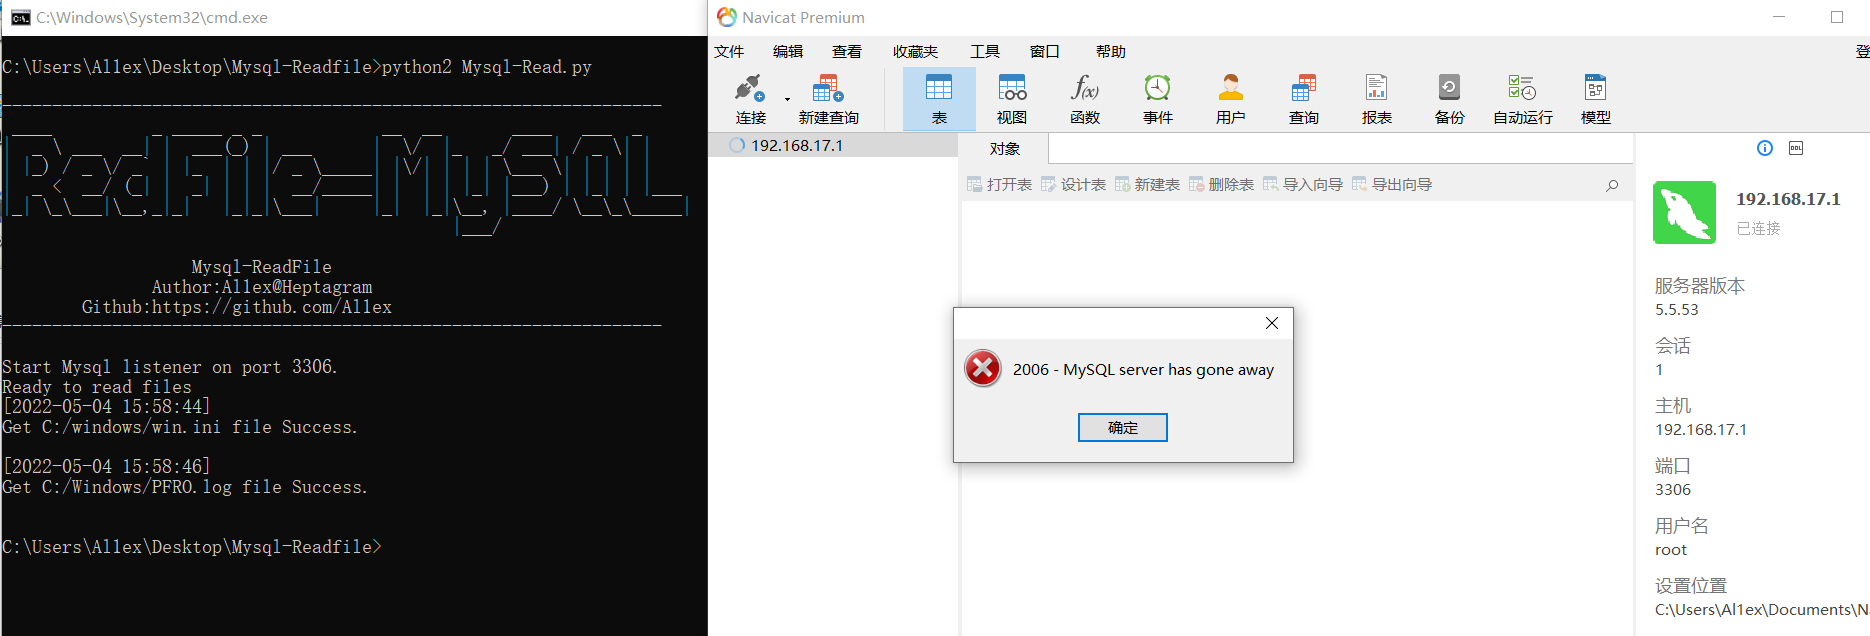
Datart v1.0.0-rc.3 JDBC Connection String Injection Leading to Arbitrary File Read
 lisa-2905/cve-2024-56429
Exploit for CVE-2024-56429 demonstrating extraction of Apache Derby database boot password from iLabClient source code, enabling local database…
 mbadanoiu/cve-2024-34693
CVE-2024-34693: Server Arbitrary File Read in Apache Superset
 shanika04/cp30_xxe_partial_fix
version between CVE-2018-20433 and CVE-2019-5427
 xiaoxiaoranxxx/cve-2025-70829
An information exposure vulnerability in Datart v1.0.0-rc.3 allows authenticated attackers to access sensitive data via a custom H2 JDBC connection…
 jdusane/cve-2024-4879
Python script designed to detect specific vulnerabilities in ServiceNow instances and dump database connection details if the vulnerability is found.…