
PIIHunter
 owasp/piihunter
Scans PostgreSQL databases and Jira issues for PII using regex, NER/ML, and optional self-hosted LLM detection, with redacted reports and audit…
ai-securitydatabase-securitydata-exfiltration+6
3
owasp/piihunterScans PostgreSQL databases and Jira issues for PII using regex, NER/ML, and optional self-hosted LLM detection, with redacted reports and audit…
 qucklecrabik/cve-2026-23921
Proof-of-concept exploit for CVE-2026-23921, a time-based blind SQL injection in Zabbix API via the sortfield parameter, enabling data extraction…
 dinosn/ghost-cve-2026-26980
CVE-2026-26980 — Ghost CMS Content API SQL Injection Lab (unauthenticated blind SQLi via slug filter ordering)
 toanln-cov/cve-2026-74251
Unauthenticated SQL Injection via Attribute Filter in Phoca Cart - CVSS 9.3
 vognik/cve-2026-26980
Unauthenticated SQL injection exploit for Ghost CMS Content API (CVE-2026-26980); dumps database tables from SQLite/MySQL with active/passive checks…
 ridhinva/drupal-jsonapi-sqli-scanner
Scanner: CVE-2026-9082 Drupal PostgreSQL SQLi via JSON:API — Python scanner for unauthenticated SQLi leading to RCE (CISA KEV)
 0xdak/cve-2026-69083_exploit
Python PoC for CVE-2026-69083, an unauthenticated SQL injection in SiYuan's asset-content search endpoint. Supports REGEXP breakout and raw SQL…
 george0papasotiriou/cve-2026-11115-database-connection-string-injection-via-env-variable
 george0papasotiriou/cve-2026-21004-sqlite-fts3-match-infoleak-via-query-crafting
Proof-of-concept exploit for CVE-2026-21004: uses crafted SQLite FTS3/4 MATCH prefix queries as a blind oracle to recover indexed secret data…
 randomrobbiebf/postgres-bruteforcer
This tool takes a list of default creds and tests it against a postgresql server and logs any that work and the databases it has access to.
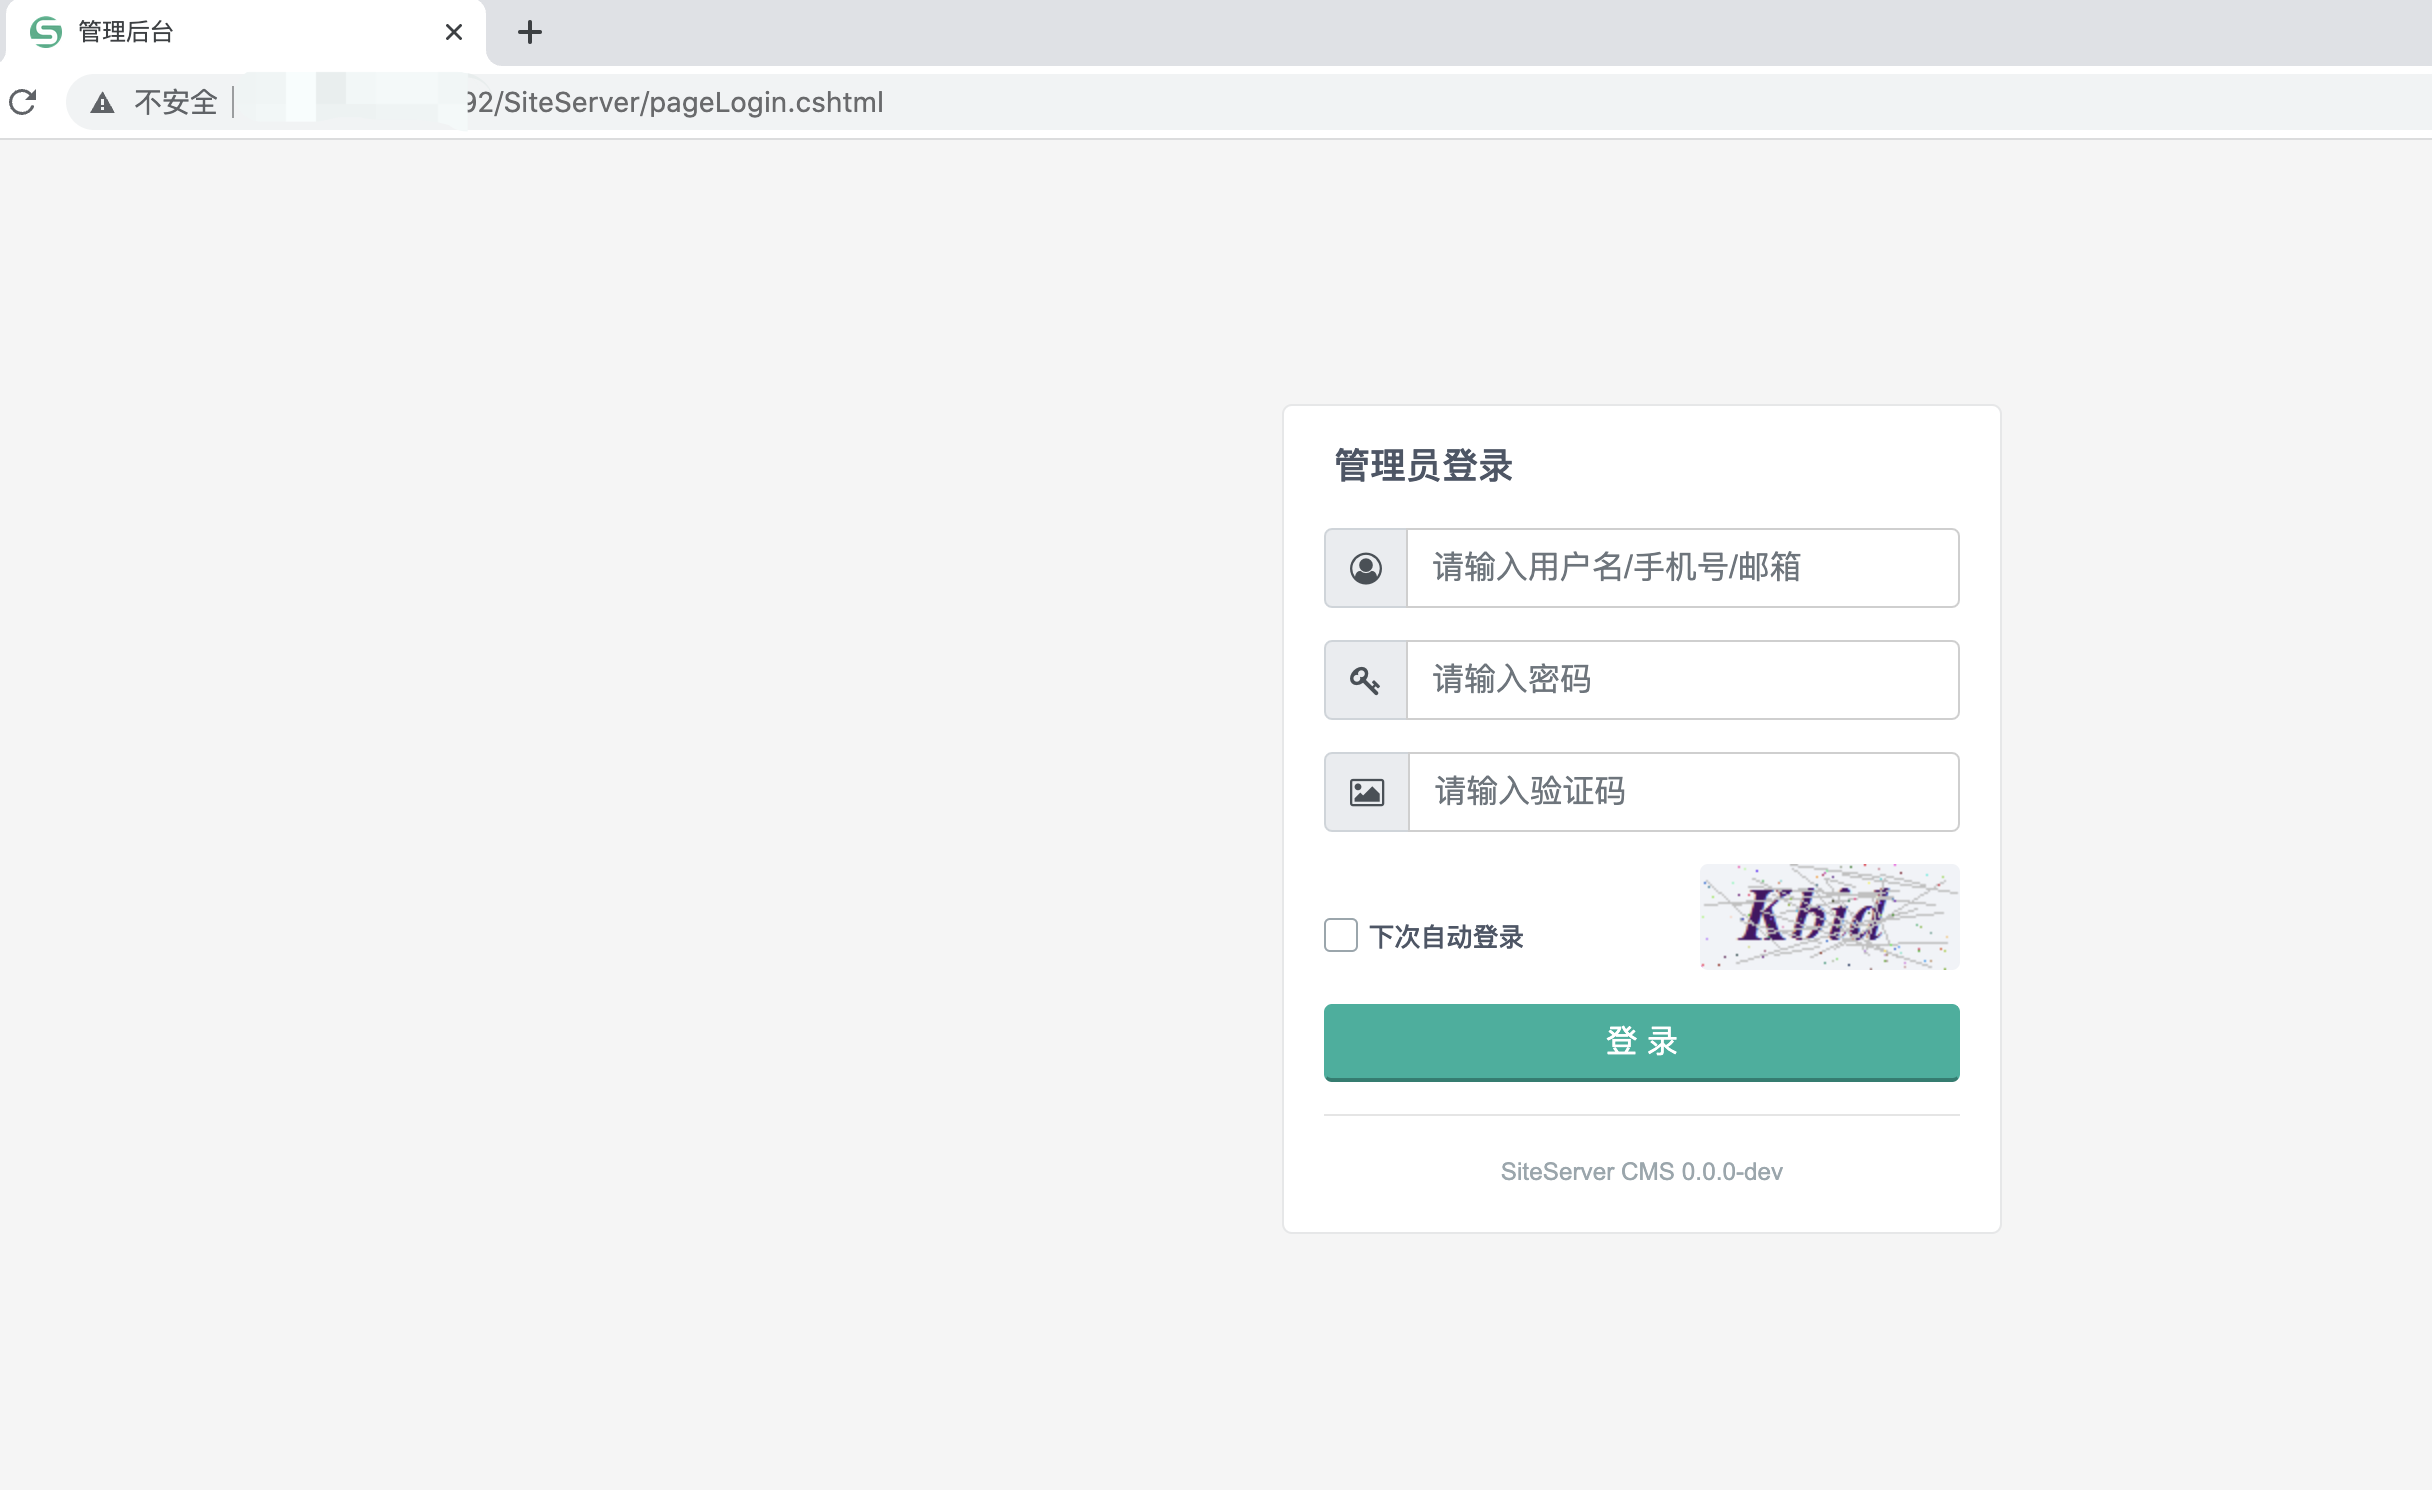 jas502n/sscms_decrypt
sscms database decrypt
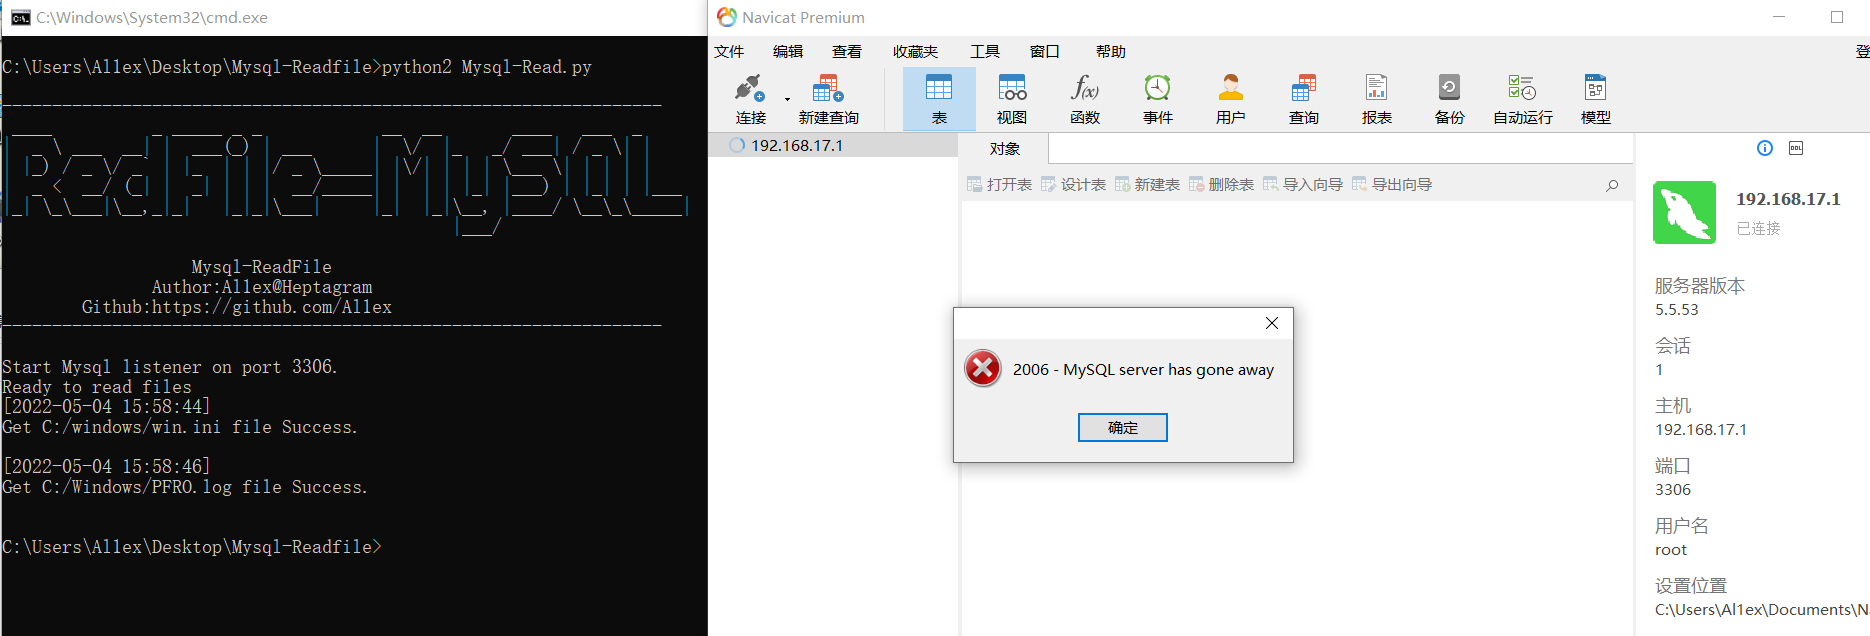
 al1ex/rogue-mysql-server
Rogue-MySql-Server
 jas502n/openfire_decrypt
OpenFire 管理后台账号密码解密
 chrissub08/cve-2026-25746_sqlinjectionvulnerabilityopenemr7.0.4
CVE-2026-25746 - SQL Injection Vulnerability in OpenEMR <8.0.0
 chrissub08/cve-2026-33917_sqlinjectionvulnerabilityopenemr8.0.0
CVE-2026-33917: SQL Injection Vulnerability in OpenEMR <8.0.0.3
 chrissub08/cve-2026-29187_sqlinjectionvulnerabilityopenemr7.0.4
CVE-2026-29187: SQL Injection Vulnerability in OpenEMR <8.0.0.3
 chrissub08/cve-2026-32127_sqlinjectionvulnerabilityopenemr8.0.0
CVE-2026-32127: SQL Injection Vulnerability in OpenEMR <8.0.0.1