
mysql-install-component-scheme
 abraxas/mysql-install-component-scheme
MySQL Community Server 26.7.0 - High - INSTALL COMPONENT qualified scheme - plugin_dir skip
database-securityexploitationlabs-practice+4
1
abraxas/mysql-install-component-schemeMySQL Community Server 26.7.0 - High - INSTALL COMPONENT qualified scheme - plugin_dir skip
 abraxas/mysql-jdv-definer-sqli
MySQL Community Server 26.7.0 - High - JSON Duality DEFINER SQLi - NO_BACKSLASH_ESCAPES
 abraxas/mysql-mysqldump-tab-path
MySQL Community Server 26.7.0 - High - mysqldump --tab path leftover - client file write
 abraxas/mysql-set-role-leftover
MySQL Community Server 26.7.0 - High - SET ROLE ALL EXCEPT leftover FILE - mysqld UID write
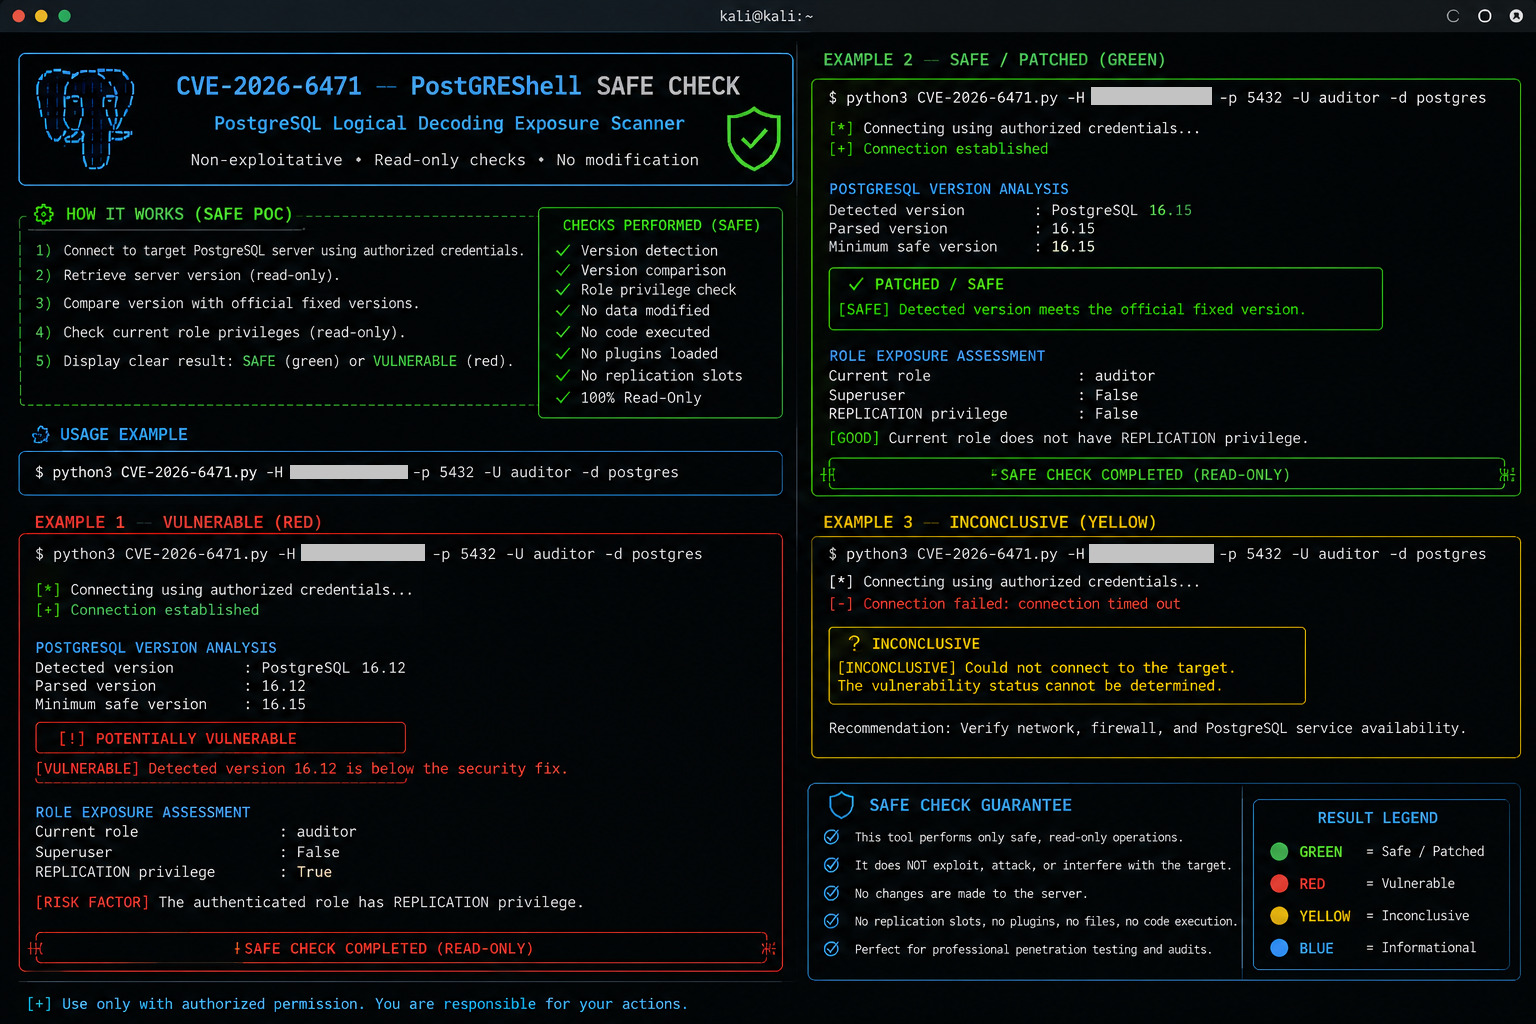 0xblackash/cve-2026-6471
Non-destructive PostgreSQL vulnerability checker for CVE-2026-6471. Audits server version and REPLICATION privileges to identify exposure to logical…
 romain-deperne/cve-2026-33980
Proof-of-concept exploit for KQL injection in adx-mcp-server via the table_name parameter, enabling data exfiltration and destructive commands in…
 joakimbulow/cve-2026-34308
Proof-of-concept for CVE-2026-34308, a MySQL Server JSON component denial-of-service vulnerability. Demonstrates stack exhaustion via deep $ref…
 ignitetechnologies/mssql-pentest-cheatsheet
Practical MSSQL penetration testing cheat sheet covering enumeration, linked-server pivoting, privilege escalation, persistence, and command…
 xforcered/sqlrecon
A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.
 randomrobbiebf/postgres-bruteforcer
This tool takes a list of default creds and tests it against a postgresql server and logs any that work and the databases it has access to.
 tarunkant/gopherus
This tool generates gopher link for exploiting SSRF and gaining RCE in various servers
 al1ex/rogue-mysql-server
Rogue-MySql-Server
 knqyf263/redis-post-exploitation
Educational Redis rogue server tool for post-exploitation. Deploys a malicious Redis server to achieve remote code execution and execute arbitrary…
 blue0x1/sqlwinds
SQLWinds - SQL Server Security Assessment & Post-Exploitation Toolkit
 netspi/sqlc2
SQLC2 is a PowerShell script for deploying and managing a command and control system that uses SQL Server as both the control server and the agent.
 shamo0/cve-2021-27928-poc
CVE-2021-27928-POC
 furkankayapinar/cve-2025-14847-mongobleed-exploit
CVE-2025-14847 MongoBleed - MongoDB Memory Leak Vulnerability PoC
 heavyghost-le/poc_sql_injection_in_parse_server_prior_6.5.7_-_7.1.0
Advanced PostgreSQL database enumeration tool exploiting CVE-2024-39309 in Parse Server - Comprehensive SQL injection exploitation for security…