Magento-CVE-2019-7139-SQLi-PoC

Python proof-of-concept exploit for CVE-2019-7139, an unauthenticated SQL injection in Magento's product_frontend_action endpoint, enumerating…

Python proof-of-concept exploit for CVE-2019-7139, an unauthenticated SQL injection in Magento's product_frontend_action endpoint, enumerating…

CVE-2026-79752 disclosure pack for CakePHP 5.2.13 SQL injection via FunctionsBuilder::cast, with a Python PoC script and Docker lab for authorized…

Documents CVE-2025-69295, a blind SQL injection in the TeconceTheme Coven Core WordPress component, covering technical details, impact, and detection…

Local GeoServer/PostGIS lab reproducing OGC Filter SQL injection (CVE-2023-25157/25158) with vulnerable, patched, and mitigated A/B test modes.

Self-contained Docker lab for practicing exploitation of CVE-2026-2005, a heap buffer overflow in PostgreSQL's pgcrypto extension, enabling privilege…

CVE-2026-26980 — Ghost CMS Content API SQL Injection Lab (unauthenticated blind SQLi via slug filter ordering)

Scanner and educational guide for CVE-2025-49844 (RediShell), a Redis Lua scripting use-after-free vulnerability. Checks Redis servers for exposure,…

Reproduces and analyzes CVE-2026-3494, an audit logging bypass in MariaDB server_audit plugin, using Docker-based multi-version testing to compare…

Intentionally vulnerable Golang programs exposing web, gRPC, and database/sql flaws for security training, vulnerability discovery, and remediation…

Redis UAF RCE PoC collection for CVE-2026-23479: safe version checker, exploit module, GDB-assisted PoC, and Sigma detection rules for authorized…


CVE-2025-49844 (RediShell)

PoC exploit for CVE-2026-17543: SQL injection in PHP ext/pgsql via backslash breakout, with data exfiltration and admin privilege-escalation payloads…

SQL injection in PyAthena via DefaultParameterFormatter (CVE-2026-65321)

Proof-of-concept demonstrating CVE-2026-17351 SQL injection bypass in pgAdmin 4's AI Assistant via sqlparse/PostgreSQL lexer differential, including…

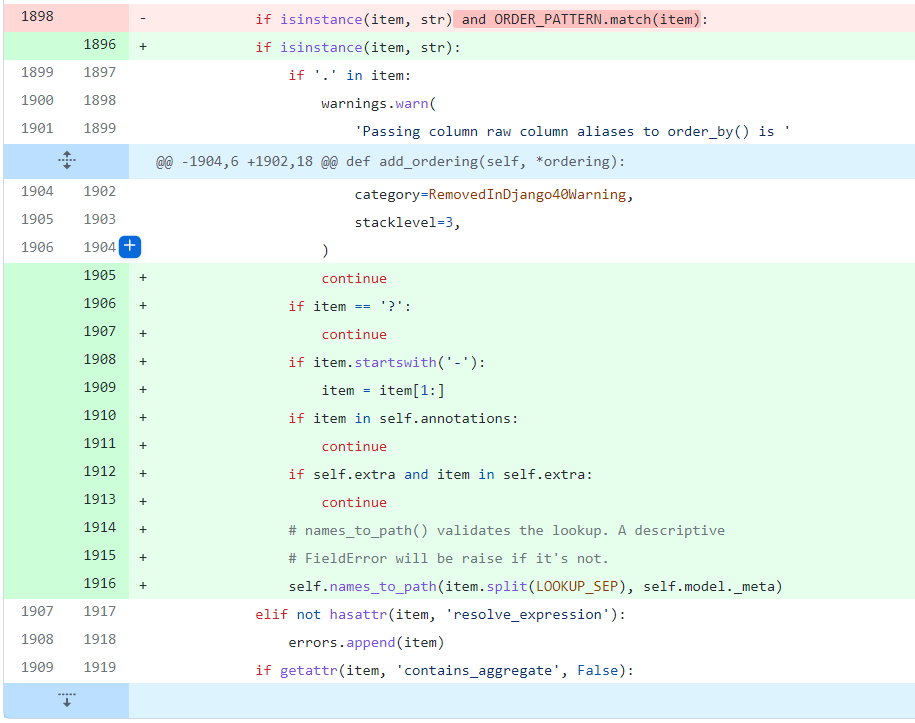
Django SQL injection vulnerability


Educational Redis rogue server tool for post-exploitation. Deploys a malicious Redis server to achieve remote code execution and execute arbitrary…