
CVE-2025-24799
 galisko/cve-2025-24799
Unauthenticated SQL injection exploit for GLPI versions before 10.0.18, enabling database enumeration, credential extraction, and API token…
database-securityexploitationpenetration-testing+3
galisko/cve-2025-24799Unauthenticated SQL injection exploit for GLPI versions before 10.0.18, enabling database enumeration, credential extraction, and API token…
 warp-tech/warpgate
Fully transparent SSH, HTTPS, Kubernetes, database and RDP/VNC bastion/PAM that doesn't need additional client-side software
 maliktawfiq/cve-2025-22953
EPICOR HCM Unauthenticated Blind SQL Injection CVE-2025-22953
 redfr0g/cve-2023-20110
PoC script for CVE-2023-20110 - Cisco Smart Software Manager On-Prem SQL Injection Vulnerability
 sadshade/cve-2022-24706-couchdb-exploit
Apache CouchDB 3.2.1 - Remote Code Execution (RCE)
 mateustesser/cve-2023-31717
Proof-of-concept SQL injection exploit for FUXA SCADA software (<=1.1.12) via HTTP POST JSON id parameter, enabling extraction of SQLite database…
 afnaan-ahmed/cve-2025-14598
Technical advisory and analysis of CVE-2025-14598, a critical unauthenticated SQL injection in BET e-Portal enabling database manipulation and…
 bridgeralderson/cve-2024-51482
ZenoMinder Blind SQL Injection PoC
 misp/misp
MISP (core software) - Open Source Threat Intelligence and Sharing Platform
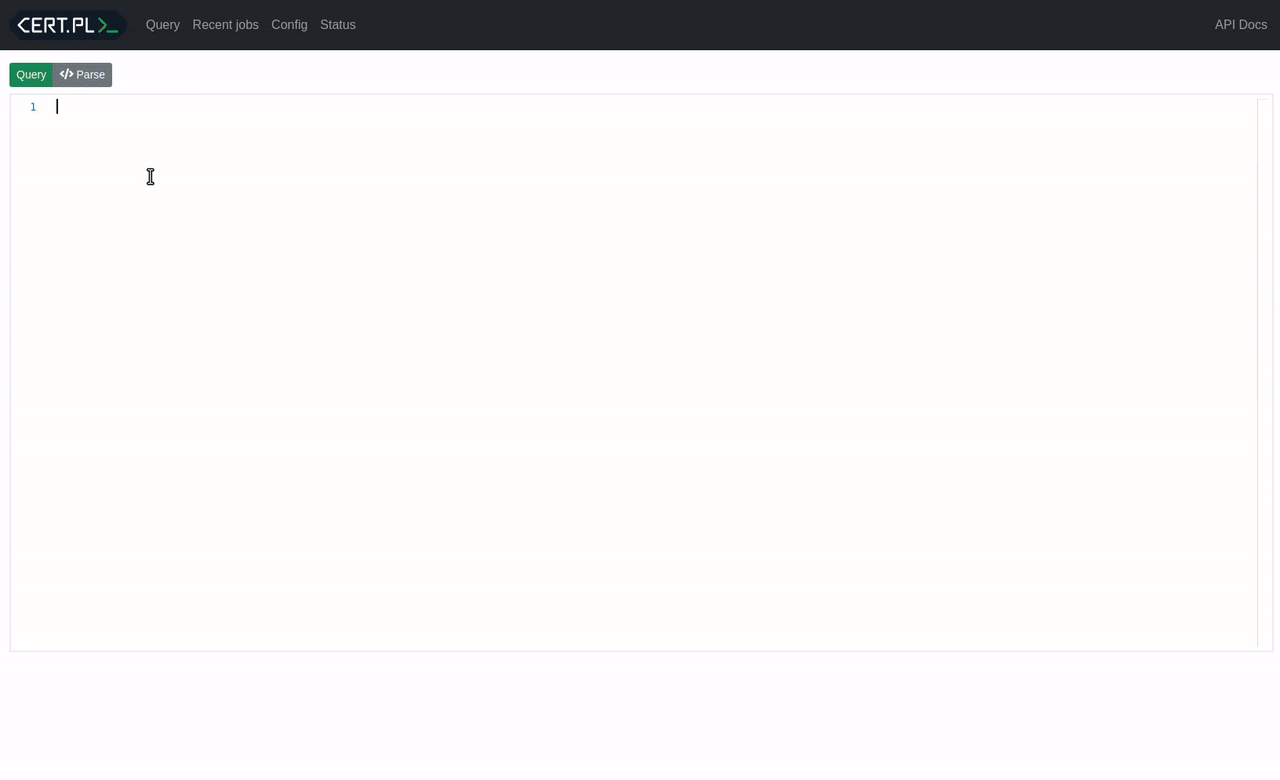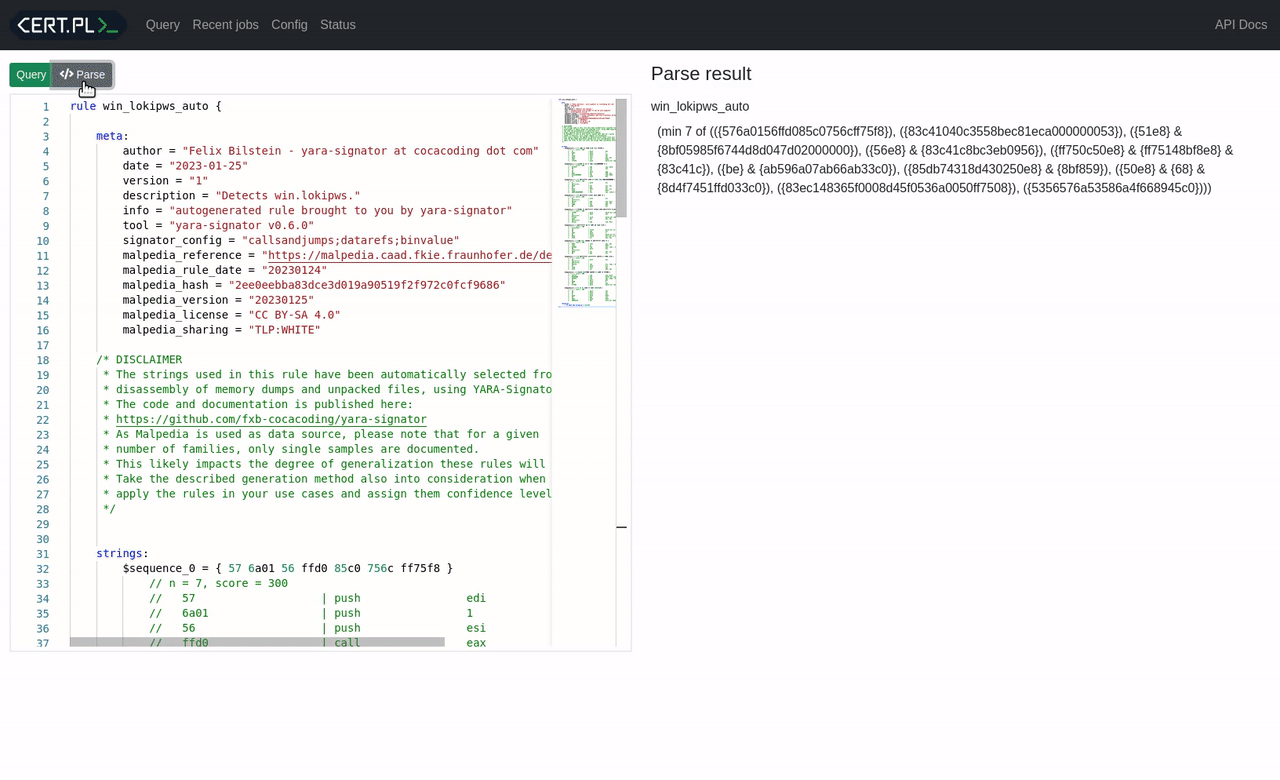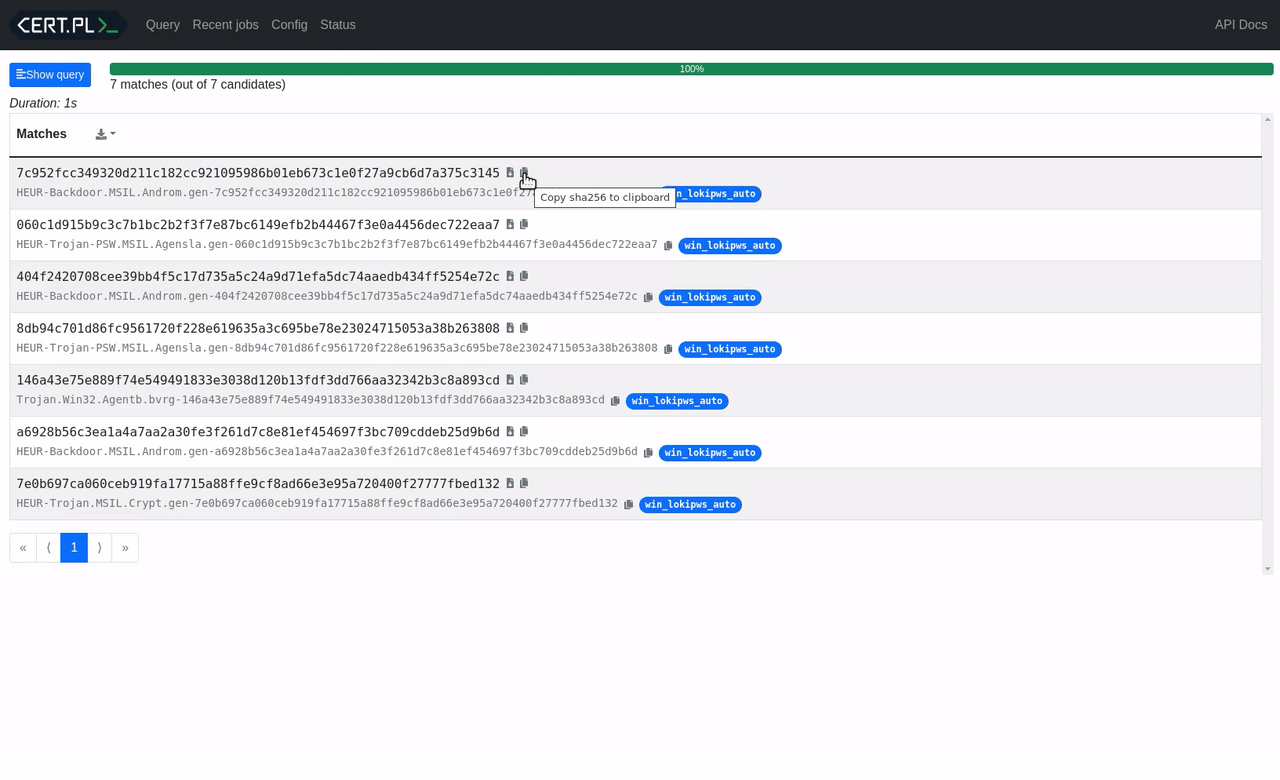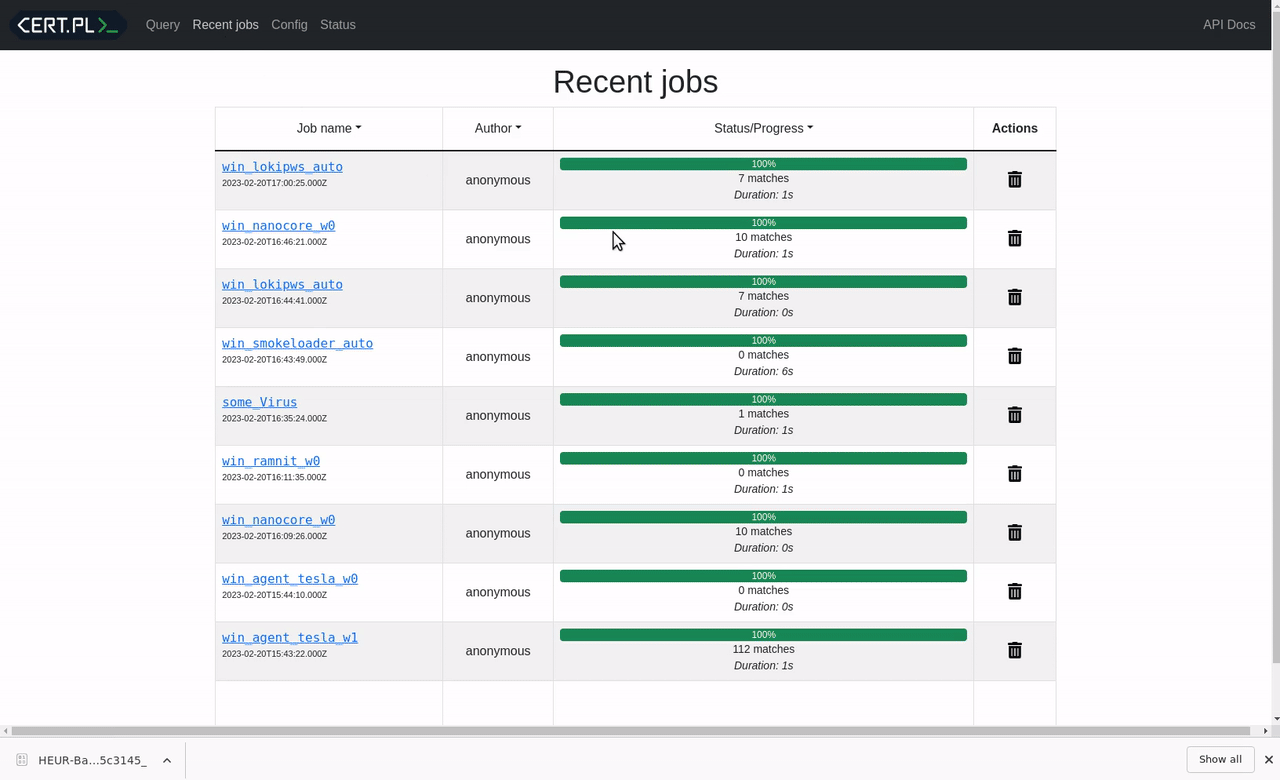 cert-polska/mquery
YARA malware query accelerator (web frontend)
 aboutcode-org/vulnerablecode
Open-source vulnerability database aggregating CVE data from multiple sources with a web UI and API. Maps vulnerabilities to specific software…
 adityaks/melee
Python-based tool to detect ransomware infections and malicious code in MySQL instances. Performs reconnaissance, user enumeration, and deep scans…
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…