Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
23 results
CVE-2026-67401-cPanel-EmailTrack-SQLi preview

CVE-2026-67401-cPanel-EmailTrack-SQLi

GitHubjithinkrishnanrs/cve-2026-67401-cpanel-emailtrack-sqli

Read-only IOC scanner and mitigation toolkit for cPanel & WHM EmailTrack SQL injection (CVE-2026-67401). Performs version fingerprinting, file…

cloud-infrastructure-securityconfiguration-auditingdatabase-security+6
13 days ago
CVE-2025-46817-PoC preview

CVE-2025-46817-PoC

GitHubslayerkkkk/cve-2025-46817-poc

C-based exploit for CVE-2025-46817, a Redis integer overflow vulnerability, enabling crash detection and potential RCE via Lua unpack() payload.

database-securityexploitationfuzzing+2
211 months ago
CVE-2026-58048-PoC-Exploit preview

CVE-2026-58048-PoC-Exploit

GitHubtc4dy/cve-2026-58048-poc-exploit

👾 CVE-2026-58048 – cPanel Root SQL Execution Toolkit (CVSS 9.4) | Full Red/Blue Team Toolkit suite for unpatched cPanel & WHM 11.x. 2 tools: Safe…

database-securityexploitationincident-response+7
51 month ago
postgres-bruteforcer preview

postgres-bruteforcer

GitHubrandomrobbiebf/postgres-bruteforcer

This tool takes a list of default creds and tests it against a postgresql server and logs any that work and the databases it has access to.

authenticationdatabase-securityexploitation+2
3 years ago
Rogue-MySql-Server preview

Rogue-MySql-Server

GitHubal1ex/rogue-mysql-server

Rogue-MySql-Server

database-securitydata-exfiltrationexploitation+3
56 years ago
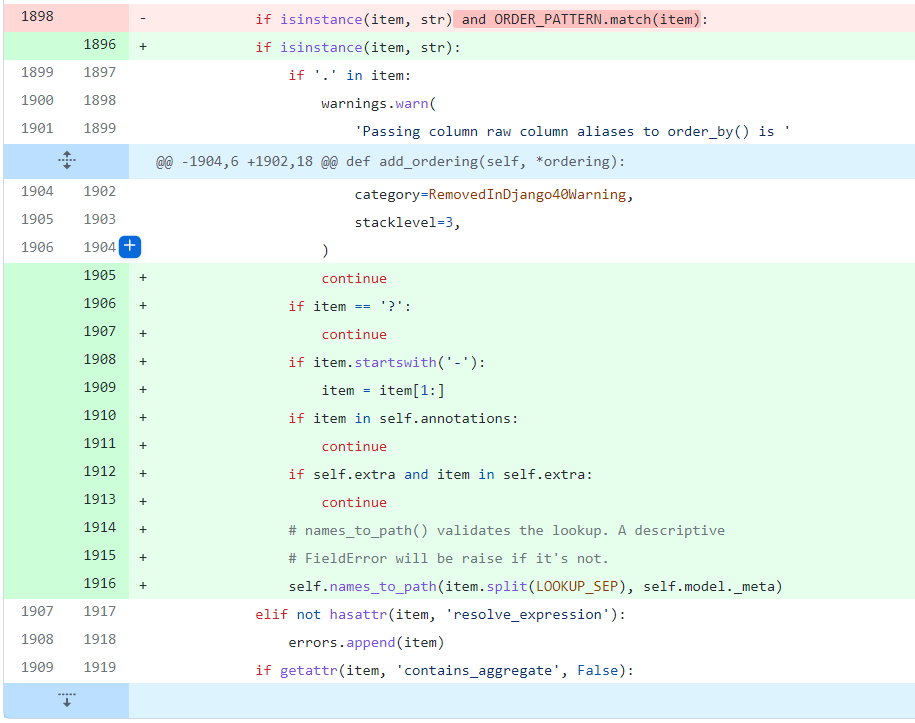
CVE-2021-35042 preview

CVE-2021-35042

GitHubluuanhduc/cve-2021-35042

Django SQL injection vulnerability

database-securityeducationexploitation+3
3 years ago
CVE-2025-14847-mongobleed preview

CVE-2025-14847-mongobleed

GitHubshokribardiya/cve-2025-14847-mongobleed

CVE-2025-14847 mongobleed python file

database-securityeducationexploitation+2
13 months ago
CVE-2024-51747 preview

CVE-2024-51747

GitHubl20170217b/cve-2024-51747

Proof-of-concept exploit for CVE-2024-51747 enabling authenticated file read and deletion via SQLite database manipulation in a web application's…

database-securitydata-exfiltrationexploitation+2
1 year ago
MySQL-Fu.rb preview

MySQL-Fu.rb

GitHubhood3drob1n/mysql-fu.rb

MySQL-Fu is a Ruby based MySQL Client Script I wrote. It does most of the stuff a normal MySQL client might do: SQL Shell, Update/Delete/Drop…

database-securityexploitationpayload-generation+3
313 years ago
CVE-2024-34693 preview

CVE-2024-34693

GitHubmr-r00t11/cve-2024-34693

An input validation vulnerability in Apache Superset allows an authenticated attacker to create a MariaDB connection with local_infile enabled,…

database-securitydata-exfiltrationexploitation+3
2 years ago
CVE-2025-70828 preview

CVE-2025-70828

GitHubxiaoxiaoranxxx/cve-2025-70828

Datart v1.0.0-rc.3 JDBC Connection String Injection Leading to Arbitrary File Read

database-securityexploitationinformation-gathering+3
47 months ago
CVE-2024-34693 preview

CVE-2024-34693

GitHubmbadanoiu/cve-2024-34693

CVE-2024-34693: Server Arbitrary File Read in Apache Superset

database-securitydata-exfiltrationexploitation+3
102 years ago
CVE-2021-31856 preview

CVE-2021-31856

GitHubssst0n3/cve-2021-31856

Detailed CVE-2021-31856 report with PoC and code analysis for a SQL injection vulnerability in Meshery's pattern file API, enabling unauthenticated…

code-analysisdatabase-securitypenetration-testing+2
5 years ago
mysqld_safe-CVE-2016-6662-patch preview

mysqld_safe-CVE-2016-6662-patch

GitHubkonstantin-kelemen/mysqld_safe-cve-2016-6662-patch

Ansible playbook that applies the Percona patch for CVE-2016-6662 to the mysqld_safe file on CentOS and FreeBSD systems.

configuration-auditingdatabase-securitydevsecops+1
10 years ago
cve-2016-6662 preview

cve-2016-6662

GitHubboompig/cve-2016-6662

Exploit code for MySQL remote root code execution and privilege escalation (CVE-2016-6662), including Python and C implementations.

database-securityexploitationpayload-development+3
19 years ago
CVE-2019-14529 preview

CVE-2019-14529

GitHubwezery/cve-2019-14529

OpenEMR Security issue

database-securityinformation-gatheringpenetration-testing+2
6 years ago
CVE-2025-26198 preview

CVE-2025-26198

GitHubwailyacoubi9/cve-2025-26198

Educational reproduction of CVE-2025-26198 SQL injection in CloudClassroom-PHP-Project, demonstrating four exploitation techniques (boolean, union,…

authenticationdatabase-securityeducation+3
8 months ago
CVE-2020-11579 preview

CVE-2020-11579

GitHubshieldersec/cve-2020-11579

Exploit code for CVE-2020-11579, an arbitrary file disclosure through the MySQL client in PHPKB

database-securitydata-exfiltrationexploitation+3
252 years ago
Previous12Next