

sqlmap
 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
api-securityapi-security-testingcrawler+12
sqlmapproject/sqlmapAutomatic SQL injection and database takeover tool
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 oscarbataille/cve-2025-26794
CVE-2025-26794: Blind SQL injection in Exim 4.98 (SQLite DBM)- exploit writeup
 cve-search/cve-search
Local CVE/CPE vulnerability database with search, ranking, web interface, and API for offline vulnerability analysis and management.
 dovankha/cve-2024-34222
Proof-of-concept for SQL injection vulnerability in SourceCodester Human Resource Management System 1.0, demonstrating arbitrary SQL command…
 geraldoalcantara/cve-2023-49970
Customer Support System 1.0 - SQL Injection Vulnerability in the "subject" Parameter During "save_ticket" Operation
 joe-desimone/mongobleed
Proof-of-concept exploit for CVE-2025-14847, a MongoDB zlib decompression vulnerability that leaks uninitialized server memory via crafted BSON…
 osandamalith/cve-2015-4870
MySQL DoS in the Procedure Analyse Function – CVE-2015-4870
 xsshk/cve-2024-46981
Proof-of-concept exploit for CVE-2024-46981 targeting Redis 6.2.11, demonstrating a remote code execution vulnerability in the in-memory data store.
 hakaioffsec/cve-2026-44706
Chatwoot SQL injection in FilterService
 bridgeralderson/cve-2024-51482
ZenoMinder Blind SQL Injection PoC
 joshuavanderpoll/cve-2025-14847
CVE-2025-14847 (MongoBleed)
 saferman/cve-2020-7471
django 漏洞:CVE-2020-7471 Potential SQL injection via StringAgg(delimiter) 的漏洞环境和 POC
 berabuddies/redis-poc
RCE PoC for Redis 6.2.22, 7.4.9, 8.6.4, 8.8.0, 8.8.1
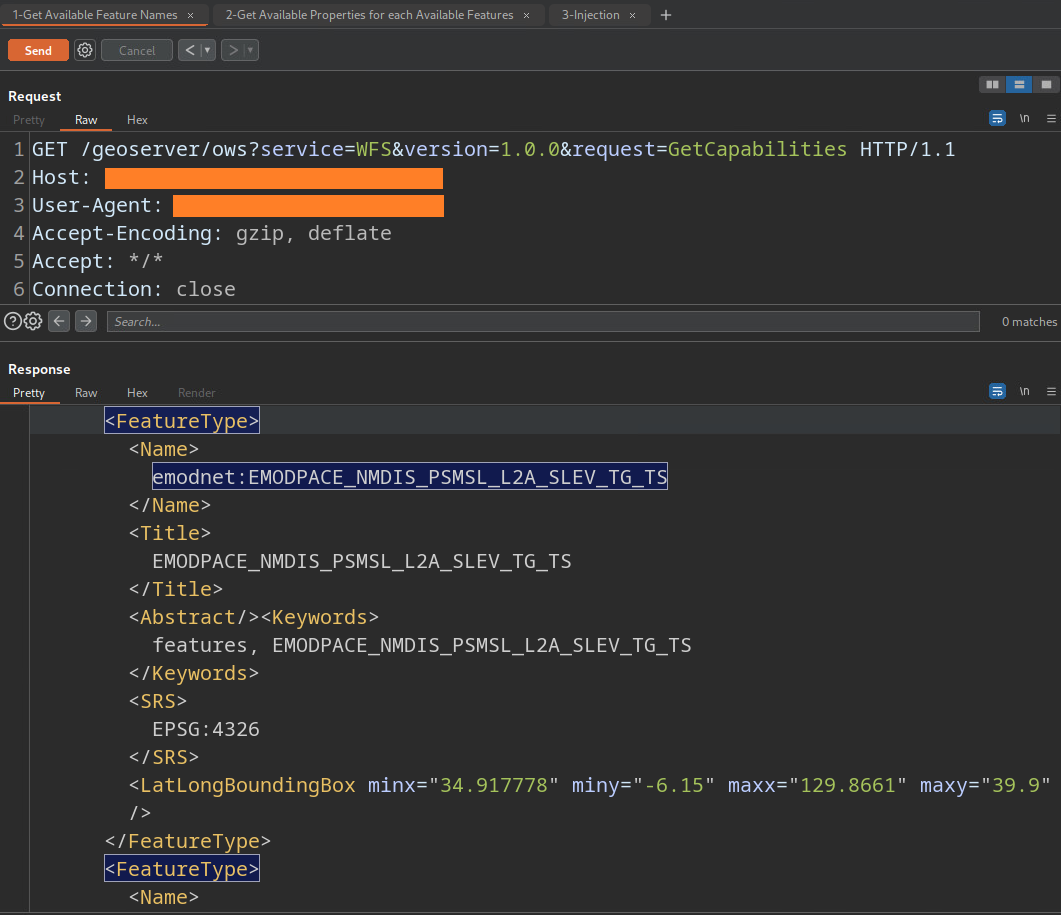 murataydemir/cve-2023-25157-and-cve-2023-25158
GeoServer & GeoTools SQL Injection (CVE-2023-25157 & CVE-2023-25158)
 mateustesser/cve-2023-31717
Proof-of-concept SQL injection exploit for FUXA SCADA software (<=1.1.12) via HTTP POST JSON id parameter, enabling extraction of SQLite database…