
custom-oscp-tooling
 wattocyber/custom-oscp-tooling
OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…
database-securitydns-analysishash-analysis+9
wattocyber/custom-oscp-toolingOSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…

 nu11secur1ty/complete-google-dorks
Curated collection of Google dork queries for advanced search engine reconnaissance, uncovering exposed databases, configuration files, admin panels,…
 aboutcode-org/vulnerablecode
Open-source vulnerability database aggregating CVE data from multiple sources with a web UI and API. Maps vulnerabilities to specific software…
 trailofbits/cvedb
CVE querying library and utility that uses a local store syncing directly to the National Vulnerability Database
 cve-search/cve-search
Local CVE/CPE vulnerability database with search, ranking, web interface, and API for offline vulnerability analysis and management.
 ianxtianxt/mongodb-redis-scan
mongodb-redis匿名扫描脚本,支持mongodb和redis的匿名扫描
 galisko/cve-2025-24799
Unauthenticated SQL injection exploit for GLPI versions before 10.0.18, enabling database enumeration, credential extraction, and API token…
 etlownoise/xolo
Tool to crawl, visualize and interact with SQL server links in a d3 graph to help in your red/blue/purple/.../risk assessments pentest hacking team…
 cerberusmrxi/cve-2026-44680-mikroorm-sql-injection-exploit-framework
PoC tool for CVE-2026-44680 affecting MikroORM ≤7.0.13. Exploits JSON path injection to extract database contents via UNION-based attacks. Features…
 codingo/nosqlmap
Automated NoSQL database enumeration and web application exploitation tool.
 proxydom/supahunter
Automated reconnaissance and exploitation framework for misconfigured Supabase instances. Features schema enumeration, Selenium-based key extraction,…
 m8sec/enumdb
Relational database brute force and post exploitation tool for MySQL and MSSQL
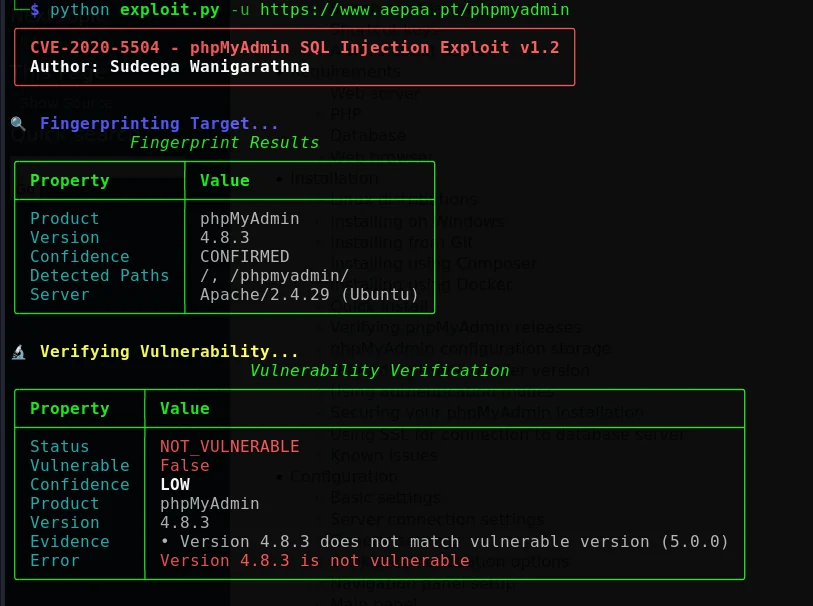 cerberusmrxi/phpmyadmin-cve-2020-5504-exploit
Authorized SQL injection exploitation framework for CVE-2020-5504 in phpMyAdmin, featuring automated database enumeration, blind injection, proxy…
 gnosticplayers/solr-grab
Steal Apache Solr instance Queries with or without a username and password.
 fantasy-fql/esapi-sqlinjection-cve-2025-5878-exploit
Exploit for CVE-2025-5878 targeting ESAPI's encodeForSQL() method with OracleCodec, enabling time-based blind SQL injection. Supports database…
 daniel2005d/mapxplore
Allow exporting the information downloaded with sqlmap to a relational Database like Postgres and sqlite
 nabeelmkhan/cve-2026-78837
Proof-of-concept exploit for CVE-2026-78837, an unauthenticated SQL injection in AppNitro MachForm v30 allowing enumeration of database column names…