metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Scans PostgreSQL databases and Jira issues for PII using regex, NER/ML, and optional self-hosted LLM detection, with redacted reports and audit…

Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…

Open-source vulnerability database aggregating CVE data from multiple sources with a web UI and API. Maps vulnerabilities to specific software…

Local CVE/CPE vulnerability database with search, ranking, web interface, and API for offline vulnerability analysis and management.

Automated SQL injection detection and exploitation tool for extracting database information from web applications, supporting multiple injection…

Proof-of-concept SQL injection exploit for FUXA SCADA software (<=1.1.12) via HTTP POST JSON id parameter, enabling extraction of SQLite database…

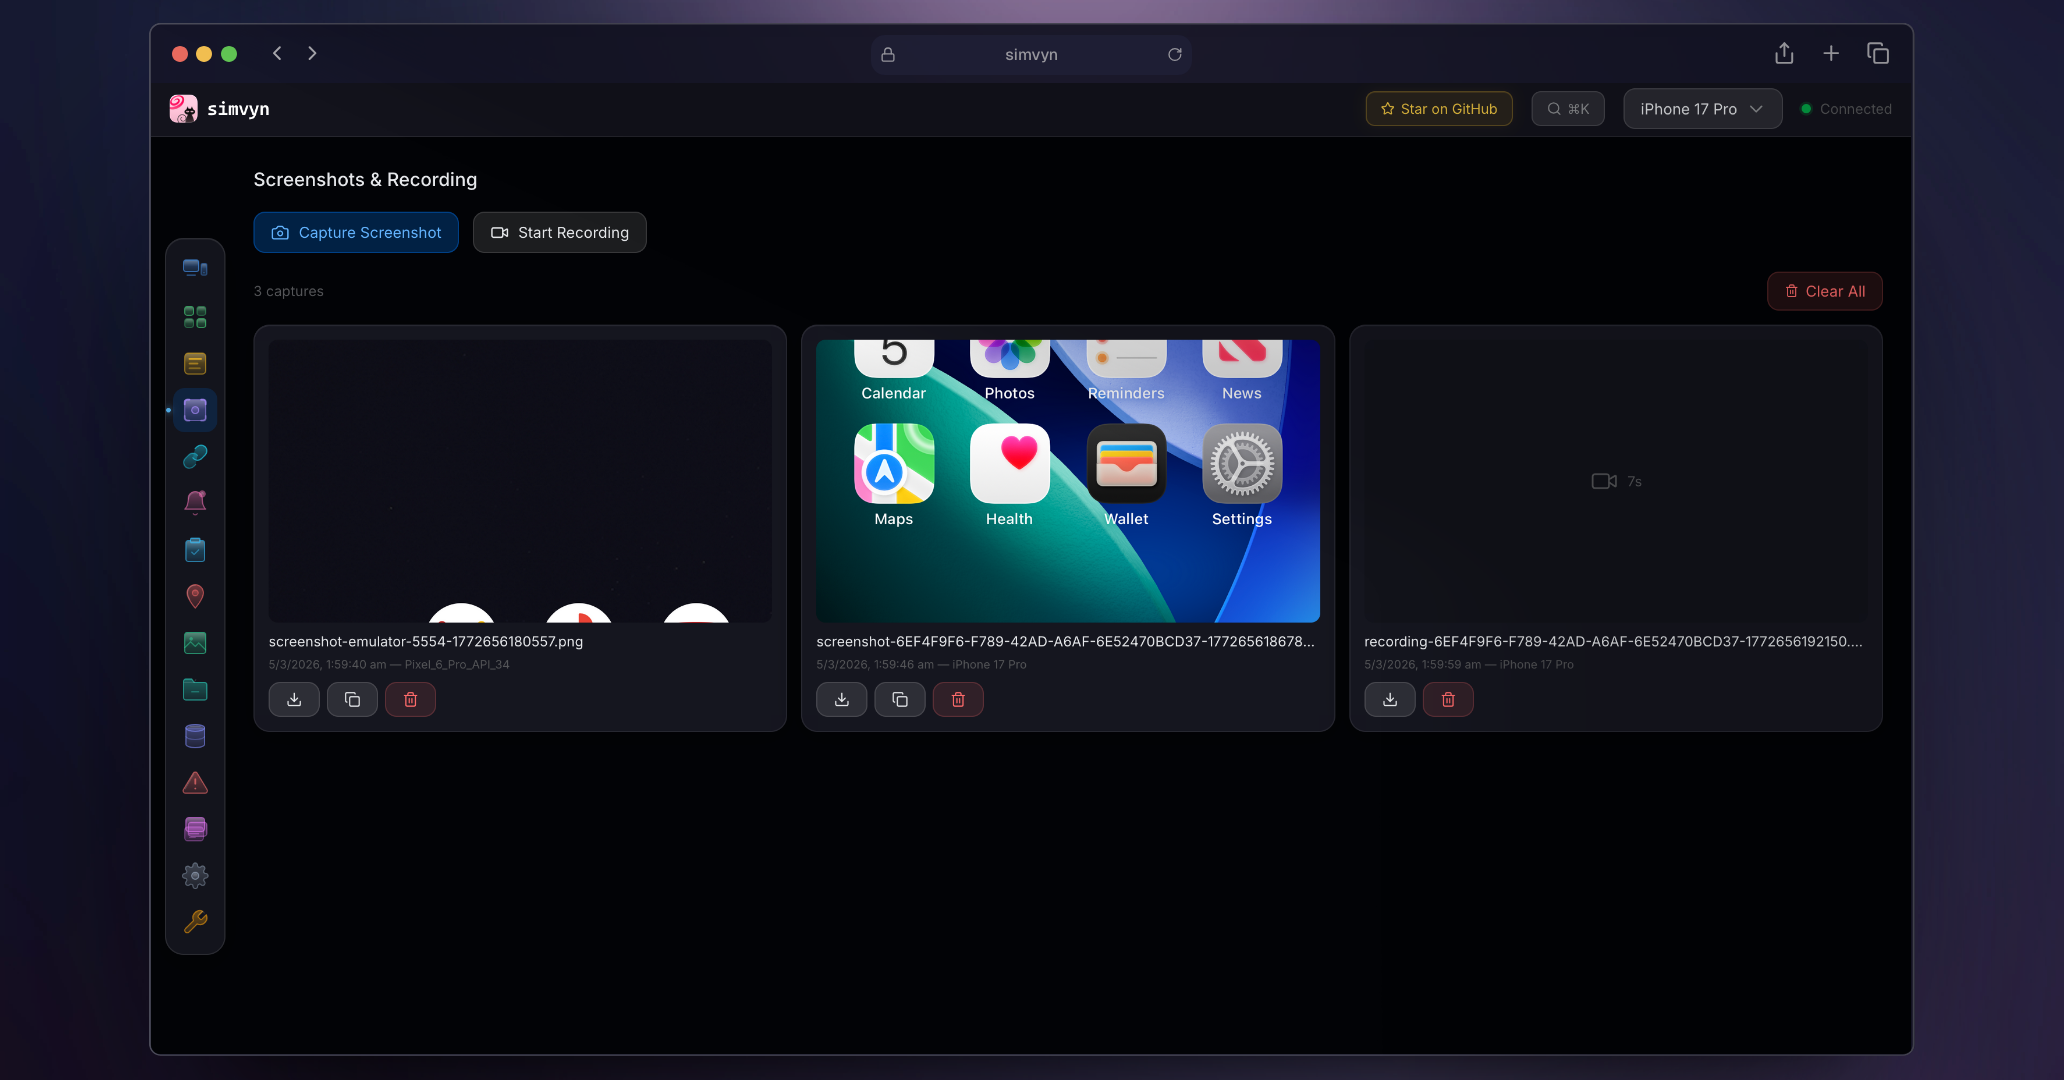
Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI

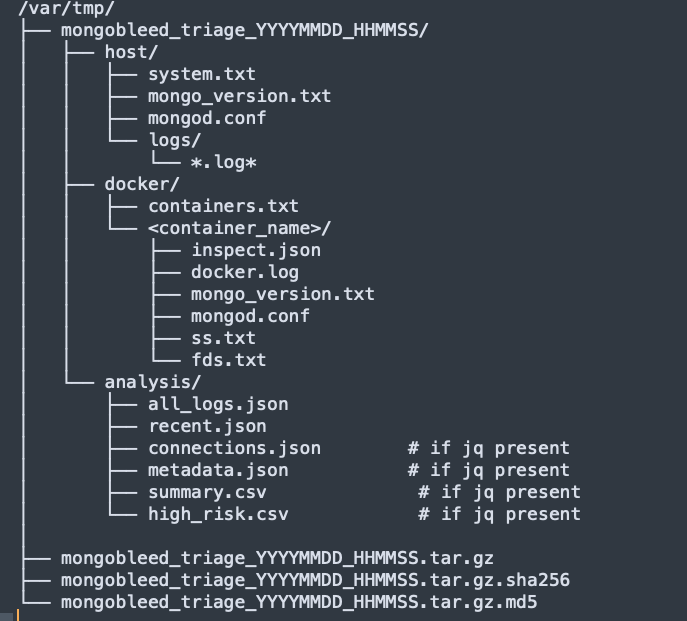
The script focuses on safe artifact acquisition first, followed by optional on-host analysis, and produces a portable, hashed forensic archive…


Unauthenticated SQL injection exploit for Ghost CMS Content API (CVE-2026-26980); dumps database tables from SQLite/MySQL with active/passive checks…

Scanner: CVE-2026-9082 Drupal PostgreSQL SQLi via JSON:API — Python scanner for unauthenticated SQLi leading to RCE (CISA KEV)

Proof-of-concept exploit for CVE-2026-23921, a time-based blind SQL injection in Zabbix API via the sortfield parameter, enabling data extraction…

Unauthenticated SQL Injection via Attribute Filter in Phoca Cart - CVSS 9.3

The tool exfiltrates data from Couchbase database by exploiting N1QL injection vulnerabilities.

OSINT tool to search, parse and dump only the open Elasticsearch and MongoDB directories that have the data you care about exposing

Attempts to exploit CVE-2012-3137 on vulnerable Oracle servers

Exploit code for CVE-2020-11579, an arbitrary file disclosure through the MySQL client in PHPKB