
CVE-2023-31717
 mateustesser/cve-2023-31717
Proof-of-concept SQL injection exploit for FUXA SCADA software (<=1.1.12) via HTTP POST JSON id parameter, enabling extraction of SQLite database…
database-securityexploitationscada-ics-security+2
mateustesser/cve-2023-31717Proof-of-concept SQL injection exploit for FUXA SCADA software (<=1.1.12) via HTTP POST JSON id parameter, enabling extraction of SQLite database…
 learner202649/cve-2025-45809-poc
Time-based blind SQL injection proof-of-concept for LiteLLM v1.65.4. Exploits the `/key/block` endpoint to extract database contents and read server…
 cerberusmrxi/cve-2026-44680-mikroorm-sql-injection-exploit-framework
PoC tool for CVE-2026-44680 affecting MikroORM ≤7.0.13. Exploits JSON path injection to extract database contents via UNION-based attacks. Features…
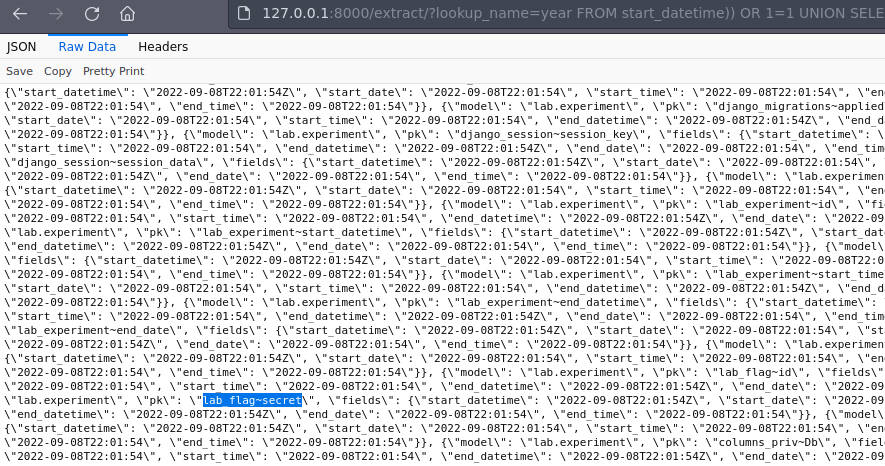 lnwza0x0a/ctf_django_cve-2022-34265
Docker-based CTF challenge demonstrating SQL injection in Django's Trunc() and Extract() database functions (CVE-2022-34265) with UNION-based payload…
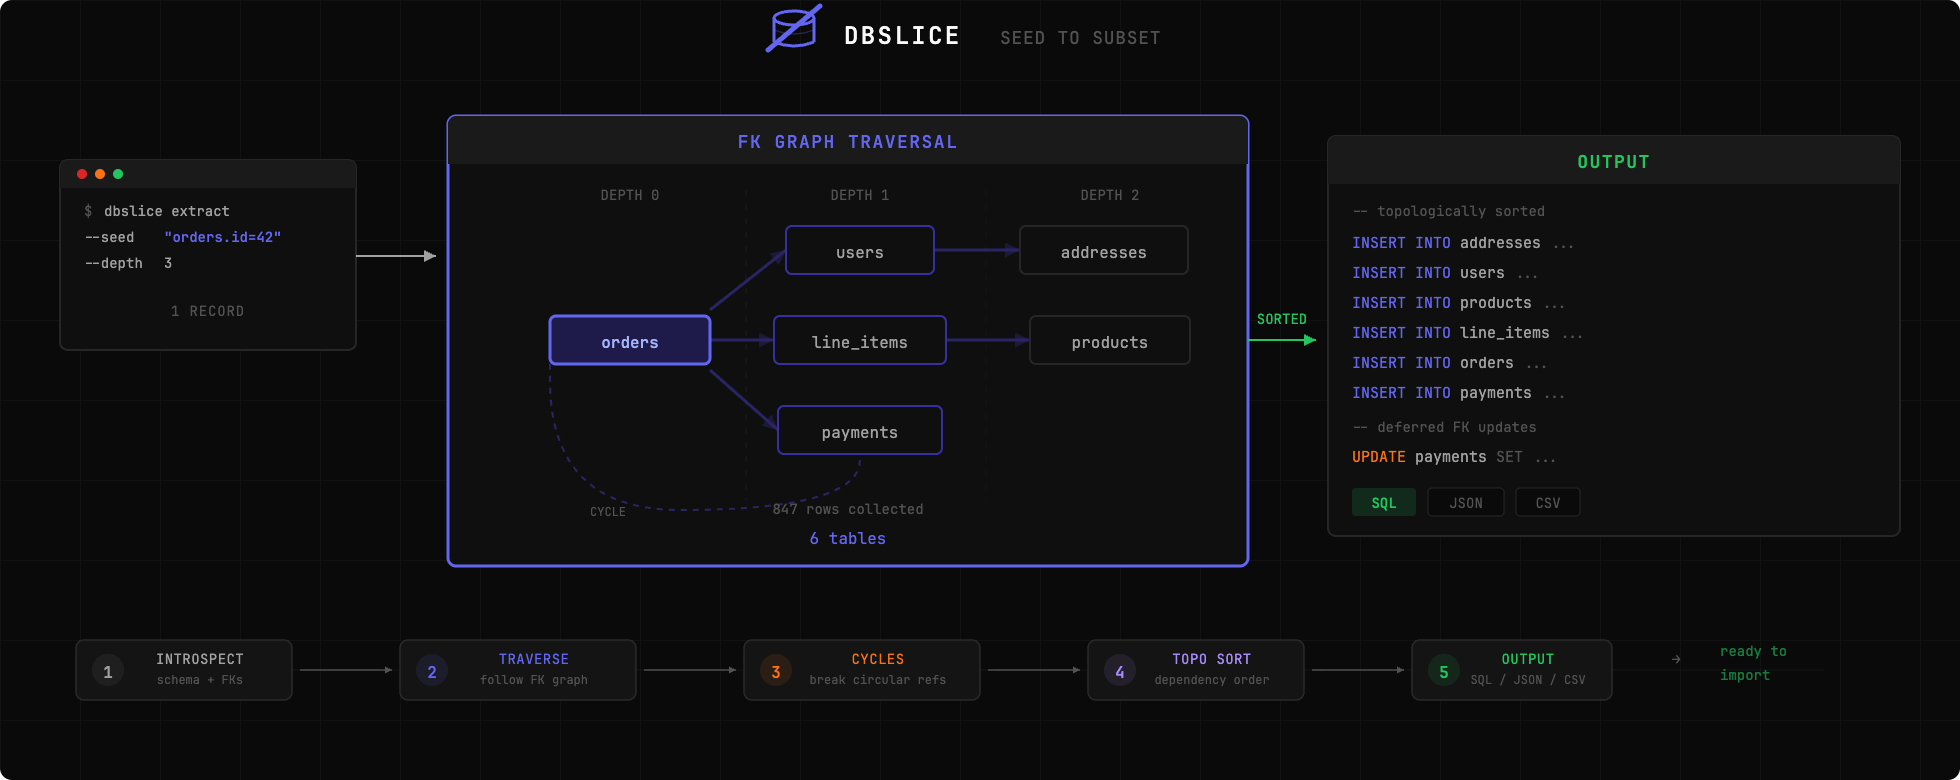 nabroleonx/dbslice
Extract a slice of your production database to reproduce bugs locally. Point dbslice at a record, it follows foreign keys and gives you a complete,…
 metthk/cve-2023-48084-revised
Python PoC exploiting time-based blind SQLi in Nagios XI to extract database contents, with multithreaded binary-search extraction and CLI…
 cybertechajju/cve-2025-14847_expolit
a critical memory disclosure vulnerability in MongoDB's zlib compression handling. This tool allows security researchers to extract sensitive data…
 0xsu3ks/cve-2025-45346
Proof-of-concept exploit for time-based blind SQL injection in Bacula-Web's jobfiles endpoint, using pg_sleep() delays to extract PostgreSQL version…
 hakaioffsec/cve-2026-40083
Proof-of-concept exploit for CVE-2026-40083, a SQL injection in Cacti managers.php allowing authenticated users to extract MySQL databases, user…
 m0b1u3/cve-2025-50565
Proof-of-concept exploit for an SQL injection vulnerability in Doubo ERP 1.0, enabling remote attackers to extract sensitive database information.
 huangyanqwq/cve-2023-49496_poc
Proof-of-concept exploit for CVE-2023-49496, demonstrating SQL injection in UCServer via the /login/wwx_corpInfo/ endpoint to extract sensitive…
 traumatising/cve-2022-34265
CVE-2022-34265 Vulnerability
 0xdeku/cve-2021-42668
Proof-of-concept exploit for CVE-2021-42668, a SQL injection in Engineers Online Portal. Uses the vulnerable id parameter in my_classmates.php to…
 holypryx/cve-2024-10140
SQL injection exploit script targeting CVE-2024-10140 in the /php/manage_supplier.php endpoint, enabling arbitrary SQL command injection via the id…
 t0x1cx/cve-2021-36396-moodle-time-based-sqli-exploit
This script demonstrates a time-based blind SQL injection on Moodle platforms, exploiting response delays to extract data.