

CVE-2024-4879
 0xwhoami35/cve-2024-4879
Exploit script for ServiceNow CVE-2024-4879 that enables unauthenticated remote code execution, with mass target scanning and database dumping…
database-securityexploitationinformation-gathering+3
0xwhoami35/cve-2024-4879Exploit script for ServiceNow CVE-2024-4879 that enables unauthenticated remote code execution, with mass target scanning and database dumping…
 aboutcode-org/vulnerablecode
Open-source vulnerability database aggregating CVE data from multiple sources with a web UI and API. Maps vulnerabilities to specific software…
 cve-search/cve-search
Local CVE/CPE vulnerability database with search, ranking, web interface, and API for offline vulnerability analysis and management.
 0xdea/exploits
Public exploit repository covering local privilege escalation, buffer overflows, and database exploits across Linux, Solaris, AIX, OpenBSD, Zyxel,…
 metthk/cve-2023-48084-revised
Python PoC exploiting time-based blind SQLi in Nagios XI to extract database contents, with multithreaded binary-search extraction and CLI…
 daniel2005d/mapxplore
Allow exporting the information downloaded with sqlmap to a relational Database like Postgres and sqlite
 etlownoise/xolo
Tool to crawl, visualize and interact with SQL server links in a d3 graph to help in your red/blue/purple/.../risk assessments pentest hacking team…
 gnosticplayers/solr-grab
Steal Apache Solr instance Queries with or without a username and password.
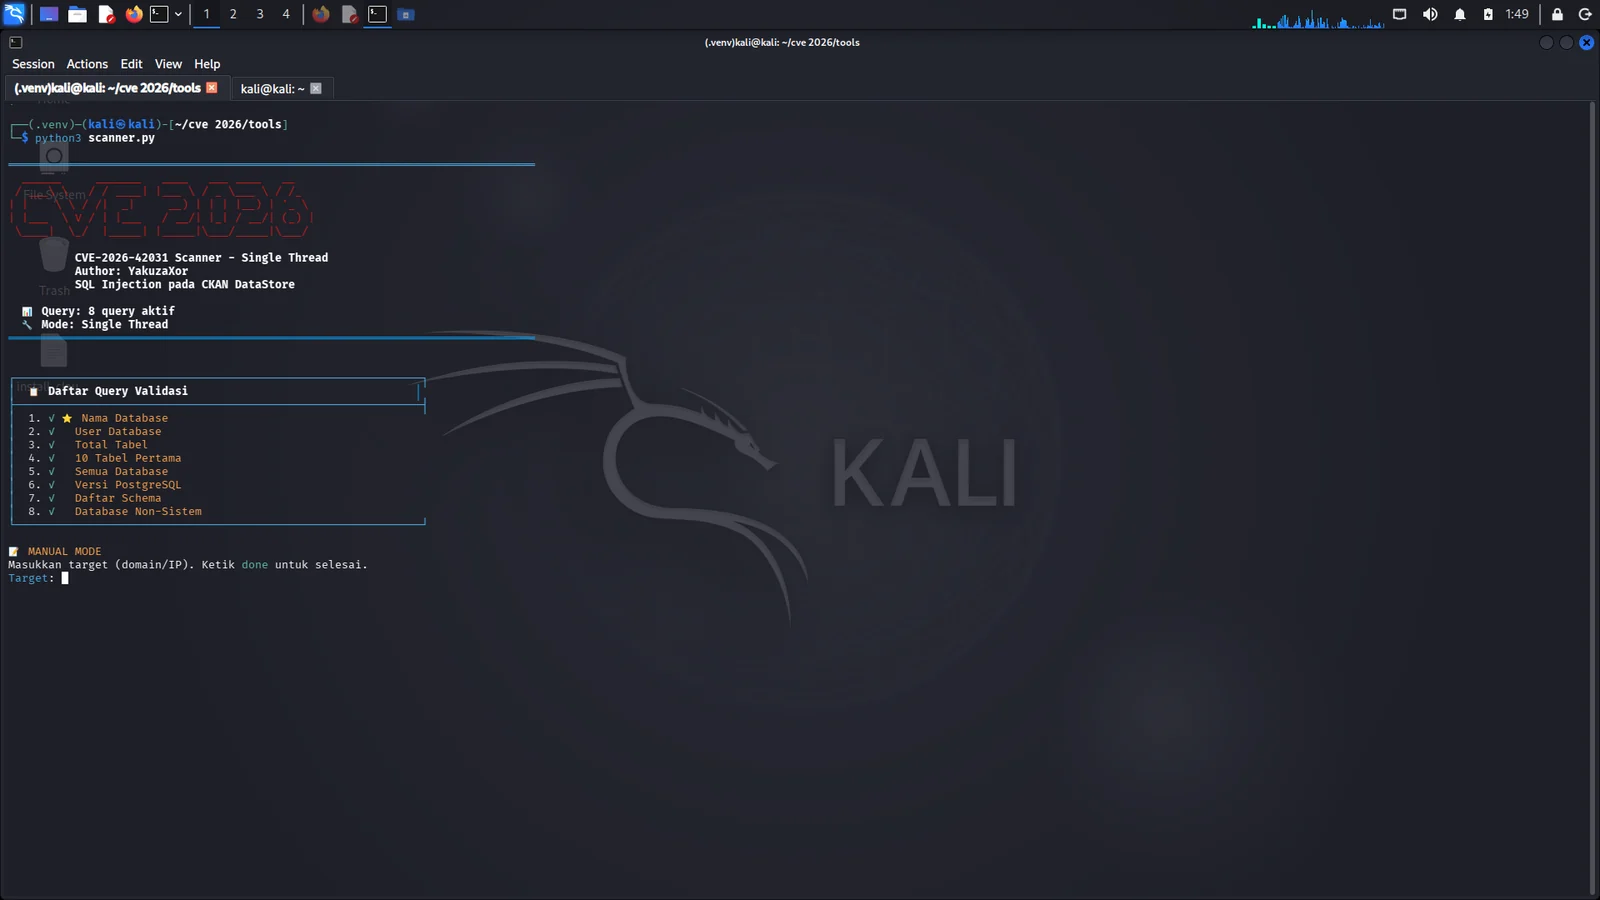 ddrvahandzo90-hue/cve-2026-42031-sql-injection-scanner
Automated SQL injection scanner for CKAN DataStore, detecting and validating CVE-2026-42031 with multi-target scanning, data dumping, and report…
 pedrocruz2202/mongobleed-scanner
🔍 Scan for MongoDB vulnerabilities with MongoBleed, a high-performance tool for detecting CVE-2025-14847 across large networks quickly and…
 fantasy-fql/esapi-sqlinjection-cve-2025-5878-exploit
Exploit for CVE-2025-5878 targeting ESAPI's encodeForSQL() method with OracleCodec, enabling time-based blind SQL injection. Supports database…
 xploitgh0st/cve-2025-26794-exploit
SQL injection exploit for CVE-2025-26794 in Exim 4.98. Automated data extraction via time-based blind SQLi. For authorized penetration testing only.