
CVE-2022-34265
 aeyesec/cve-2022-34265
PoC for CVE-2022-34265 (Django)
database-securityexploitationpenetration-testing+2
aeyesec/cve-2022-34265PoC for CVE-2022-34265 (Django)
 againstthelight/cve-2022-37203
CVE-2022-37203 POC
 drkbcn/lblfixer_cve_2022_31181
Module for PrestaShop 1.6.1.X/1.7.X to fix CVE-2022-31181 / CVE-2022-36408 vulnerability (Chain SQL Injection)
 sadshade/cve-2022-24706-couchdb-exploit
Apache CouchDB 3.2.1 - Remote Code Execution (RCE)
 againstthelight/cve-2022-37206
CVE-2022-37206 POC
 againstthelight/cve-2022-37204
Proof-of-concept exploit for an authenticated SQL injection vulnerability in JFinal CMS 5.1.0, demonstrating information disclosure and potential…
 spring-io/cve-2022-22976-bcrypt-skips-salt
CLI tool to detect and update BCrypt password hashes with vulnerable work factor 31, integrating with Spring Security databases for CVE-2022-xxxx…
 againstthelight/cve-2022-37205
CVE-2022-37205 POC
 h4md153v63n/cve-2022-40032_simple-task-managing-system-v1.0-sql-injection-vulnerability-unauthenticated
CVE-2022-40032: Simple Task Managing System - 'login' and 'password' SQL Injection (Unauthenticated)
 open-flaw/cve-2022-33171
CVE-2022-33171: TypeORM SQL Injection Vulnerability
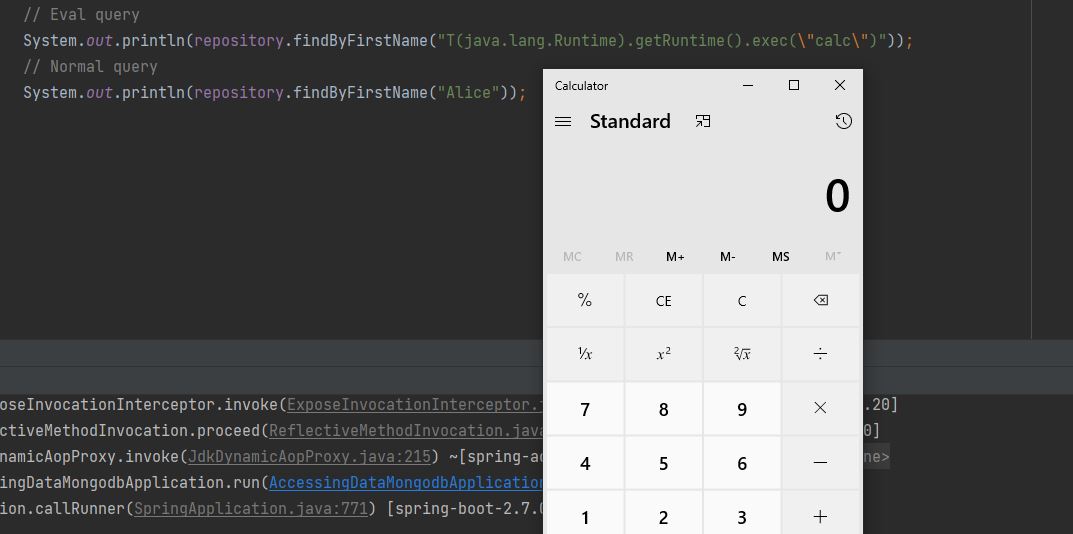 trganda/cve-2022-22980
Proof-of-concept exploit for CVE-2022-22980 targeting Spring Data MongoDB. Demonstrates remote code execution via crafted MongoDB queries. Requires…
 safe3s/cve-2022-21661
The first poc video presenting the sql injection test from ( WordPress Core 5.8.2-'WP_Query' / CVE-2022-21661)
 againstthelight/cve-2022-37210
CVE-2022-37210 POC
 murataydemir/cve-2022-22980
[CVE-2022-22980] Spring Data MongoDB SpEL Expression Injection
 h4md153v63n/cve-2022-40347_intern-record-system-phone-v1.0-sql-injection-vulnerability-unauthenticated
CVE-2022-40347: Intern Record System - 'phone', 'email', 'deptType' and 'name' SQL Injection (Unauthenticated)
 tomoe-12/cve_2022_3141
Detailed security analysis and proof-of-concept for CVE-2022-3141, an unauthenticated SQL injection in ACS EDU 3rd Gen, including reproduction steps…
 charondefalt/wordpress--cve-2022-21661
Proof-of-concept exploit for CVE-2022-21661, a SQL injection vulnerability in WordPress Core WP_Query, demonstrating the attack and providing…
 vesu-nights/multiexploit
CVE-2023-21173 Exploit - Remote Code Execution in SQL Server 2022