
etherblob-explorer
 litneet64/etherblob-explorer
Search and extract blob files on the Ethereum Blockchain network
ctfdata-recoveryforensics+2
435 years ago
litneet64/etherblob-explorerSearch and extract blob files on the Ethereum Blockchain network
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 fox-it/dissect
Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…
 vikwin/pcapfex
'Packet Capture Forensic Evidence eXtractor' is a tool that finds and extracts files from packet capture files
 carmaa/interrogate
Interrogate is a proof-of-concept tool for identification of cryptographic keys in binary material (regardless of target operating system), first and…
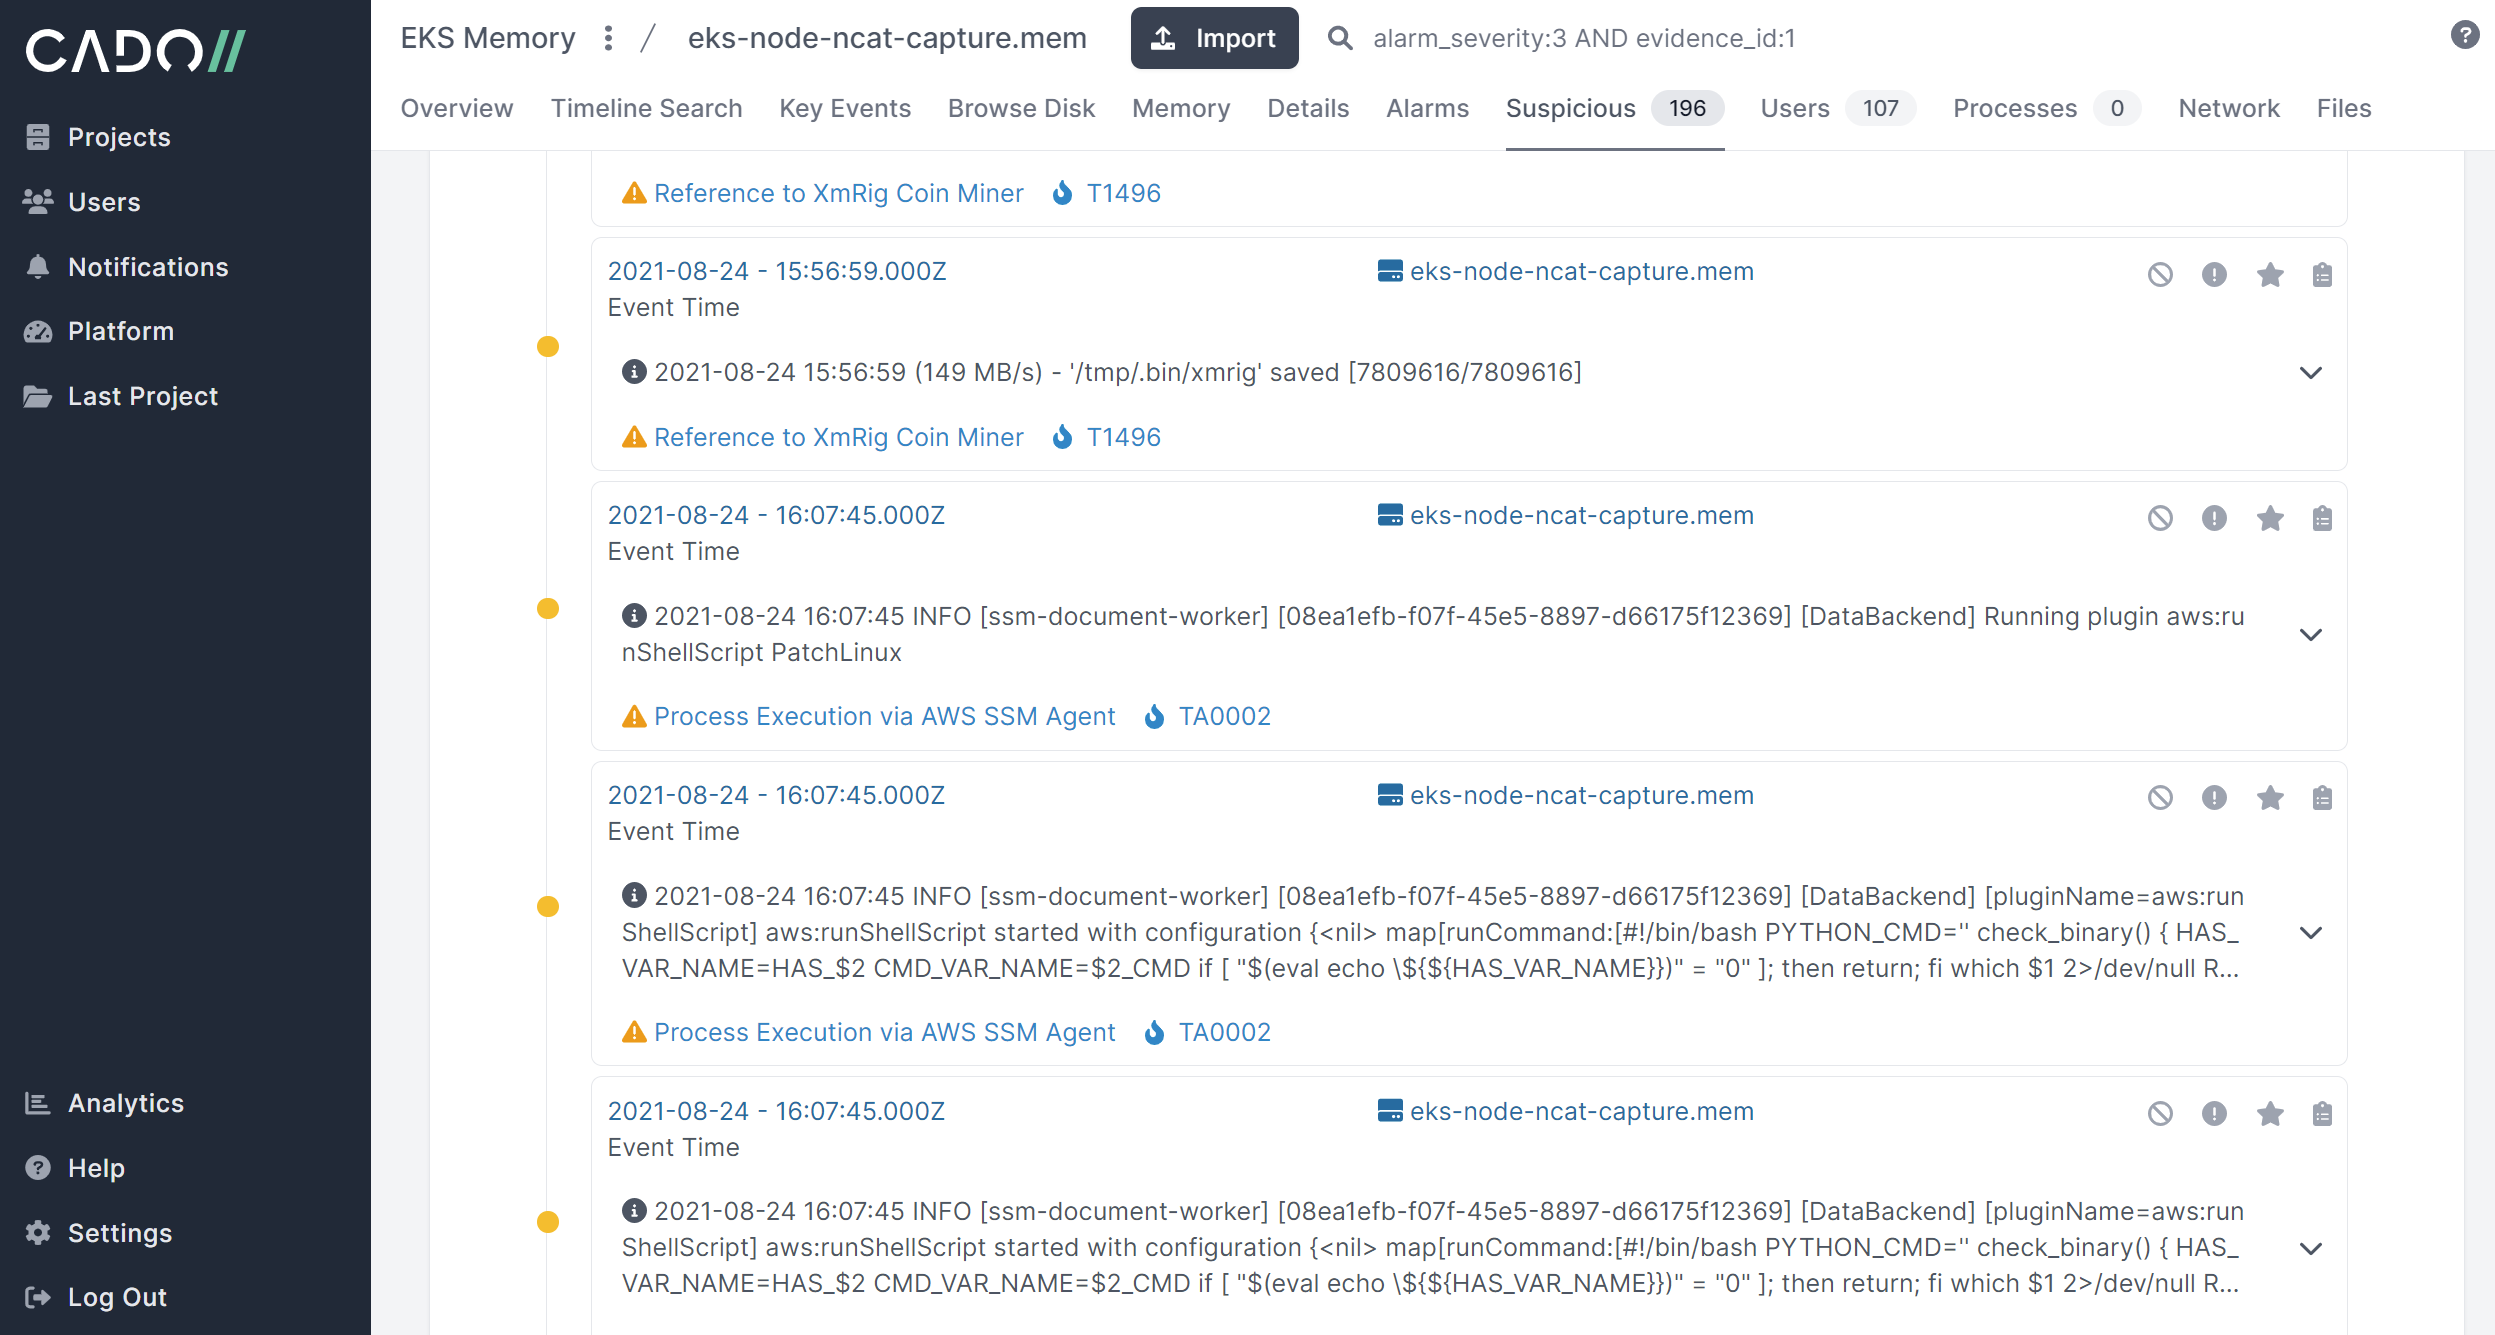 cado-security/rip_raw
Rip Raw is a small tool to analyse the memory of compromised Linux systems.

 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 b16f00t/whapa
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…

 cristianzsh/forensictools
Collection of forensic tools
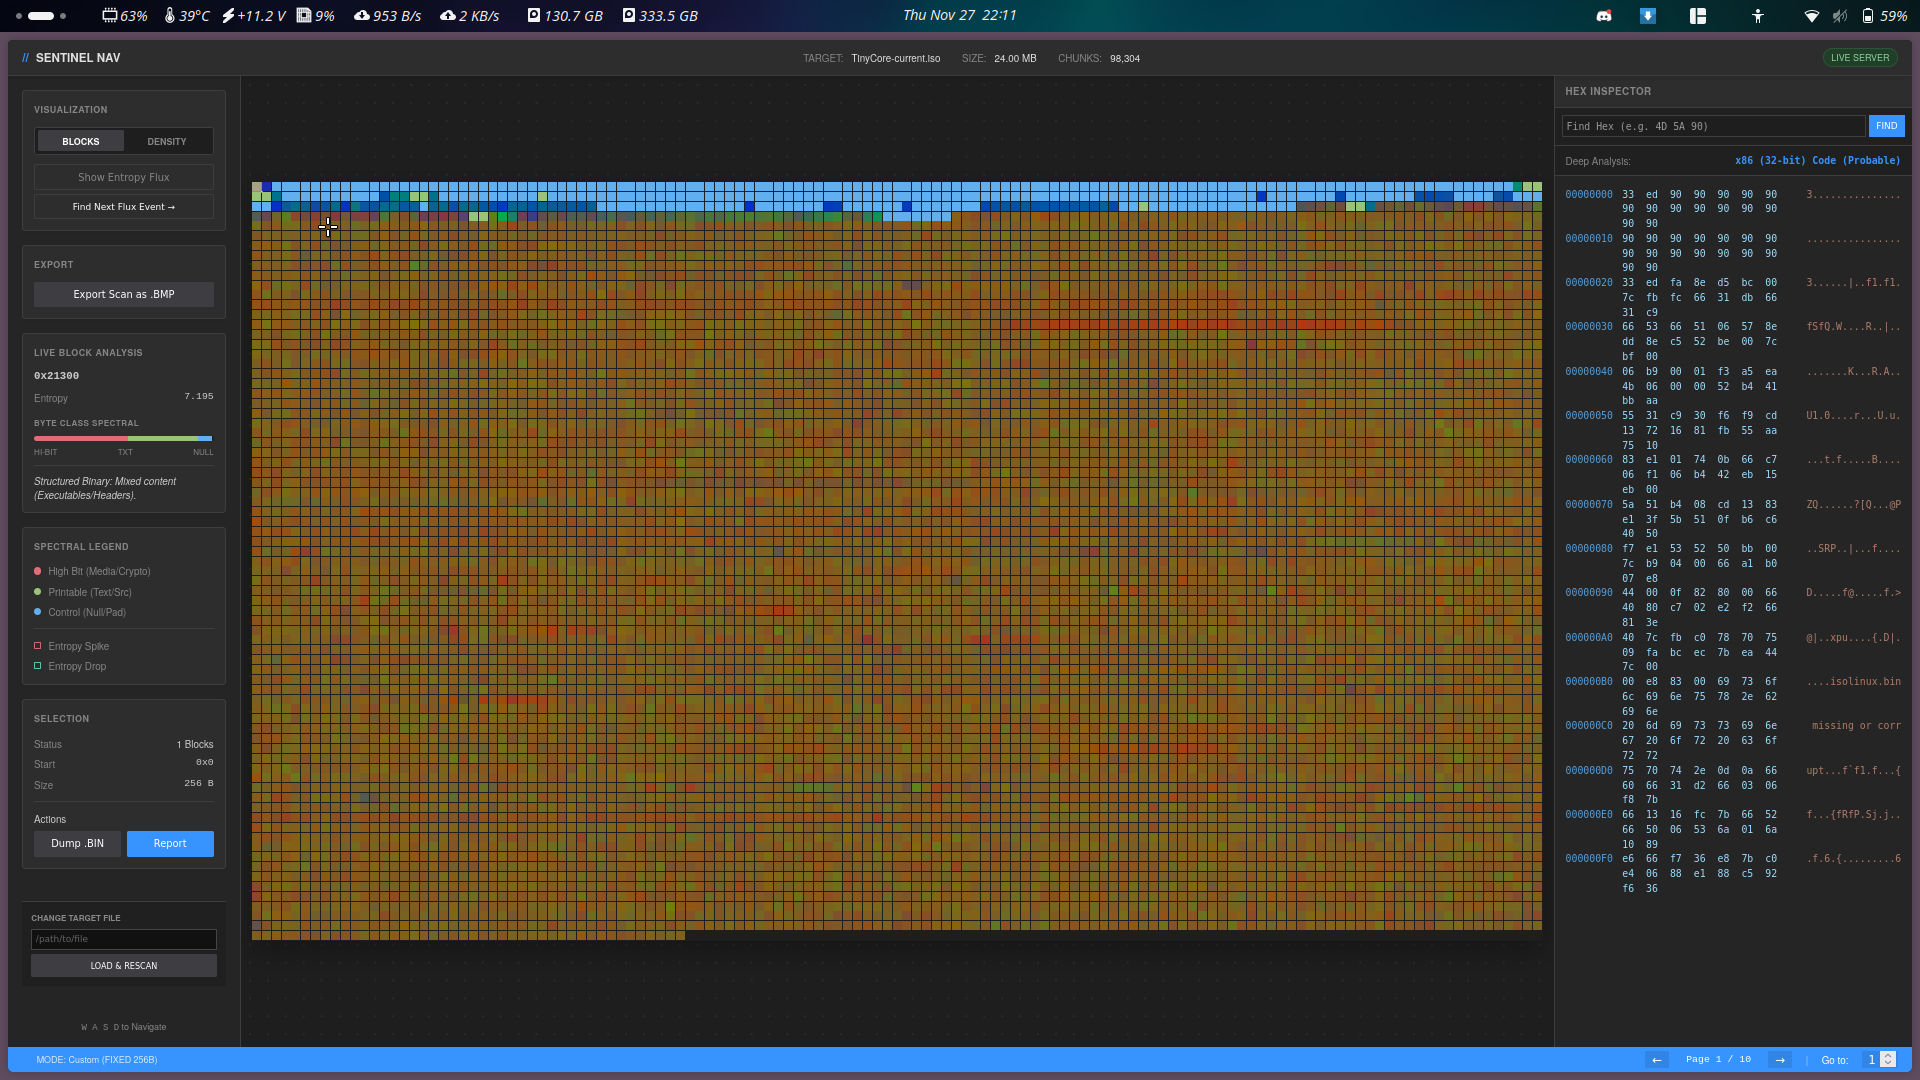 smolfiddle/sentinelnav
SentinelNav: zero-dependency, pure Python binary visualization and forensics tool.
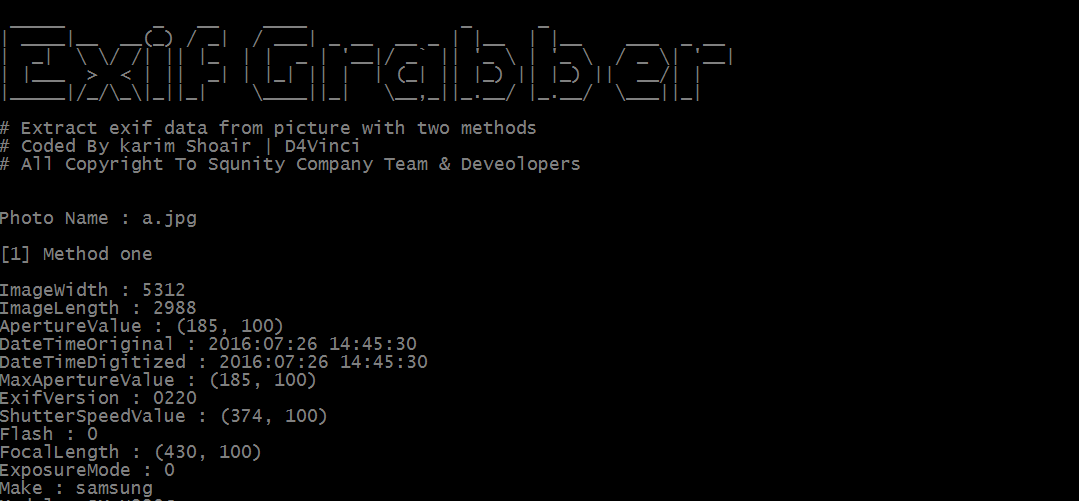 d4vinci/exif-grabber
A python tool that will extract exif data from picture with two methods
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
 emrekybs/osintcase
An OSINT investigation case mapping tool for organizing entities, relationships, evidence, and intelligence.
 sleuthkit/autopsy
Autopsy® is a digital forensics platform and graphical interface to The Sleuth Kit® and other digital forensics tools. It can be used by law…