
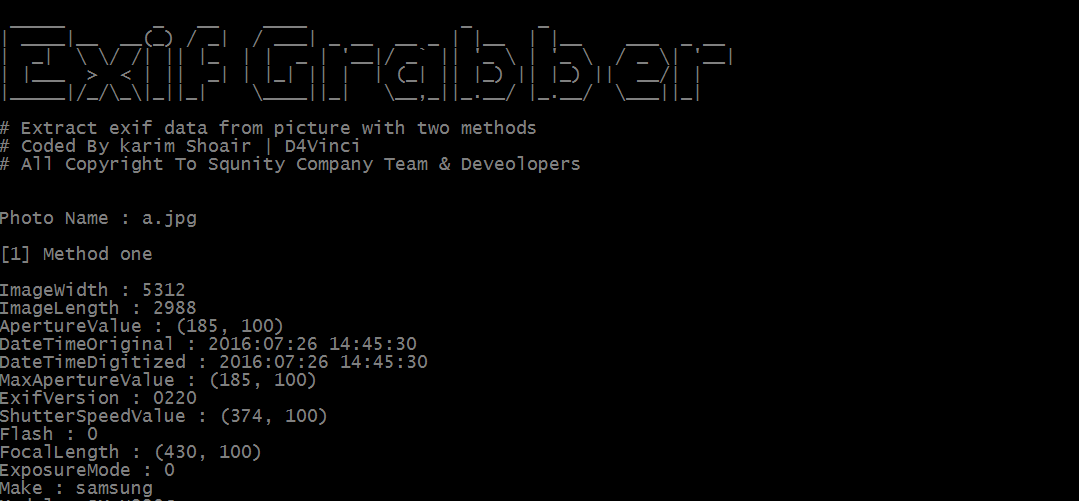
Exif-Grabber
 d4vinci/exif-grabber
A python tool that will extract exif data from picture with two methods
data-recoverydigital-forensicsforensics+3
43
d4vinci/exif-grabberA python tool that will extract exif data from picture with two methods
 trustedsec/tscopy
Python tool that parses the NTFS $MFT to copy locked files during incident response, bypassing OS locks by reading raw disk locations. Supports…
 rejithregi-group/securityproject
Python Security Project that implements a file encryption and decryption tool
 iqbaalilmii/acropalypse-reconstructor
A lightweight CLI tool to detect and reconstruct cropped images vulnerable to Acropalypse (CVE-2023-21036 and CVE-2023-28303) written in Python.
 log2timeline/plaso
Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…
 battalkoc/kalici-dosya-silme-araci
Securely deletes files by overwriting them with user-specified iterations of random data, then removes the file to prevent recovery. Supports Python…
 infobyte/cve-2023-21036
Detection and sanitization for Acropalypse Now - CVE-2023-21036
 fox-it/dissect
Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…
 juanceresa/sift-kg
Turn any collection of documents into a knowledge graph. Extract entities and relationships via LLM, deduplicate with your approval. Map domains,…
 vikwin/pcapfex
'Packet Capture Forensic Evidence eXtractor' is a tool that finds and extracts files from packet capture files
 dmtrkovalenko/ffs
F*ck file system - cli file search tool that bypasses OS kernel and reads your disc directlry
 disqualifier/psa-2026-00043-recovery
Recovery notes for proxmox advisory ID: PSA-2026-00043-1 (CVE-2023-54391)
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 ang13t/dronextract
Digital forensics suite for DJI drones that parses telemetry files, extracts hidden data via steganography, visualizes flight paths, and detects…
 korczis/foremost
File carving utility that recovers deleted files from disk images and raw drives by matching headers, footers, and internal structures via…
 kfallahi/underlaycopy
PowerShell toolkit that extracts locked Windows files (SAM, SYSTEM, NTDS, ...) using MFT parsing and raw disk reads
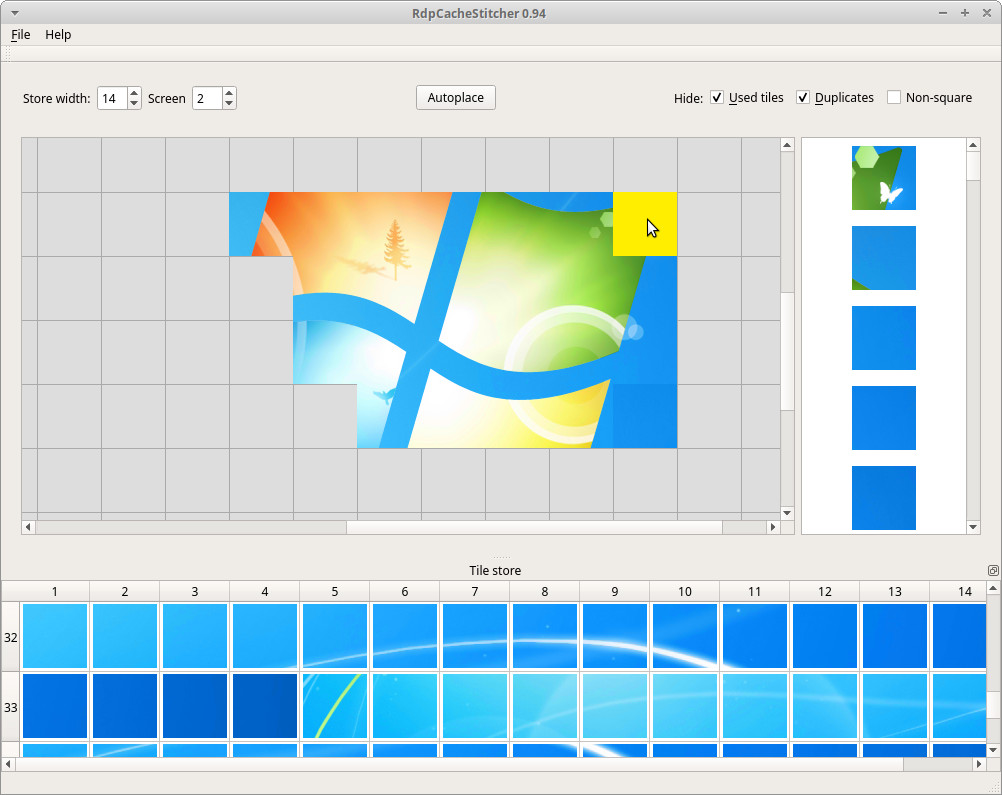 bsi-bund/rdpcachestitcher
RdpCacheStitcher is a tool that supports forensic analysts in reconstructing useful images out of RDP cache bitmaps.