

IPED
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
data-recoverydigital-forensicsdisk-forensics+9
3.1k
sepinf-inc/ipedIPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 log2timeline/plaso
Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…
 fox-it/dissect
Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…
 juanceresa/sift-kg
Turn any collection of documents into a knowledge graph. Extract entities and relationships via LLM, deduplicate with your approval. Map domains,…
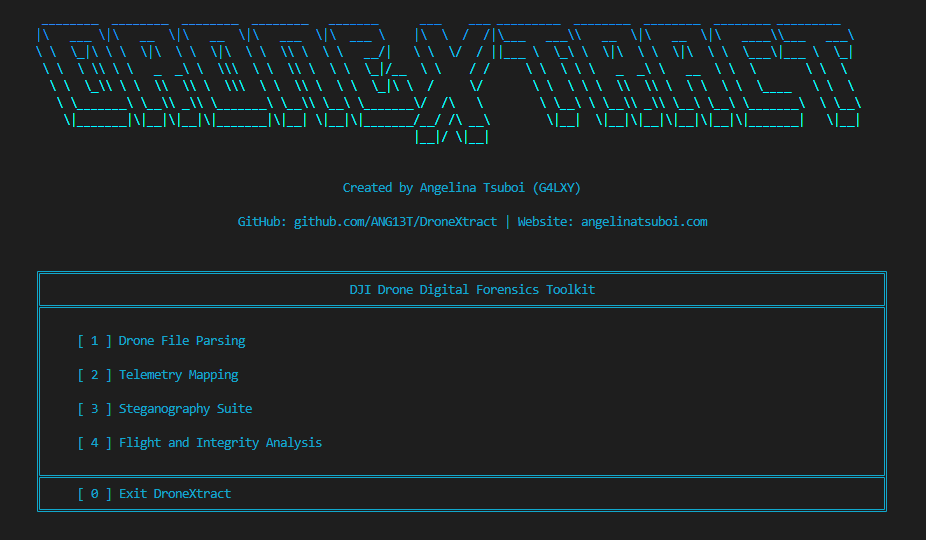 ang13t/dronextract
Digital forensics suite for DJI drones that parses telemetry files, extracts hidden data via steganography, visualizes flight paths, and detects…
 korczis/foremost
File carving utility that recovers deleted files from disk images and raw drives by matching headers, footers, and internal structures via…
 kfallahi/underlaycopy
PowerShell toolkit that extracts locked Windows files (SAM, SYSTEM, NTDS, ...) using MFT parsing and raw disk reads
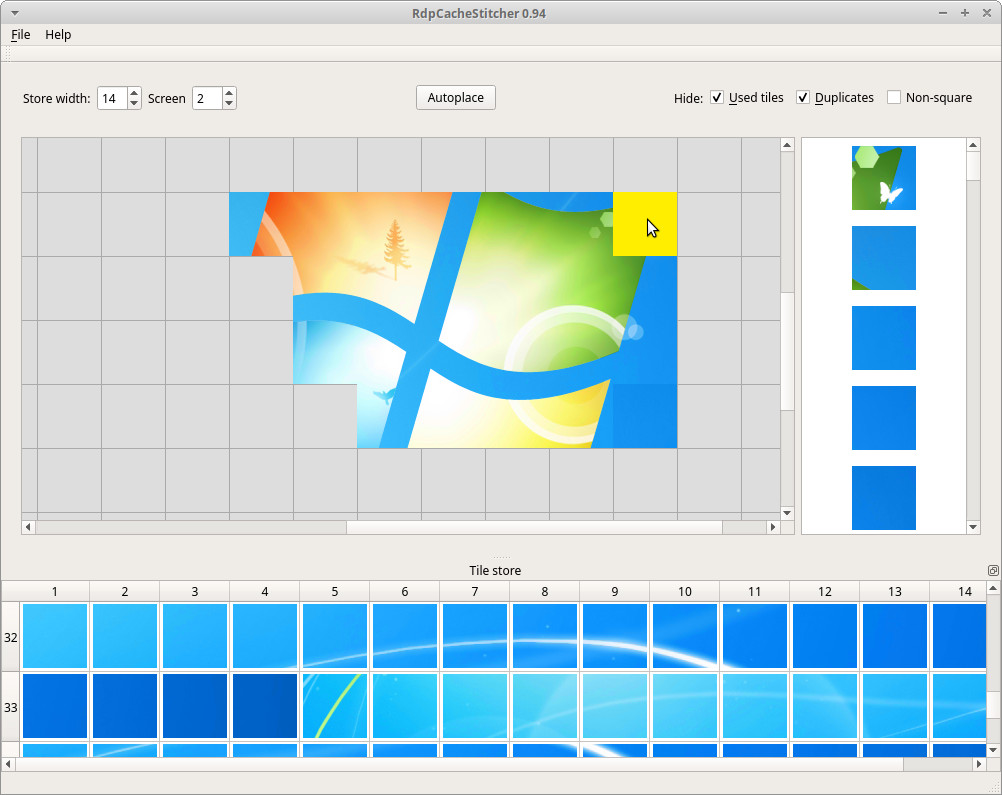 bsi-bund/rdpcachestitcher
RdpCacheStitcher is a tool that supports forensic analysts in reconstructing useful images out of RDP cache bitmaps.
 redrum0381/ataboy
ATAboy is a user-friendly bridge that allows legacy CHS only style IDE (PATA) hard drives to be connected to a modern computer as a standard USB Mass…
 vikwin/pcapfex
'Packet Capture Forensic Evidence eXtractor' is a tool that finds and extracts files from packet capture files
 trustedsec/tscopy
Python tool that parses the NTFS $MFT to copy locked files during incident response, bypassing OS locks by reading raw disk locations. Supports…
 dmtrkovalenko/ffs
F*ck file system - cli file search tool that bypasses OS kernel and reads your disc directlry
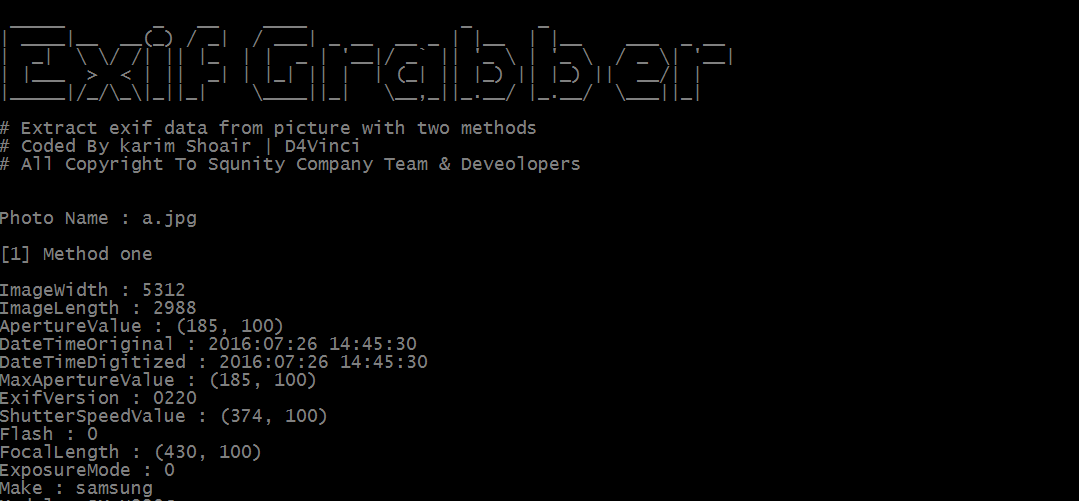 d4vinci/exif-grabber
A python tool that will extract exif data from picture with two methods
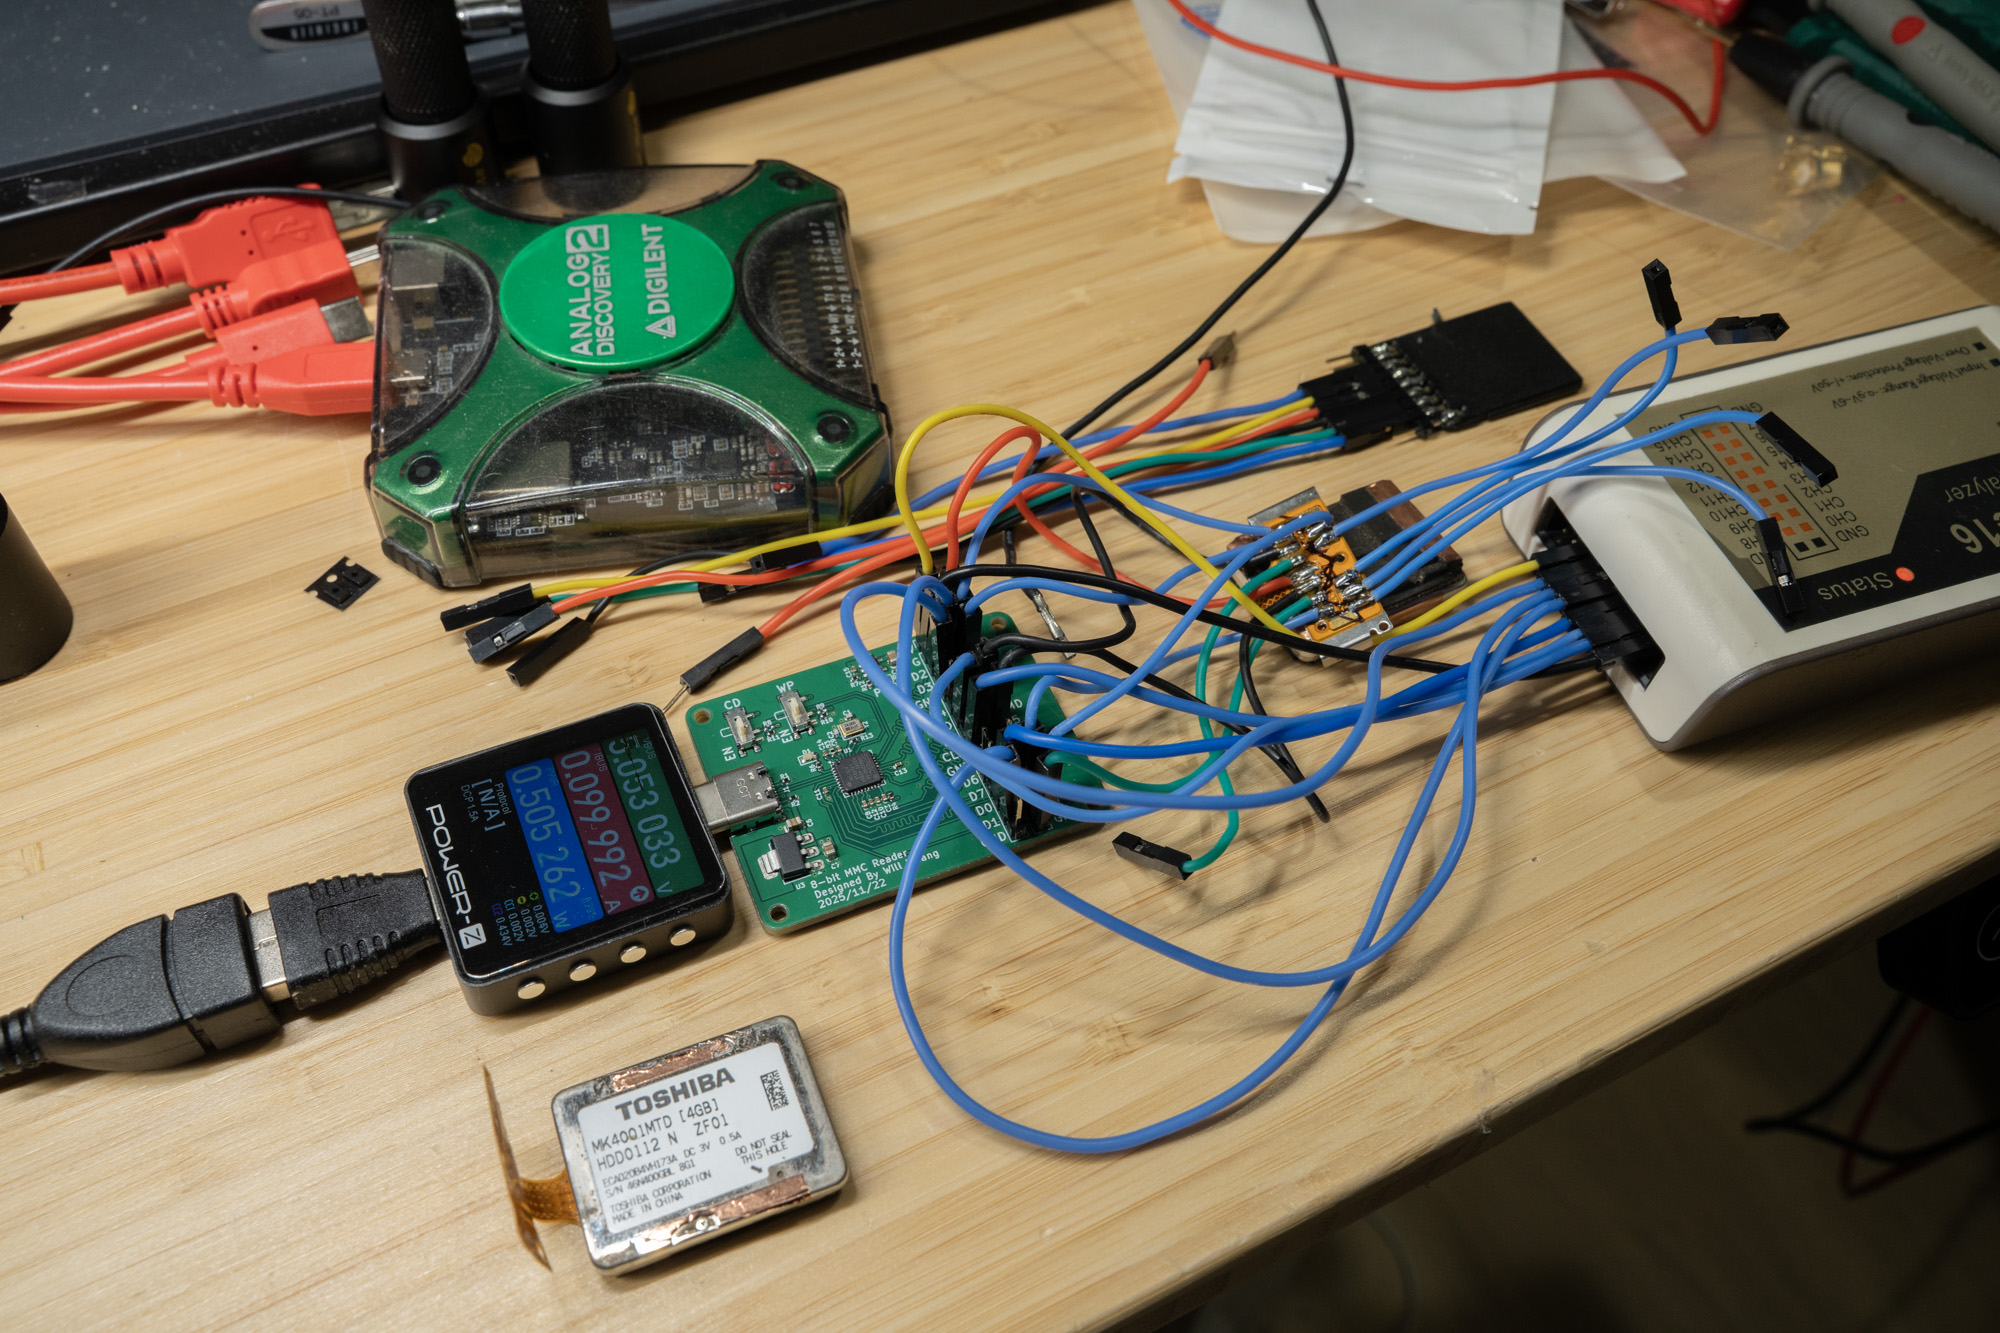 will127534/mk4001mtd-usb-bridge
RP2040 firmware that bridges a Toshiba MK4001MTD 0.85" SDIO microdrive as a USB mass storage device, implementing the full SDIO-ATA protocol stack…
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
 rejithregi-group/securityproject
Python Security Project that implements a file encryption and decryption tool
 a-poc/blueteam-tools
Tools and Techniques for Blue Team / Incident Response